
GDPR: data protection in the same system as information security.
Record of processing, DPIAs, data-subject requests and technical measures use the same assets, vendors and controls as your ISMS. Deadlines sit on the request, and the list of technical measures comes from the ISMS controls.



 5.0 out of 5
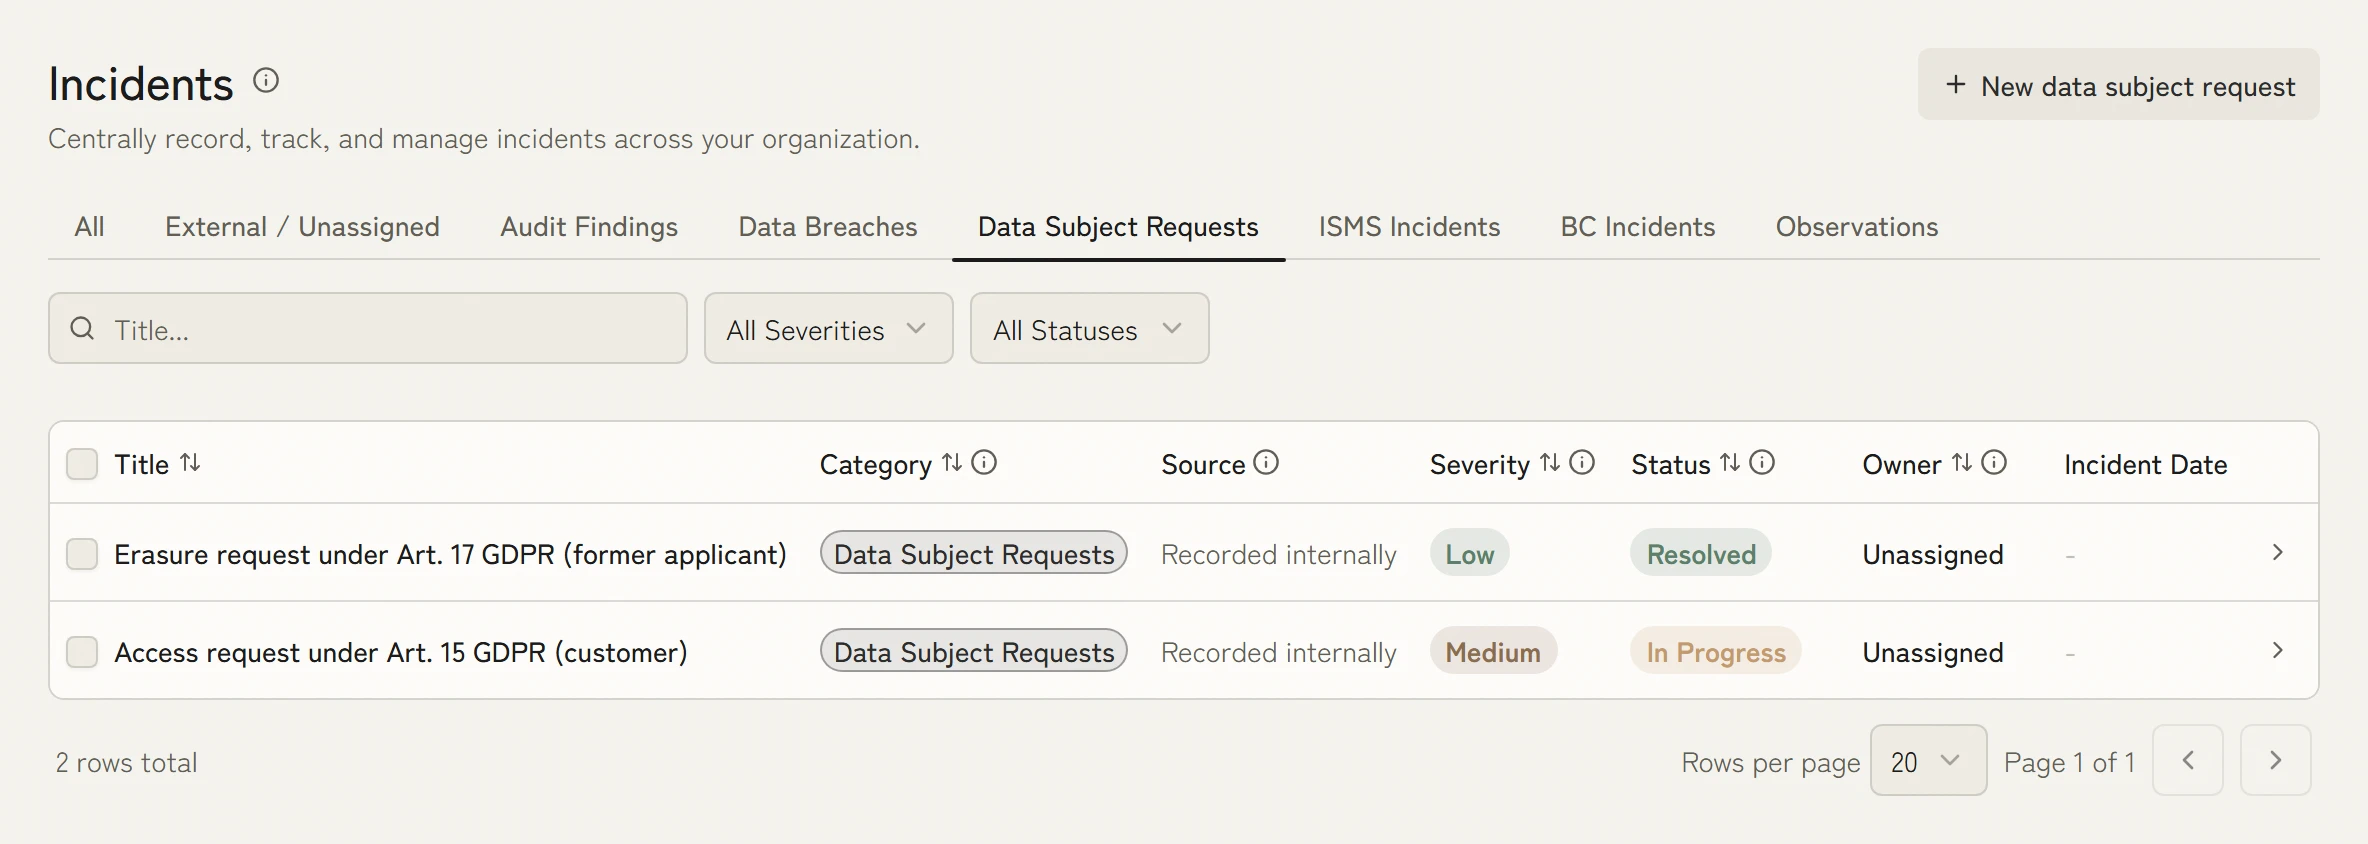
Data subject requests with deadline and owner
Access, erasure, rectification and portability run as a case with a deadline, an owner, a review and a completion. The month set by Article 12 sits on the case rather than in an inbox, and every step stays traceable afterwards.
1 monthData subject request deadline
DPIAs with a documented threshold check
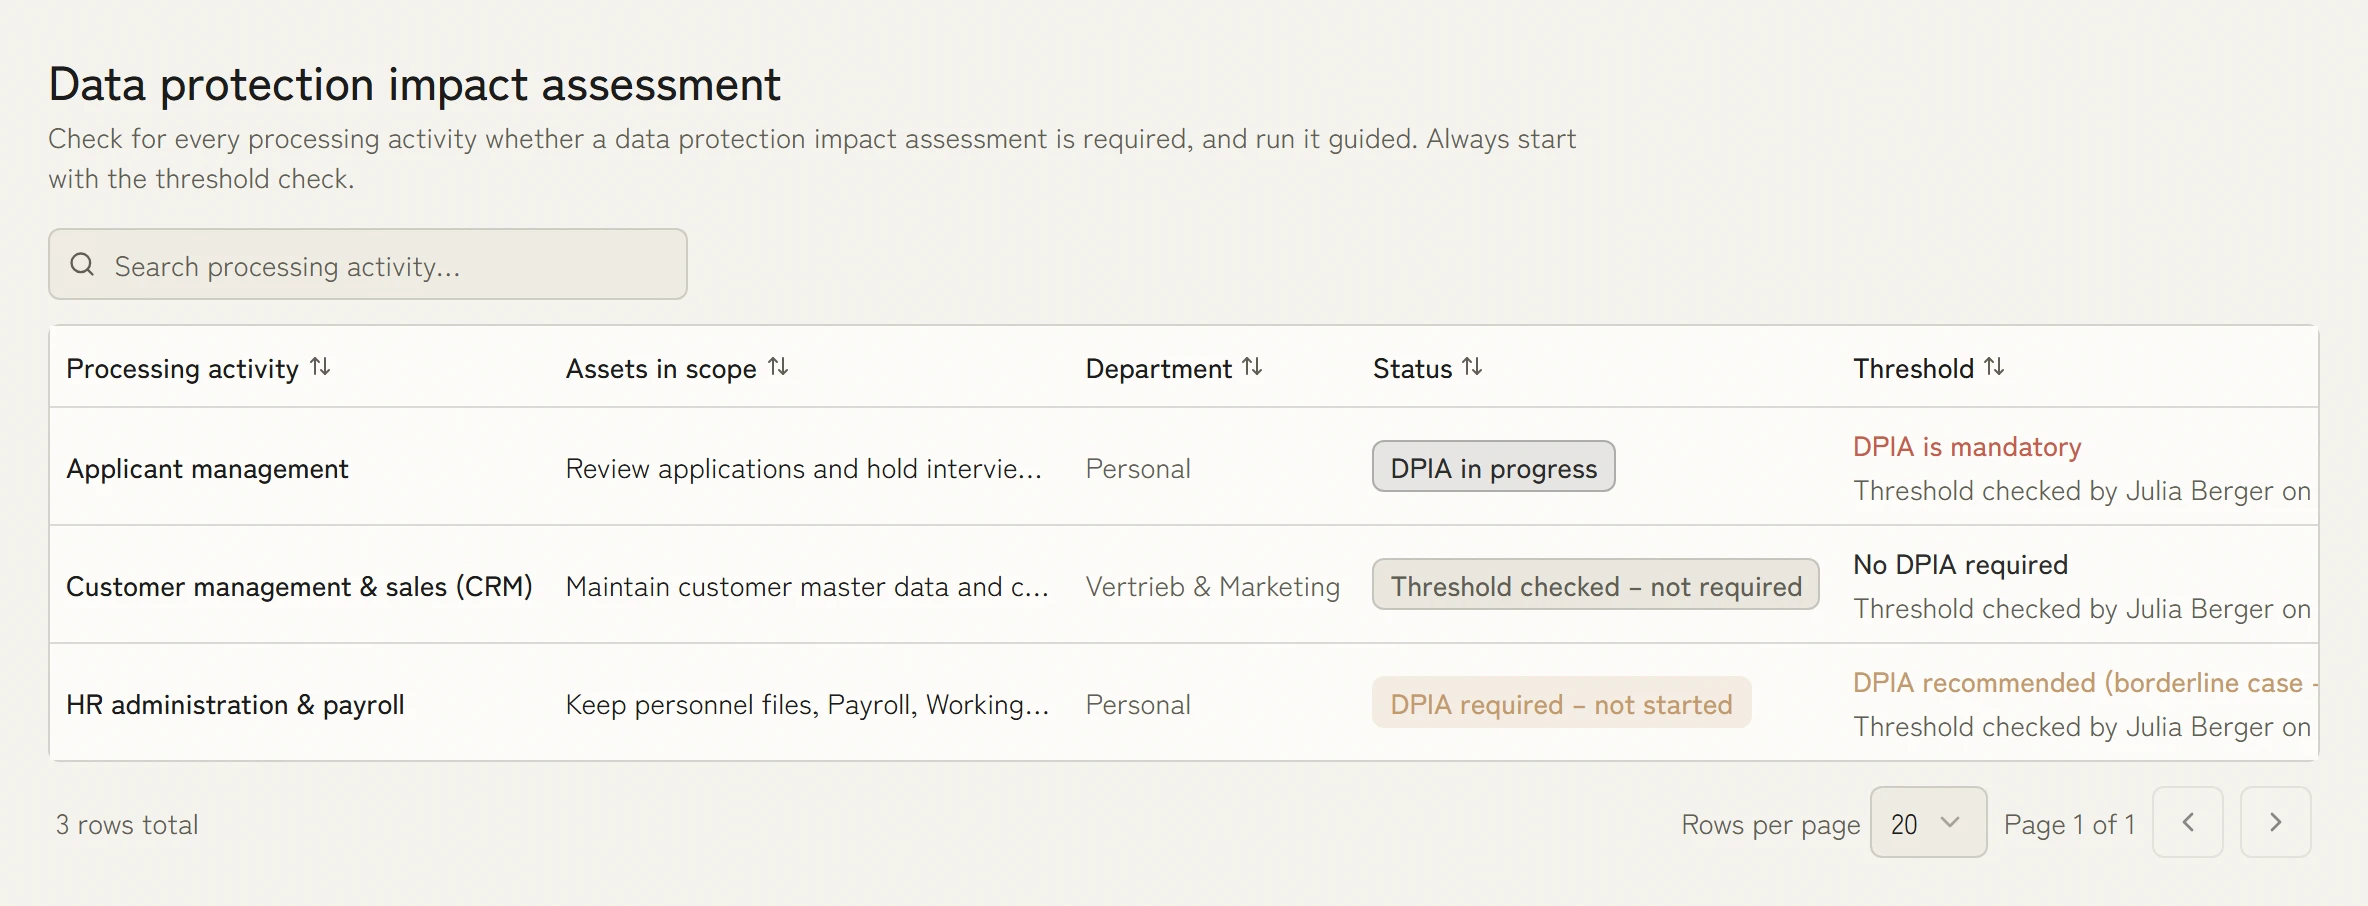
For every processing activity, KaitoSec records whether a data protection impact assessment is required, who checked the threshold and where the assessment stands. Article 35 asks for the reasoning, not only the outcome.
Security measures from the ISMS, not from an annex
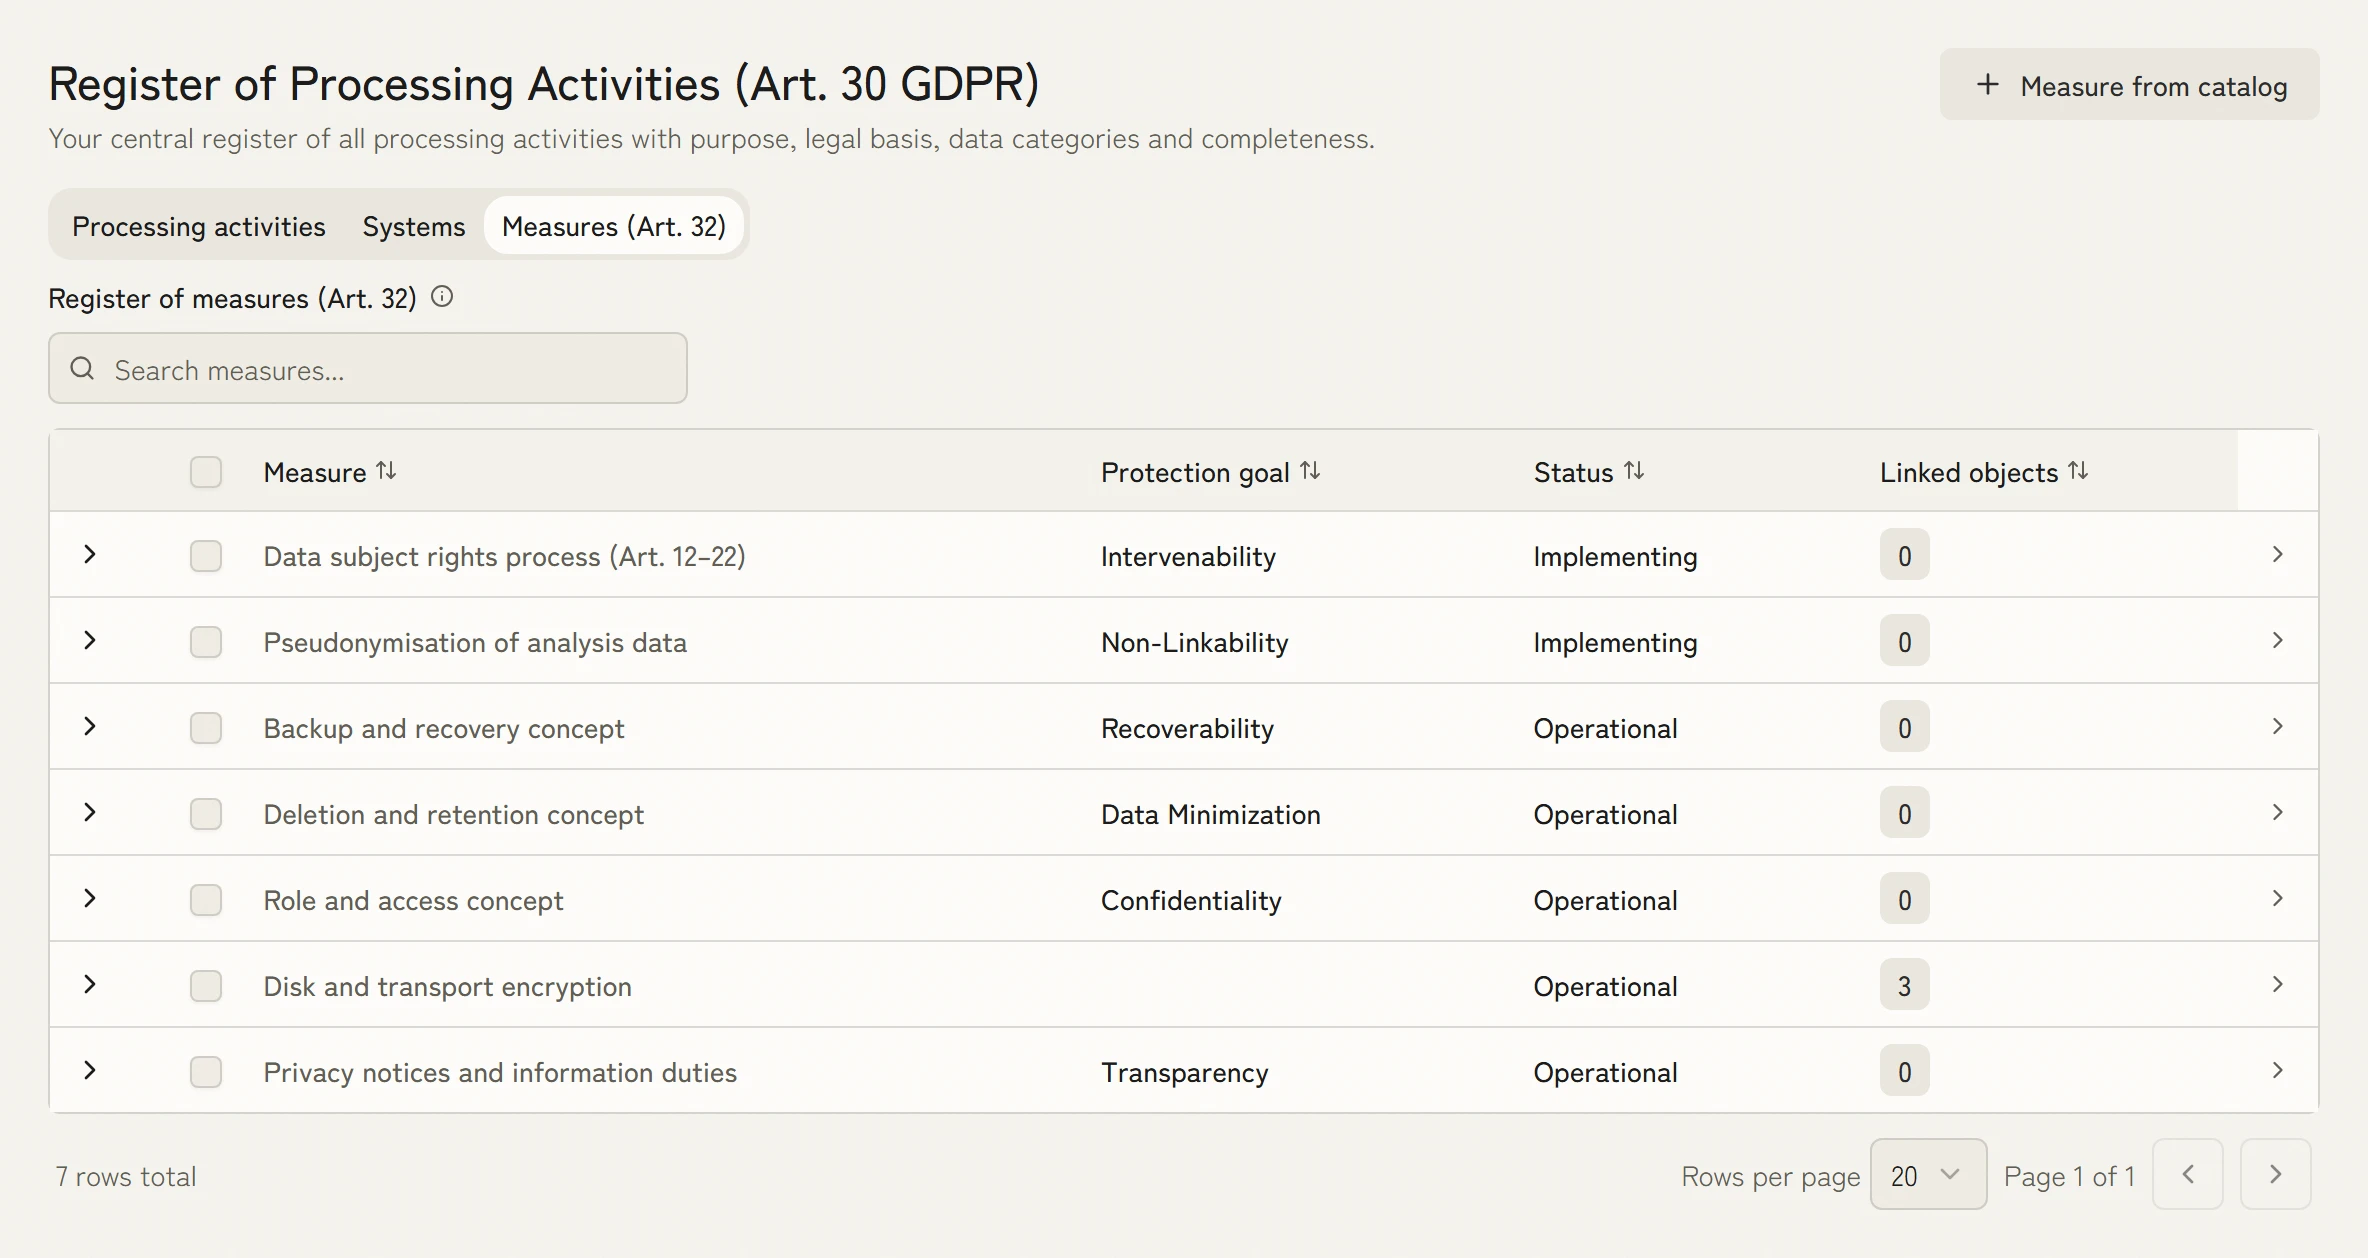
The register of technical and organisational measures reads the same controls the ISMS maintains. Objective, status and linked objects sit on the record, instead of a measures list living its own life as a contract annex.
GDPR on one model with ISO 27001 and NIS2
A processor risk found here feeds the supplier review in the ISMS, an ISO 27001 access control also evidences a security measure under Article 32, and the breach chain carries the NIS2 notification. One inventory, one risk register, three audit regimes.
72hBreach notification window
Connect the GDPR with other standards
Connect data protection with the standards already running in the same house.
GDPR by company and role
More for the GDPR
Controlled data subject request workflow
Capture access, erasure, portability and rectification requests in a controlled workflow. Accountability, deadline, review and completion remain traceable on the request.
Guided DPIA
Data Protection Impact Assessments are mandatory for high-risk processing activities. KaitoSec guides teams through the structured DPIA process, captures prior consultation requirements, and links assessments to your processing register for ongoing review.
A RoPA linked to your actual systems
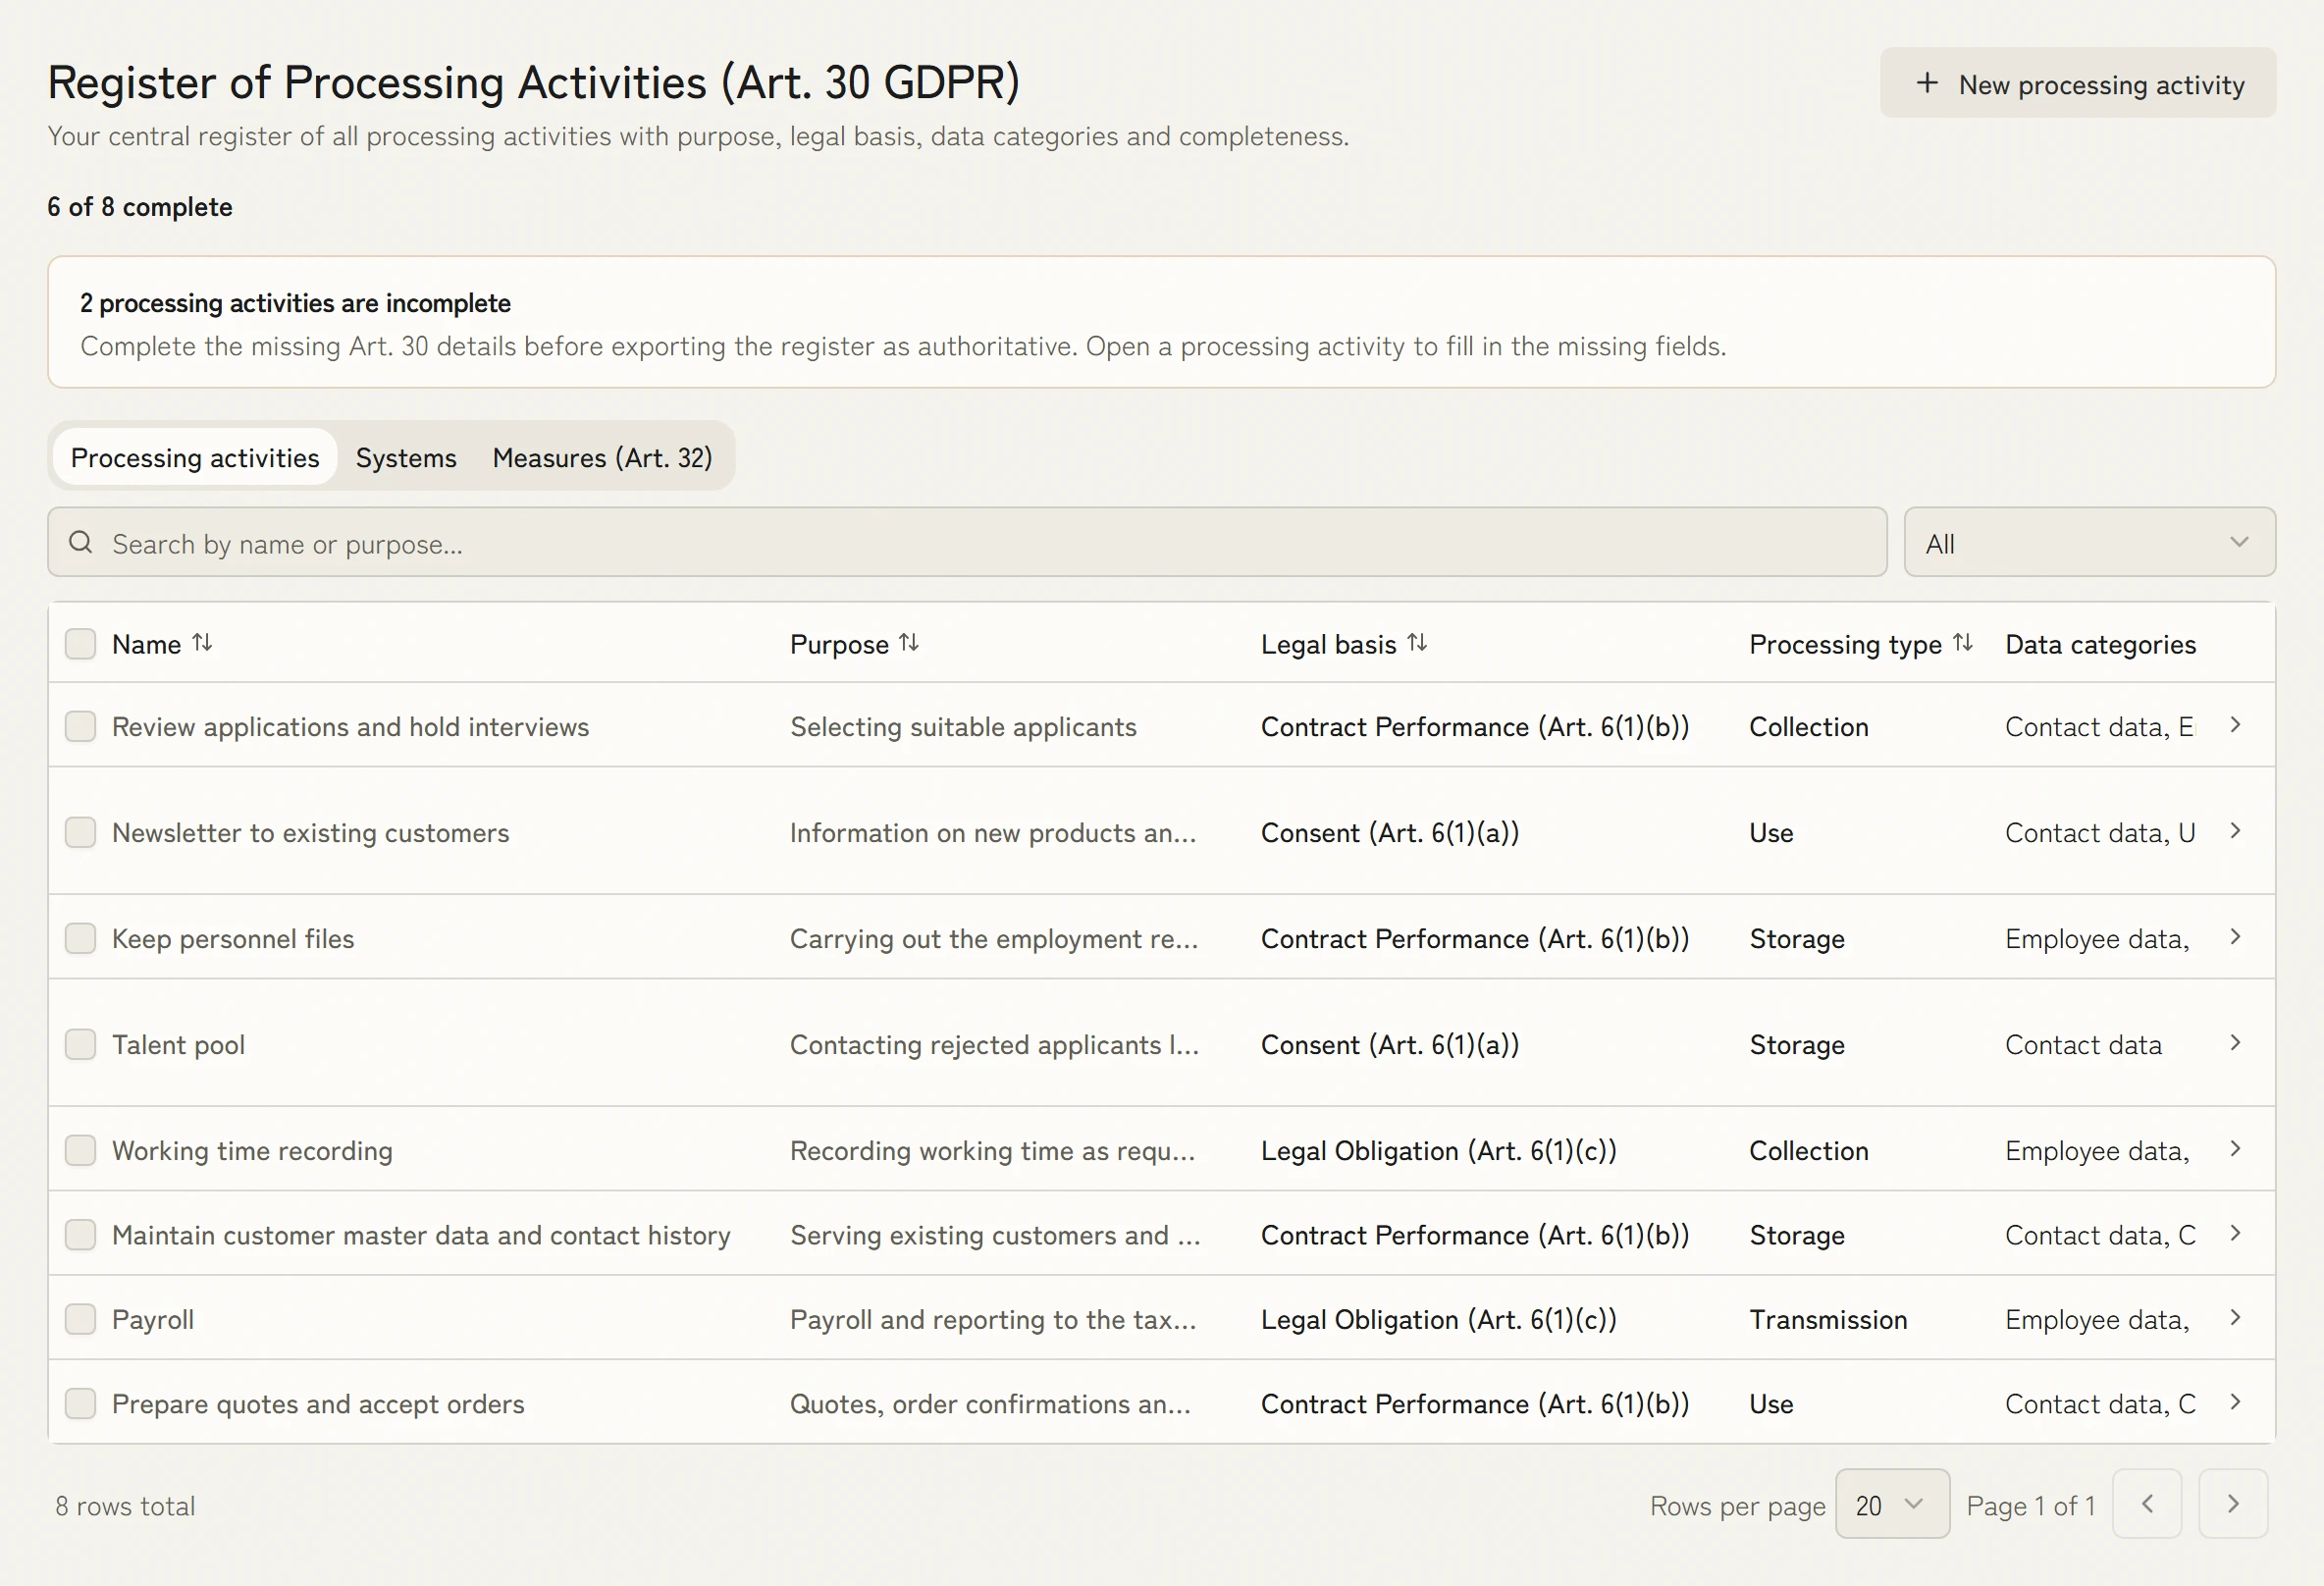
Connect processing activities with systems, purposes, legal bases, data categories and accountable owners. Changes in the linked context show which entries require professional review.
GDPR on one model with ISO 27001 and NIS2
A processor risk identified in the DSMS feeds the ISMS supplier review. An ISO 27001 access control also evidences a GDPR security measure. The breach notification chain feeds NIS2 incident reporting. One asset register, one risk register, three audit regimes answered from the same workspace.
Records of Processing Activities (RoPA)
Map every processing activity to a data category, legal basis, retention period, and responsible team. KaitoSec keeps your Record of Processing Activities audit-ready and exportable for supervisory authority requests at any time.
Vendor Data Processing Agreements
Track all third-party data processors, their DPA status, and sub-processor chains. KaitoSec alerts you when DPAs are missing, expired, or no longer reflect current processing scope, a common source of regulatory findings.
Consent & Cookie Management
Maintain a structured record of consent mechanisms across your products. KaitoSec integrates with your consent management platform to provide a unified view of consent status, withdrawal handling, and purpose limitation.
What the GDPR requires
The GDPR asks for accountability: a record of processing activities under Article 30, a legal basis per purpose, impact assessments for high-risk processing under Article 35, appropriate technical and organisational measures under Article 32, deadlines for data subject rights, and breach notification within 72 hours.
Frequently asked questions about the GDPR
What is a DPIA and when is it required?
A Data Protection Impact Assessment is a structured process to identify and minimise privacy risks before starting a high-risk processing activity. GDPR requires a DPIA when processing is likely to result in a high risk to individuals, for example, large-scale profiling, systematic monitoring, or processing special categories of data. KaitoSec provides a guided DPIA template aligned with EDPB guidelines. Our DPIA knowledge article walks through the process step by step.
What is the difference between a data controller and a data processor under GDPR?
A controller determines the purposes and means of processing personal data. A processor handles data on behalf of a controller. Both have distinct obligations under GDPR, and the relationship must be formalised in a Data Processing Agreement. KaitoSec's vendor module tracks all processor relationships and DPA status. Our data protection knowledge hub covers RoPA, DPIAs and breach response in depth.
How do we handle a data breach under GDPR?
GDPR requires you to notify your supervisory authority within 72 hours of becoming aware of a personal data breach, and to notify affected individuals without undue delay if the breach is high risk. KaitoSec's incident module provides breach assessment workflows, severity scoring, and pre-filled notification templates to meet both deadlines.
Do we need a Data Protection Officer?
A DPO is mandatory for public authorities, organisations that systematically monitor individuals at large scale, or organisations processing special category data at large scale. Even if not mandatory, a DPO or privacy lead is strongly recommended. In Germany, section 38 BDSG additionally requires a DPO once at least 20 people are regularly and permanently involved in automated processing of personal data. KaitoSec supports DPO workflows including DPIA consultation, training records, and authority liaison.
How does GDPR interact with NIS2 for security requirements?
Both regulations require appropriate technical and organisational security measures to protect personal data and IT systems respectively. GDPR focuses on personal data protection, while NIS2 covers broader network and information security. KaitoSec maintains a shared control library so overlapping requirements are implemented once and evidenced across both frameworks.

Your data protection plan in thirty minutes.
In the demo we walk through the record, legal bases, deadlines and processors. You leave knowing which entries need professional review.