
TISAX: only as much work as your assessment level requires
KaitoSec narrows down the required assessment level, maps the VDA ISA criteria to your controls and keeps the evidence on the object. The next OEM assessment reuses the approved work as far as the scope allows.



 5.0 out of 5
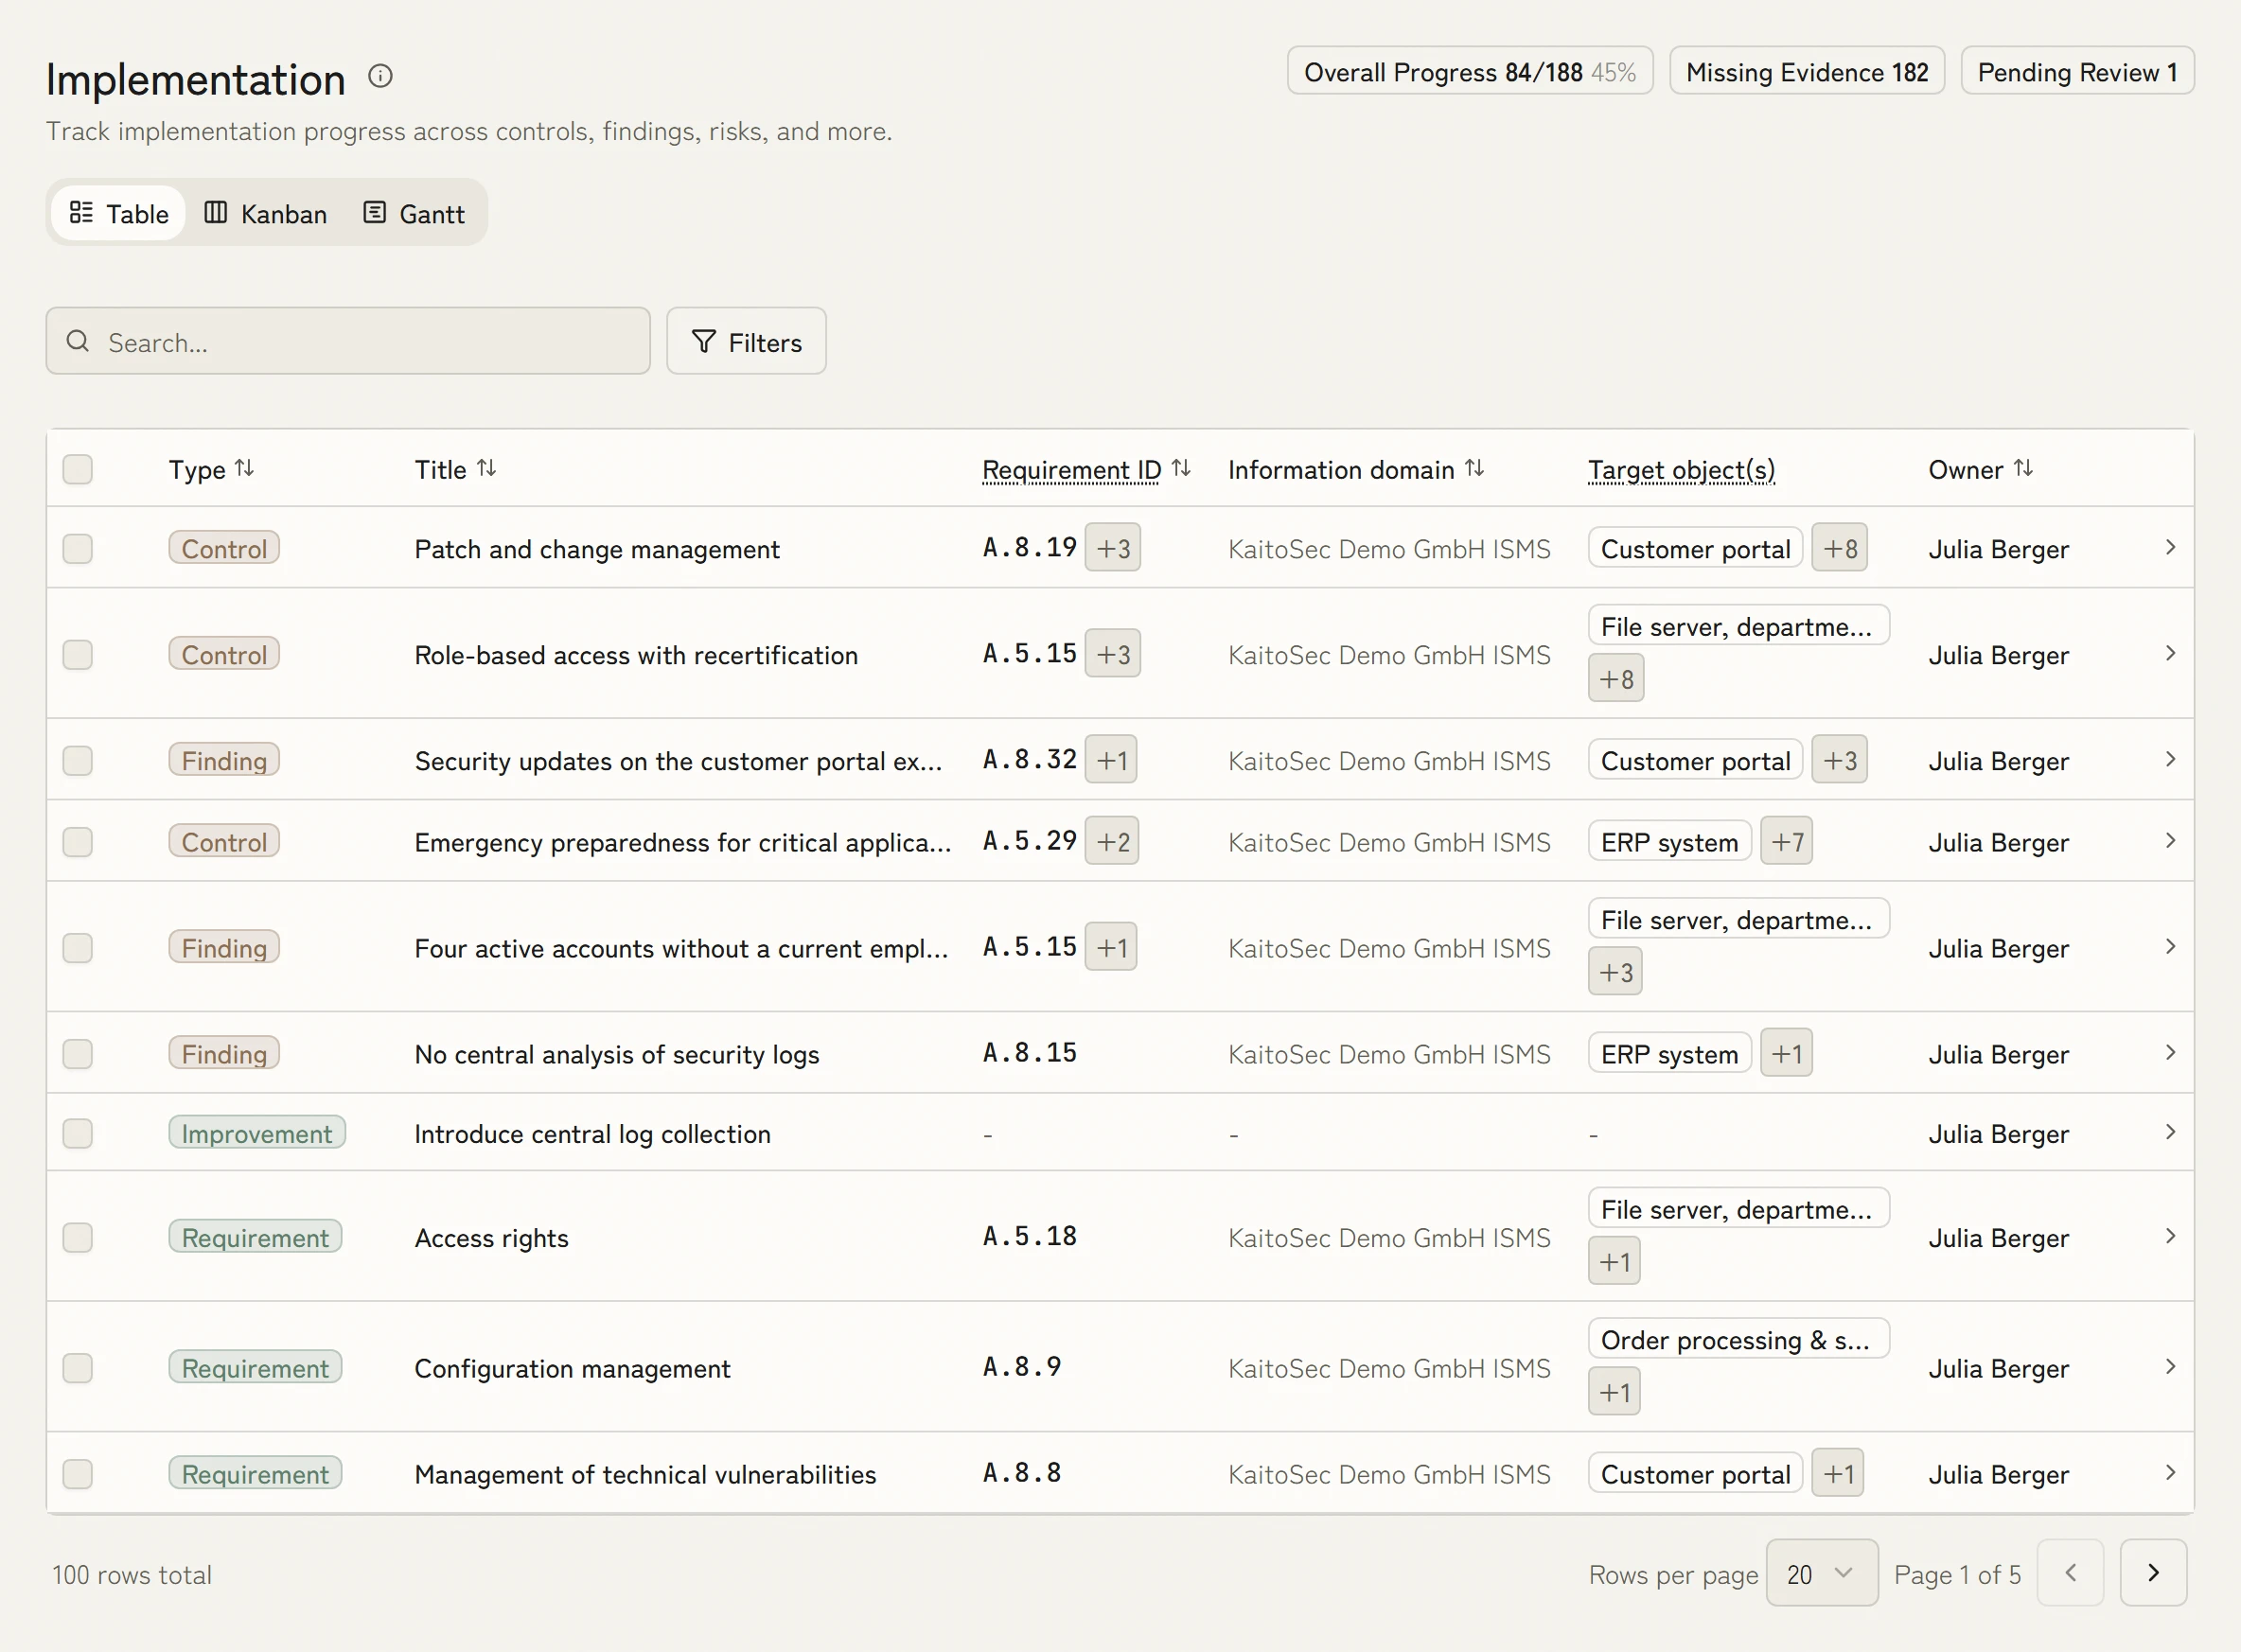
Evidence on the object it proves
For every criterion, the evidence sits on the object it proves: the encryption status of the laptops, an external test report on the TLS configuration. Confidentiality level and next review date come with it, so it is clear during the assessment what the audit provider may see.
1 packageENX-ready evidence package per assessment
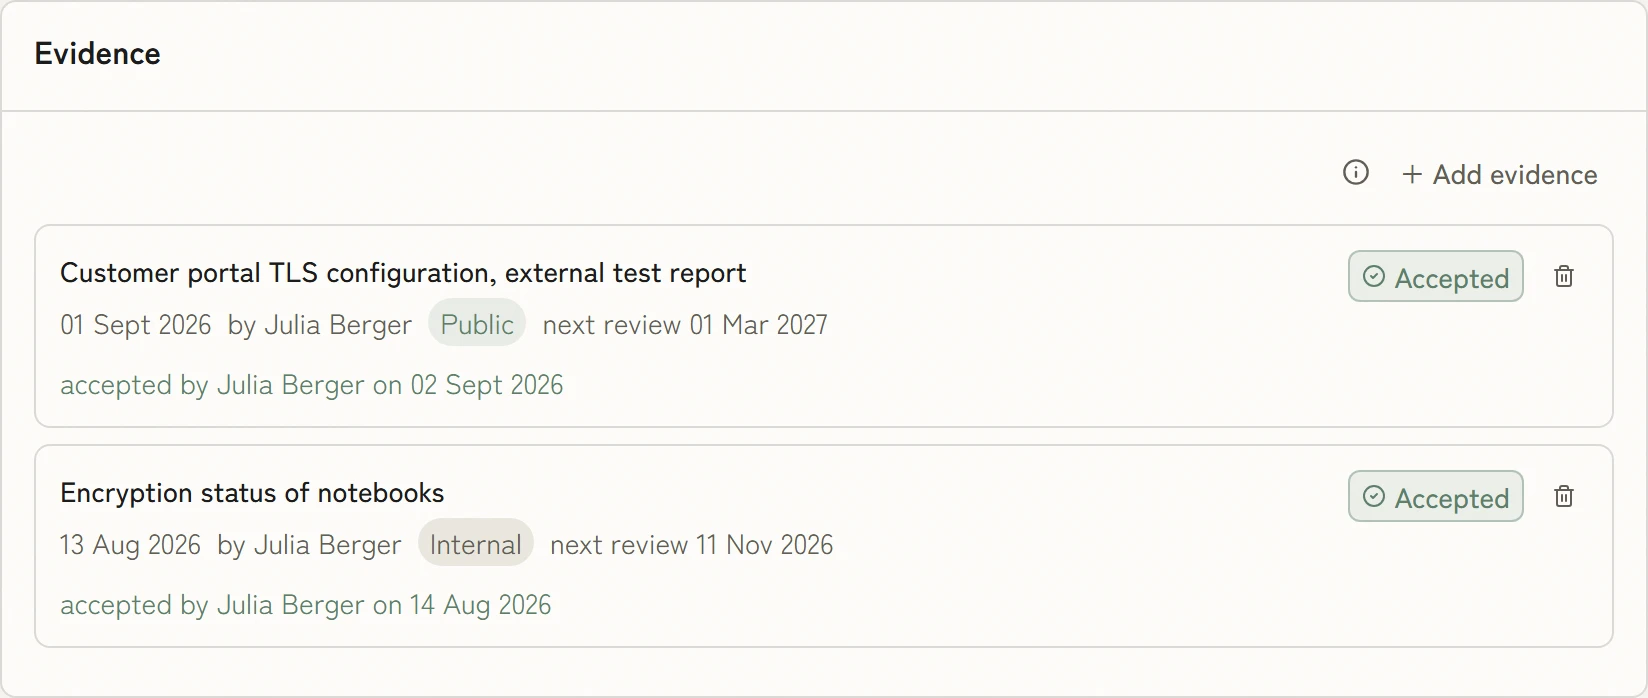
Maturity from interviews, not from self-declaration
Short interviews with the business record how a requirement is actually lived, with the accountable person, the source and the status. Maturity then comes from statements that hold up when the assessor repeats the question.
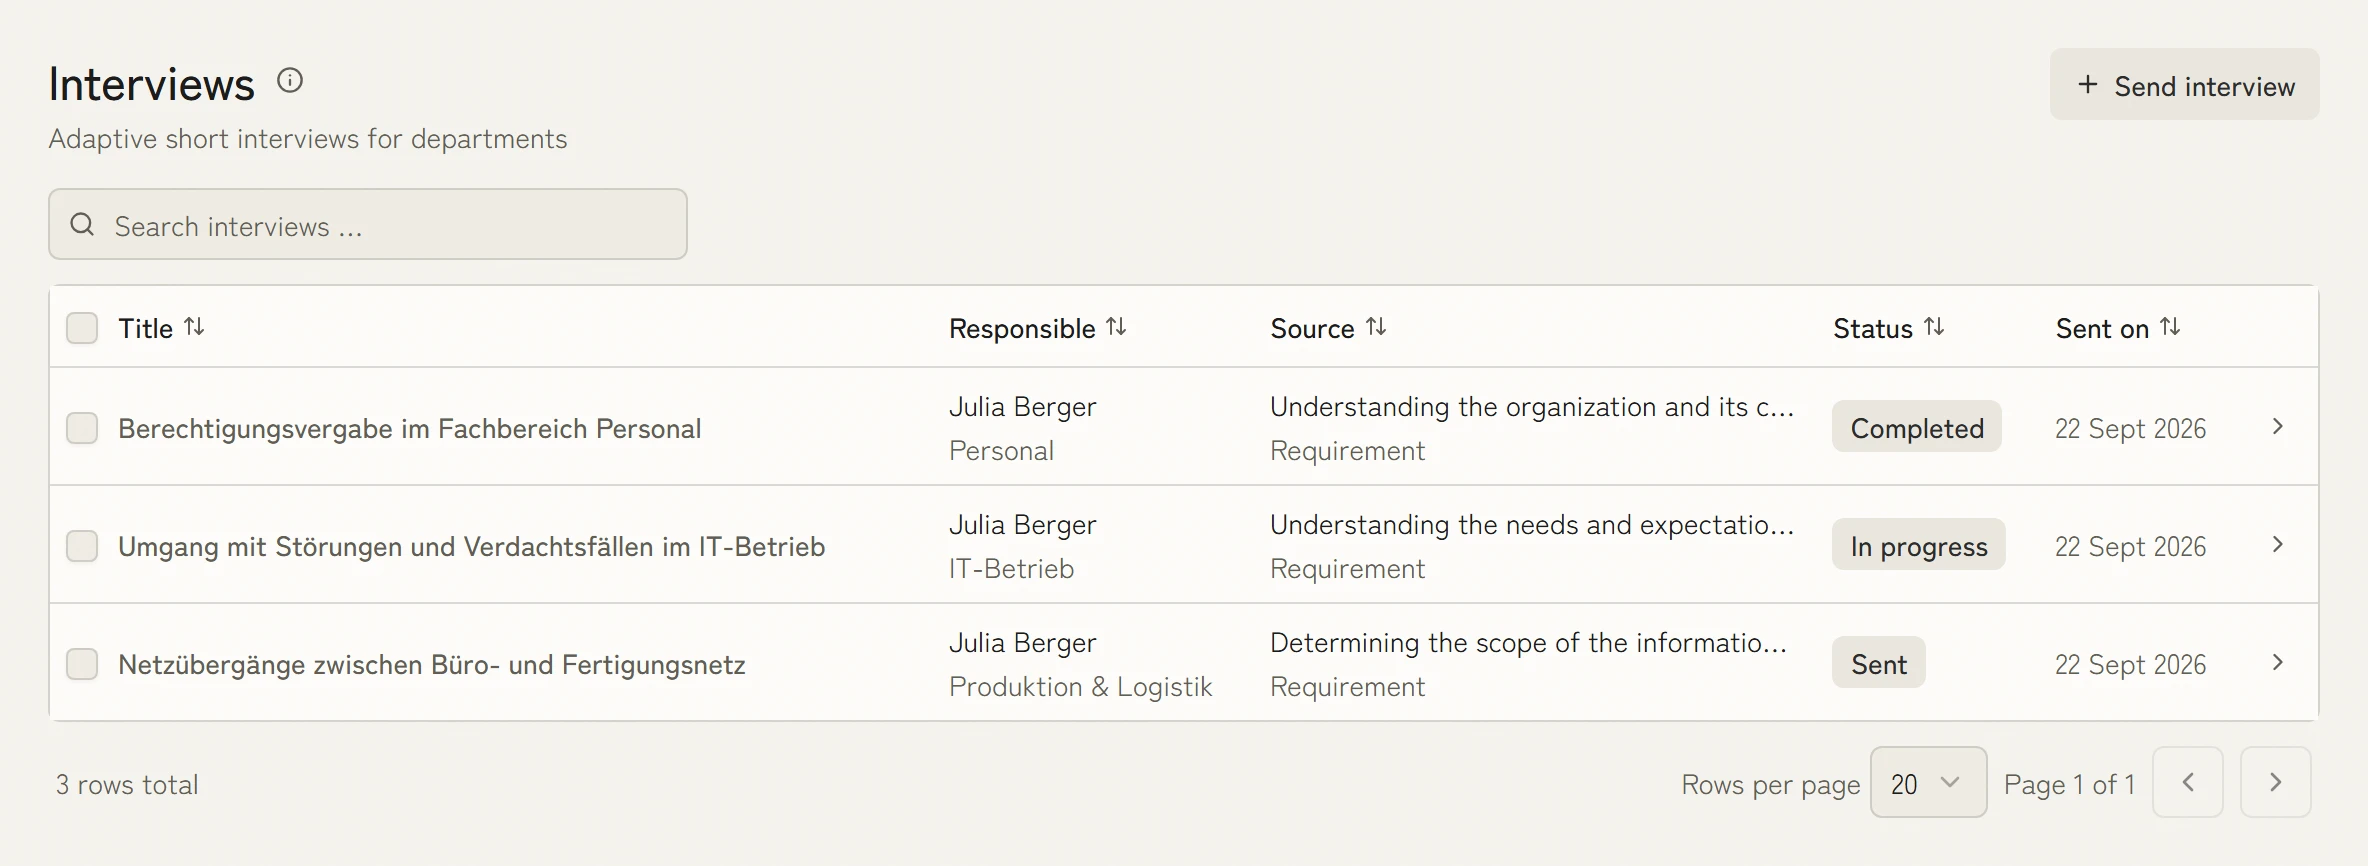
Prototype data needs its own protection level
Target objects carry type, unit, owner and protection level. For prototype and development data you set it high, and both assessment level and controls follow from that rather than applying flatly to the whole company.
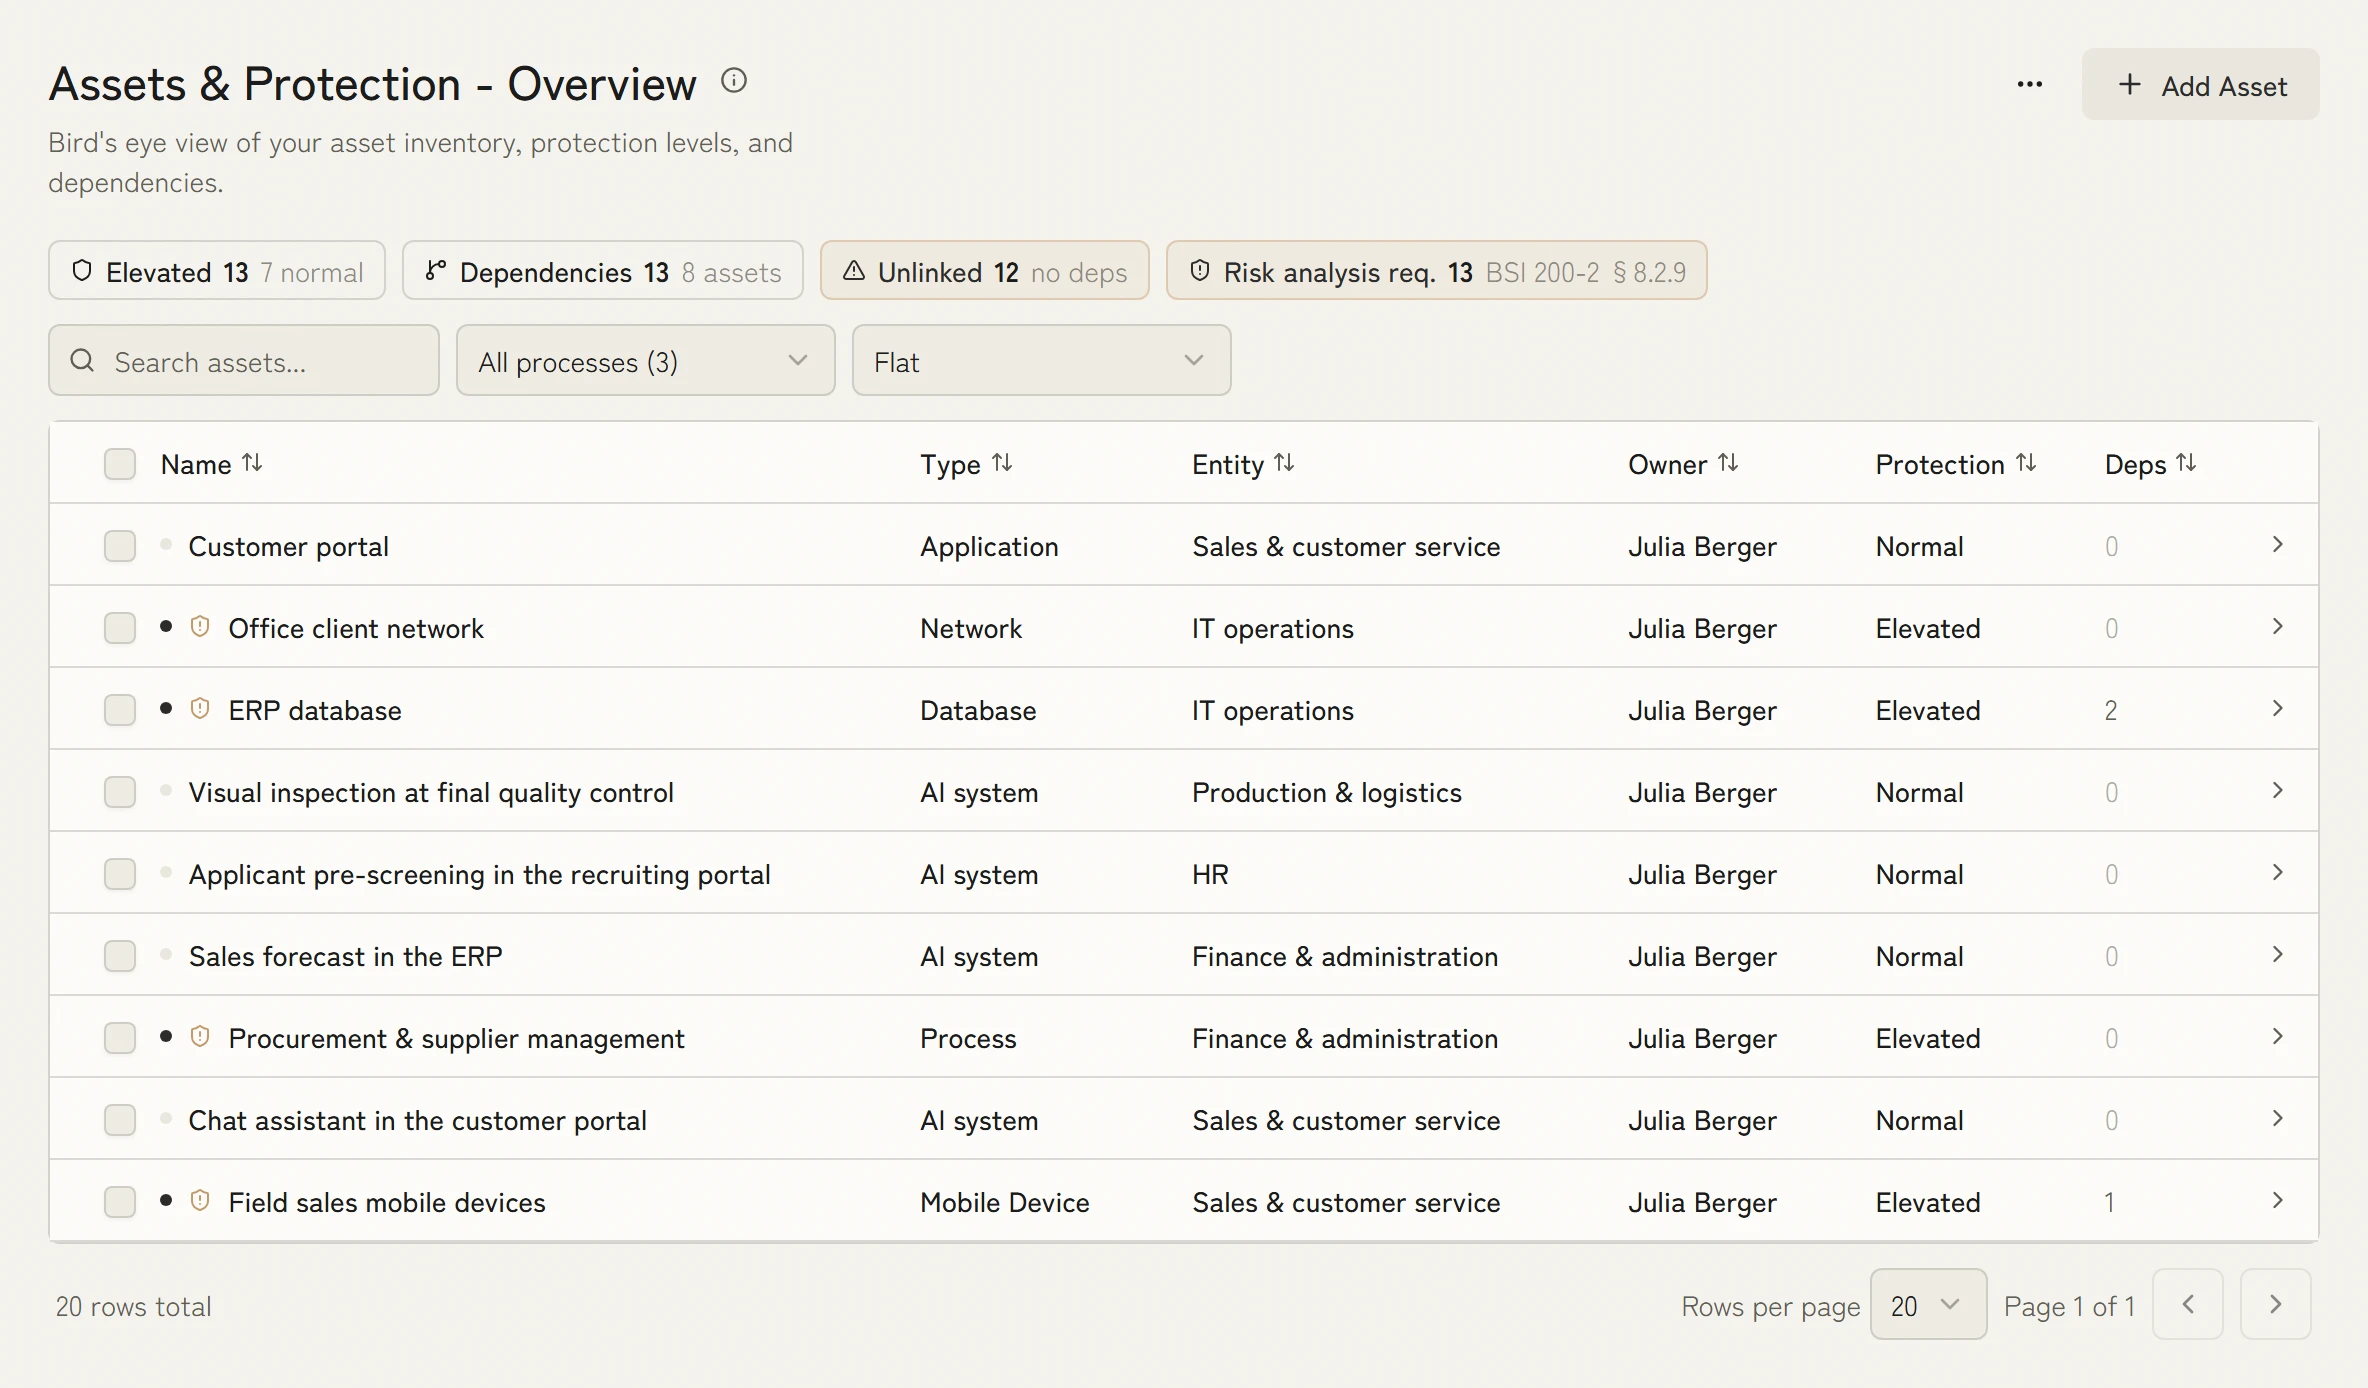
Build TISAX on the ISO 27001 baseline
The VDA ISA catalogue overlaps heavily with Annex A. If you already run ISO 27001, TISAX builds on the same set of controls and you only work through the additional requirements of the assessment level asked of you, instead of starting a second programme.
3 levelsAL1 self-assessment, AL2 remote, AL3 on-site
Connect TISAX with other standards
Put the TISAX work to use for the standards that examine the same substance.
TISAX by company and role
More for TISAX
Full VDA ISA catalogue coverage
KaitoSec ships with the complete VDA ISA (Information Security Assessment) catalogue structured as assignable criteria. Every criterion, including the additional requirements for high and very high protection needs, is linked to implementation guidance, so your team knows what is required and which evidence to collect.
Scope the right assessment level
TISAX defines three assessment levels: AL1 as self-assessment, AL2 with remote audit, AL3 with on-site audit for prototype data. KaitoSec helps determine which level your OEM customers require and limits the implementation work to that level, so no effort goes into a level nobody requires.
ENX portal readiness
The ENX Association portal is where TISAX results are registered and shared with OEM customers. KaitoSec prepares your evidence package in the format ENX-accredited audit providers expect and tracks submission status through the assessment.
Track maturity per ISA criterion
For each ISA criterion, KaitoSec tracks the current maturity level against the target maturity of 3 that the TISAX methodology sets for all criteria. Ahead of the assessment date you see which criteria are furthest from target.
Prototype and Development Data Controls
TISAX AL3 includes specific requirements for handling prototype data and development secrets. KaitoSec provides dedicated control sets for physical security, need-to-know access and securing R&D environments.
Manage sharing with OEM customers
Once your TISAX label is active on the ENX portal, KaitoSec keeps track of which OEM customers you have shared results with and which scope each release covers. You stay in control of who sees what.
What TISAX requires
TISAX assesses information security against the VDA ISA catalogue at three assessment levels: AL1 as a self-assessment, AL2 with a remote audit, AL3 on site for prototype data. The methodology sets target maturity 3 for every criterion, the label is valid for three years, and results are shared with OEM customers through the ENX portal.
Frequently asked questions about TISAX
What is TISAX and who needs it?
TISAX (Trusted Information Security Assessment Exchange) is an automotive industry information security assessment standard based on the VDA ISA catalogue. It is required by most major German OEMs and is increasingly demanded by Tier 1 suppliers. Any company in the automotive supply chain that handles sensitive OEM data, prototype information, or critical development assets is likely to need a TISAX label.
How does TISAX differ from ISO 27001?
TISAX is specifically designed for the automotive supply chain and focuses on protection of vehicle data, prototype data, and supplier relationships. ISO 27001 is a general ISMS standard applicable to any sector. TISAX builds on ISO 27001 concepts but has sector-specific requirements. Results are shared exclusively through the ENX portal; there is no public certificate as with ISO 27001. See the TISAX glossary entry for the assessment-level structure and ENX portal role.
Which assessment level do we need?
Assessment level depends on the sensitivity of the data you handle for OEM customers. AL1 covers normal information protection and is a self-assessment only; it does not lead to a TISAX label, which starts at AL2. AL2 is required for high protection needs and involves remote audit by an ENX-accredited audit provider. AL3 covers very high protection needs, such as prototype data, and requires on-site audit. Your OEM customer will specify the required level in the contract.
How long is a TISAX label valid?
TISAX labels are valid for three years from the date of the assessment. KaitoSec tracks your label expiry and sends reminders well in advance, so reassessment preparation starts early enough and no gap opens in your supplier qualification.
Can KaitoSec map TISAX controls to ISO 27001?
Yes. KaitoSec maintains a cross-mapping between VDA ISA criteria and ISO 27001:2022 Annex A controls. If your organisation pursues a TISAX label and an ISO 27001 certificate, evidence and implementations are reused across both frameworks. That saves duplicate work.

Your TISAX plan in thirty minutes.
In the demo we settle the assessment level asked of you, the scope and the evidence. You leave knowing what is due before the assessment date.