
We are building the integrated management system we could never buy.
We want compliance to take less work and resilience to be part of everyday work, not a project before the audit. That is why KaitoSec brings information security, business continuity, data protection and AI governance into one data model that a small team can maintain.
The team behind KaitoSec

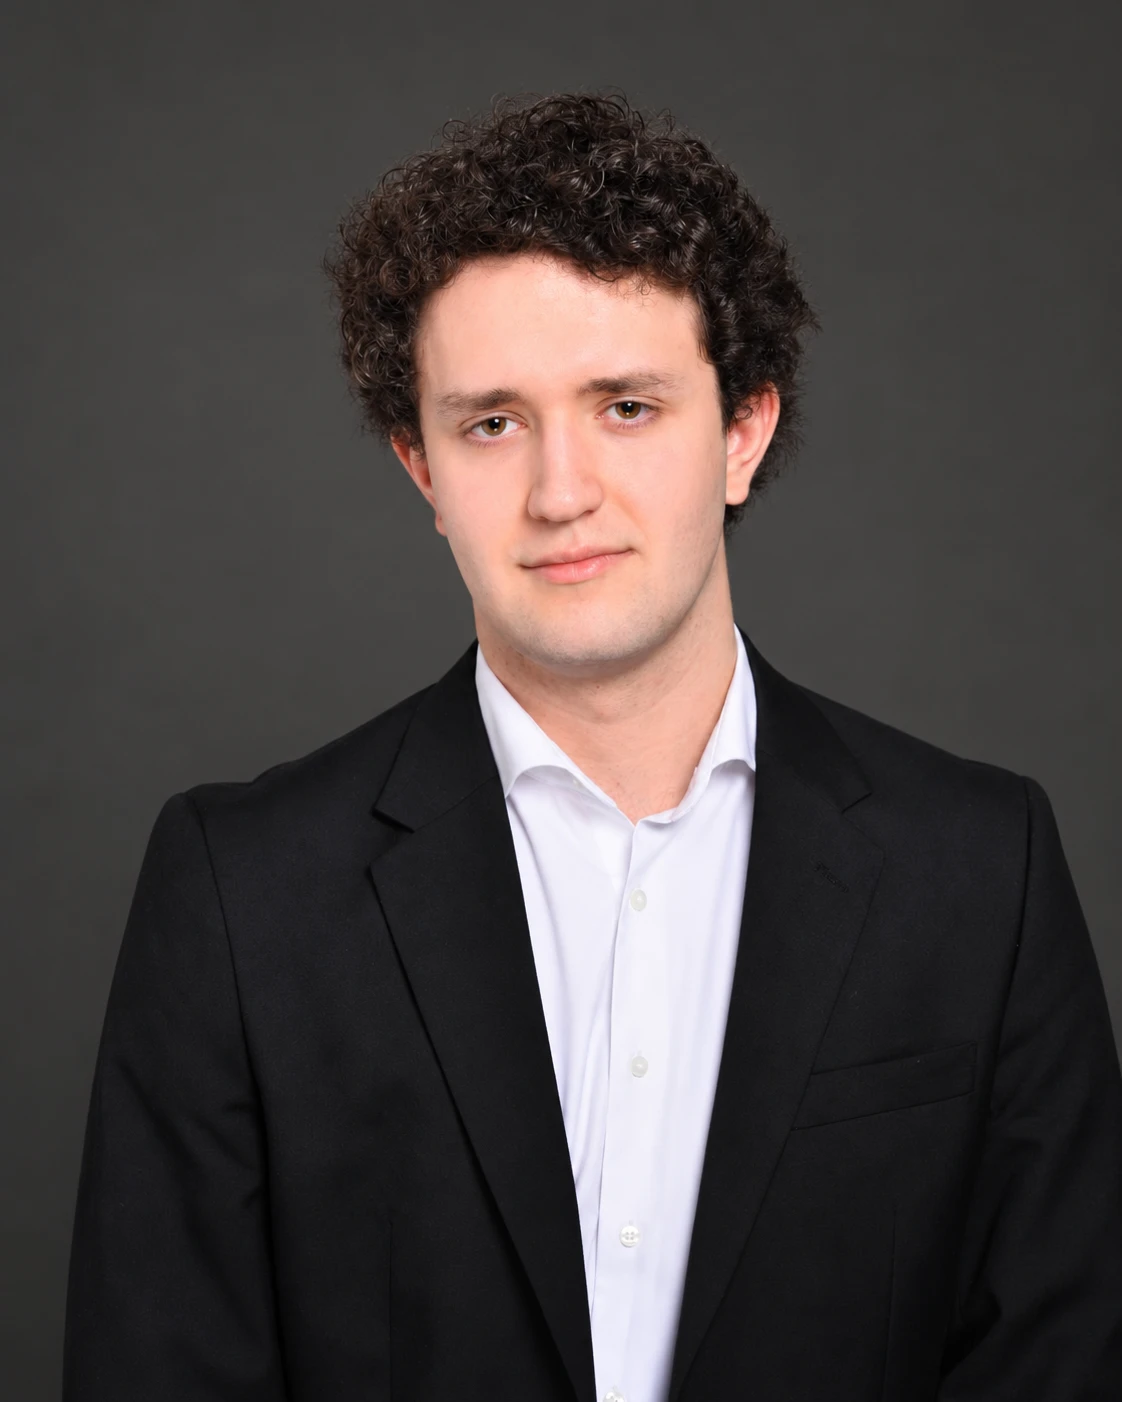
Chris Müller
Co-Founder & CEO
Ex-Big4. Ten years ISMS and BCMS, public sector and regulated industries.
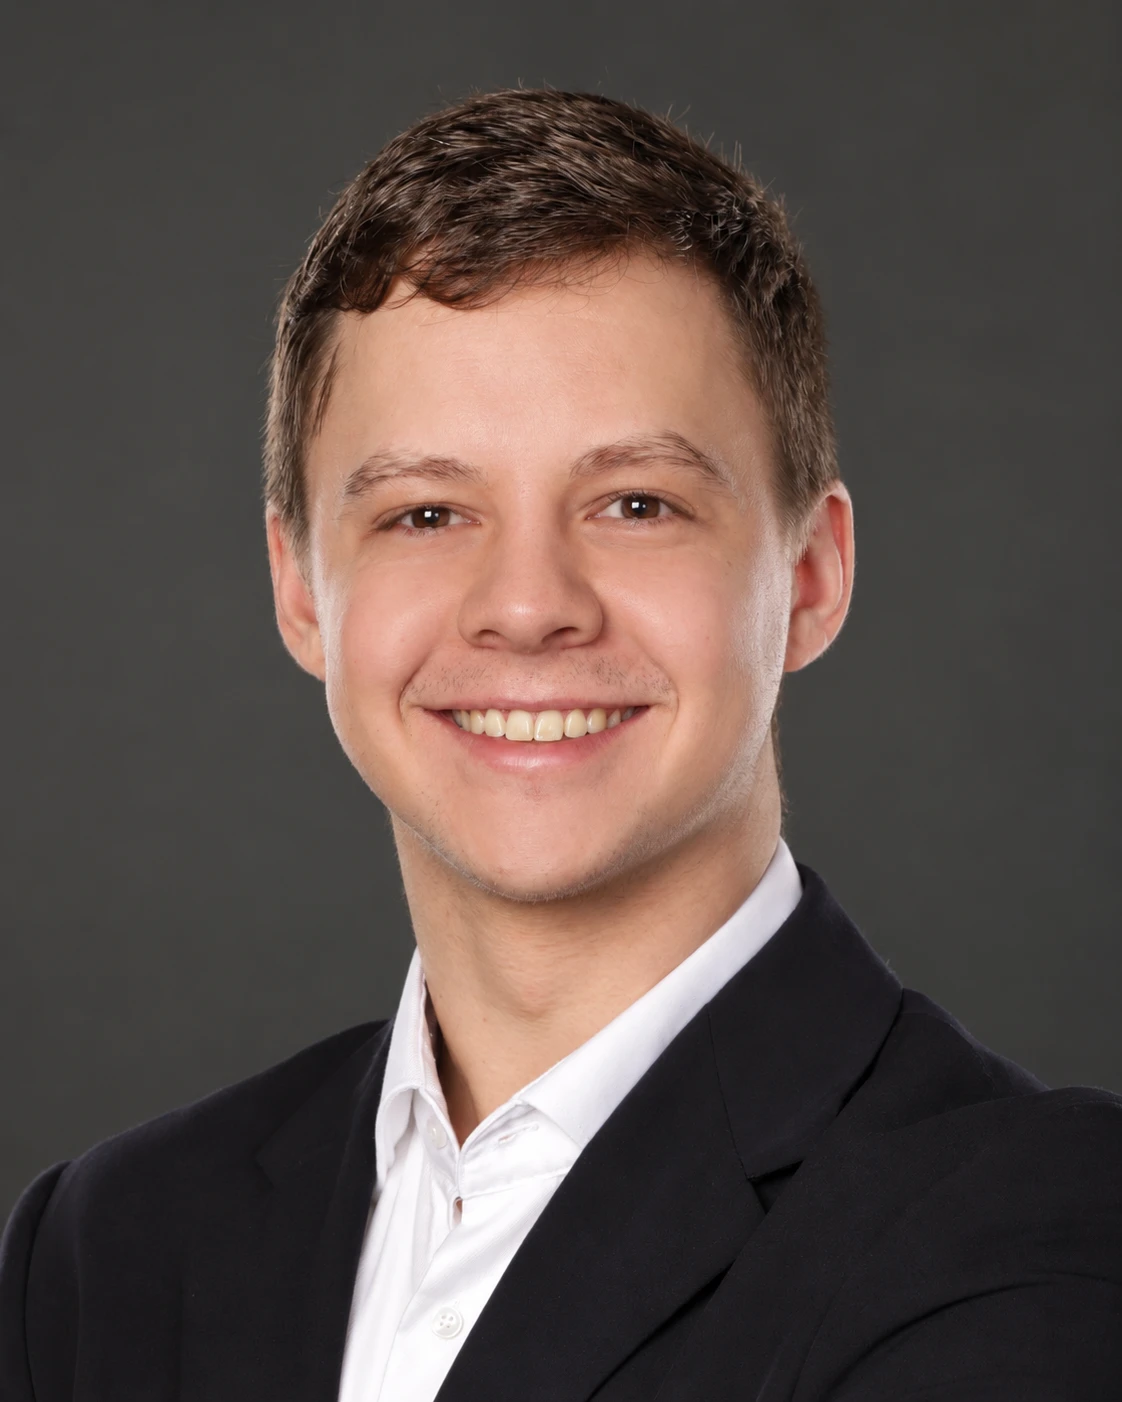
Marcel Siegert
Head of AI
Ex-Big4: cyber security and due diligence. Computer science master's from KIT.
Chukwuka Ezerioha
Head of Engineering
Full-stack, DevOps, security. Angular and React. 42 Berlin.
Elias Nassall
Co-Founder
Ex-Big4. Business Continuity Manager KRITIS. Five years of resilience, BCMS and ISMS.
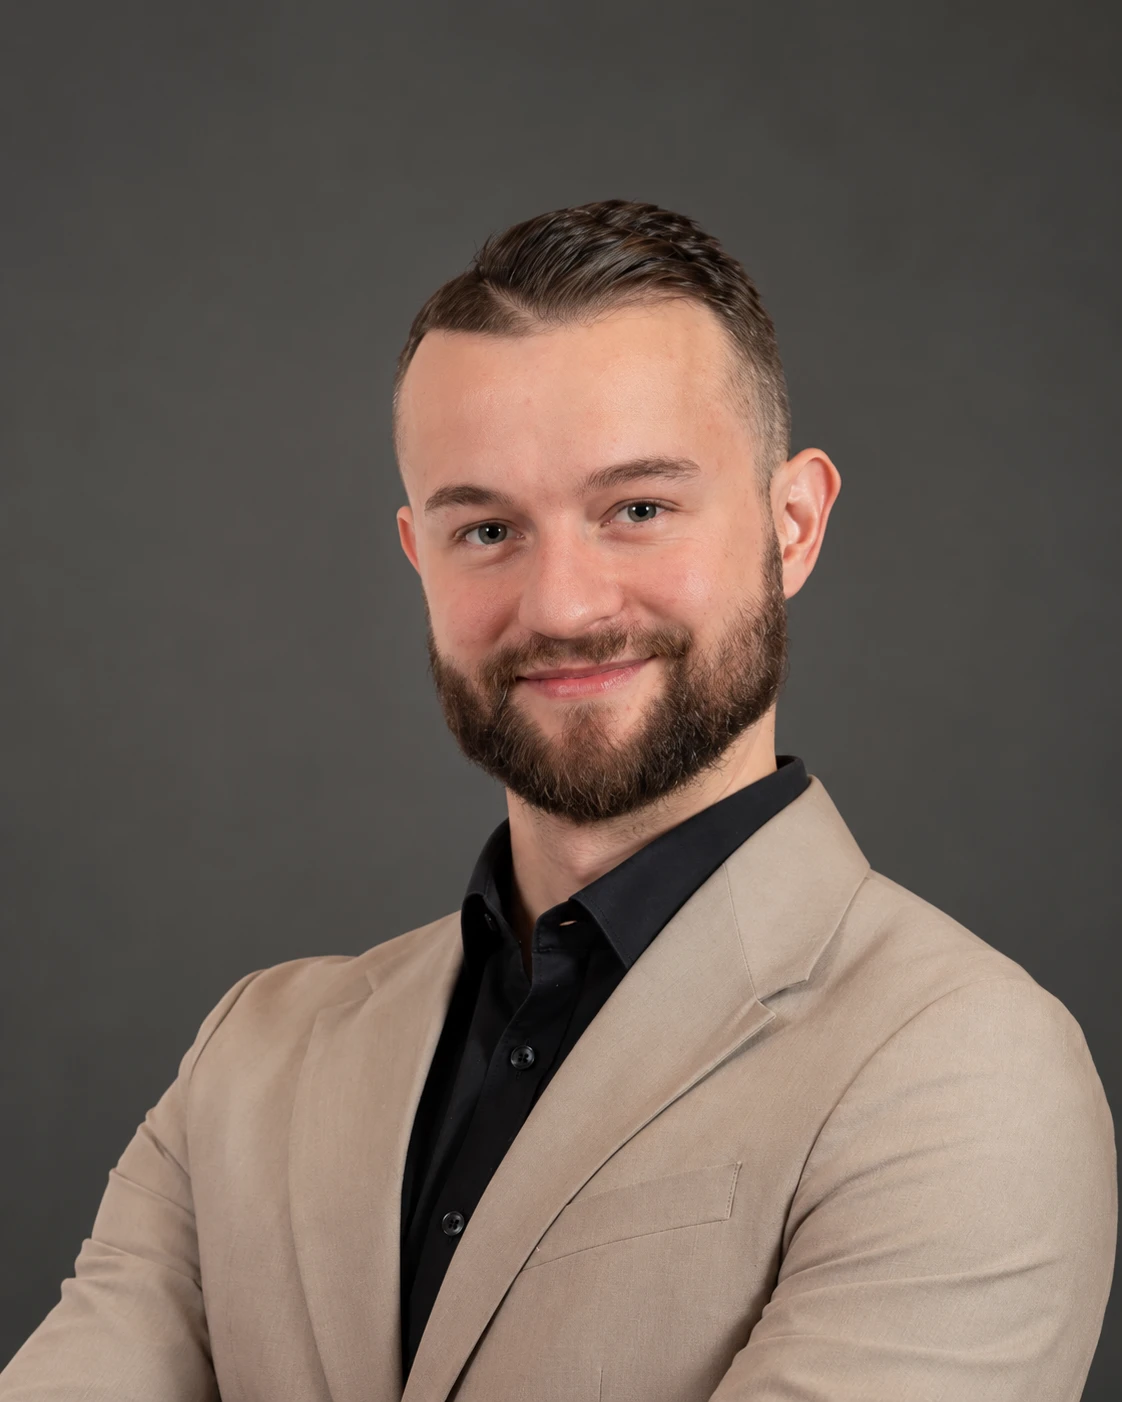
Felix Hosse
Sales
Blockchain founder, resilience enthusiast.
Zakaria Belehri
Sales
ESMT Berlin, M.Sc. analytics and AI. SQL, Python, Tableau.
Why KaitoSec exists
“With KaitoSec we democratise cybersecurity by turning expert knowledge into knowledge the whole organisation can act on.”
We come from consulting: we built and ran ISMS, BCMS and DSMS programmes there ourselves and supported AIMS work under the EU AI Act. Scarce expert time kept disappearing into separate registers, duplicate mappings and reconstructed evidence.
KaitoSec is built for security owners and public organisations carrying real regulatory responsibility without an enterprise-sized team. The platform makes relationships and next actions visible; it does not take the professional decision away.
To us, compliance evidence is a byproduct of working resilience, not its purpose. An audit should document what is already lived practice instead of producing a parallel world of documents once a year.
- Founded
- 2026 in Berlin
- Hosting
- ISO 27001-certified in Germany
What we hold to
Clarity
We explain what a requirement asks and why. Whoever has to implement something should understand it without calling a consultant.
Ownership
Every approval carries a name. The platform prepares the work; people decide and stand behind it.
Pragmatism
What does not hold up in daily work does not hold up in the audit either. We measure every feature by whether it makes the daily work easier.
Sharing knowledge
Expert knowledge should not stay in a few heads. We turn it into organisational knowledge a whole team can use.

Meet us in thirty minutes.
Bring one current register, missing piece of evidence or recurring report. We'll use it to show you how much of that work KaitoSec takes off your team.