
ISO 22301: emergency plans from data your ISMS already has.
BIA, recovery strategies, emergency plans, exercises and management review use the same processes, assets and owners as your ISMS. You record nothing twice and go into the audit with a documented exercise history.

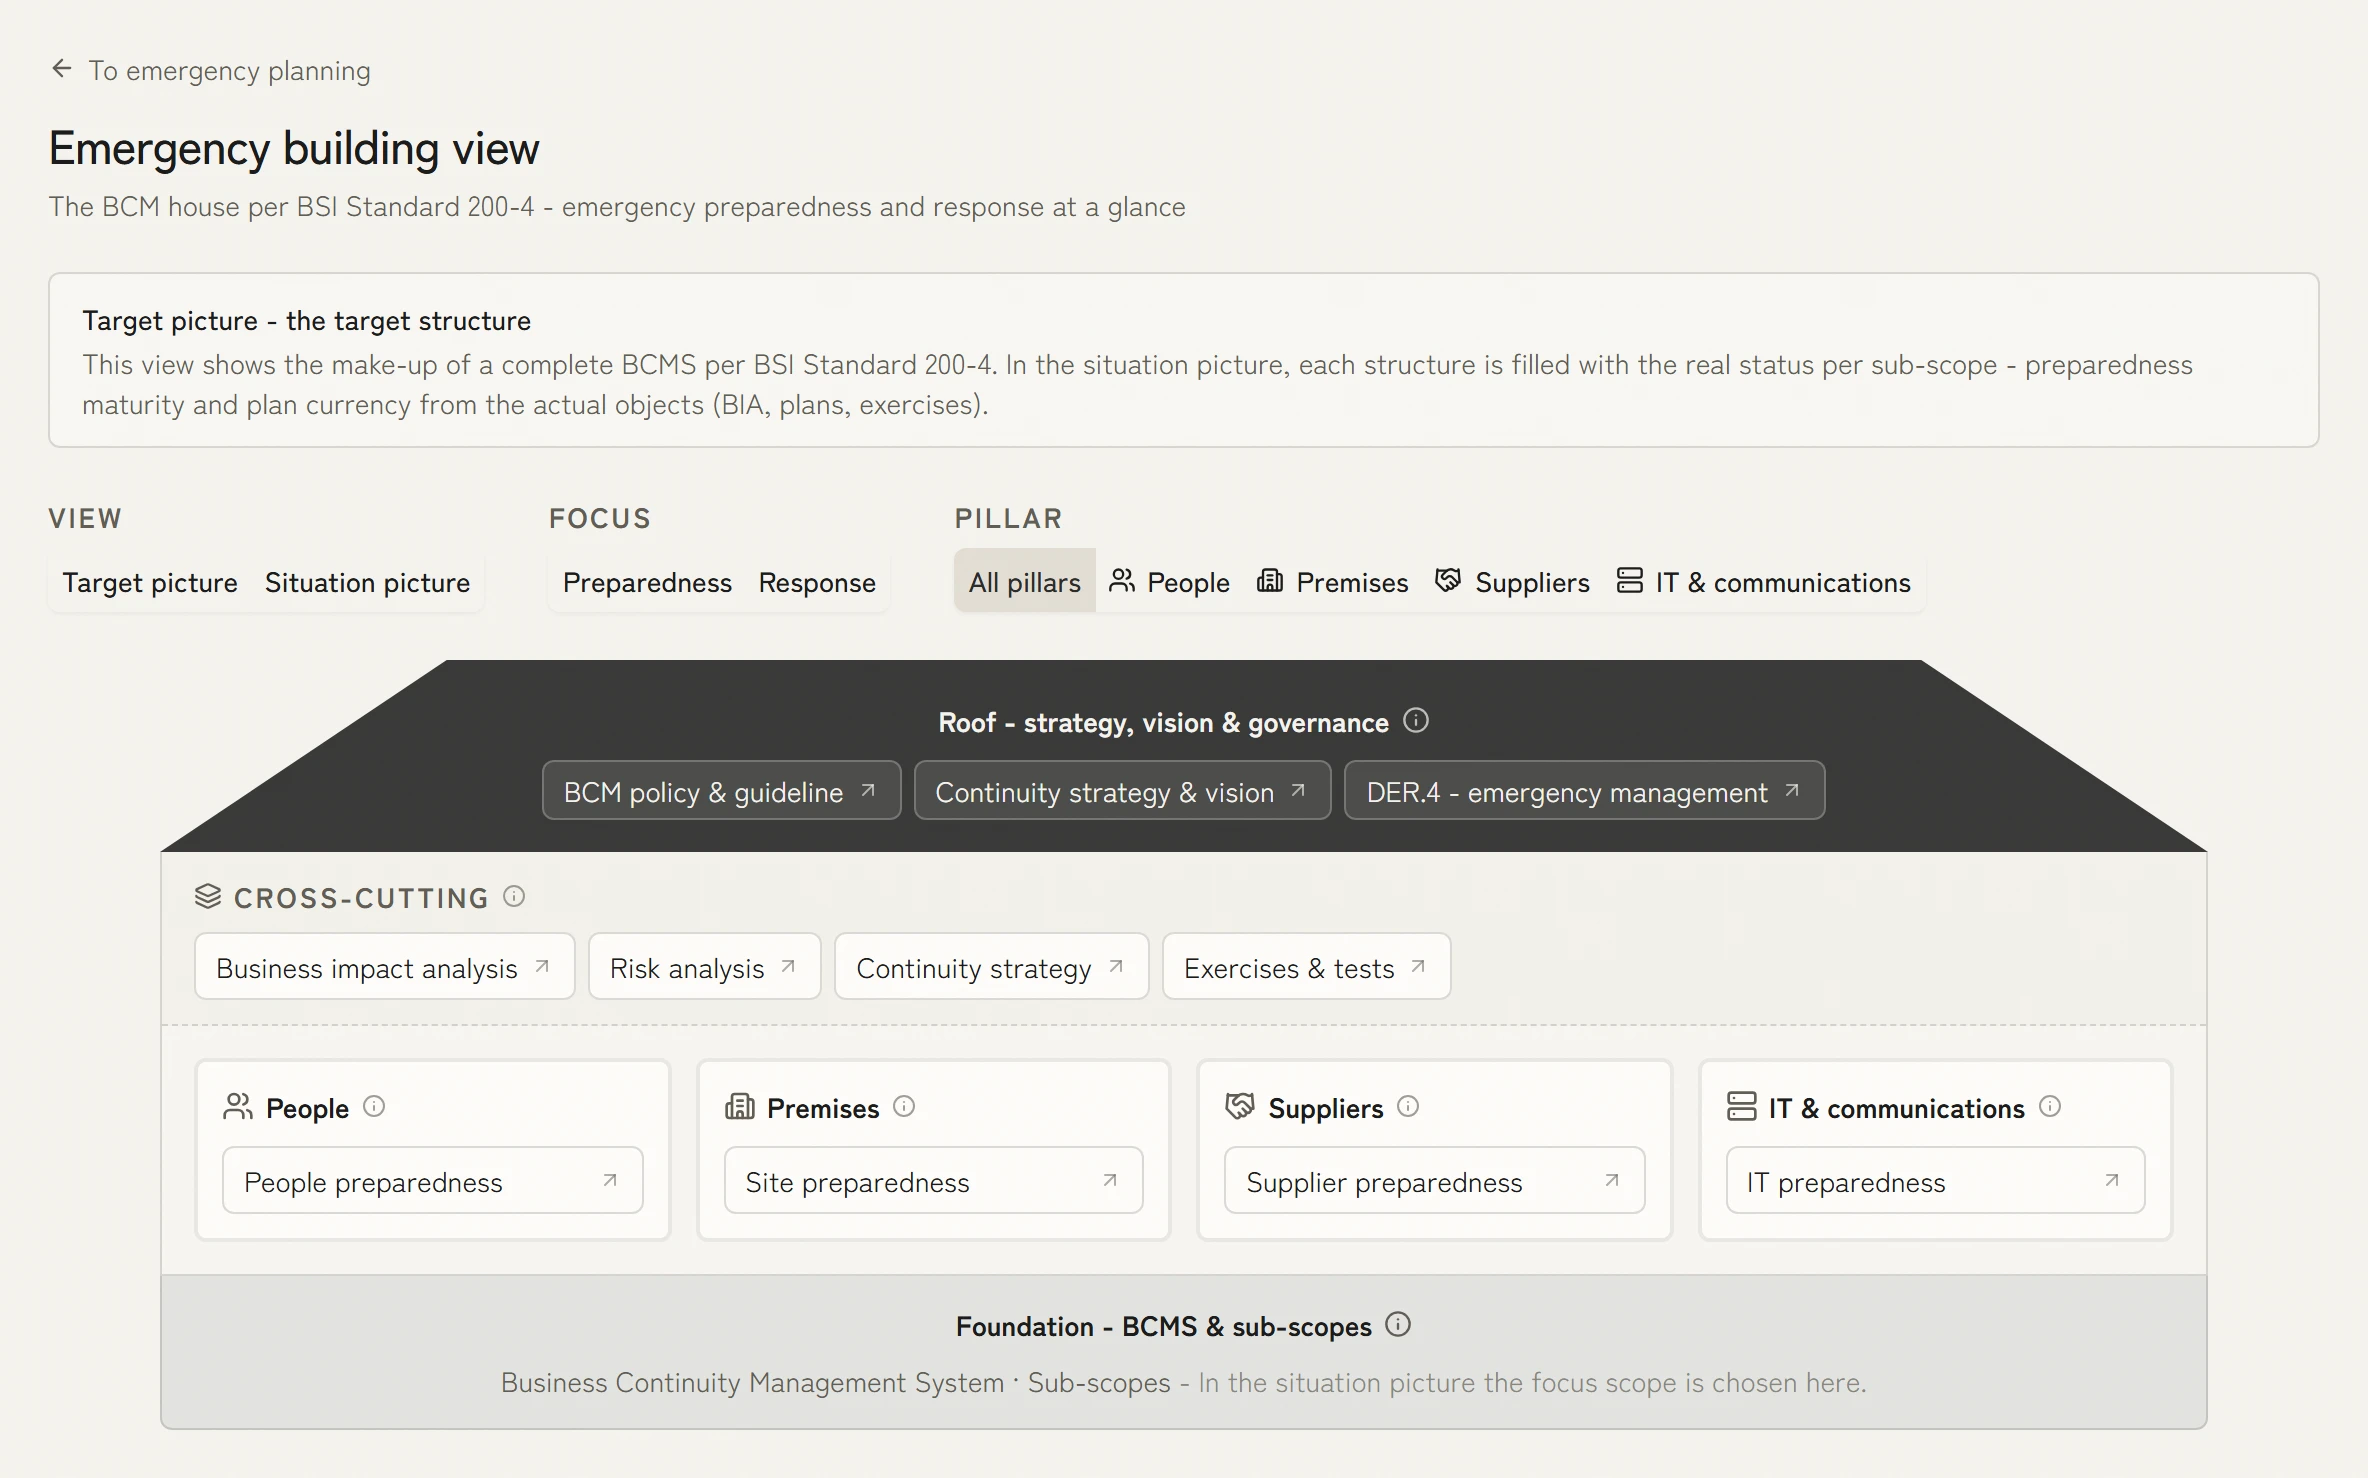


 5.0 out of 5
The BIA produces MTPD, RTO and RPO
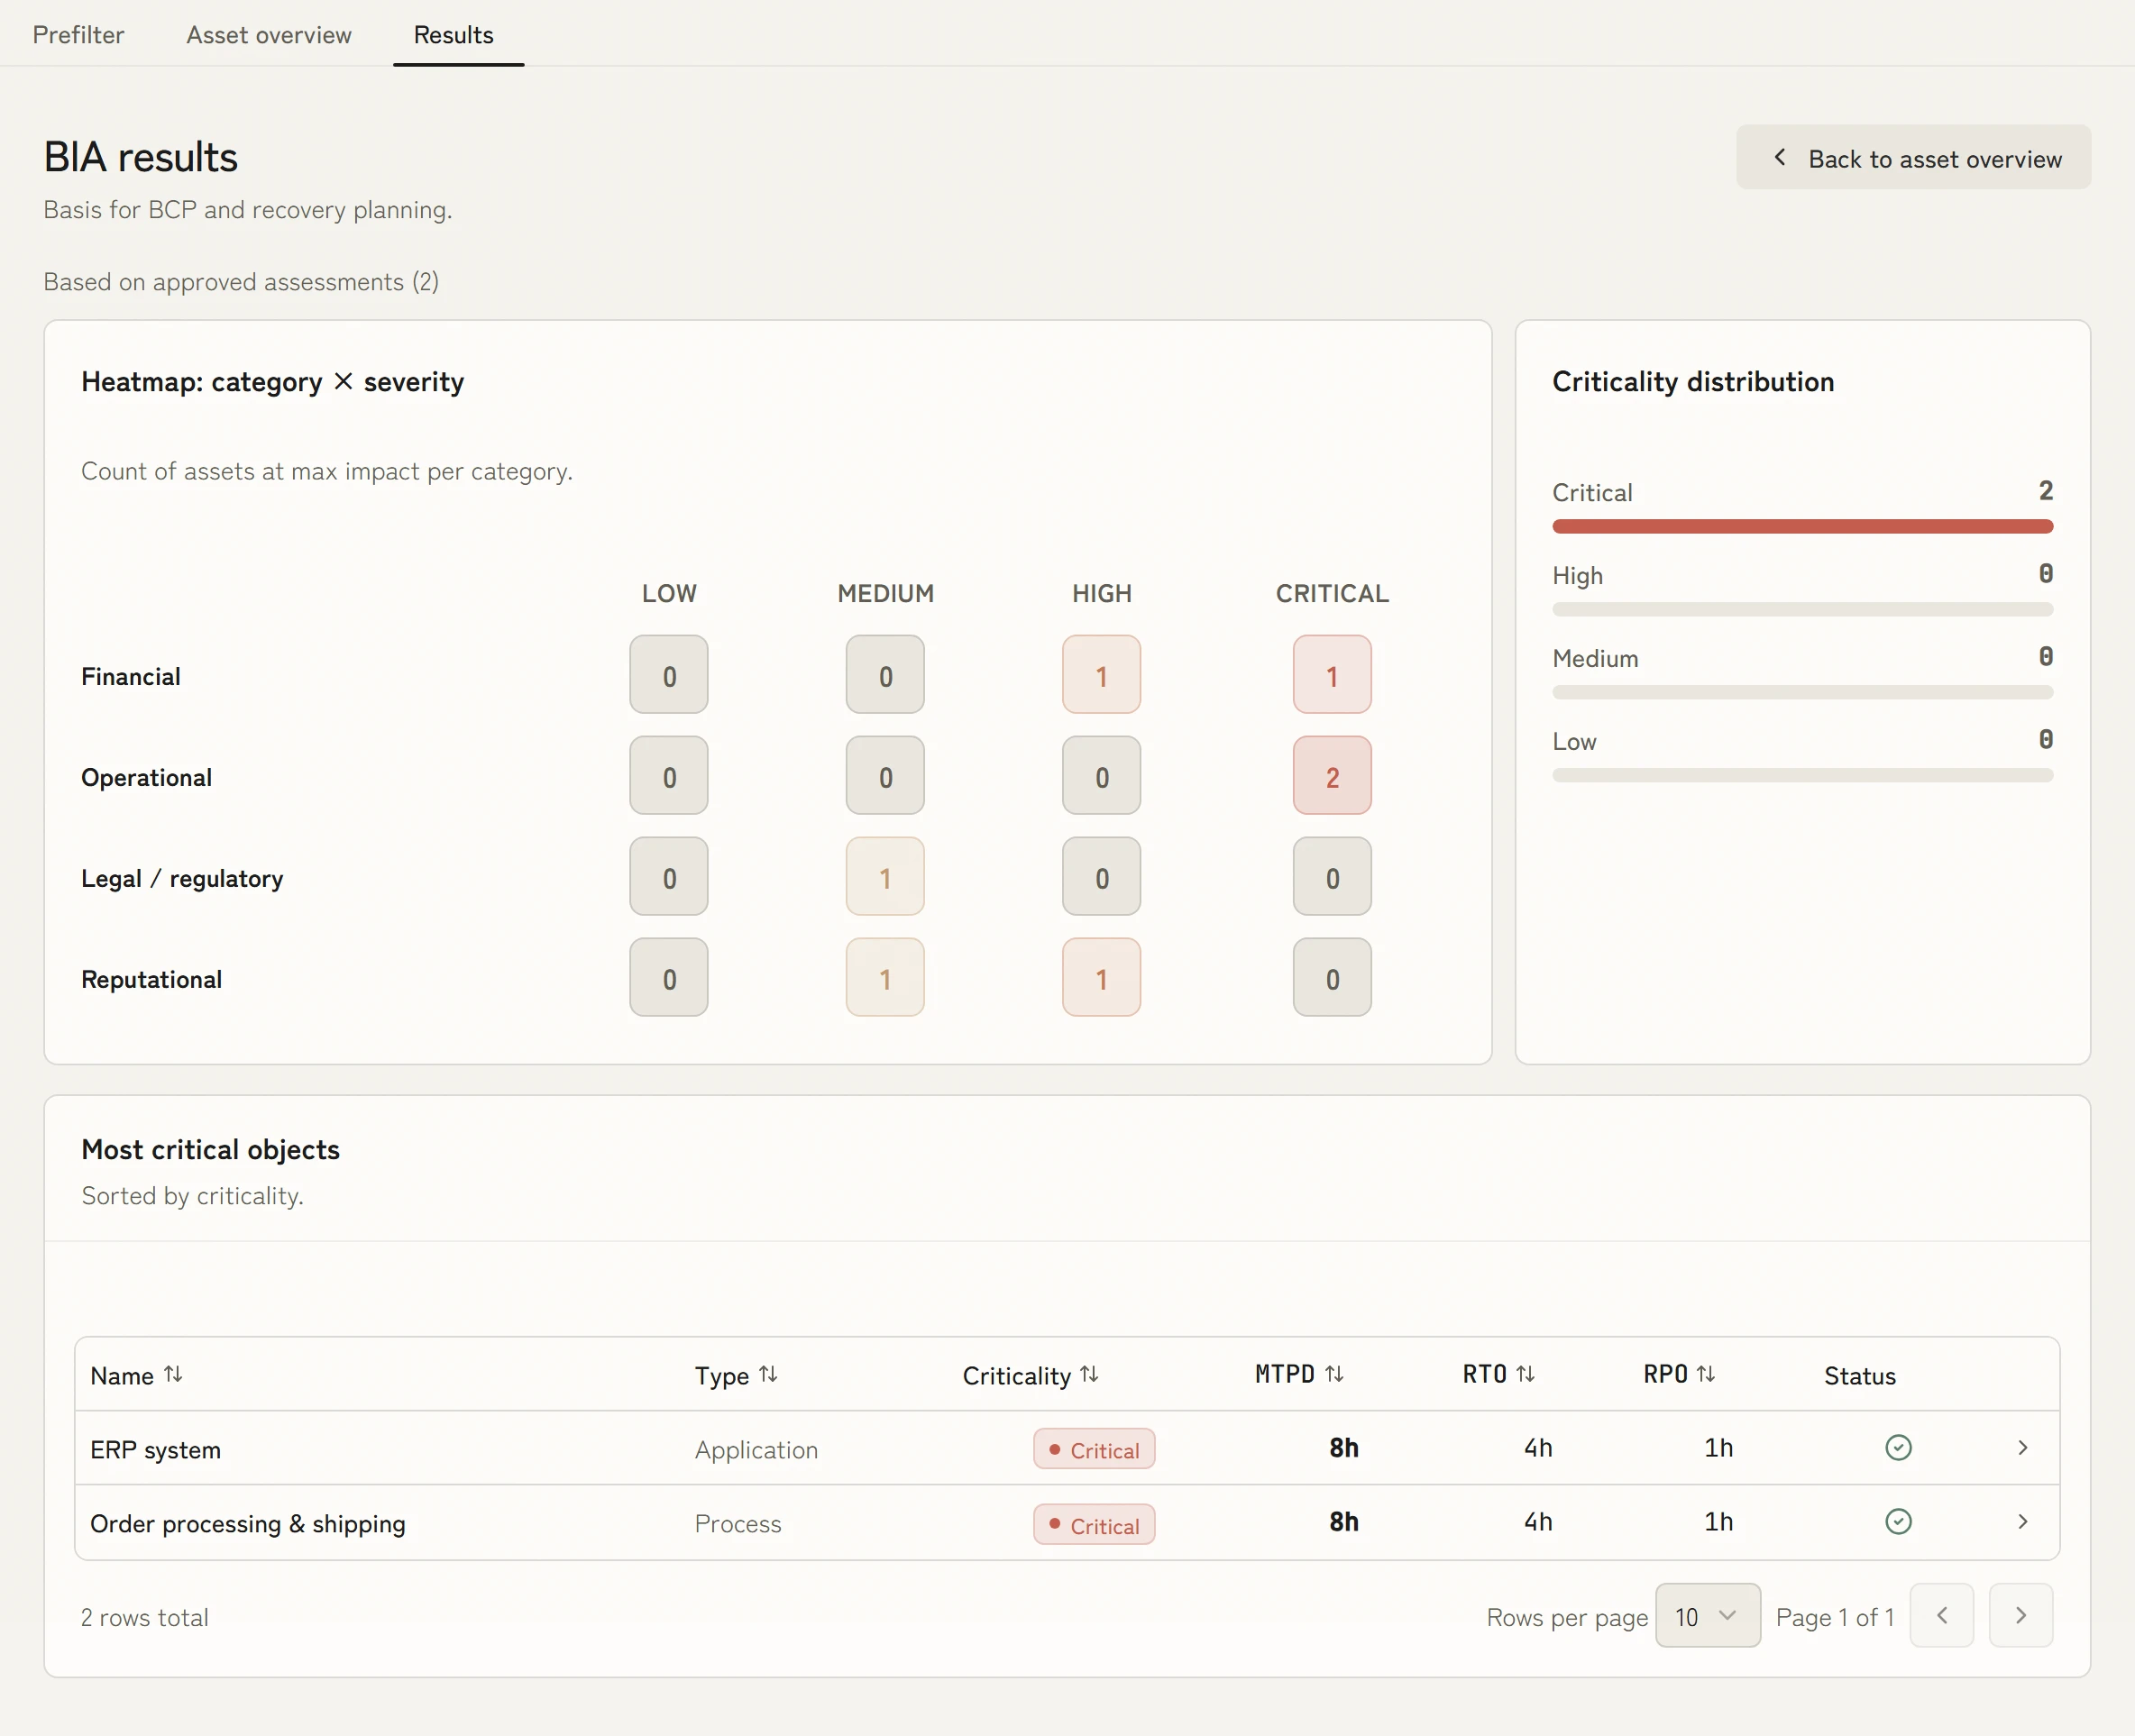
You run the business impact analysis on the same processes and target objects the ISMS already knows. The results produce criticality, MTPD, RTO and RPO, and those same figures then carry strategies, plans and exercises. Clause 8.2 asks for a business impact analysis and a risk assessment; in KaitoSec both run on the same object instead of in two separate spreadsheets.
1 BIAThe BIA feeds strategies, plans and exercises
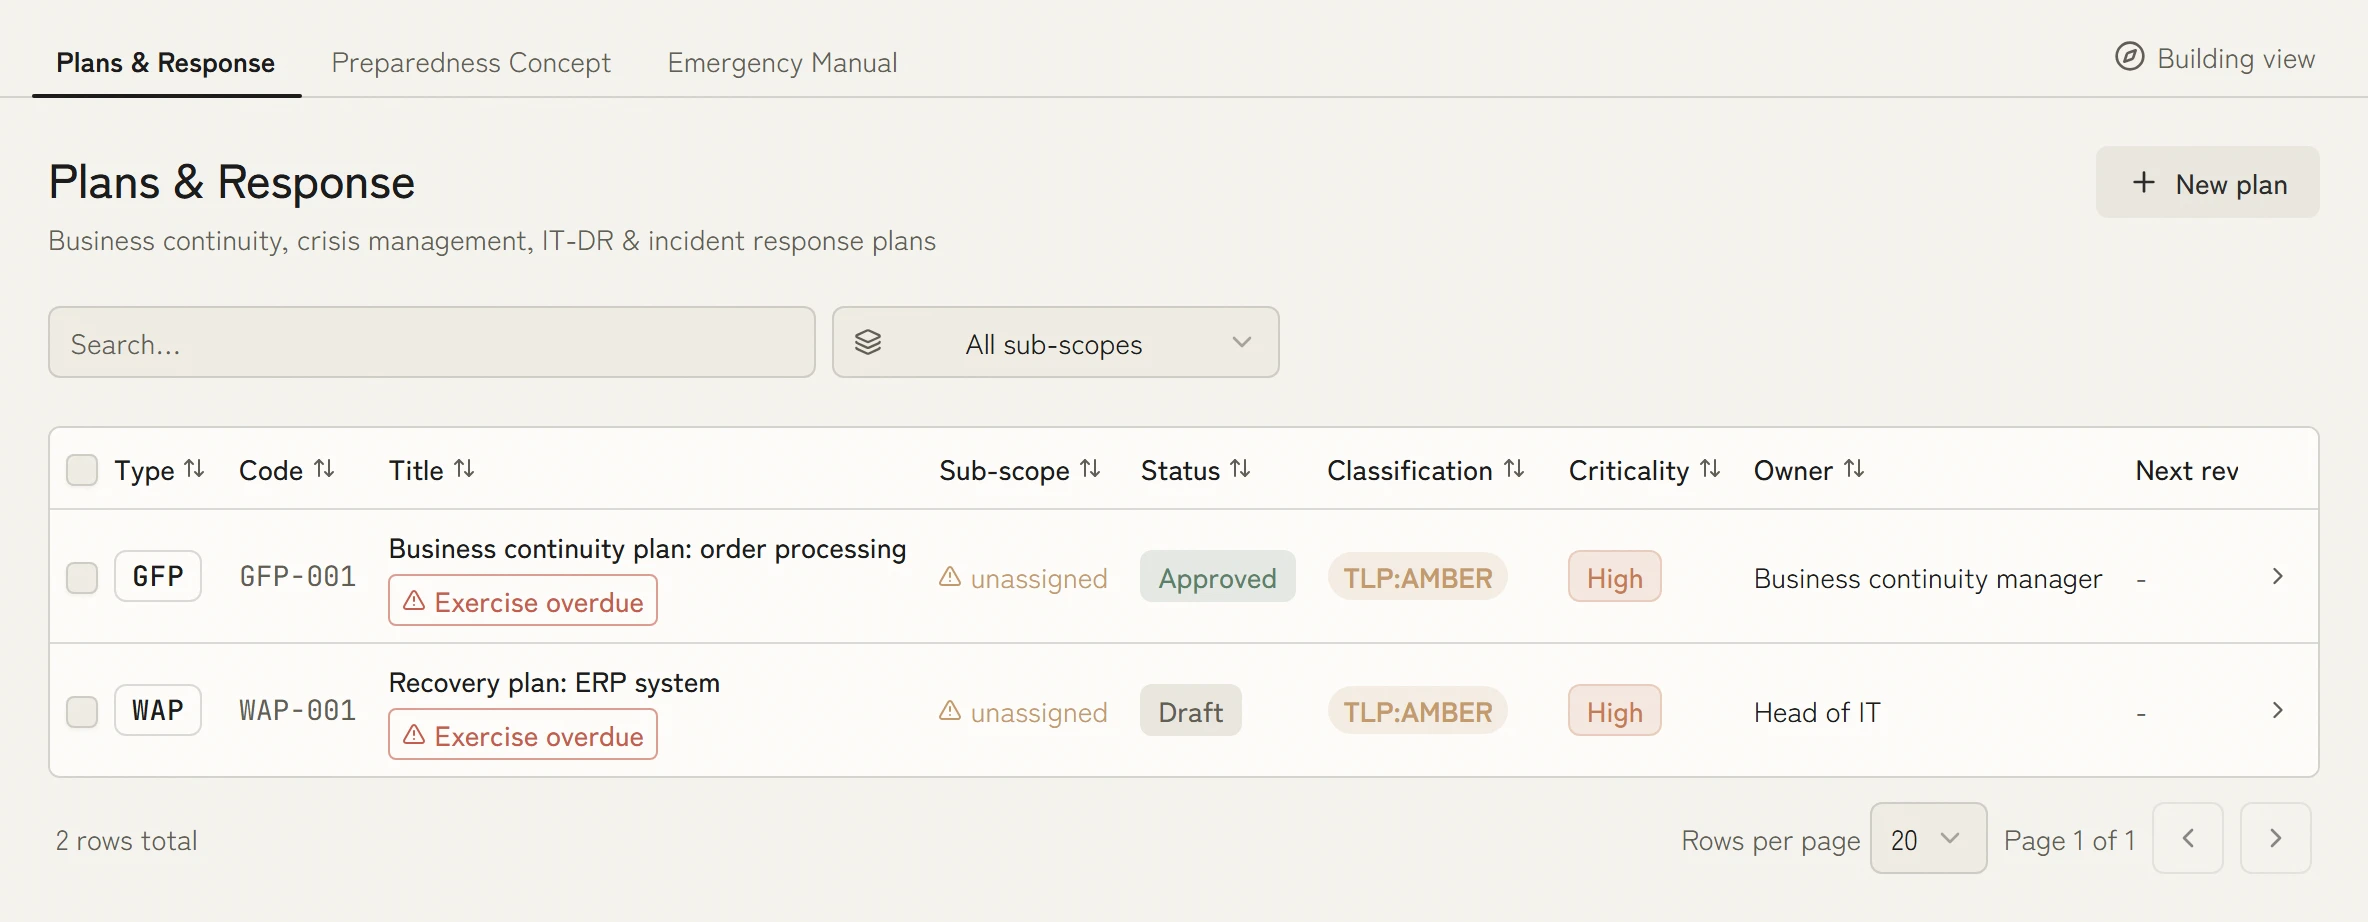
Continuity plans with version and approval
Business continuity and recovery plans hold roles, activation, communication and decision authority. Versioning, approval and acknowledgement run in the same workflow as policies, and a plan flags itself when its exercise is overdue.
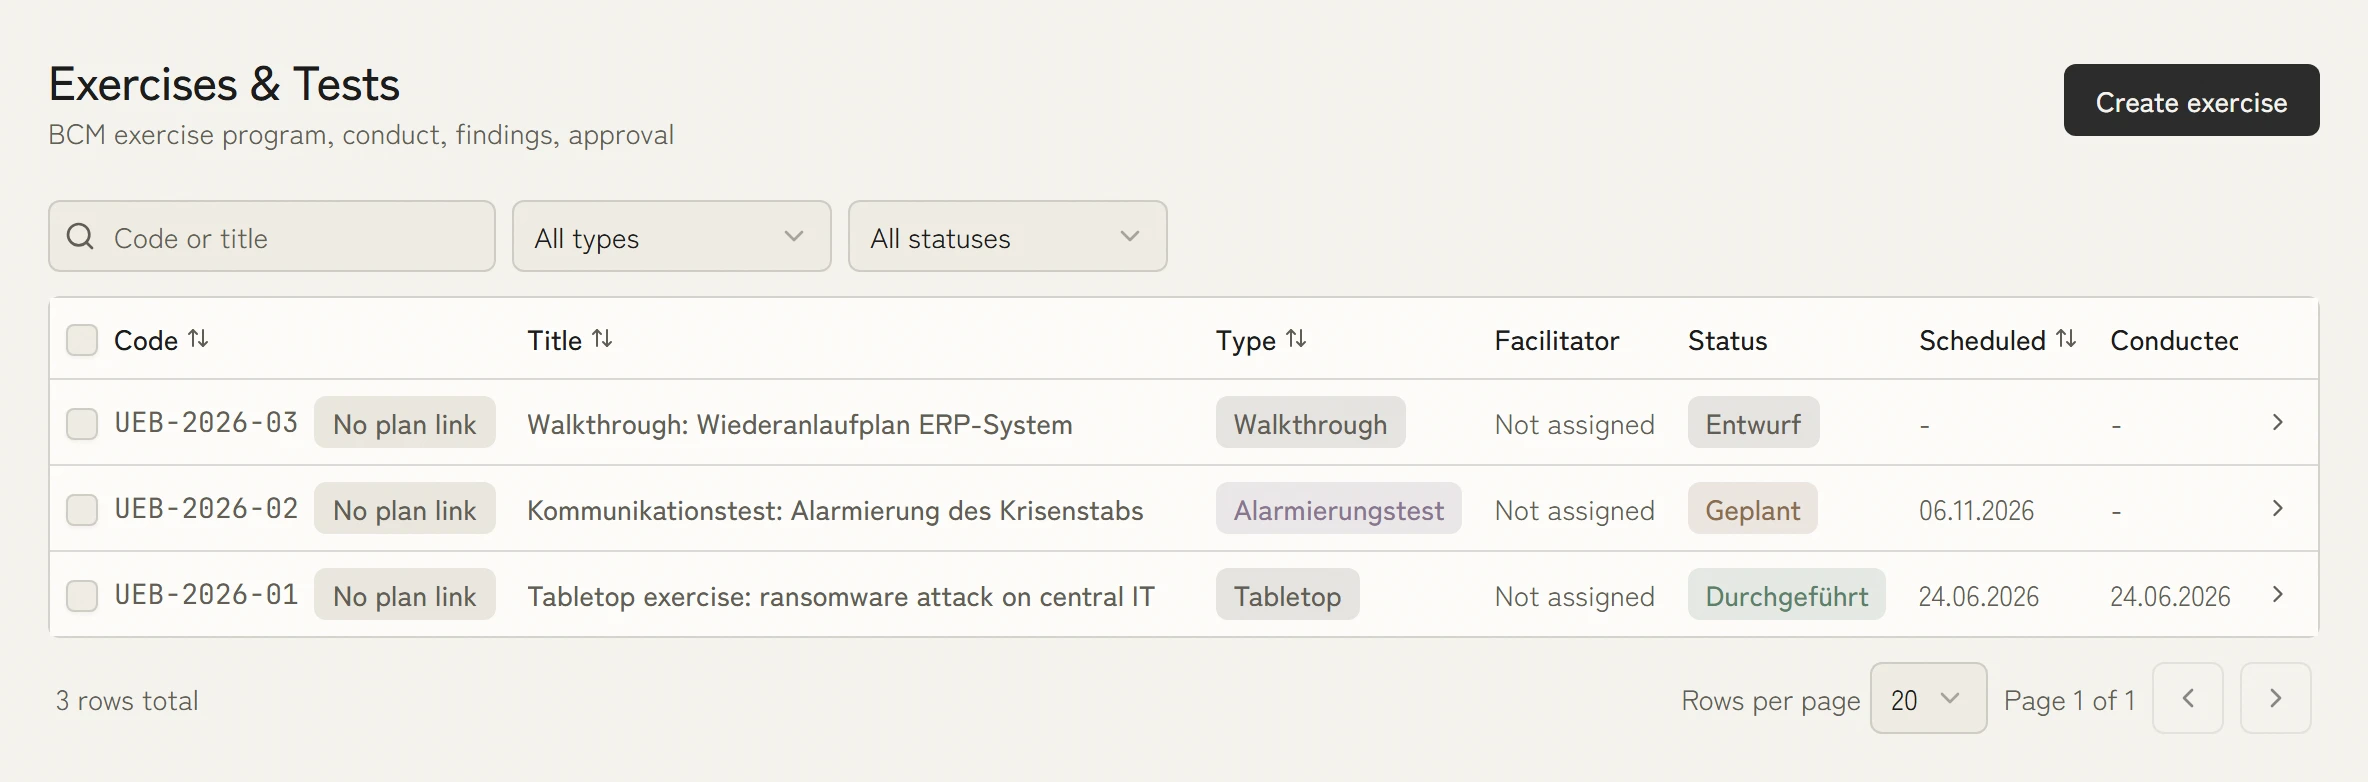
Exercises that write back to the plan
Walkthroughs, alerting tests and tabletop exercises are planned with an objective and a date. Findings and follow-up actions attach to the plan that was tested, so the exercise history is there at audit without being rebuilt.
Run ISO 22301 together with NIS2, DORA and KRITIS-DG
The same continuity evidence serves the obligations under NIS2, DORA and the KRITIS-Dachgesetz. Where the substance overlaps, evidence is kept once and shown several times; the standard-specific reasoning stays visible on the record.
4 standardsISO 22301, NIS2, DORA and KRITIS-DG use the same BC evidence
Connect ISO 22301 with other standards
Extend the same BCMS working state to the standards and obligations that apply to your organisation.
- ISO 27001The international ISMS standardLearn more
- NIS2EU cybersecurity directiveLearn more
- DORAFinancial sector resilienceLearn more
- KRITIS-DGCritical infrastructure lawLearn more
ISO 22301 by company and role
More for ISO 22301
BCMS as a peer to your ISMS, not a side project
ISO 22301 sits alongside the ISMS, the DSMS and the AIMS in KaitoSec, on one data model. A risk identified in the ISMS becomes a BC scenario, a critical asset feeds both control selection and recovery planning, the management review covers all four. No parallel registers, no silo handovers.
The path to certification is plannable
Stage 1 examines your documentation, Stage 2 the implementation in practice, followed by annual surveillance audits in a three-year cycle. KaitoSec shows per requirement which evidence stands and where gaps remain, so you set the audit date based on maturity.
Plans tested before reality tests them
Plan and run tabletop walkthroughs, functional tests and full-scale simulations. Capture findings, lessons learned and follow-up actions, then link them back to the BC plan that was tested. ISO 22301, NIS2 and DORA evidence is generated by the work, not compiled after it.
BIA and risk assessment as one step (clause 8.2)
The standard requires both as the foundation: understanding impact and assessing continuity risks. You run the BIA at process, service or asset level, assess risks on the same object and define RTO, RPO, MTPD and MBCO per process. Registers and objects are the same as in the ISMS, nothing is entered twice.
Strategies with a justified selection (clause 8.3)
BIA results become continuity requirements, from which you derive strategies and solutions. Each option documents cost, feasibility and resource needs, because the standard requires a justified selection, not just an outcome.
Plans and procedures for the real event (clause 8.4)
BC plans capture roles, activation, communication and decision authority. Versioning, approval, distribution and acknowledgement run in the same workflow as policies. That way, every role knows its part before it is needed.
Plans are only worth as much as the last exercise (clause 8.5)
The standard requires an ongoing exercise programme with defined objectives, from tabletop walkthroughs through functional tests to full-scale exercises. Findings and follow-up actions are documented directly on the tested plan; the exercise history is fully evidenced at audit.
Performance evaluation and management review (clauses 9.1 to 9.3)
Metrics, internal audit and management review are separate obligations in the standard. KaitoSec brings exercise results, incidents and review decisions together in one place; every improvement stays traceable to its trigger.
What ISO 22301 requires
ISO 22301 requires a managed BCMS: context and scope, business impact analysis and risk assessment, strategies chosen with a documented rationale, written plans, an ongoing exercise programme, and evaluation, internal audit and management review. BSI standard 200-4 is compatible with it.
Frequently asked questions about ISO 22301
Do we have to certify against ISO 22301 to use the BCMS?
No. The BCMS module works with or without a certification goal. If you pursue ISO 22301, you connect requirements, BIA, plans, exercises and reviews. For other obligations, suitable evidence can be reused where your scope genuinely supports it.
How does ISO 22301 relate to NIS2 and DORA?
NIS2 Article 21 explicitly requires business continuity and crisis management. DORA expects financial entities to maintain digital operational resilience including ICT business continuity policies. A BCMS aligned to ISO 22301 covers much of both and produces the evidence supervisory authorities expect. KaitoSec maps ISO 22301 requirements to NIS2 measures and DORA articles on one data model.
What is the difference between a BC plan and a disaster recovery plan?
A BC plan covers the overall response: which processes keep going, who decides, how the organisation communicates, how the business escalates. A disaster recovery plan covers the technical restoration of systems. KaitoSec carries both and keeps the relationships explicit, so neither plan drifts from the other.
How often should BC plans be tested?
ISO 22301, NIS2 and DORA all expect regular testing, typically at least annually for critical plans and more often for high-impact processes. KaitoSec schedules, documents and tracks exercises in the same place as the plans themselves, so the cadence is provable without manual record-keeping.
We already run an ISMS. What changes if we add the BCMS?
The asset register, the risk register and the policy library stay in place; the BCMS extends them with BIA, recovery strategies, BC plans, exercises and crisis activation. Your ISBs work in the same workspace, your management review covers both systems, and audit evidence compiles from one source. Our BCM knowledge hub covers BIA, recovery strategies and exercises in depth.

Your BCMS plan in thirty minutes.
In the demo we walk through your critical processes: BIA, recovery times, plans and exercises. You leave knowing which audit date is realistic.