
EU AI Act: every AI system classified, with its reasoning.
KaitoSec keeps your AI systems in one register, guides the classification under Annex III and reminds you when a reassessment is due. Transparency duties and documentation sit on the system, together with ISO 42001.



 5.0 out of 5
A classification with reasons, not a hunch
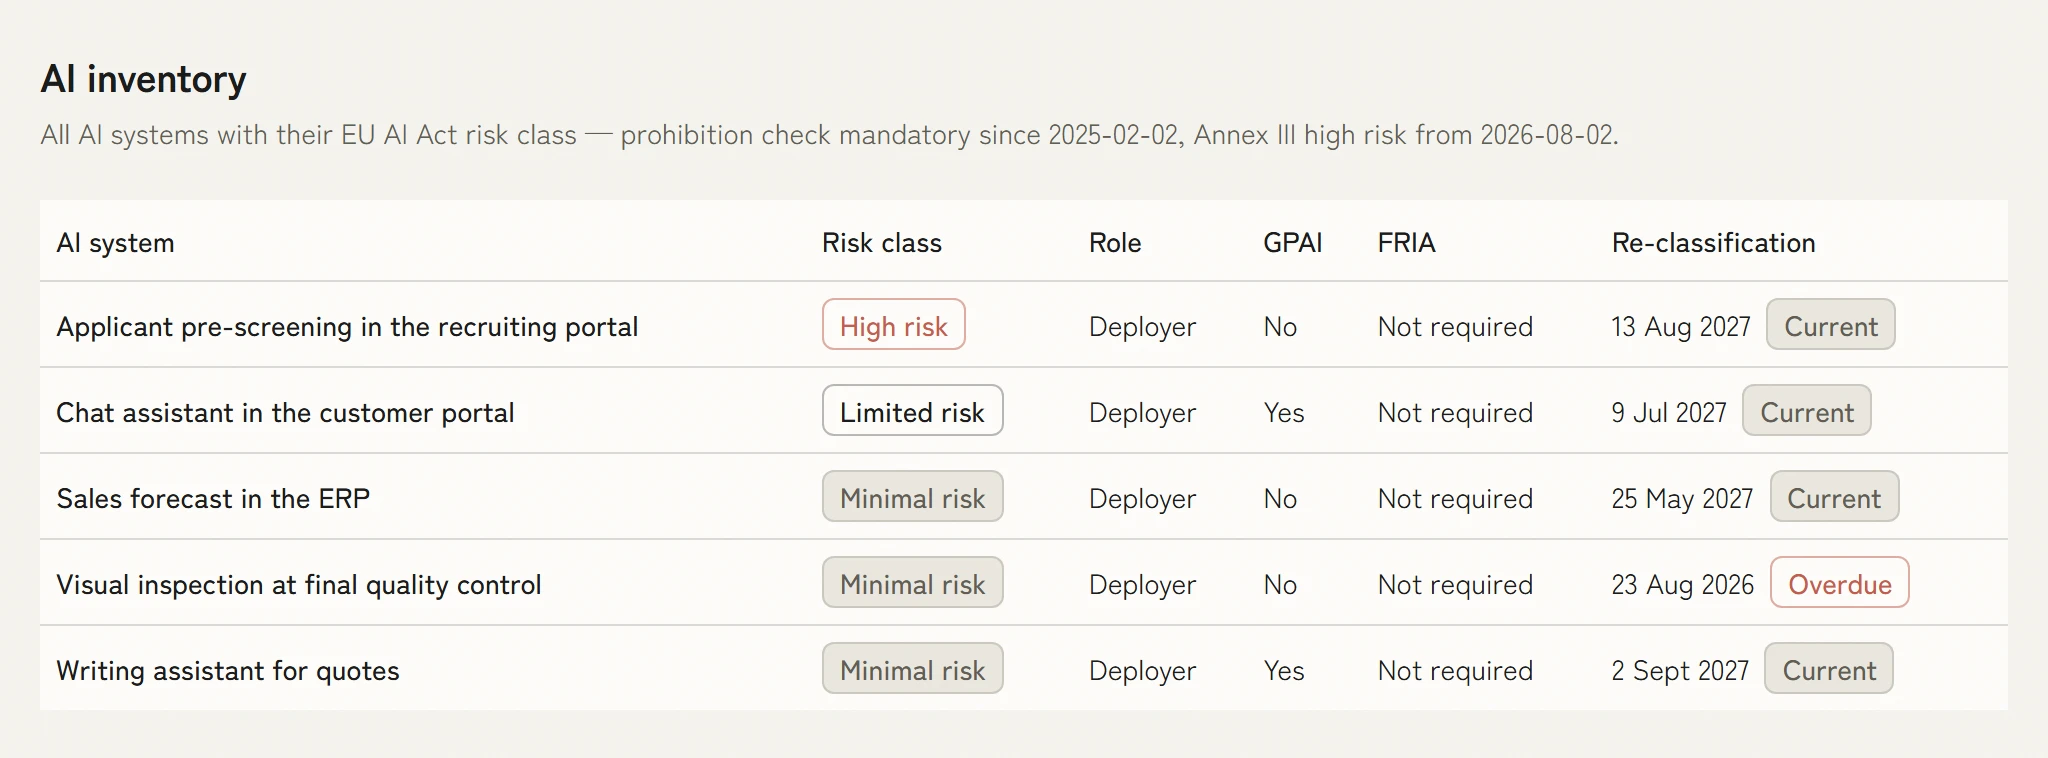
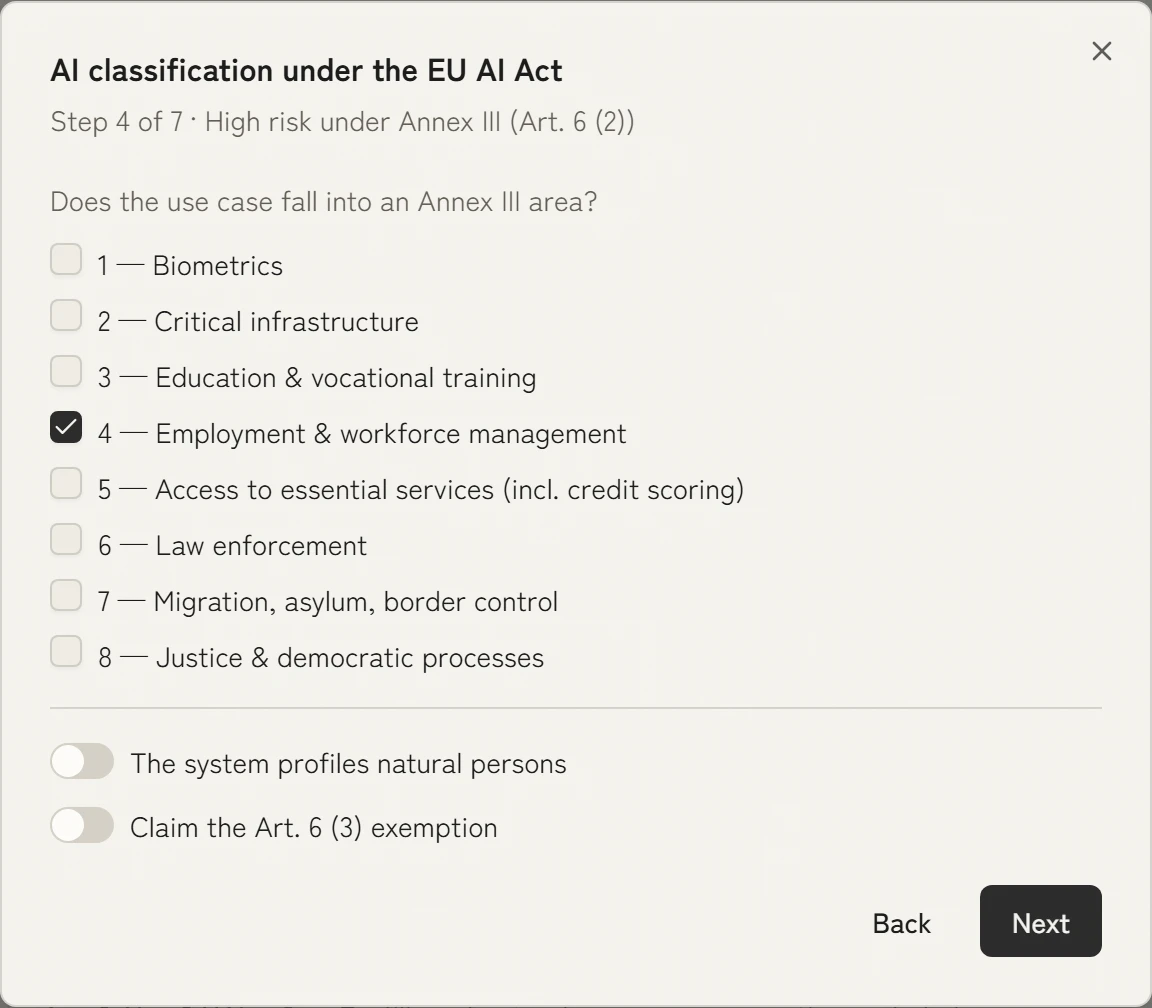
The classification run walks through the Annex III criteria and the prohibited practices and records why a system counts as high risk, which role you hold and from when the obligations bite. That reasoning is the first thing a supervisory authority asks for.
4 tiersUnacceptable, high, limited, minimal risk classification
Evidence the transparency duties per system
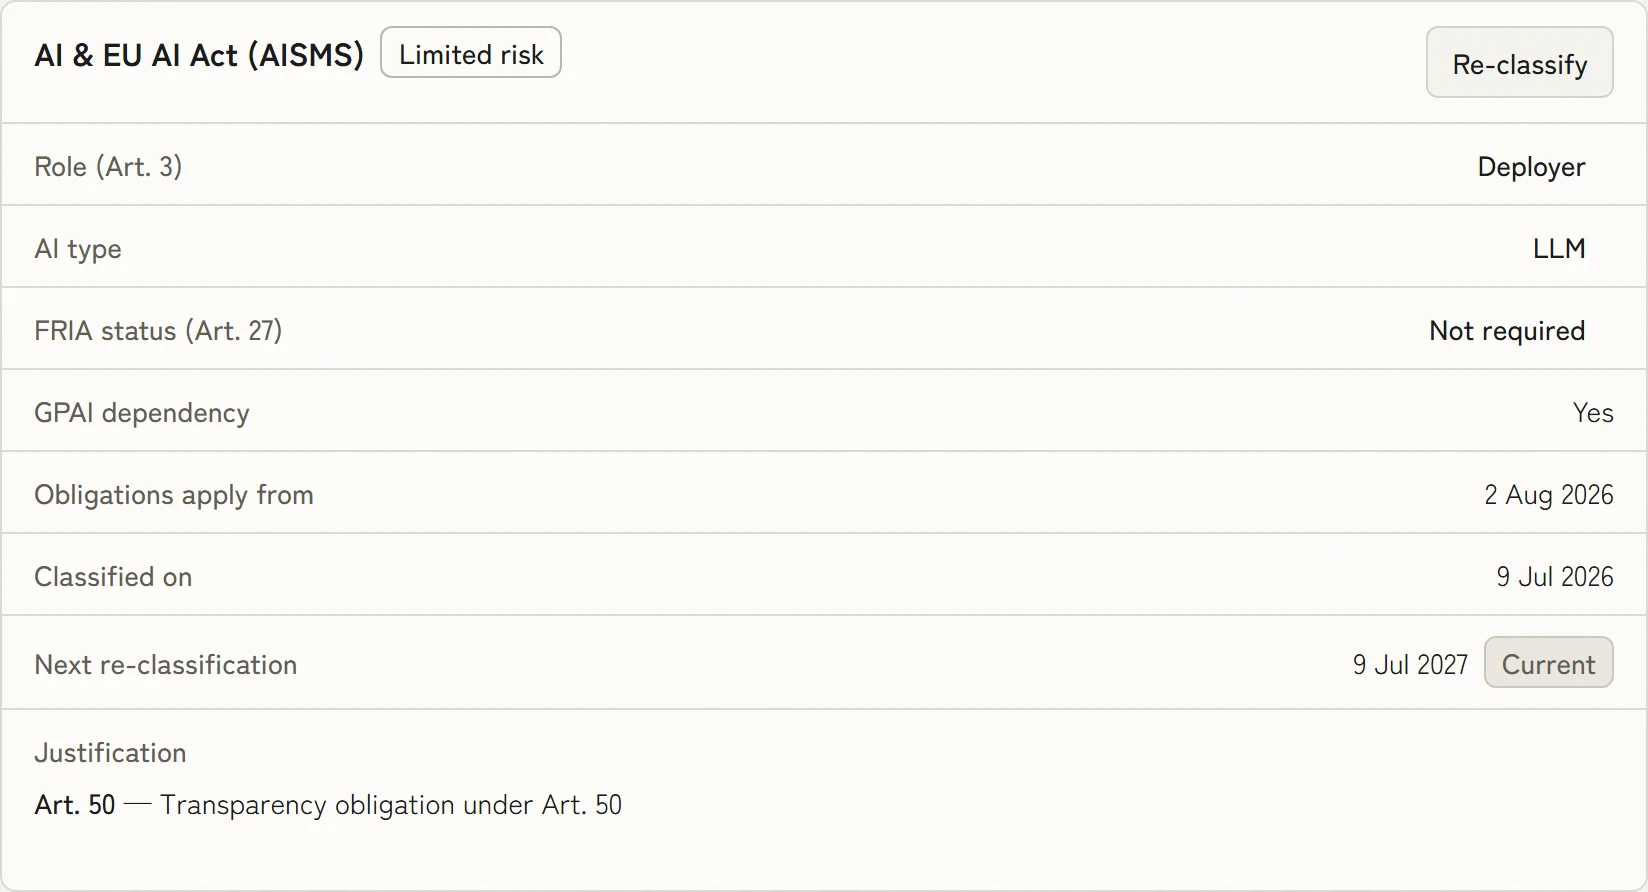
A chat assistant falls under limited risk and therefore under the disclosure duty of Article 50. The record states which transparency duty applies and whether a general-purpose model sits behind it.
A classification ages, the product remembers
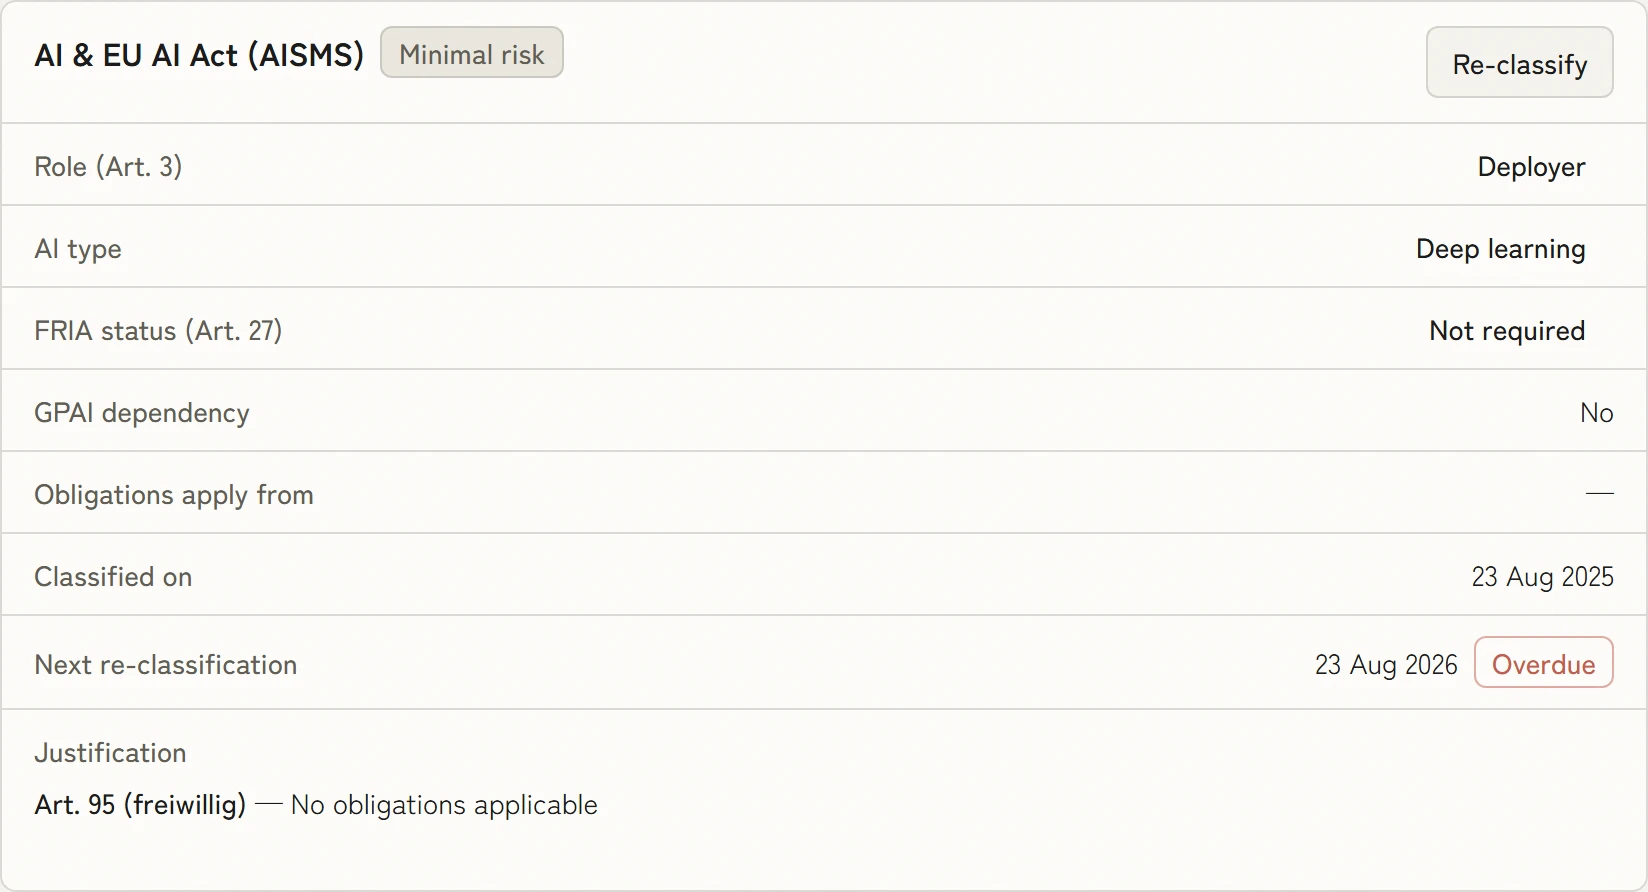
Every classification carries a date for its reassessment. Once that date passes, KaitoSec flags the system instead of letting last year's judgement quietly stand.
EU AI Act and ISO 42001 on the same controls
ISO 42001 supplies the management system, the EU AI Act the obligations. KaitoSec maps both onto the same AIMS controls, so the certification work pays into the regulation at the same time.
2 frameworksEU AI Act and ISO 42001 mapped to the same AIMS controls
Connect the EU AI Act with other standards
Connect the AI obligations with the systems that already carry data protection and security.
EU AI Act by company and role
More for the EU AI Act
AI system risk classification
The EU AI Act defines four risk tiers: unacceptable, high, limited, and minimal risk. KaitoSec's classification wizard guides you through the Annex III criteria and prohibited practices, producing a documented risk classification for every AI system in your portfolio. It is the first thing a supervisory authority asks for.
High-risk conformity assessment
High-risk AI systems require comprehensive technical documentation, conformity assessments, and registration in the EU AI database. KaitoSec provides templates for technical files, risk management records, and data governance documentation aligned with the requirements of Articles 9–17.
AI governance and accountability
The Act requires organisations to establish human oversight mechanisms, designate responsible roles, and implement quality management for AI. KaitoSec's governance module tracks AI system owners, oversight procedures, incident logs, and post-market monitoring obligations in one place.
Keep every AI system in one register
Maintain a complete inventory of all AI systems your organisation develops, deploys, or uses. Each system record captures the risk classification, intended purpose, affected user groups, and compliance status, giving you the overview supervisory authorities and executive management increasingly expect.
Build the Article 11 technical documentation
High-risk AI systems require extensive technical documentation under Article 11. KaitoSec provides a structured document builder covering system design, training data governance, accuracy metrics, robustness testing, and human oversight mechanisms, exportable in regulator-ready format.
Track transparency obligations per system
Limited-risk AI systems, such as chatbots and tools for AI-generated content, must meet specific transparency obligations under Article 50, including user disclosure. KaitoSec tracks which transparency requirements apply to each system and maintains evidence that disclosure mechanisms are in place.
What the EU AI Act requires
The EU AI Act sorts AI systems into four risk tiers: unacceptable, high, limited and minimal. Prohibited practices are banned; high-risk systems need risk management, data quality, technical documentation, logging, human oversight and a conformity assessment. Limited-risk systems carry the transparency duty of Article 50.
Frequently asked questions about the EU AI Act
What are the four risk tiers under the EU AI Act?
The EU AI Act classifies AI systems into four tiers. Unacceptable-risk practices are prohibited, such as social scoring or real-time remote biometric identification in publicly accessible spaces for law enforcement, which is allowed only under narrow exceptions. High-risk systems in areas like employment, education, or critical infrastructure require conformity assessments and registration. Limited risk systems must meet transparency obligations. Minimal risk systems face no specific obligations.
Does the EU AI Act apply to companies outside the EU?
Yes. Like GDPR, the EU AI Act has extraterritorial reach. It applies to any organisation placing AI systems on the EU market or whose AI outputs are used in the EU, regardless of where the provider or deployer is headquartered. Non-EU providers of high-risk AI systems must appoint an authorised representative in the EU.
What is a GPAI model and what obligations does it have?
General Purpose AI (GPAI) models are AI models trained on large datasets capable of performing many different tasks, such as large language models. The EU AI Act imposes transparency obligations on all GPAI model providers, including model documentation and compliance with copyright law. Models with systemic risk (above defined compute thresholds) face additional requirements including adversarial testing.
When do EU AI Act obligations become enforceable?
The EU AI Act entered into force in August 2024. The prohibitions on certain AI practices have applied since February 2025, GPAI model obligations since August 2025, and the Article 50 transparency obligations since August 2026. The high-risk obligations were postponed by the Digital Omnibus in June 2026: they apply from 2 December 2027 for Annex III systems and from August 2028 for product-embedded systems under Annex I. KaitoSec tracks all deadlines and helps you prioritise work based on your compliance timeline.
How does the EU AI Act interact with GDPR?
The EU AI Act and GDPR interact closely when AI systems process personal data. GDPR governs how that data is collected, processed, and stored, while the AI Act governs how AI systems using that data must be designed, tested, and governed. KaitoSec cross-maps obligations so shared requirements, such as data quality, transparency, and human oversight, are evidenced once across both frameworks. That single-evidence approach is what our article Resilience Made Easy describes for every framework.

Your AI plan in thirty minutes.
In the demo we classify your AI systems and settle role, obligations and deadlines. You leave knowing which system needs work first.