
Mid-market
ISMS for SMEs: information security without a dedicated security team
ISMS, BSI Grundschutz, NIS2 and business continuity in one system, with clear next steps. Your team does the ongoing work itself and brings in consultants only for the hard questions.

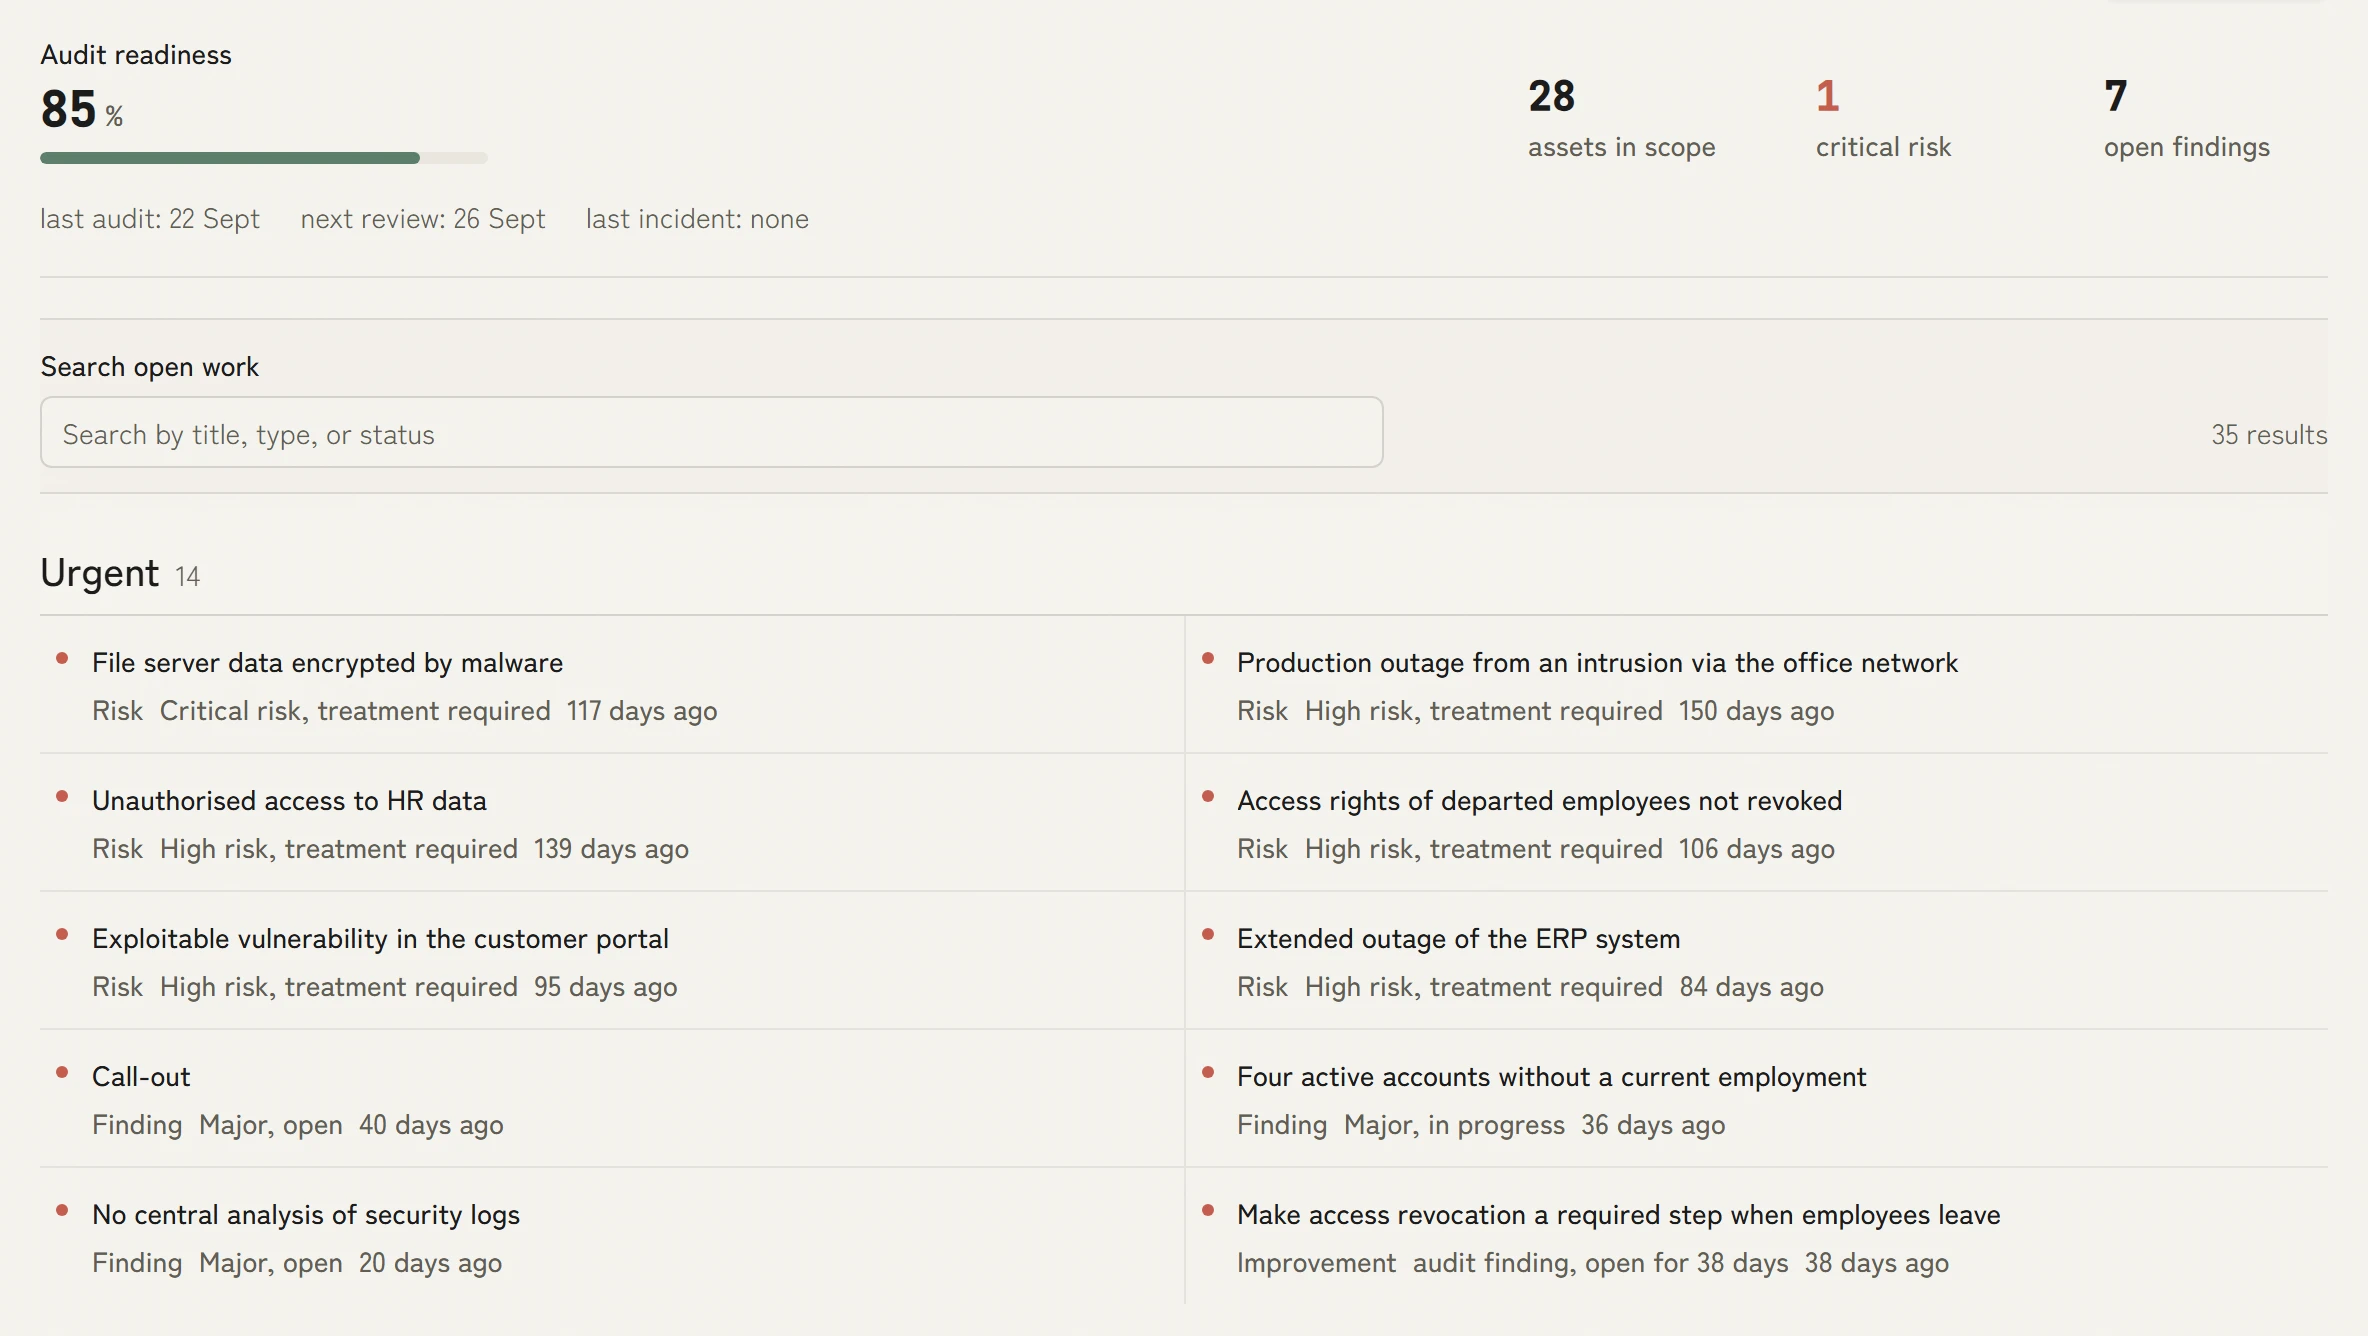


 5.0 out of 5
What changes for your team
Reduce recurring maintenance
Policies, risks, controls and evidence share owners, review dates and links in one working state. A change is maintained at its source instead of being copied into several audit lists.
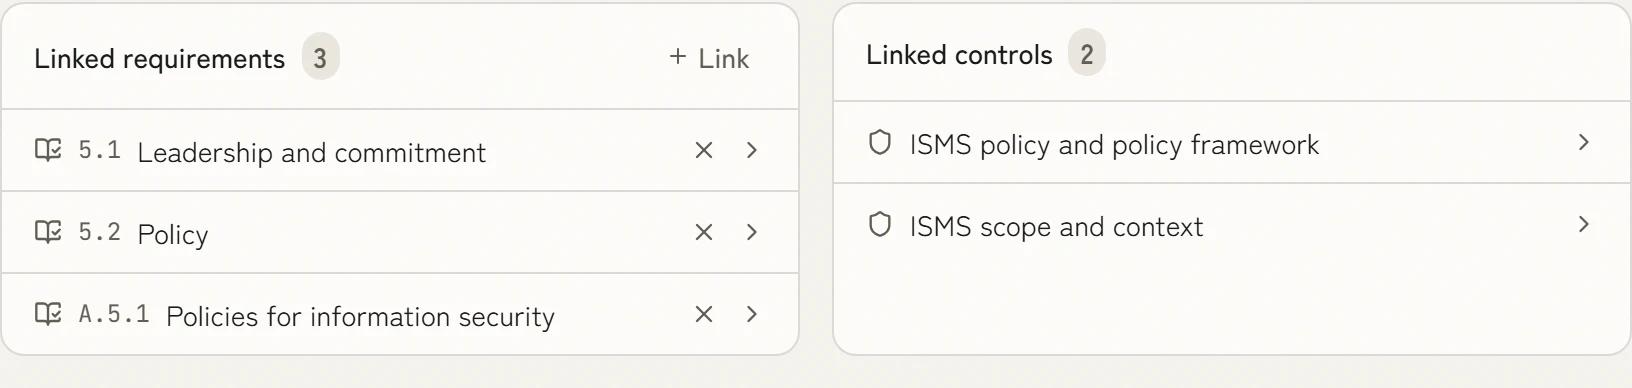
Use consulting for judgement, not clerical upkeep
Your team runs the recurring workflow and brings in an adviser for methodology, difficult decisions or audit preparation where needed. Controlled access keeps that support inside the same current context.
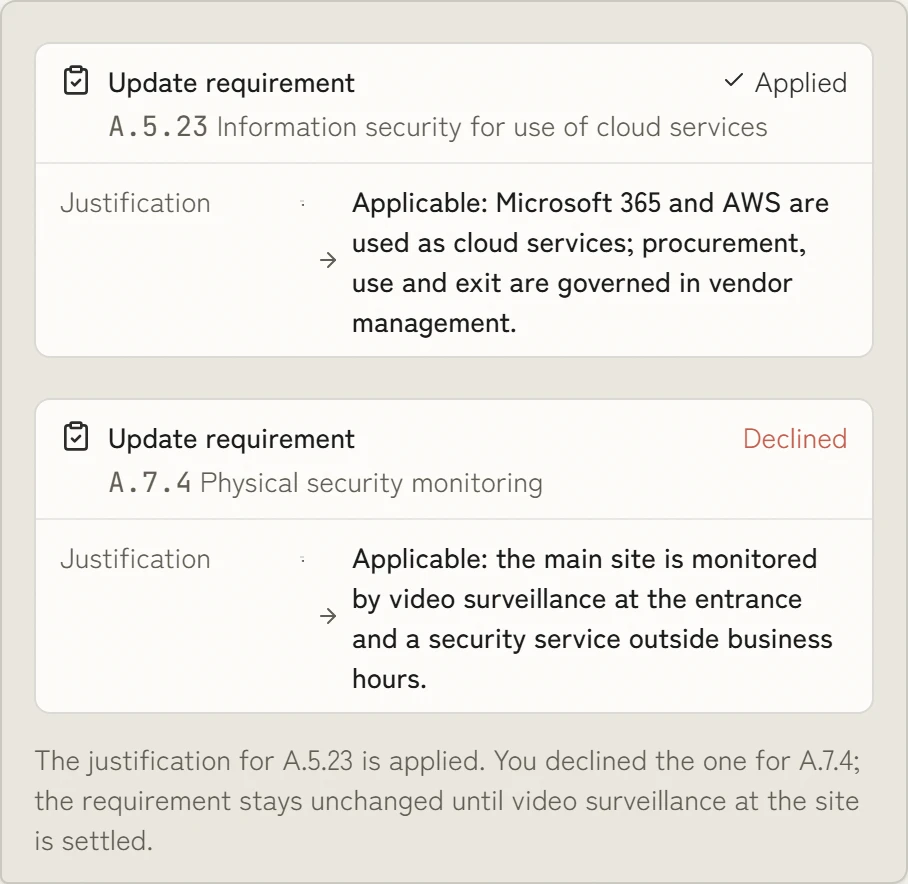
Bring existing data with you
Import existing inventory and register data, retain approved documents and connect both progressively. Useful prior work remains available instead of being re-entered solely to change tools.
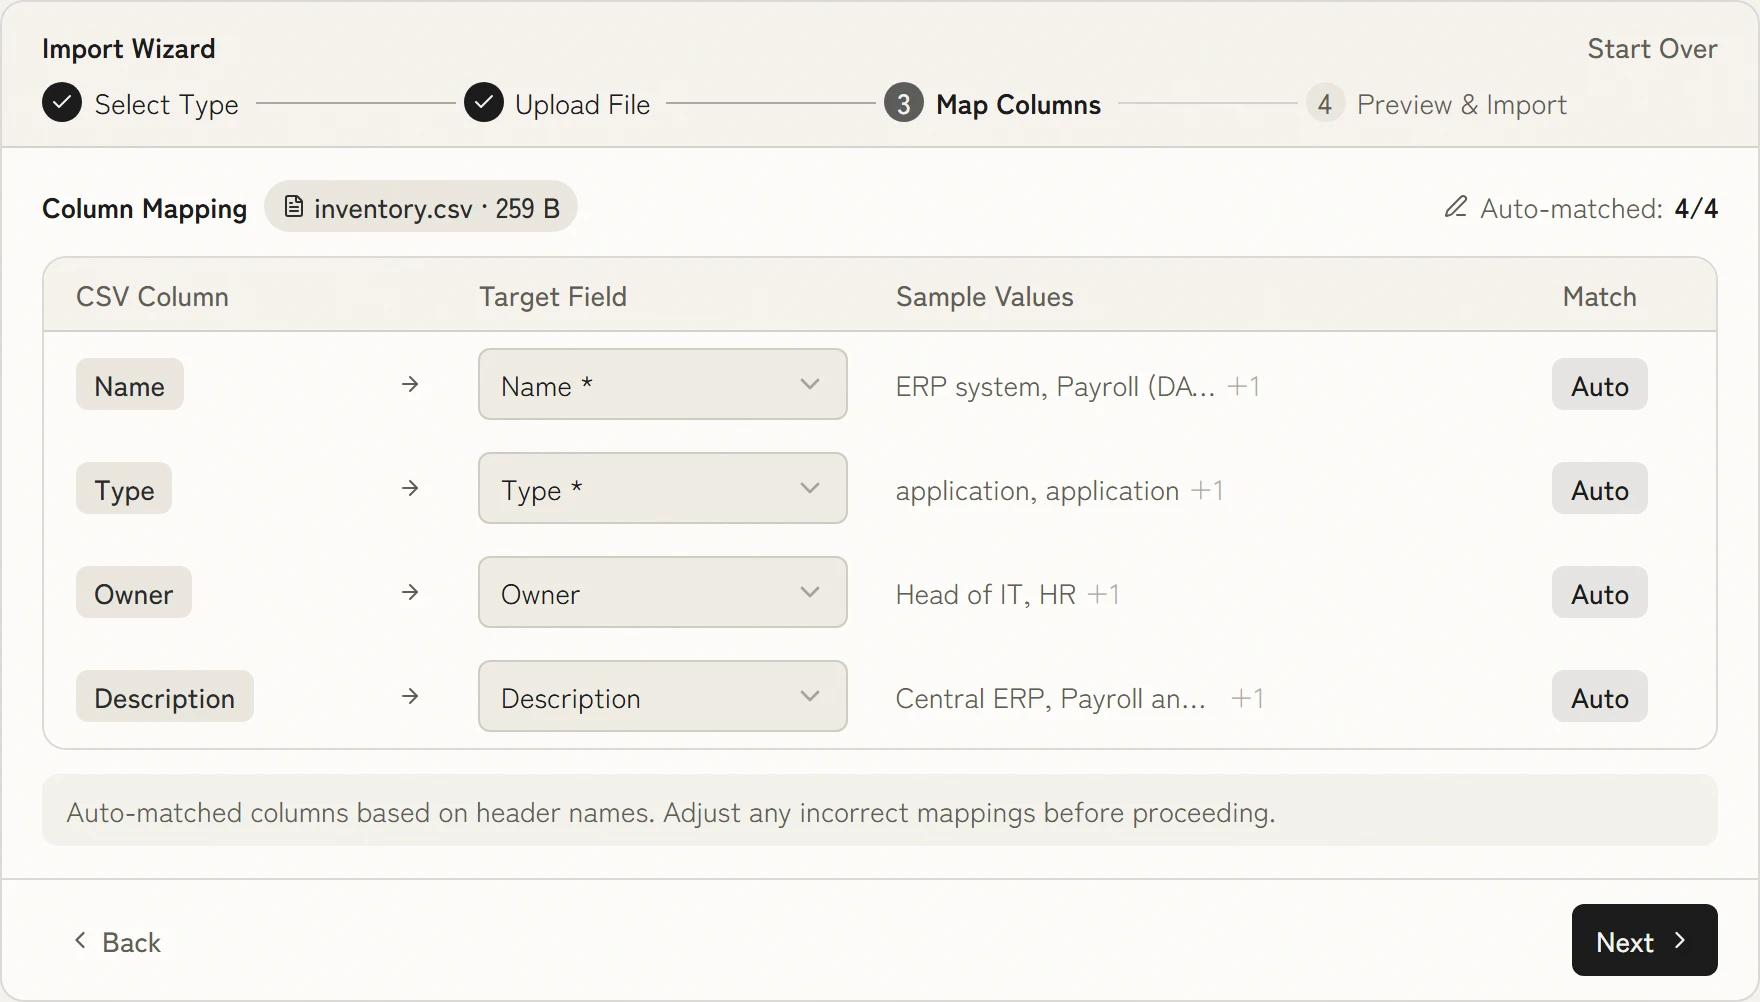
Make coordination part of the operating model
Tasks carry an owner, due date, review and approval. The information security officer steers exceptions and open decisions rather than rebuilding status by email before every meeting.
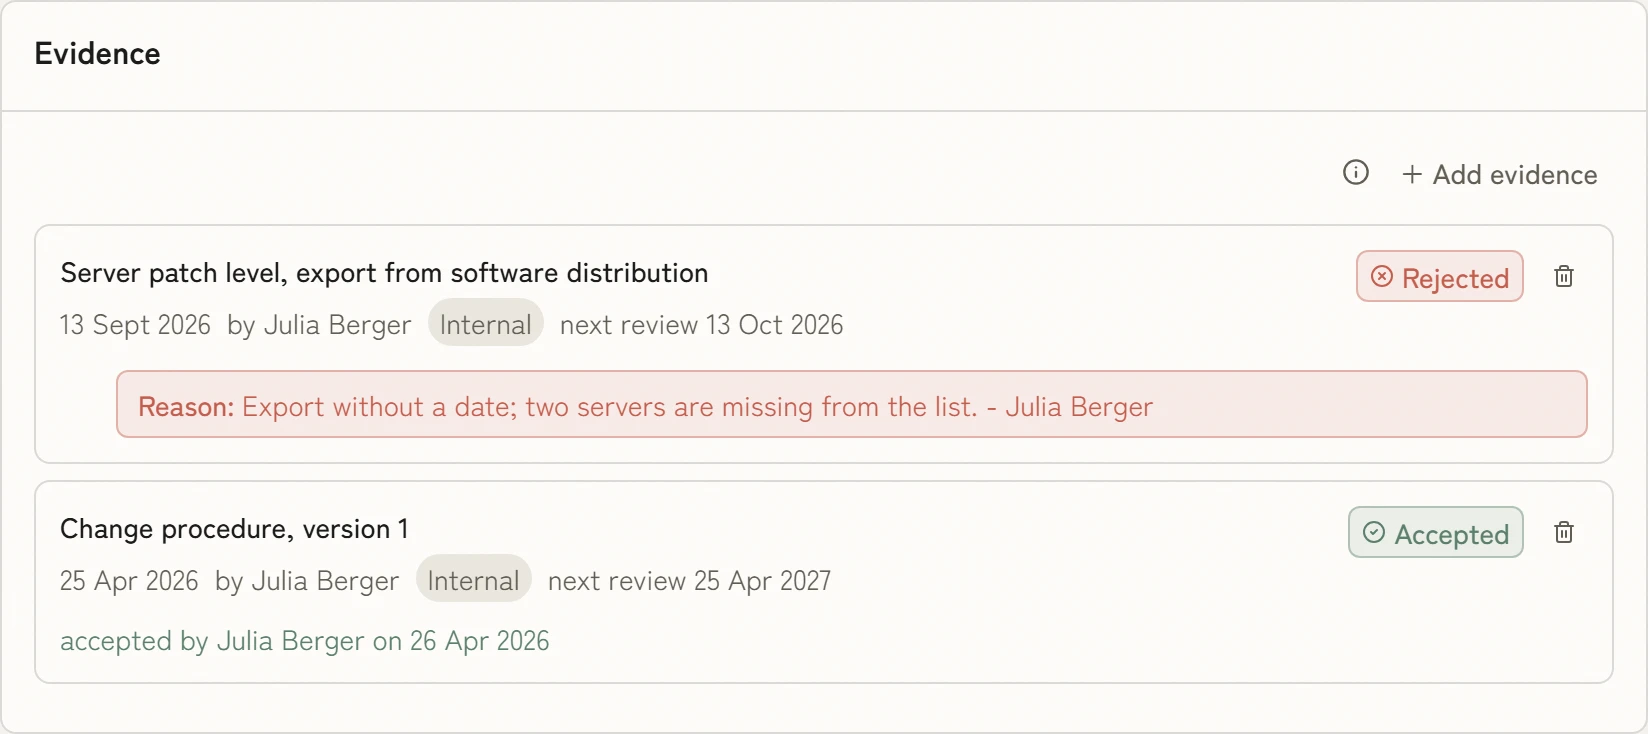
Inventory and evidence come from the systems you already use.
100+ integrations
All integrations















Matching standards and modules
Relevant requirements
How KaitoSec supports the work
Frequently asked questions from SMEs
Does a mid-sized company need an ISMS?
An ISMS is increasingly necessary for mid-sized companies because of NIS2, customer requirements from larger companies and automotive clients through TISAX, and cyber insurers. ISMS software helps SMEs answer these requirements once instead of three times.
How do you build an ISMS without a dedicated security team?
An ISMS without a dedicated security team needs a tool that guides the method and handles routine work. KaitoSec explains each requirement in context, KaitoSec AI proposes controls, and onboarding takes your team to its first working workflow. Teams that need specialist support can add consulting.
What does an ISMS cost for an SME?
The cost of an ISMS includes the software, internal effort and any consulting support. KaitoSec reduces the recurring internal workload; the ROI calculator estimates the effect for your case. We name the software cost in the call.
ISO 27001, TISAX or IT-Grundschutz: which is right for SMEs?
An ISMS for SMEs can use ISO 27001 for international customers, TISAX for the automotive supply chain, or BSI IT-Grundschutz for public-sector customers and organisations close to critical infrastructure. KaitoSec adds another standard later without starting over.
Can we continue working with Excel?
Excel can support an ISMS until the first audit or incident. After that, missing responsibilities, evidence links and history make it expensive to maintain. The migration imports existing Excel registers so previous work is retained.

Bring calm to your working week.
A personal demo in 30 minutes: we go through where you stand and show how your security officer sees the next step without spreadsheets.