
BSI IT-Grundschutz software for modelling, checks and certification
Structural analysis, protection needs, modelling, Grundschutz check and risk analysis under BSI 200-3 with the full compendium, instead of PDFs and Excel. The mapping to ISO 27001 and NIS2 saves you the second and third audit preparation.

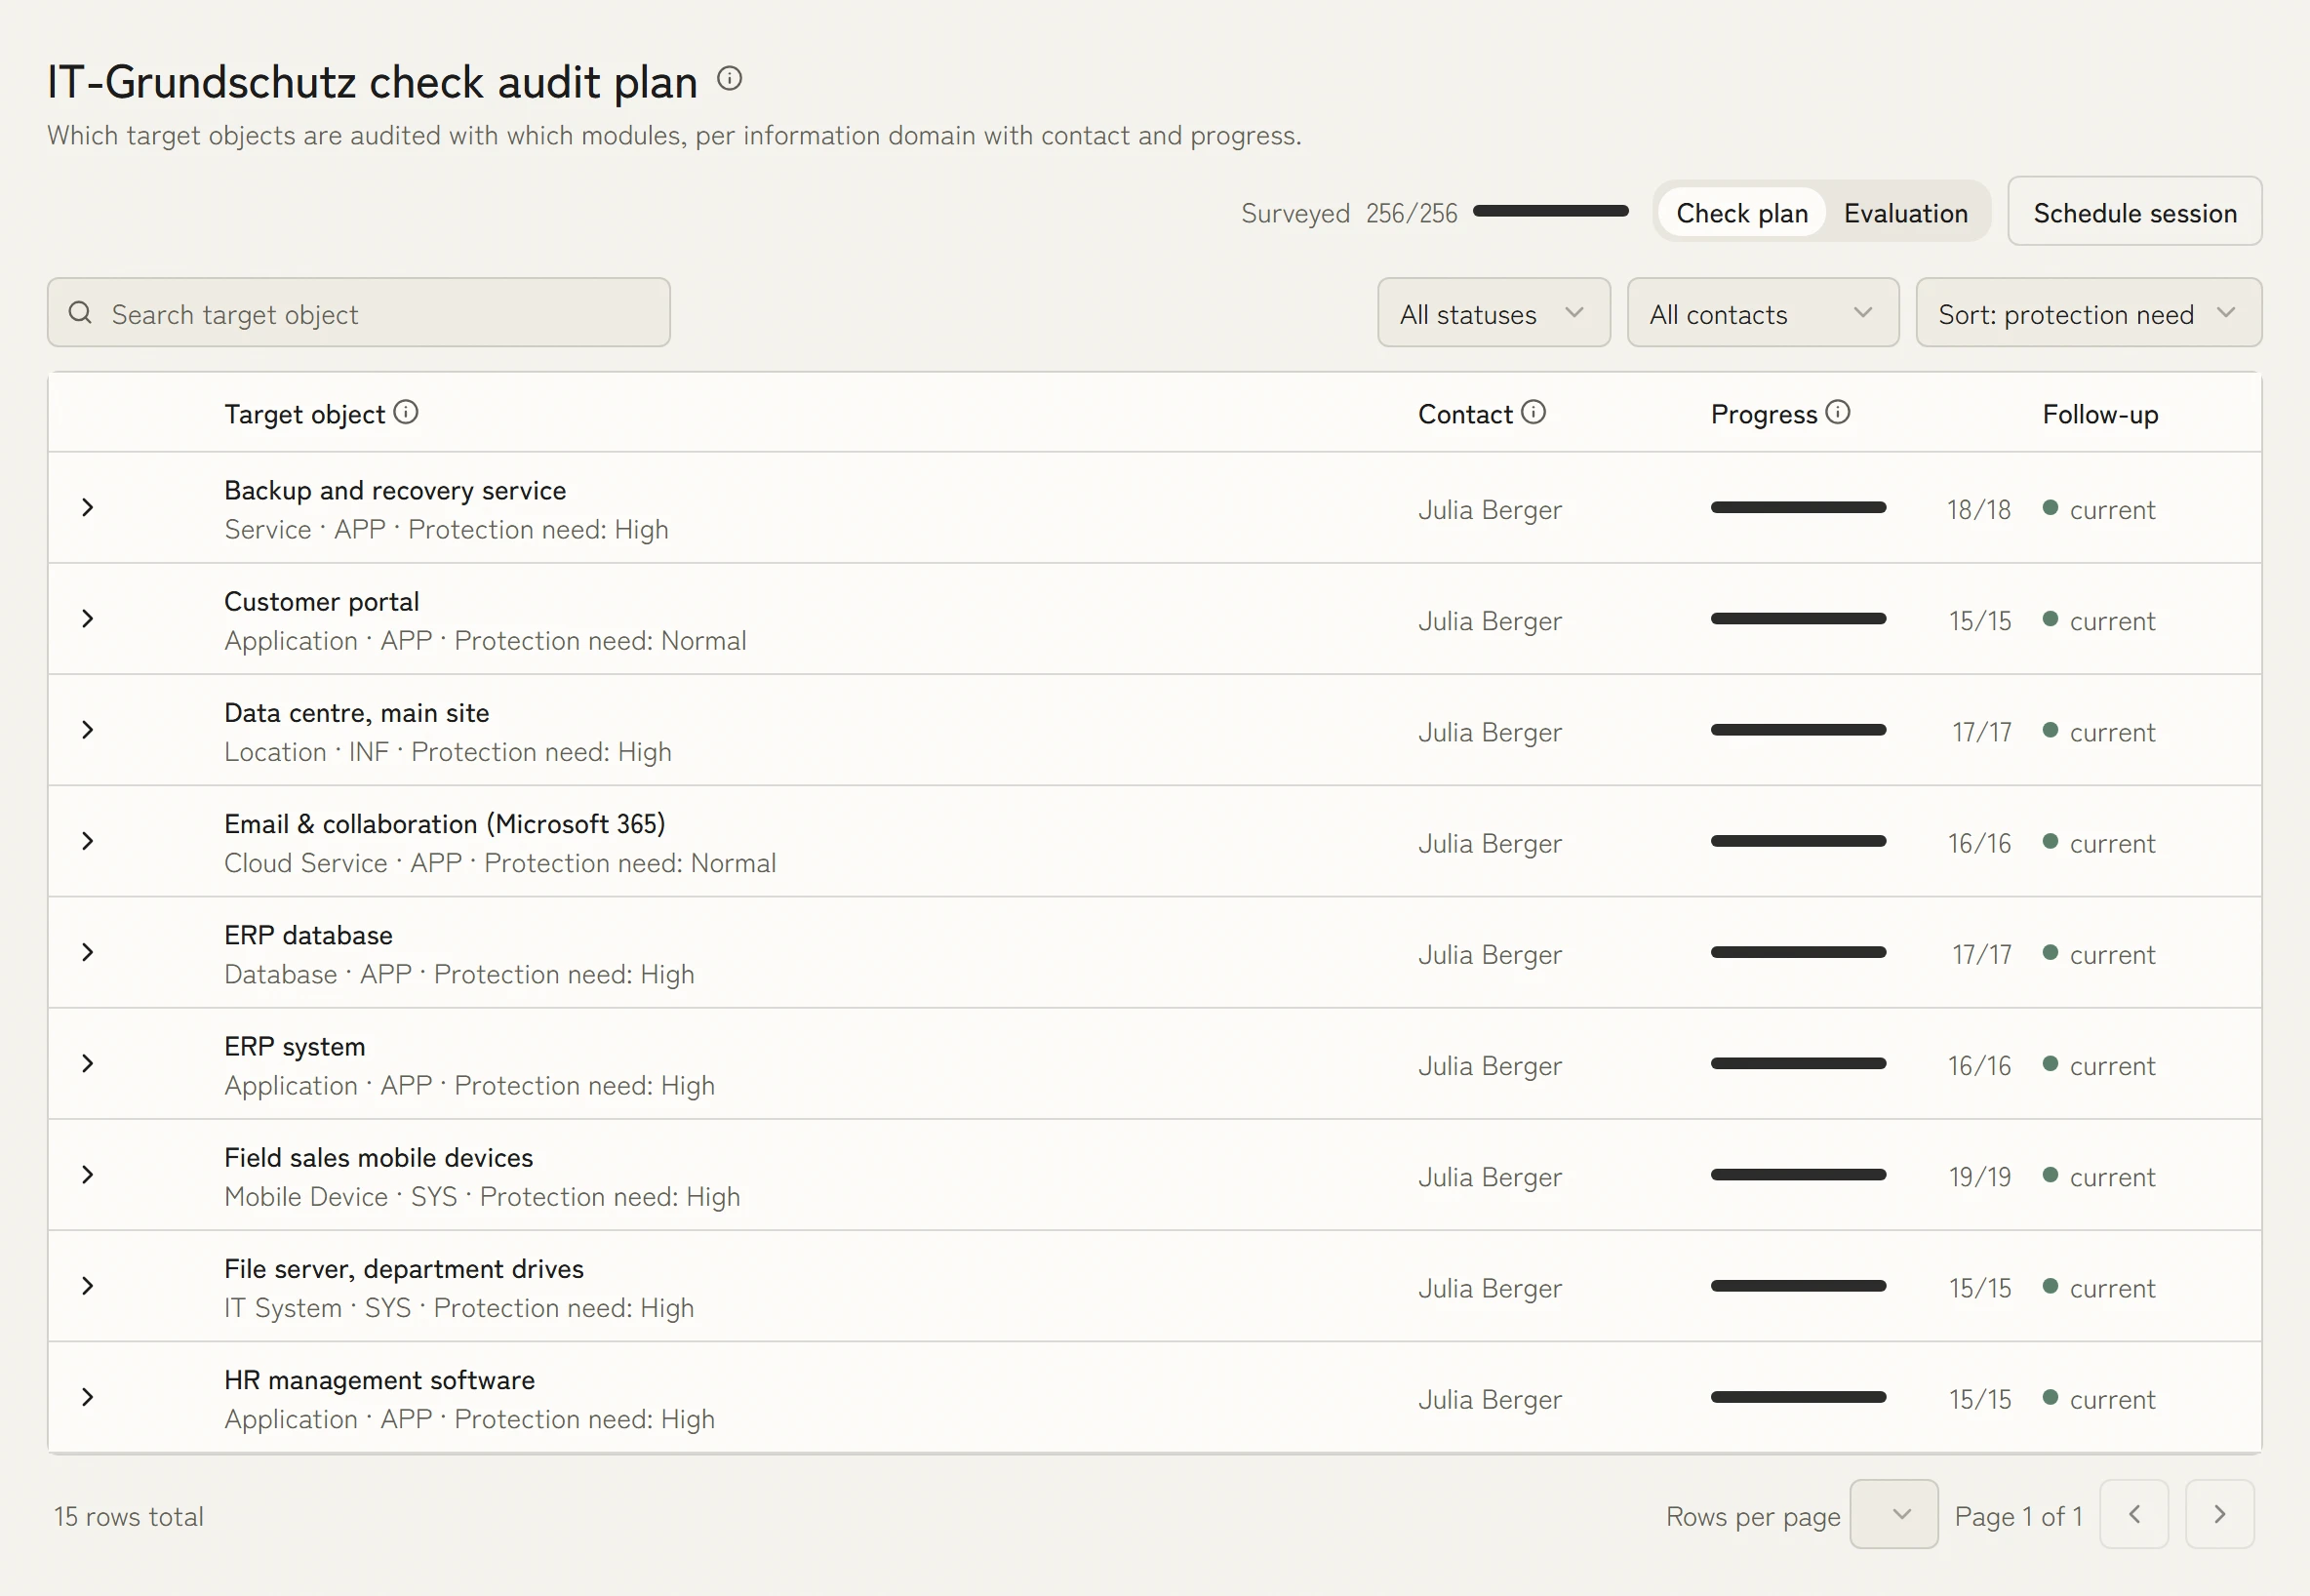


 5.0 out of 5
The complete IT-Grundschutz Compendium
Use the Bausteine, requirements and implementation guidance as structured records instead of copying the Compendium from PDFs into a separate working file.
110+Bausteine (modules) pre-loaded
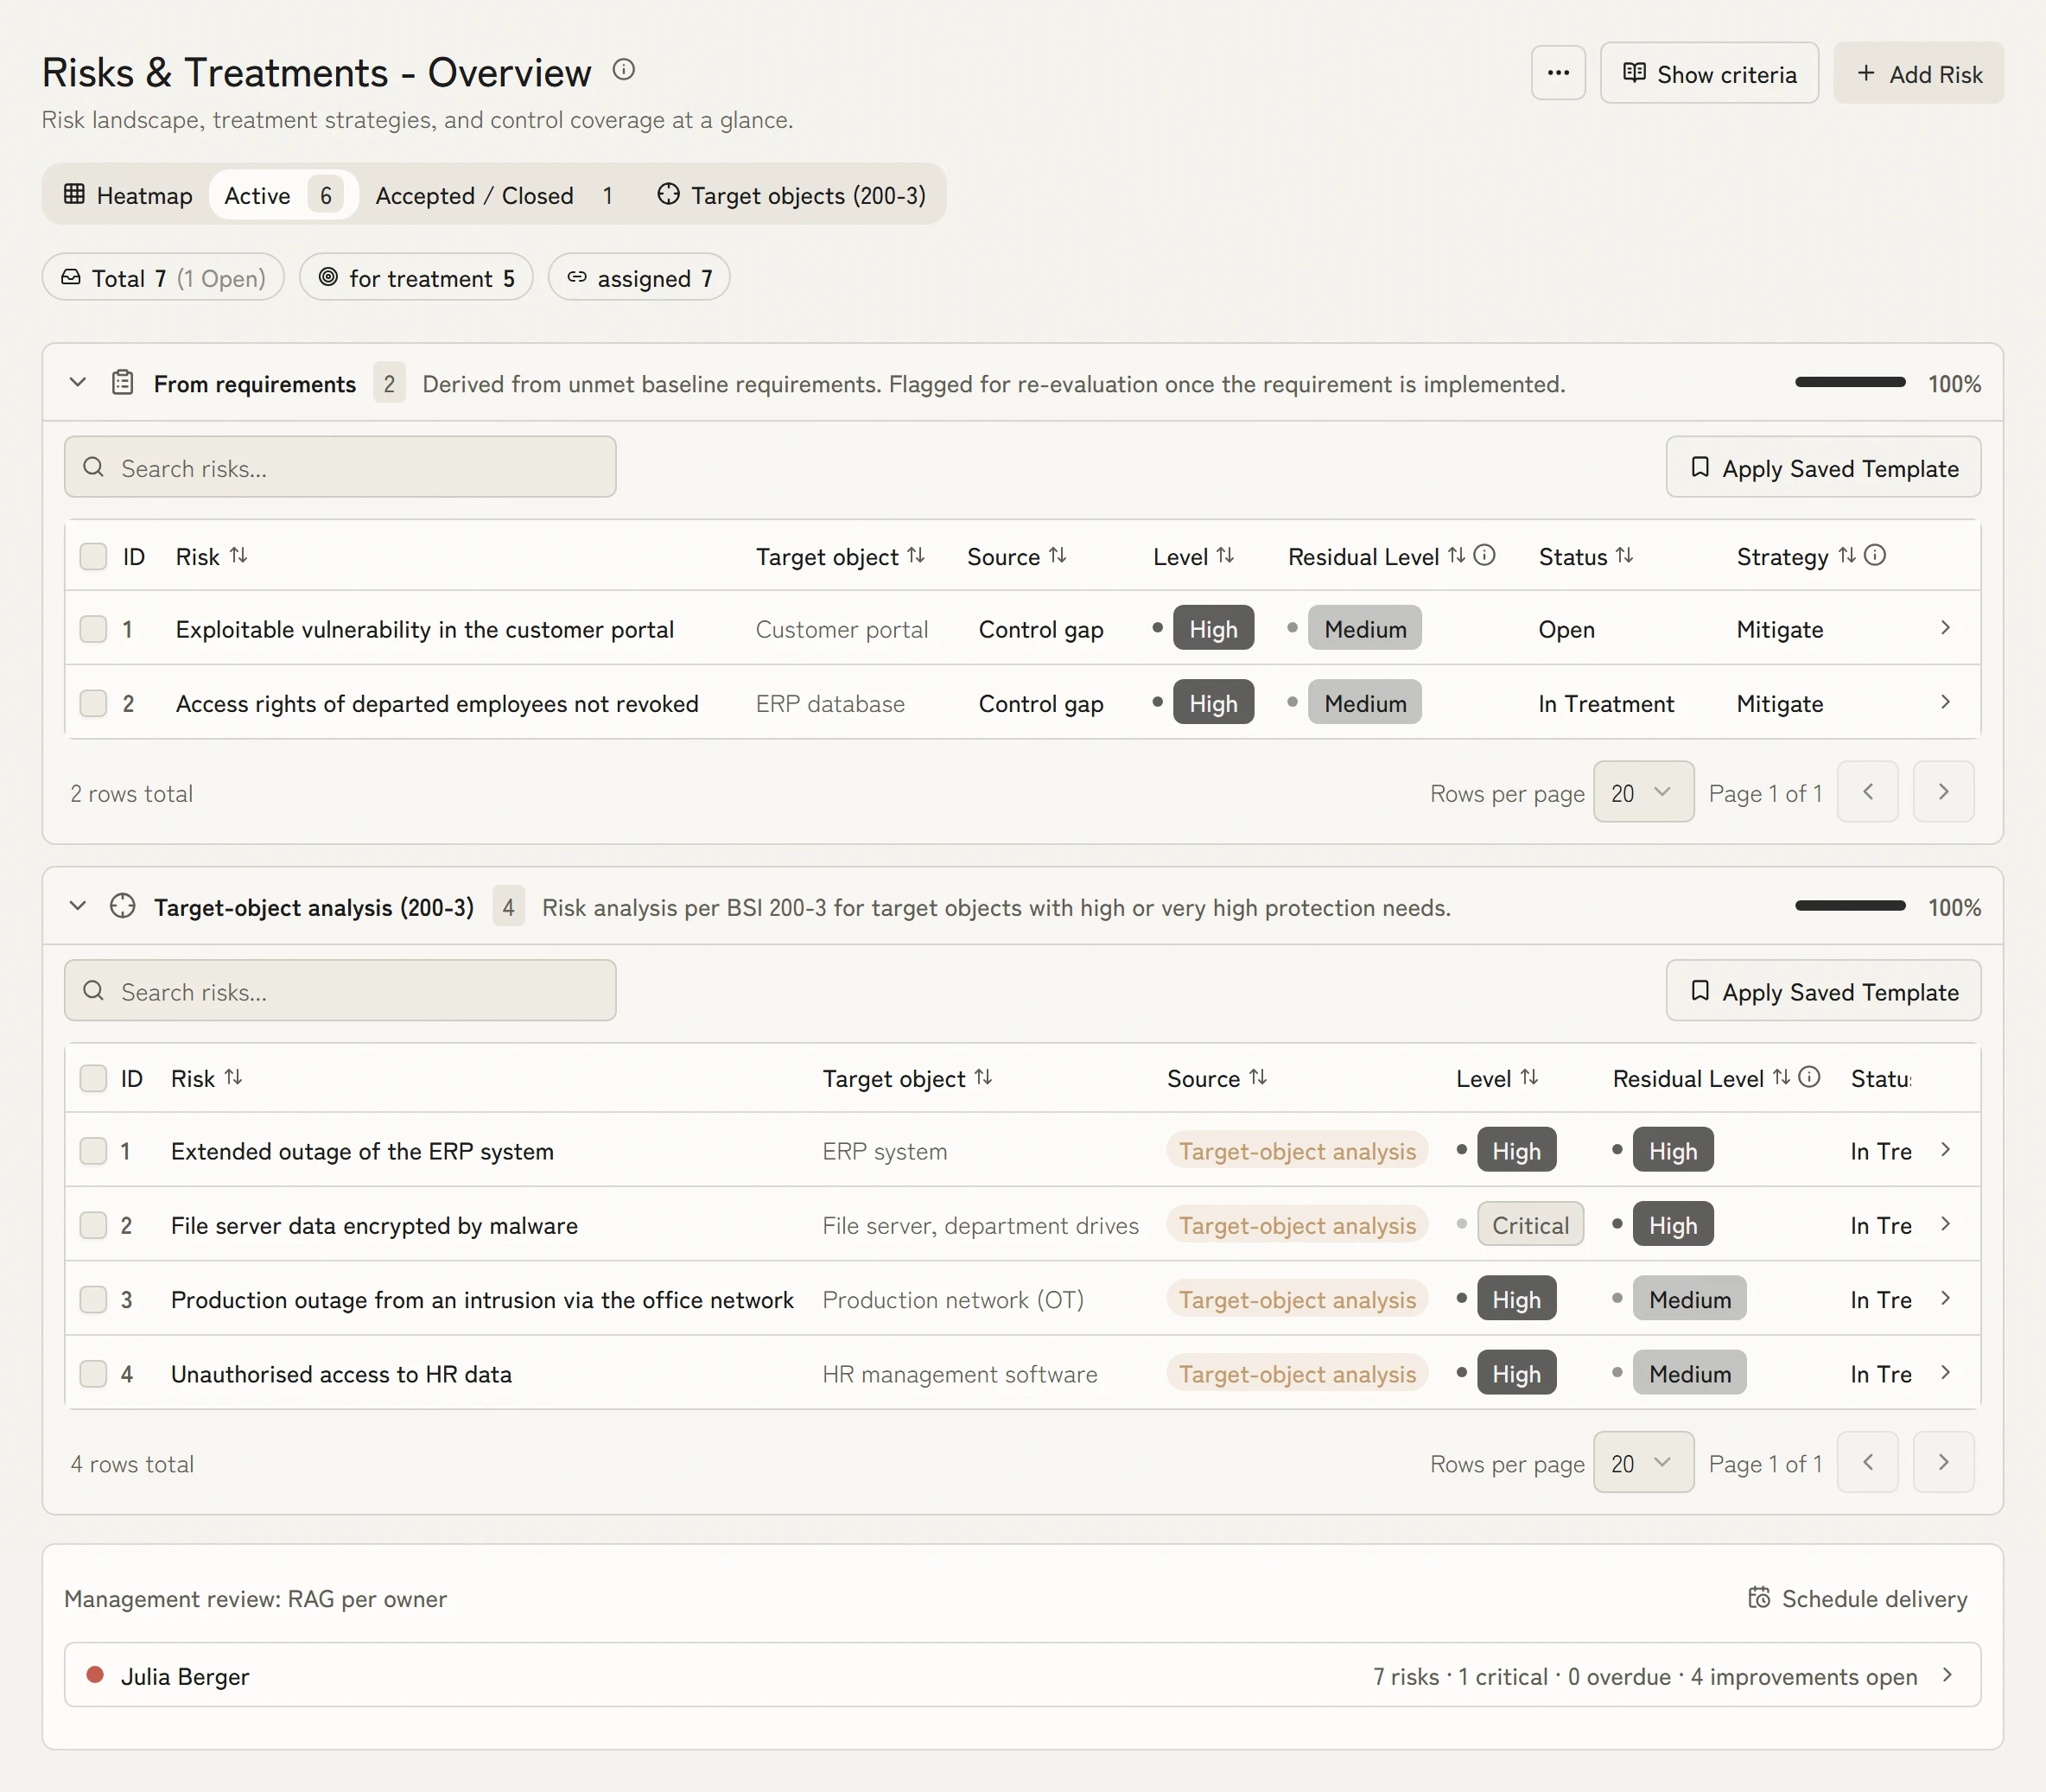
Grundschutz Check and risk analysis under BSI 200-3
Document implementation status in the Grundschutz Check and carry risks that need additional analysis into risk management software for BSI 200-3, including treatment, owner and review date.
Alternatives to verinice and HiScout
Compare methodology depth, operating model, migration paths and cross-framework work directly. The comparison pages state where each product differs instead of hiding the trade-offs.
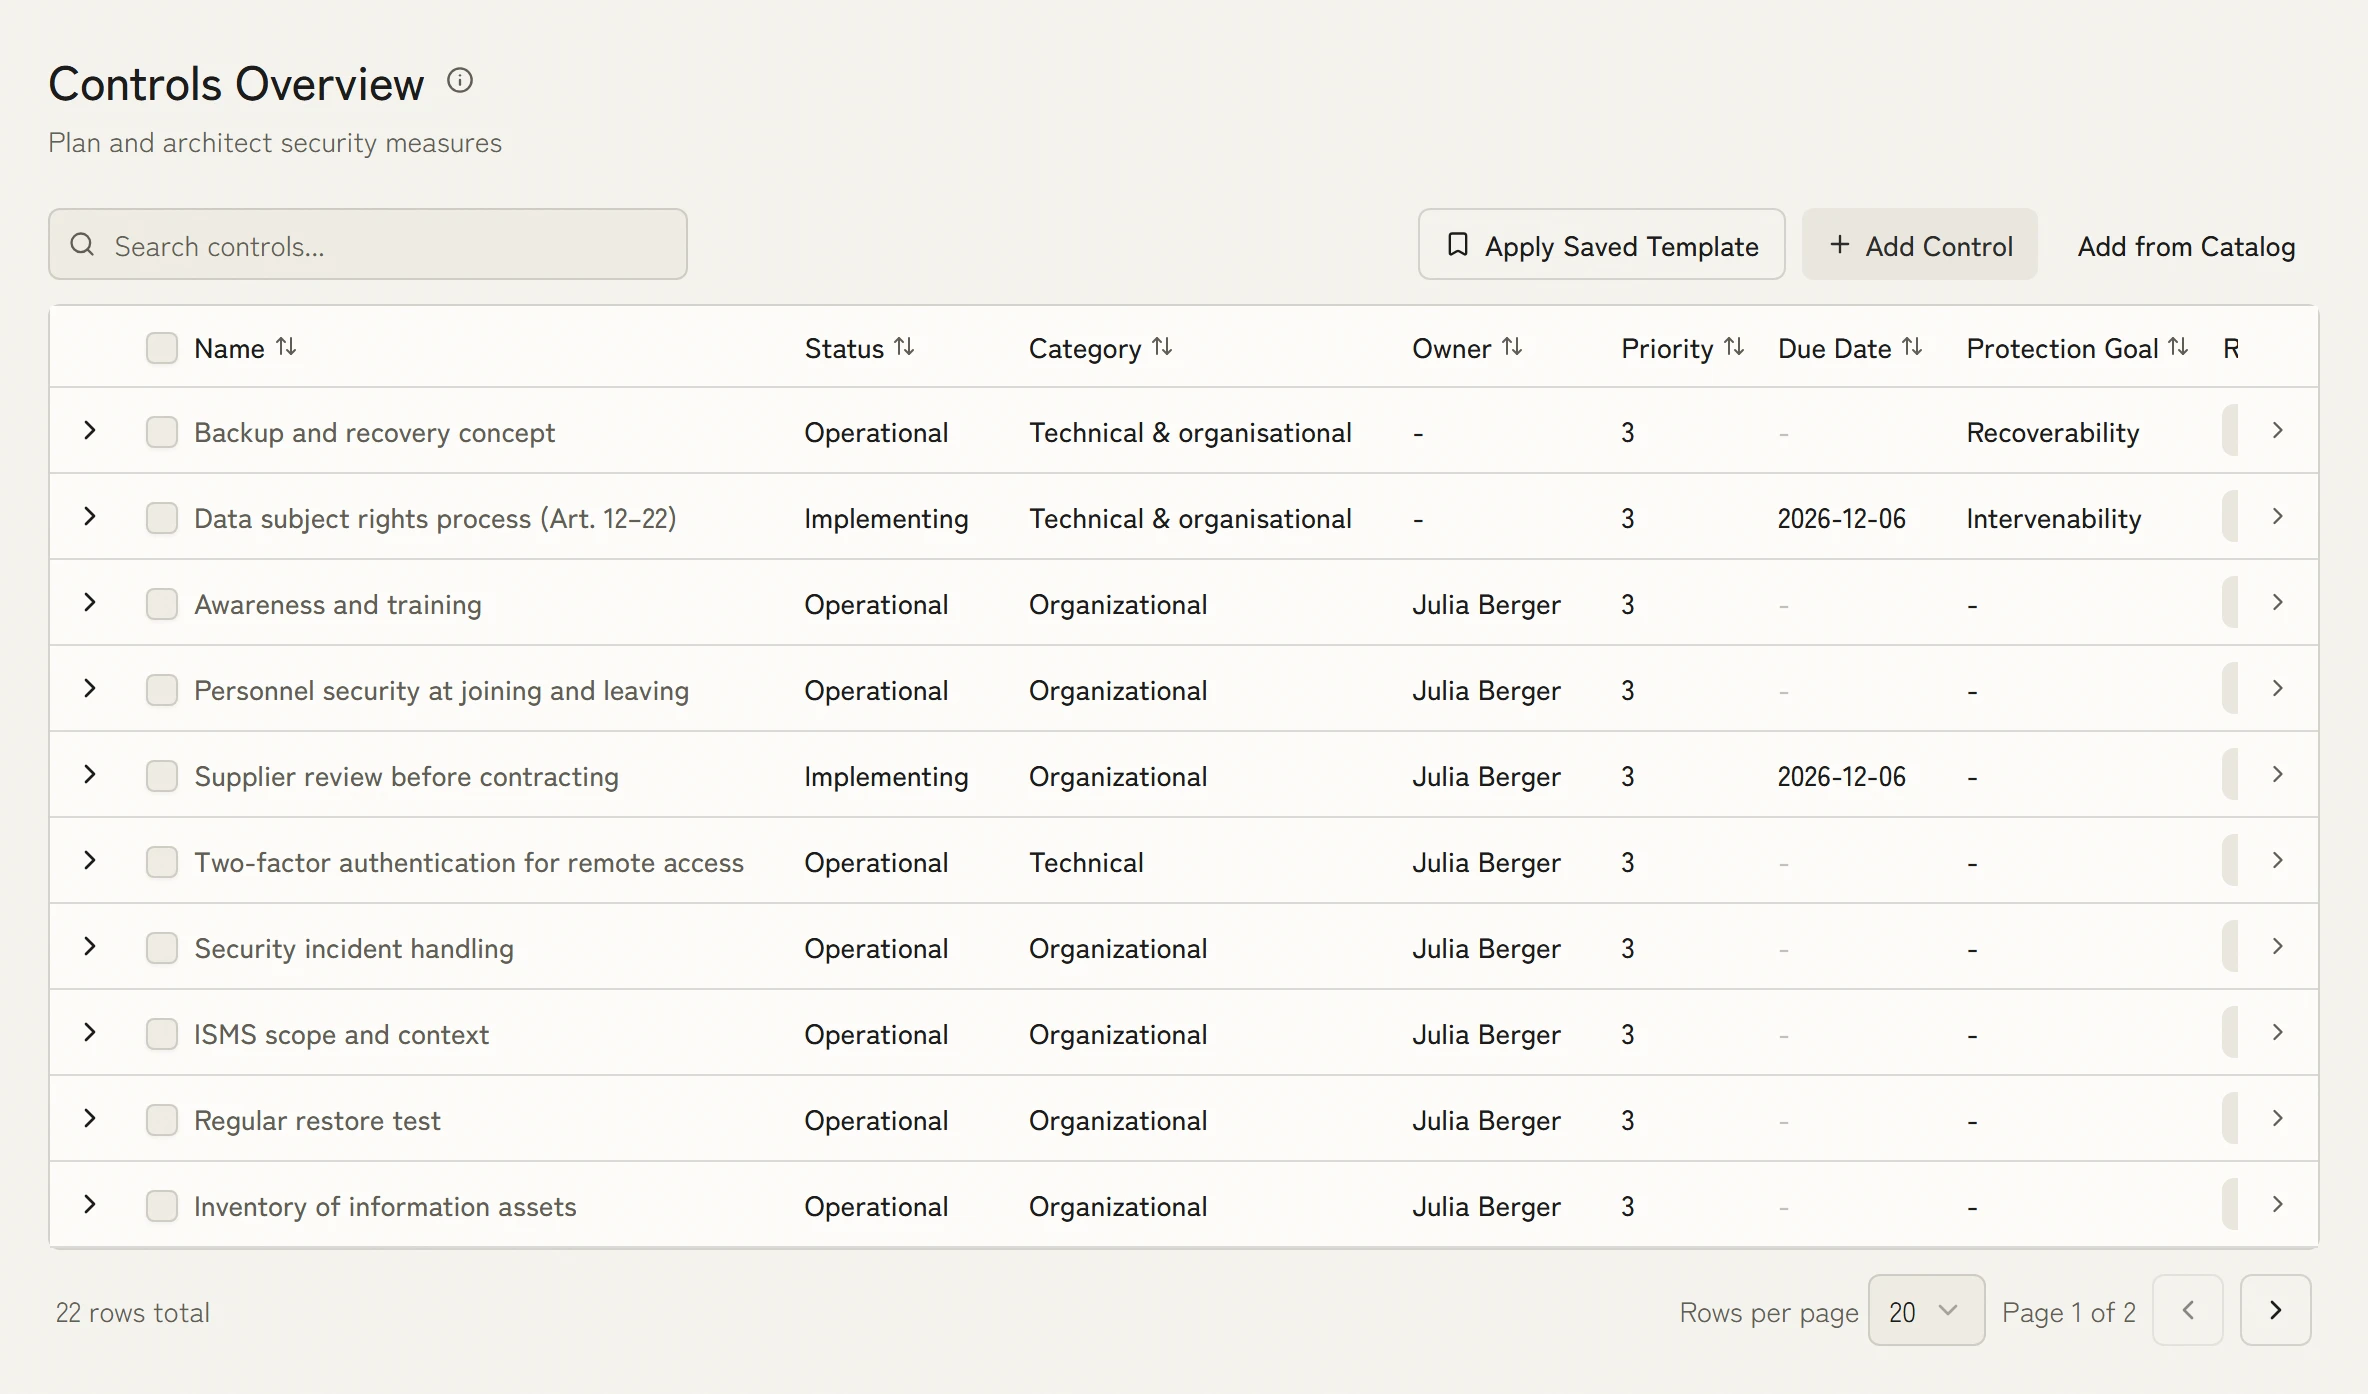
ISO 27001 certification based on IT-Grundschutz
Operate the detailed BSI methodology as ISMS software and connect approved safeguards to ISO 27001 and NIS2 where the requirements genuinely overlap. Each framework keeps its own scope and assessment logic.
4BSI 200-series standards covered (200-1 to 200-4)
Connect IT-Grundschutz with ISO 27001 and NIS2
Connect your Grundschutz programme to ISO 27001, NIS2 and the frameworks that reuse its approved safeguards and evidence.
IT-Grundschutz by company and role
More for IT-Grundschutz
Native Grundschutz-Kompendium integration
KaitoSec ships with the complete IT-Grundschutz-Kompendium structured as machine-readable Bausteine. Every module, requirement, and implementation hint is searchable, assignable, and linkable to your asset inventory. No manual copy-paste from PDFs.
BSI 200-series methodology end to end
BSI Standard 200-1 (ISMS management), 200-2 (IT-Grundschutz methodology), 200-3 (risk analysis), and 200-4 (business continuity) each have dedicated workflow templates. You follow the prescribed methodology step by step, with evidence captured at every stage. 200-4 lives in the same workspace as your ISO 22301 BCMS.
Build the Sicherheitskonzept from accountable records
Bring completed modules, risk decisions and residual-risk documentation together as the basis of the Sicherheitskonzept. The approved, versioned state remains traceable for review.
One mapping, three audits served
Many German organisations carry Grundschutz, ISO 27001 and NIS2 obligations in parallel. KaitoSec maintains bidirectional control mappings between all three. Evidence collected once feeds every framework it belongs to. One preparation carries three audits.
Track implementation per Baustein
Assign Bausteine to your IT systems, applications, and infrastructure components. KaitoSec tracks implementation status per requirement, shows your implementation level across the entire security concept, and generates the Umsetzungsplan for certification.
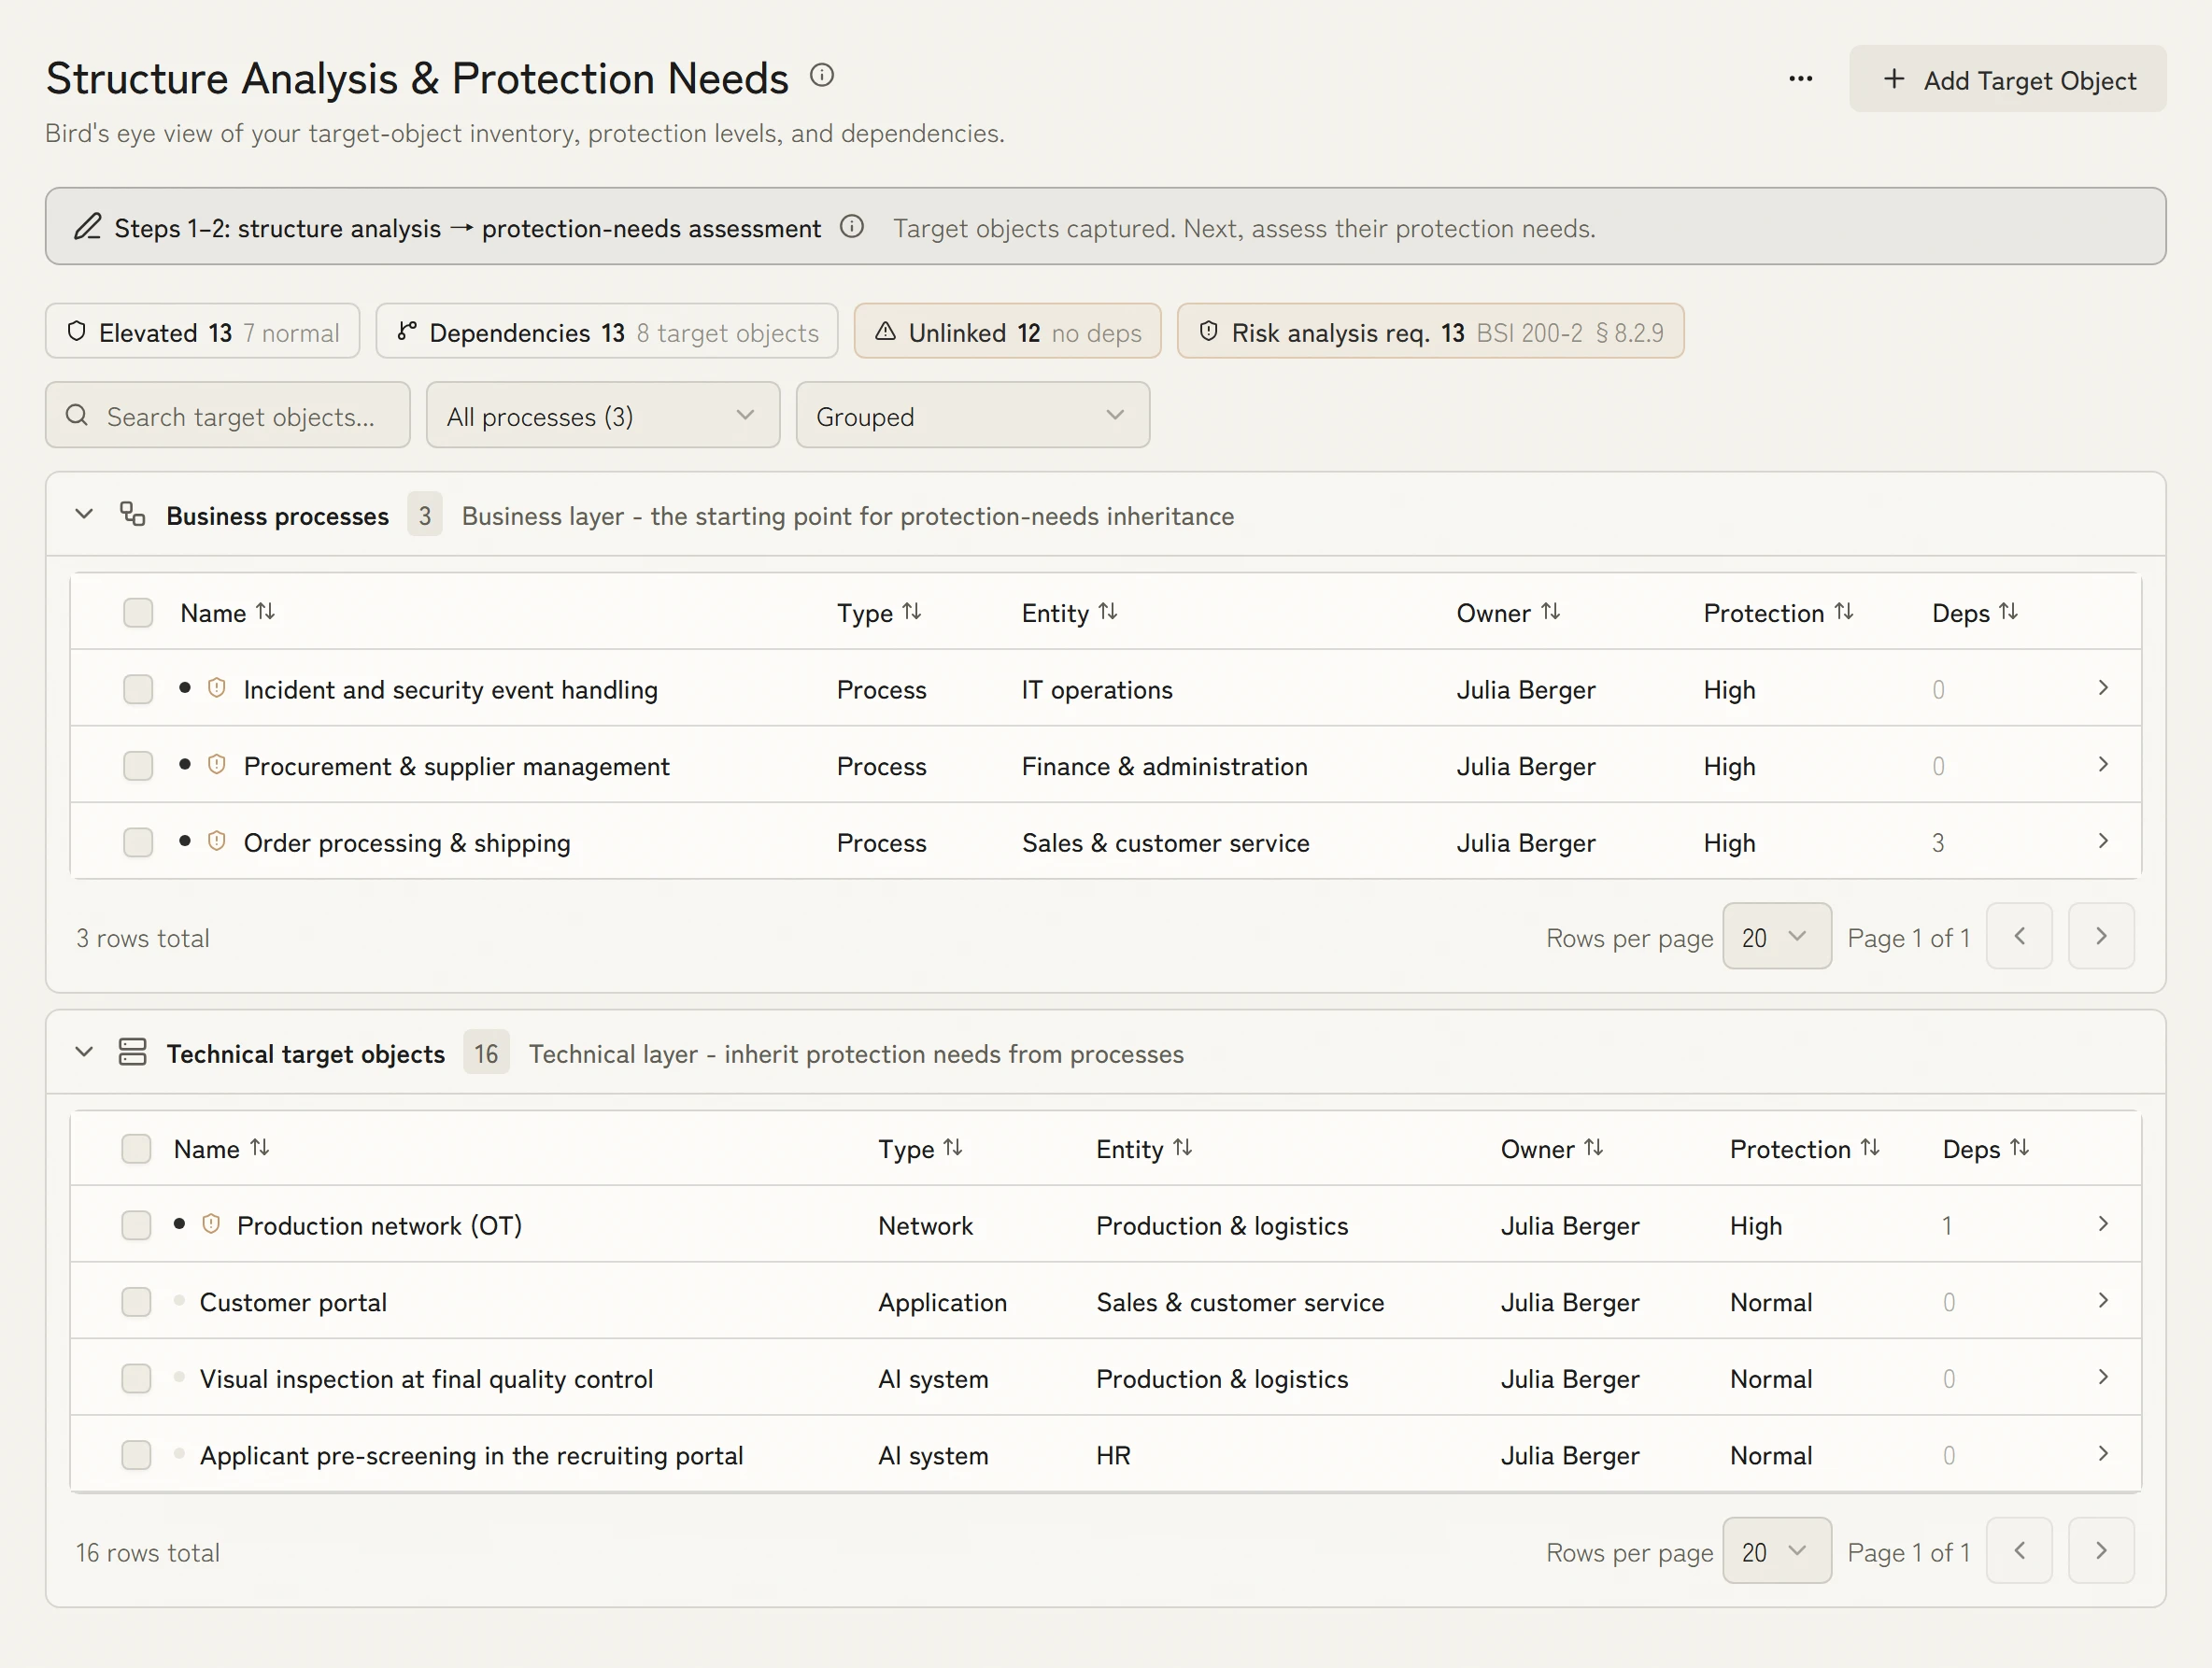
Schutzbedarfsfeststellung (Protection Needs Analysis)
KaitoSec guides the protection-needs assessment for every asset and documents classification as normal, high or very high. Relevant modules and the risk scope are suggested for review.
Cross-Mapping to ISO 27001 and NIS2
Map Grundschutz, ISO 27001 and NIS2 to the same controls where requirements genuinely align. Approved evidence can then be reused without hiding differences between the frameworks.
Structural analysis and modelling
Record the information domain, applications, systems, rooms, networks and dependencies, then apply the relevant Bausteine. The model remains connected to owners, risks and evidence.
Frequently asked questions about BSI IT-Grundschutz
Which software is suitable for BSI IT-Grundschutz?
BSI IT-Grundschutz software must represent the Compendium with all its Bausteine and support structural analysis, protection-needs assessment, modelling, the Grundschutz Check and risk analysis under BSI 200-3. KaitoSec covers all these steps through to implementation planning and uses migration to import existing registers from Excel, verinice or HiScout. Our BSI IT-Grundschutz starter guide walks through them in order.
What is the difference between Basic, Standard and Core Protection?
Basic Protection implements only the basic requirements; Standard Protection is the route to an ISO 27001 certificate based on IT-Grundschutz, while Core Protection focuses on the most critical assets. KaitoSec lets you choose the approach for each information domain.
How does modelling work in IT-Grundschutz?
In IT-Grundschutz modelling, the relevant Compendium Bausteine are assigned to the target objects from the structural analysis. The KaitoSec agent proposes the mapping and reports unmodelled Bausteine as findings, as shown in the import demo.
Is KaitoSec an alternative to verinice and HiScout?
Yes. KaitoSec imports exports from both tools and retains target objects, Bausteine and status. The tool comparison explains what changes when you switch, and migration describes the process. This comparison of IT-Grundschutz tools goes deeper on verinice and HiScout specifically.
What does Grundschutz++ mean, and is KaitoSec prepared for it?
Grundschutz++ is the BSI's machine-readable evolution of IT-Grundschutz. KaitoSec works with OSCAL-based catalogues and is therefore designed for machine-readable requirements, which is particularly relevant for municipalities moving from WiBA to Grundschutz++.

Your IT-Grundschutz plan in thirty minutes.
In the demo we walk through structure analysis, protection needs, modelling and the check. You leave knowing which target objects come first.