
Vendor Management: assessments that don't get stuck in an inbox.
You send questionnaires from KaitoSec, the answers add up to a result per area, and open points become tasks with an owner. Contract, data processing and dependencies sit on the same vendor.

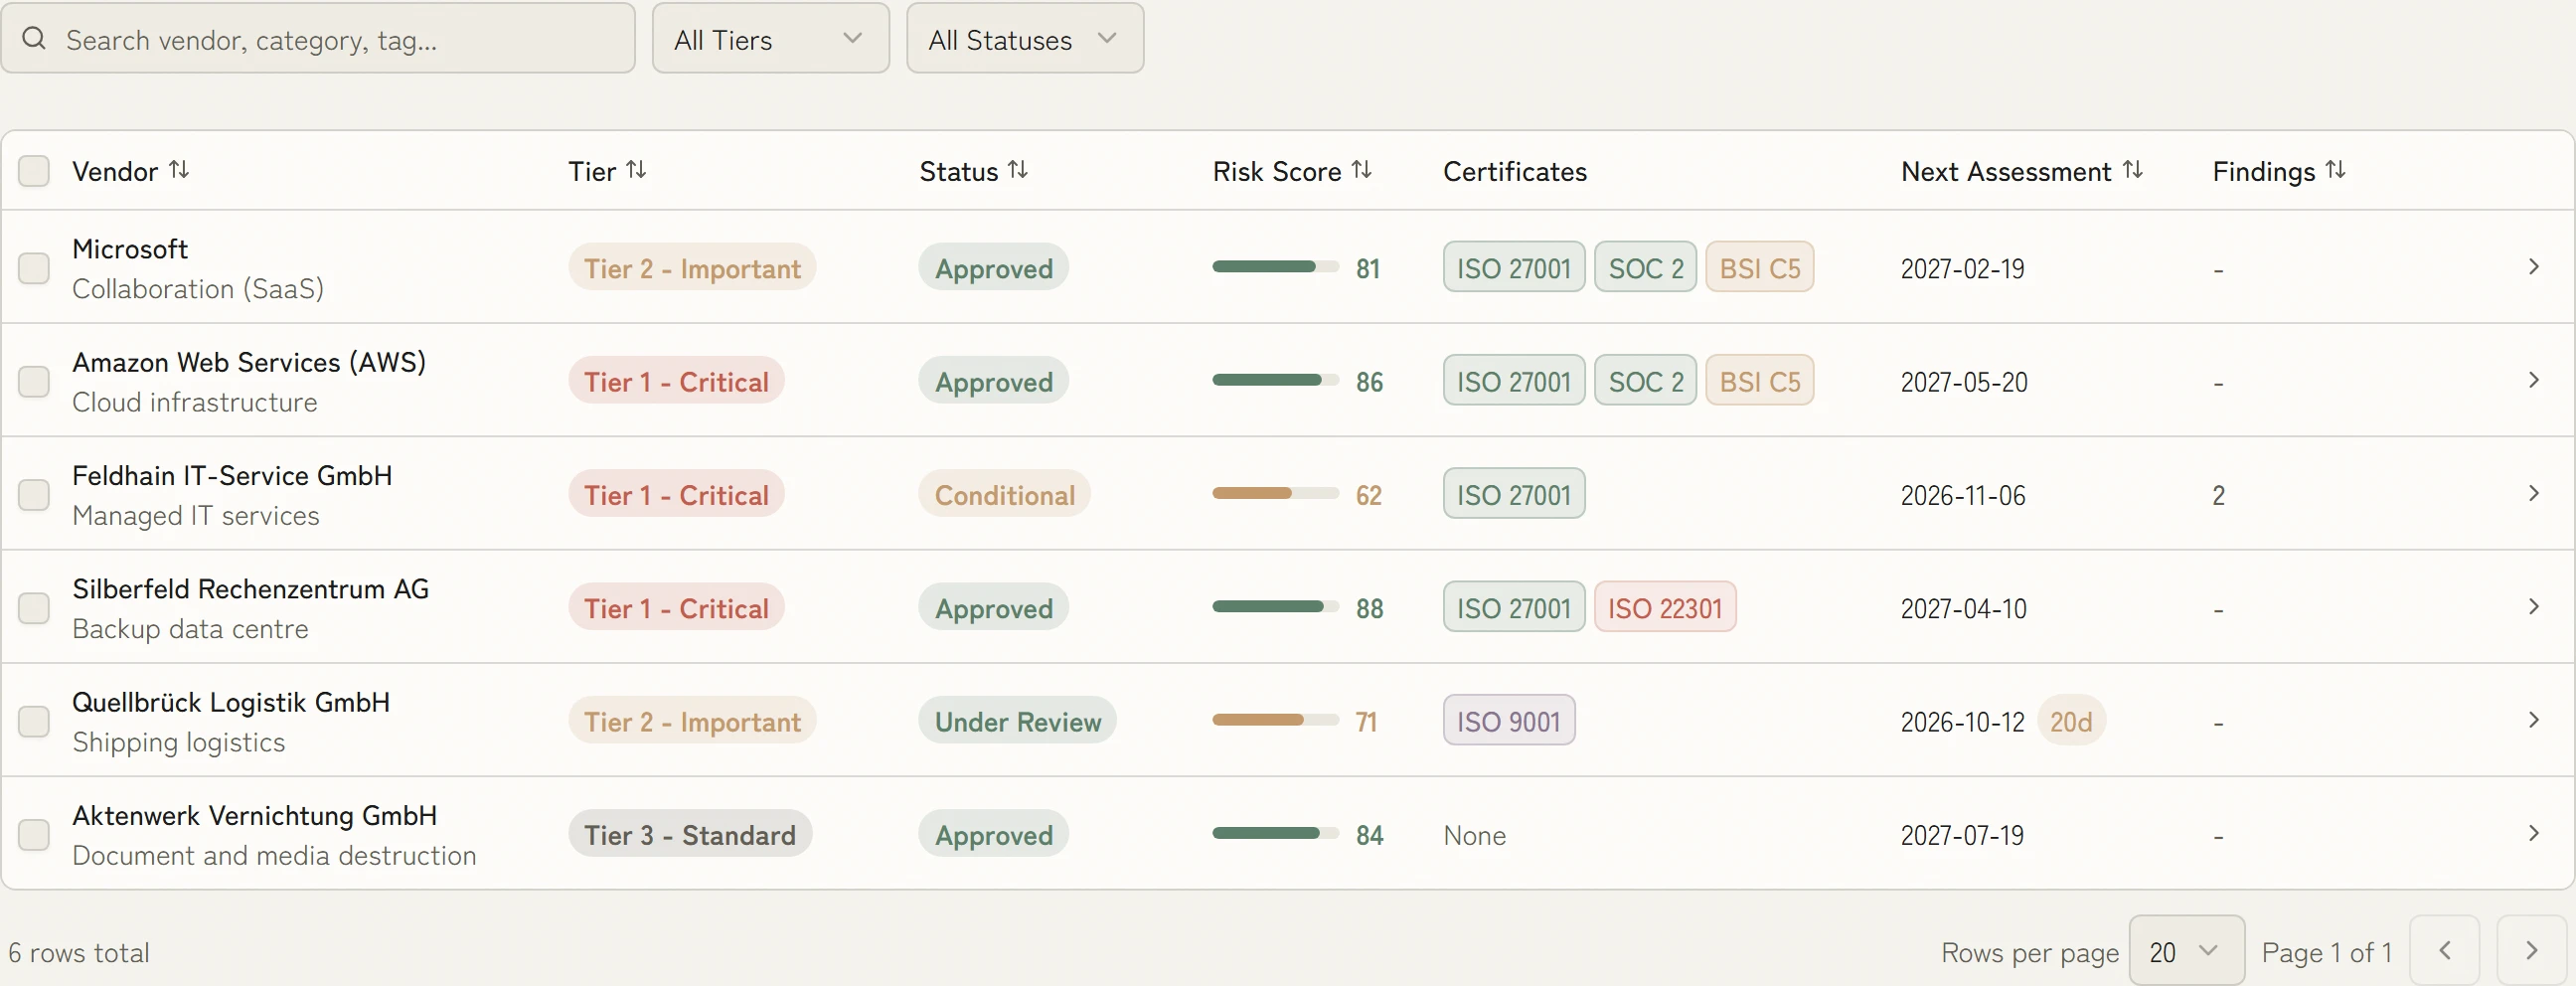


 5.0 out of 5
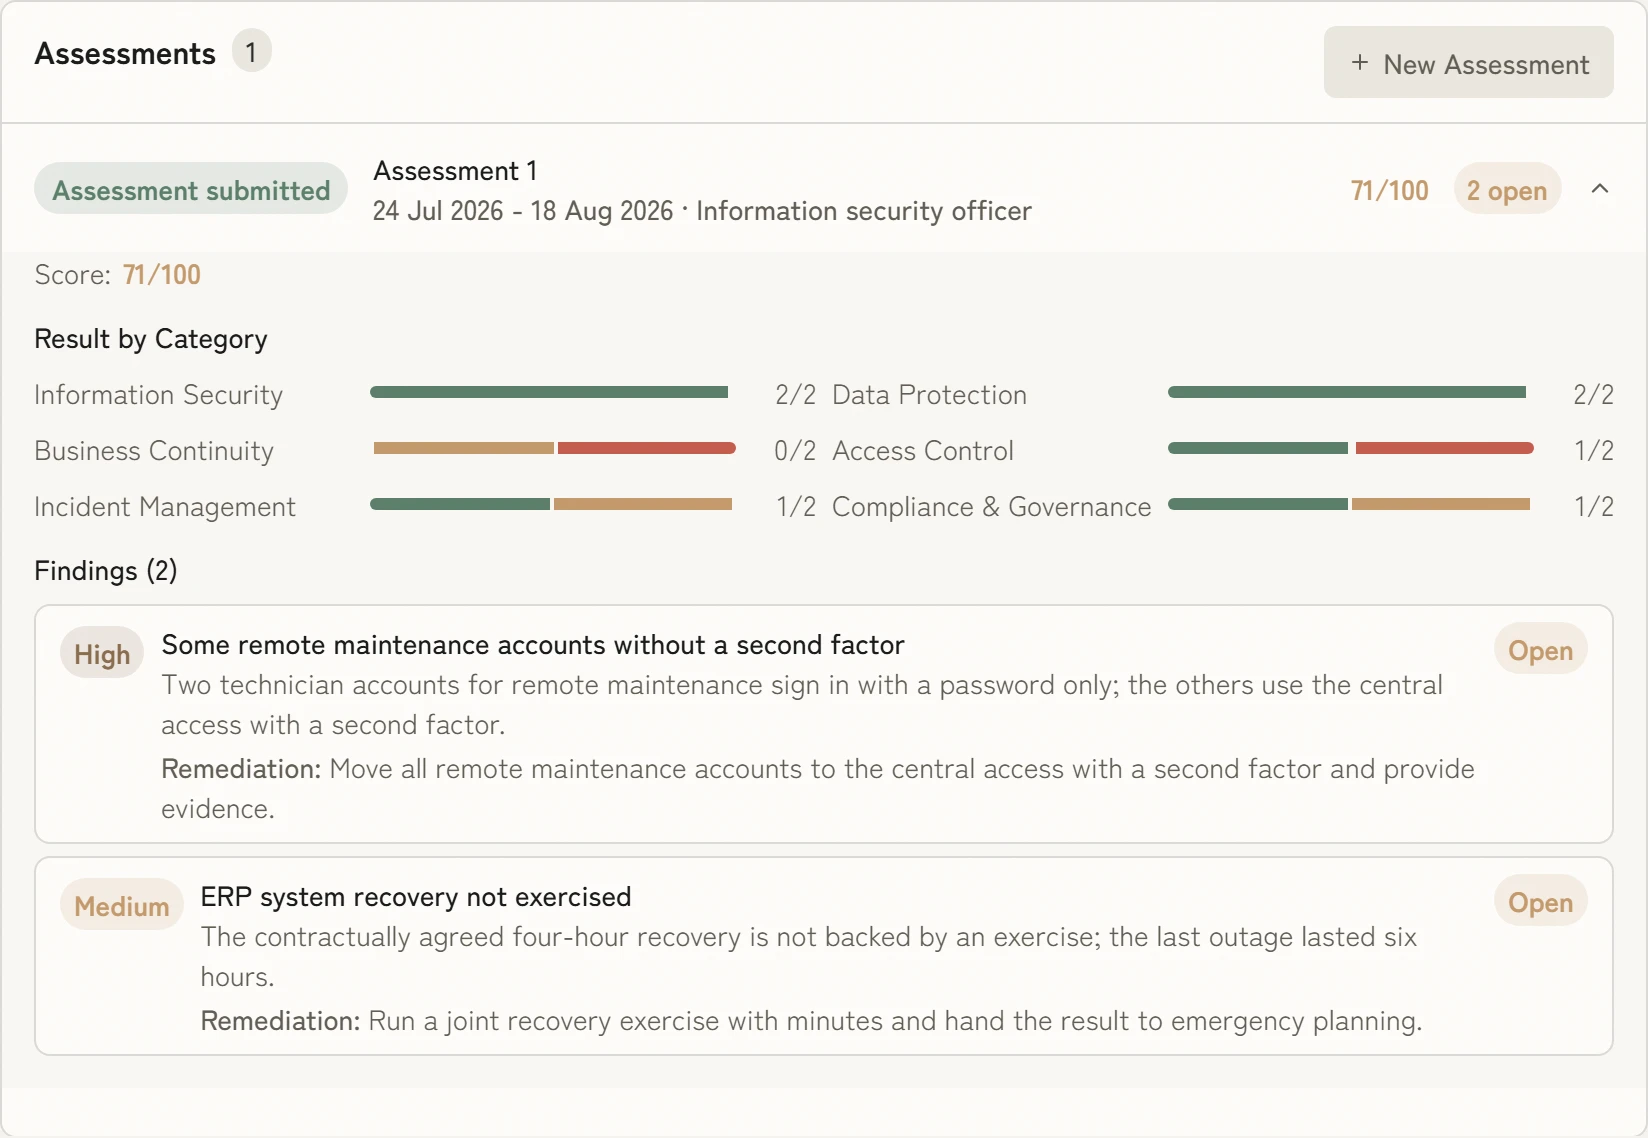
The result per area at a glance
Questionnaire, data criticality, operational dependency and contractual safeguards add up to one assessment. Open findings, on remote maintenance or recovery for example, sit underneath, each with its action.
Book a demo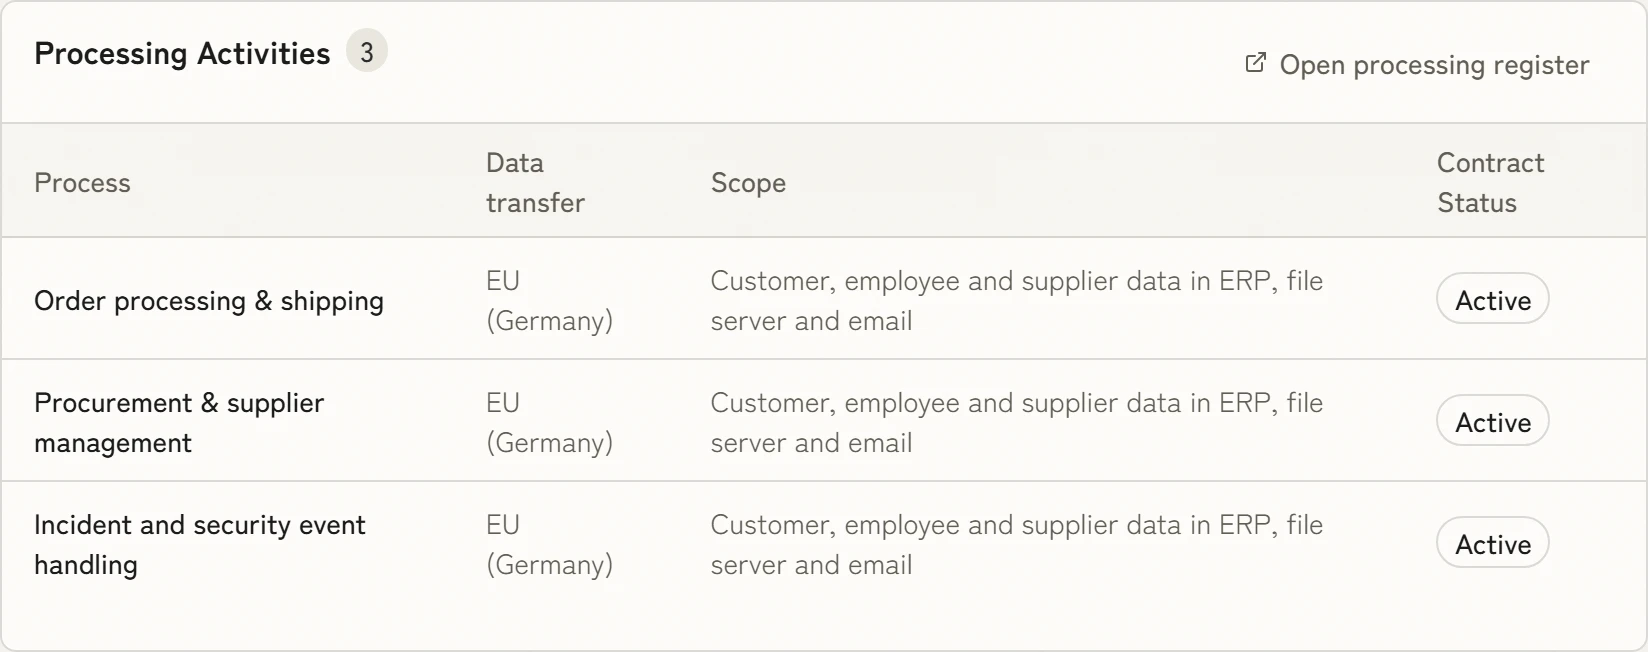
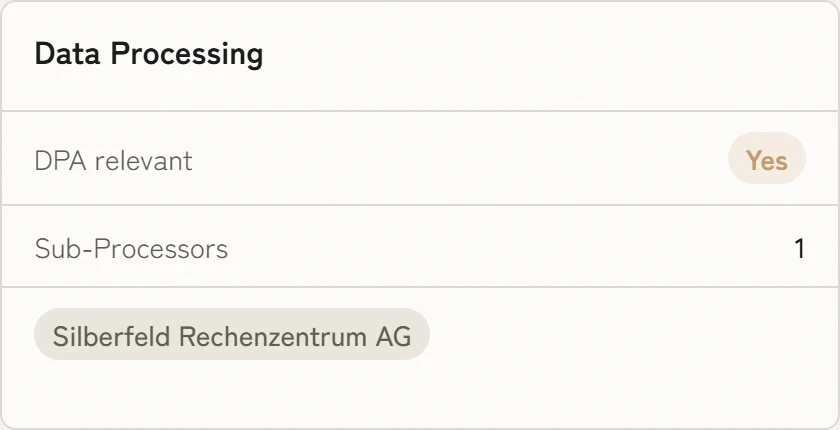
Data processing without an extra spreadsheet
You see which processing activities a provider handles and which sub-processors it uses. Both stay linked to your record of processing, without a parallel spreadsheet.
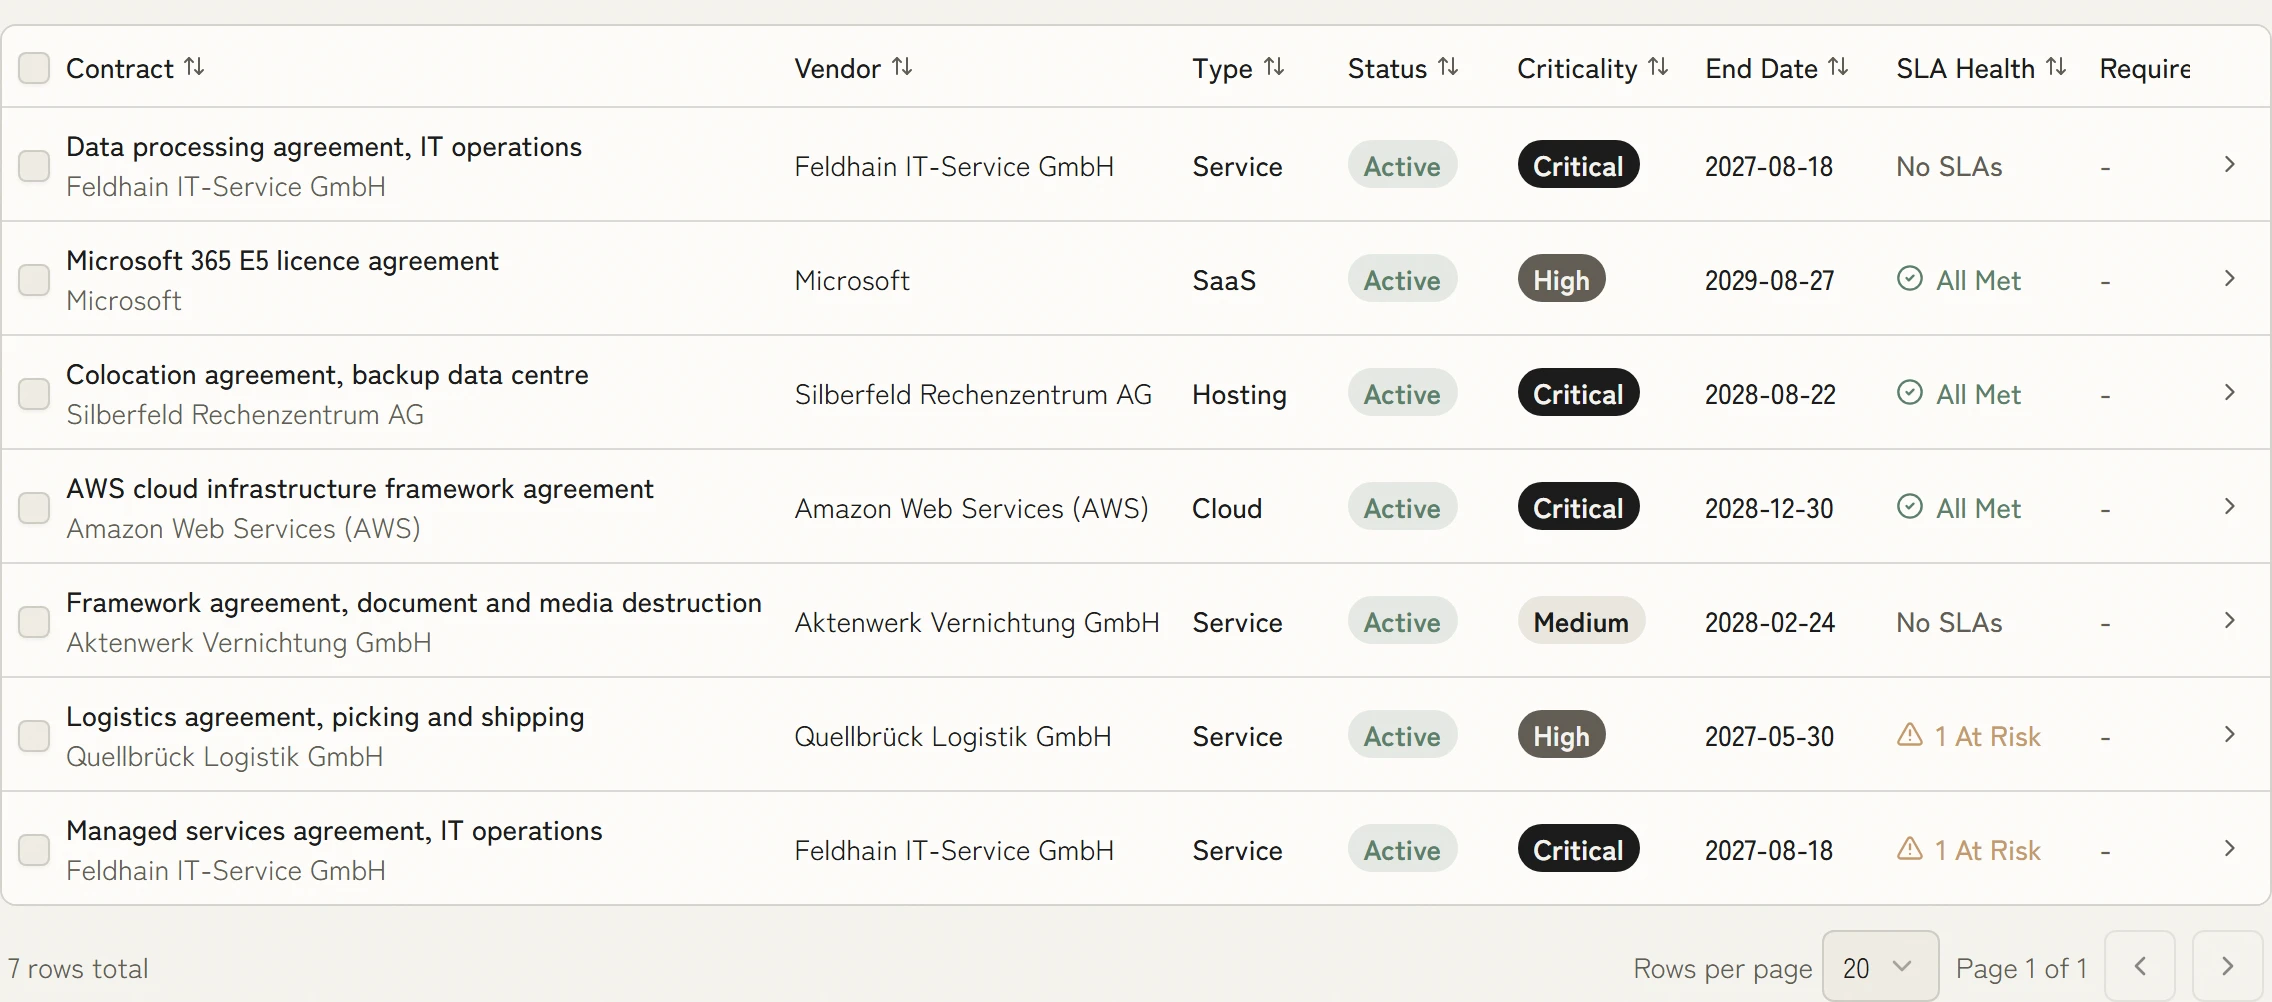
Book a demoSLAs at risk show up early
The contract register shows term, criticality and the state of the SLAs. KaitoSec warns the owners before expiry, and contracts at risk sit at the top.
- pre-mapped controls
- 100+100+
- of evidence created as the work is done
- 100 %100 %
- faster than manual work
- 10×10×
- management systems, one data model
- 4 in 14 in 1
What KaitoSec also does
These sit in the core of the platform and apply to every module.
Implemented once, done for every requirement.
More than 100 controls are already mapped to ISO 27001, NIS2, DORA and other requirements. You implement a control once and evidence it once. Every further requirement it covers costs no extra work.
You review and approve instead of filling empty fields.
Agents prepare the risk analysis, the statement of applicability and actions from audit reports. Every result is ready for approval. A person still makes the decision.
Nothing left to collect before the audit.
Evidence is created as the work gets done: a tested backup supplies its recovery time, a completed review its result. Your evidence is current every day, not just in the week before the audit.
Suppliers and contracts without prior knowledge.
In simple mode your team records providers and contracts in order, and every step says what to do and why. Anyone who needs more detail switches to expert mode and sees the same suppliers with assessments and dependencies.
You maintain each process only once.
Information security, business continuity management, data protection, AI governance and supplier management all work from the same process data. Every change takes effect in every system at once. Duplicate entry and conflicting registers go away.

Ask Chris how this would work for you.
Co-founder and CEO of KaitoSec. He walks through your case with you, live in the product.
Book a demo
The data for your vendor management is already there.
100+ integrations
All integrations















FAQ
How does KaitoSec help with GDPR Article 28 compliance?
Every processor and sub-processor is tracked in a structured register linked to the processing activities they support. DPA status, expiry, standard contractual clauses and sub-processor changes are recorded per vendor, with alerts before renewal becomes urgent.
Can vendors complete questionnaires without a KaitoSec account?
Yes. Vendors receive a secure link to a hosted form and submit responses without creating an account. Submissions are ingested directly and linked to the vendor risk profile, with follow-up routed to your team.
How does vendor management support DORA?
DORA requires financial entities to maintain a register of ICT third-party service providers and to perform regular risk assessments. KaitoSec is structured to meet those requirements, including the contractual content checklist and concentration risk view, and produces the supervisory reporting artefacts.
Can we track vendor incidents and service disruptions?
Yes. Vendor-related incidents log against the vendor record and feed your incident management workflow. The same data drives NIS2 supply-chain incident reporting and DORA major-incident analysis without parallel paperwork.

Less work in your vendor management.
One critical vendor is enough. In thirty minutes you see how KaitoSec links it to its contract, its assessment and the processes that depend on it.