
ISO 27001 software: build, operate and certify your ISMS
Annex A, statement of applicability, risks and evidence in one tool instead of spreadsheets. What you build for ISO 27001 then counts for NIS2, DORA and further standards too.



 5.0 out of 5
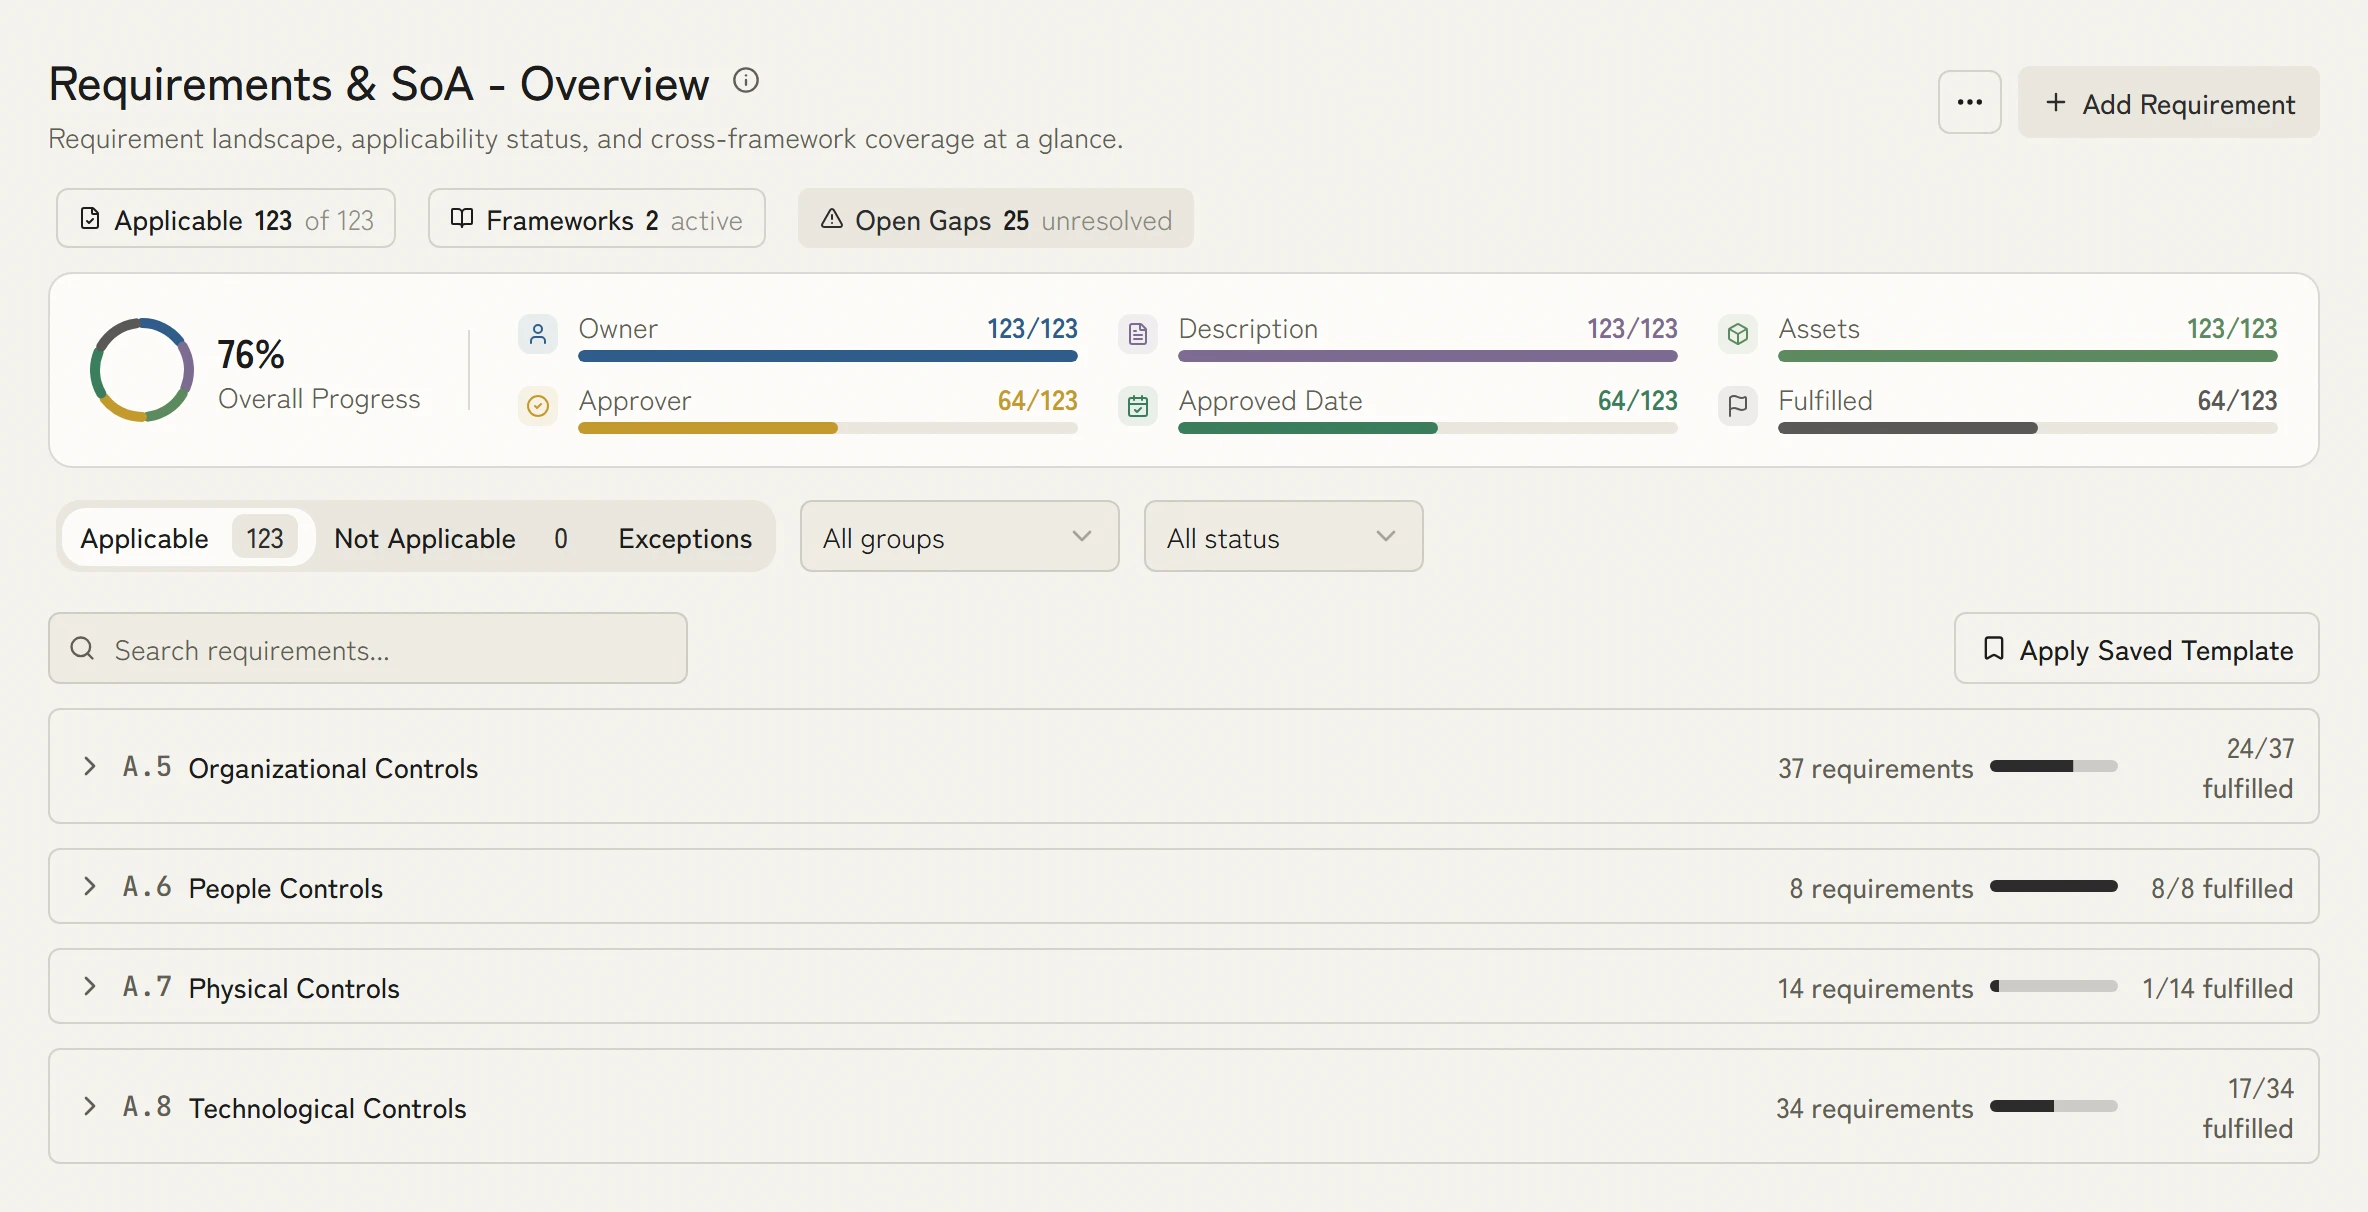
Maintain the SoA and Annex A automatically
Applicability, justification, implementation status and evidence stay together for all 93 Annex A controls. Changes update the working SoA instead of starting another spreadsheet round. Our guide to ISO 27001 certification costs breaks down what a project like this typically costs.
93ISO 27001:2022 Annex A controls pre-loaded
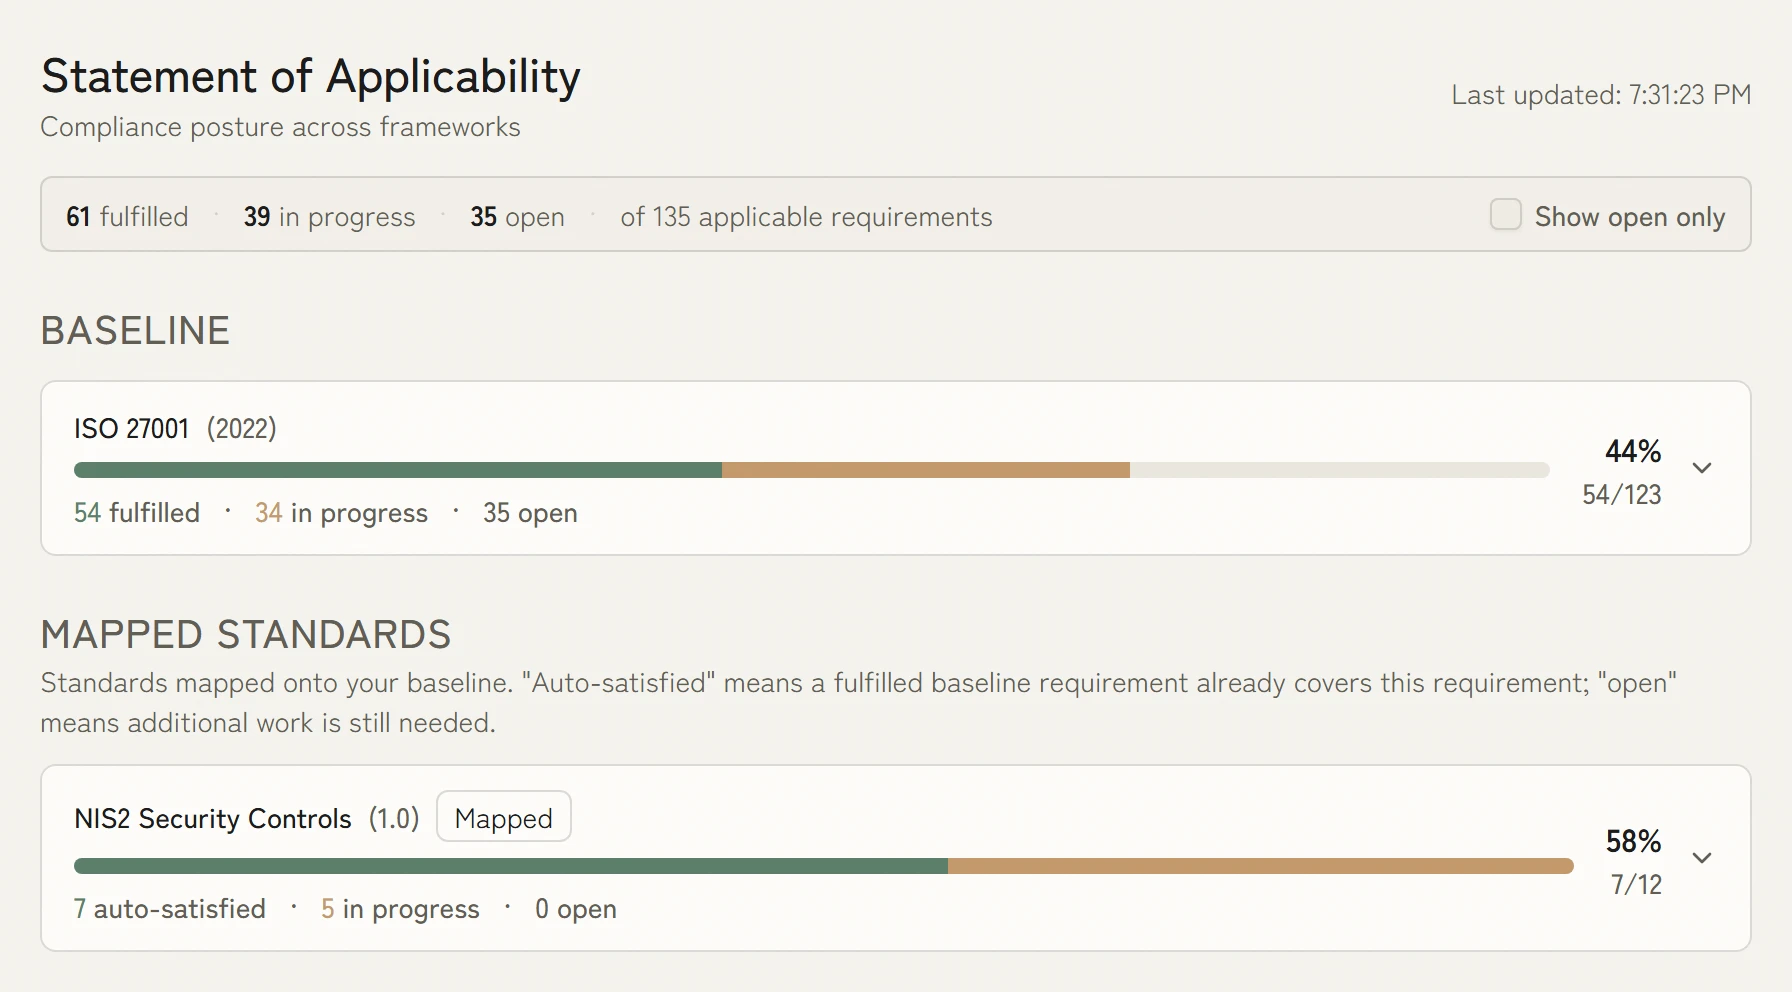
Risk assessment under ISO 27005
Assess risk in context, document treatment and residual risk, assign accountability and set the next review. The ISO 27005 view remains connected to the controls selected for treatment.
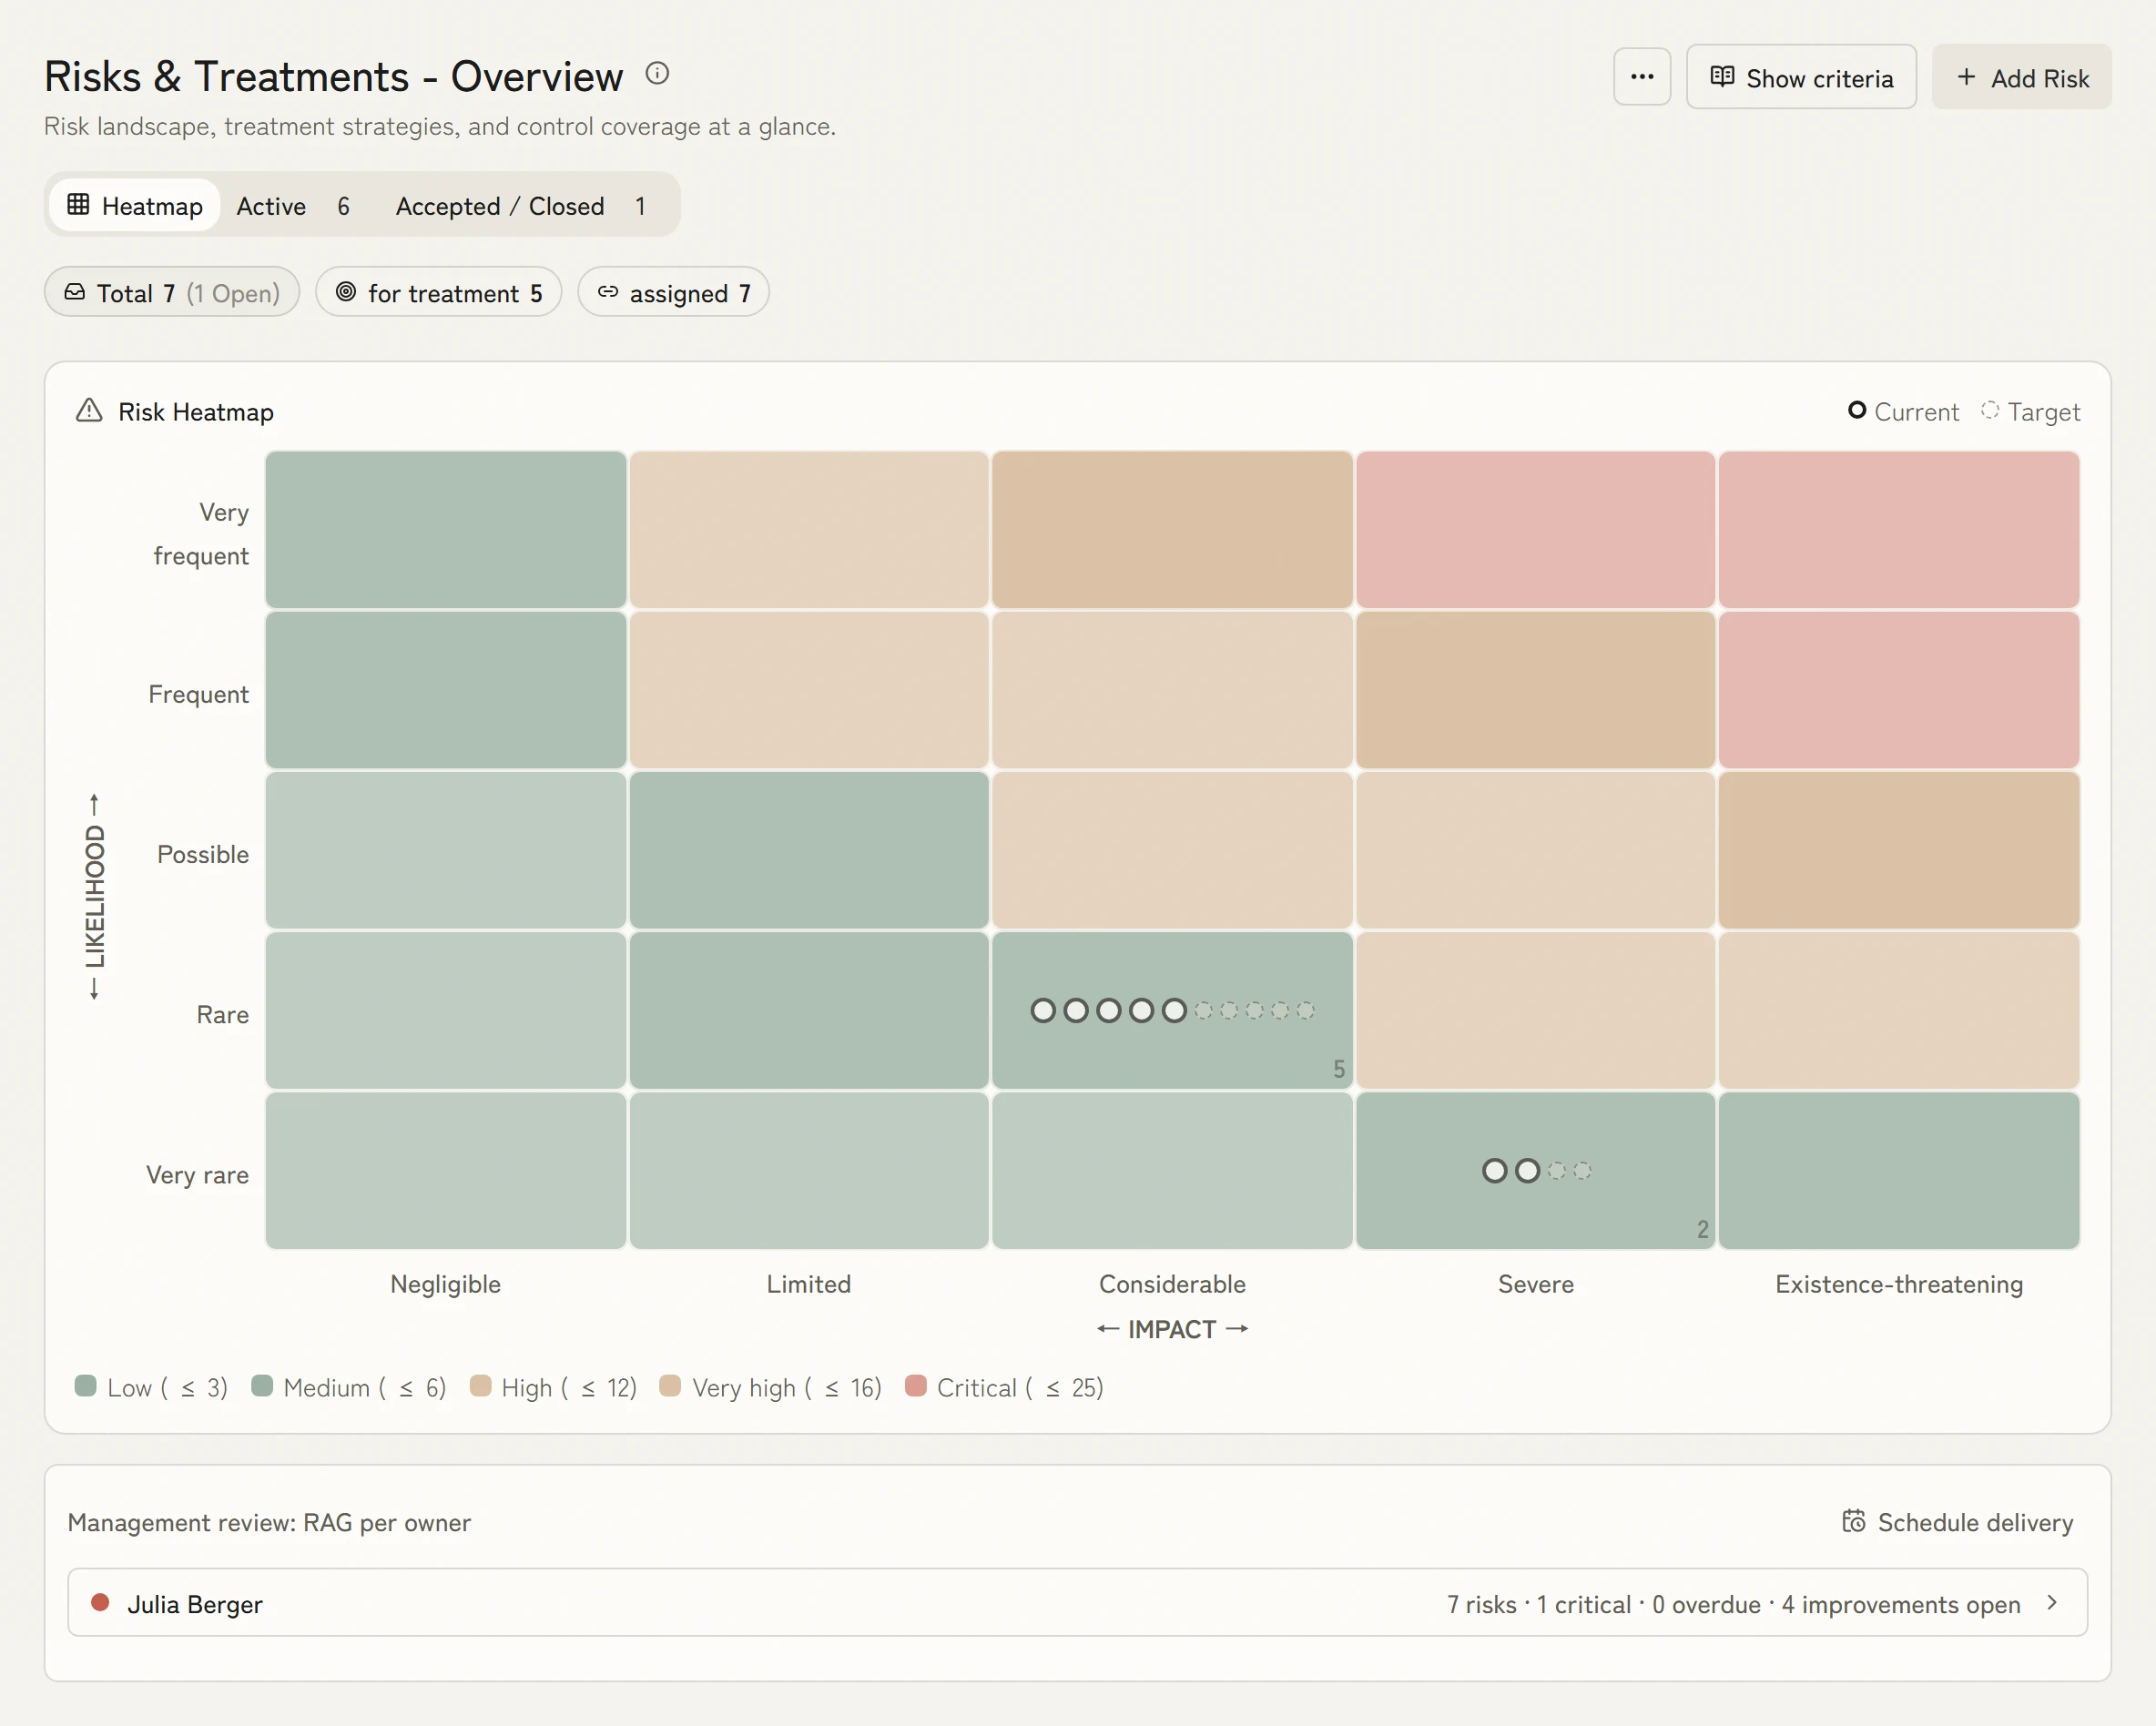
Audit evidence without spreadsheets
Versioned policies, approved evidence and a scoped auditor view keep the audit trail on the record. Reporting, mapping and risk work use the same current state.
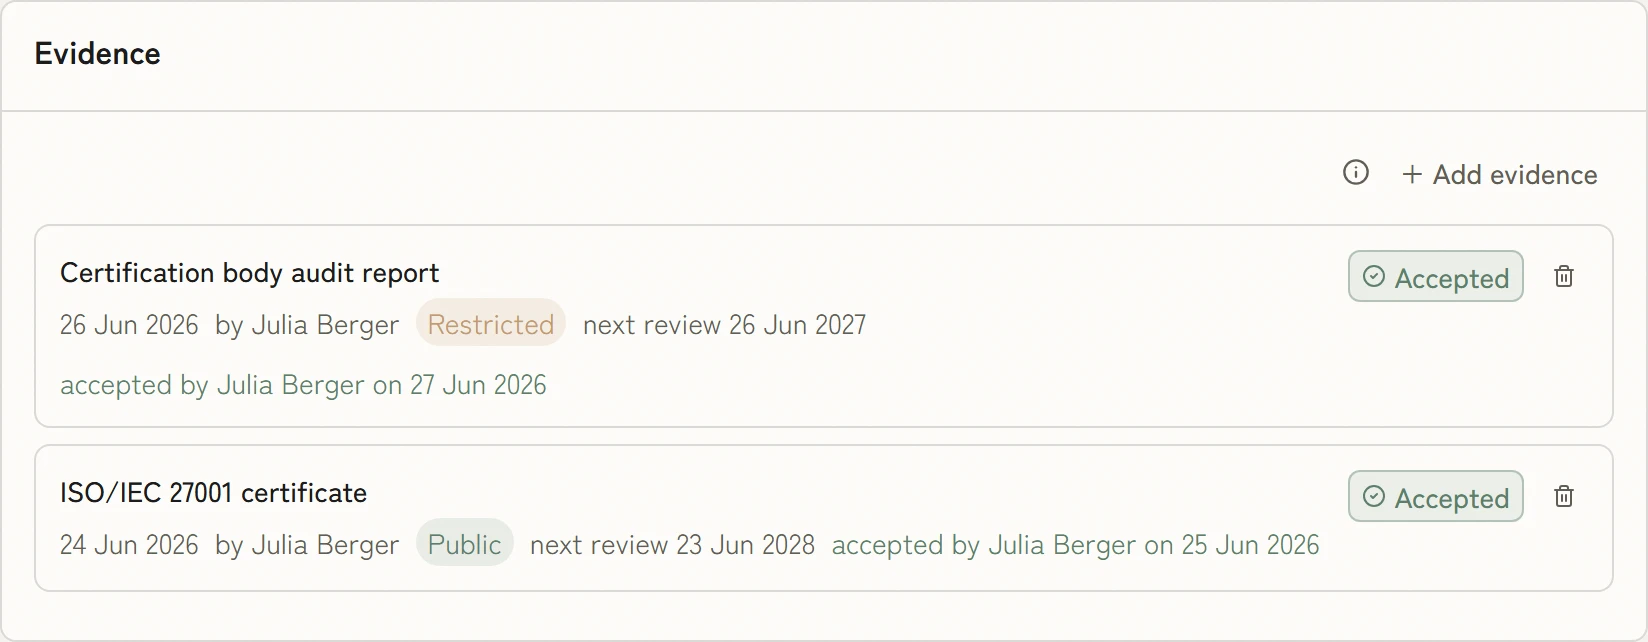
From ISO 27001 to NIS2 and DORA without duplicate work
KaitoSec keeps approved controls and evidence in one ISMS software workspace and maps them to NIS2, DORA and other frameworks only where their substance overlaps. Framework-specific wording and decisions remain visible.
4 systemsISMS controls also feed BCMS, DSMS, AIMS evidence
Connect ISO 27001 with other standards
Extend the same ISMS working state to the standards and obligations that apply to your organisation.
- BSI IT-GrundschutzGerman baseline IT securityLearn more
- NIS2EU cybersecurity directiveLearn more
- DORAFinancial sector resilienceLearn more
- TISAXAutomotive infosecLearn more
- NIST CSFUS cybersecurity frameworkLearn more
- SOC 2Trust criteria for SaaSLearn more
ISO 27001 by company and role
More for ISO 27001
Gap analysis with existing context
Map the asset inventory, policies and existing controls to your ISO 27001:2022 scope. KaitoSec prepares open items with owner and priority for professional review.
Living Statement of Applicability
Your Statement of Applicability brings applicability, justification, implementation and evidence together. Changes are versioned and your certification body can receive controlled read access to the approved state when required.
ISMS policy templates
Start with a structured policy template, adapt it to your organisation and connect the approved version to controls, versions and acknowledgements.
Control Implementation Tracker
Every Annex A control has a dedicated workspace where you assign owners, attach evidence, and track implementation status. Overall progress toward certification readiness is visible to the whole team.
Risk Treatment Workflows
Link risks directly to controls and define the treatment: accept, mitigate, transfer, or avoid. KaitoSec requires documented decisions and reminds owners when risk reviews are overdue.
Auditor Access Portal
Give your certification body scoped read access to an approved state of your ISMS evidence. Context, version and accountability stay with the evidence.
What ISO 27001:2022 requires
ISO 27001:2022 requires a managed ISMS: scope, risk-based decisions, objectives, controlled information, reviews and continual improvement. Annex A supports treatment; it does not replace the management system.
7clauses in the management system
- Clause 4Context
- Clause 5Leadership
- Clause 6Planning
- Clause 7Support
- Clause 8Operation
- Clause 9Evaluation
- Clause 10Improvement
93controls in Annex A
- organisational37
- people8
- physical14
- technological34
Frequently asked questions about ISO 27001 certification
What software do I need for ISO 27001?
For ISO 27001, you need a tool that keeps context, risk assessment, the Statement of Applicability, Annex A controls and evidence together. KaitoSec provides exactly that as ISMS software, without a parallel Excel environment. Our ISO 27001 checklist breaks the whole certification path into concrete steps.
What is the Statement of Applicability (SoA), and how do you maintain it?
The Statement of Applicability (SoA) lists all 93 controls in ISO 27001:2022 Annex A and explains whether and how each is implemented. In KaitoSec, it is generated automatically from risk management and control status, so it stays current and audit-ready.
How long does ISO 27001 certification take?
ISO 27001 certification typically takes 6 to 12 months, depending on maturity and scope. KaitoSec measurably shortens the ISMS build; the timetable to the audit still depends on the certification body. For SMEs without a security team, see ISMS for SMEs.
Can the same ISMS fulfil ISO 27001 and NIS2?
ISO 27001 and NIS2 can share the same ISMS. The measures in Section 30 BSIG overlap substantially with Annex A. Through compliance mapping, one implementation counts for NIS2, DORA and ISO 27001 at the same time; in our data, existing controls cover around 78% of ISO requirements.
ISO 27001 or BSI IT-Grundschutz: which fits us?
ISO 27001 is internationally recognised and risk-based; IT-Grundschutz is more detailed and is often required in public authorities and critical infrastructure. The two can also be combined as ISO 27001 based on IT-Grundschutz. Compare the approaches under BSI IT-Grundschutz.
What is ISO 27001, and what does ISO/IEC 27001:2022 mean?
ISO/IEC 27001 is the international standard for an information security management system (ISMS). It defines how an organisation identifies, treats and evidences risks to the confidentiality, integrity and availability of its information. The 2022 edition replaces the 2013 one: Annex A was condensed to 93 controls in four themes, and eleven controls such as threat intelligence and cloud security were added. Our article ISO 27001:2022 explained simply covers the basics.
How does ISO 27001 certification work?
An accredited certification body audits in two stages: stage 1 checks documentation and readiness, stage 2 checks that the ISMS works in day-to-day operation. The certificate is valid for three years, with annual surveillance audits and a recertification audit at the end of the cycle. Before the first audit the standard expects an internal audit and a management review to have taken place.

Your ISO 27001 plan in thirty minutes.
In the demo we walk through where you stand: scope, Annex A, risks and evidence. You leave with a plan up to the audit.