
NIST CSF 2.0 implemented once, reported many times
The six functions of CSF 2.0 sit on the same controls as ISO 27001, IT-Grundschutz and NIS2. You implement once and report against CSF without keeping a separate maturity spreadsheet.



 5.0 out of 5
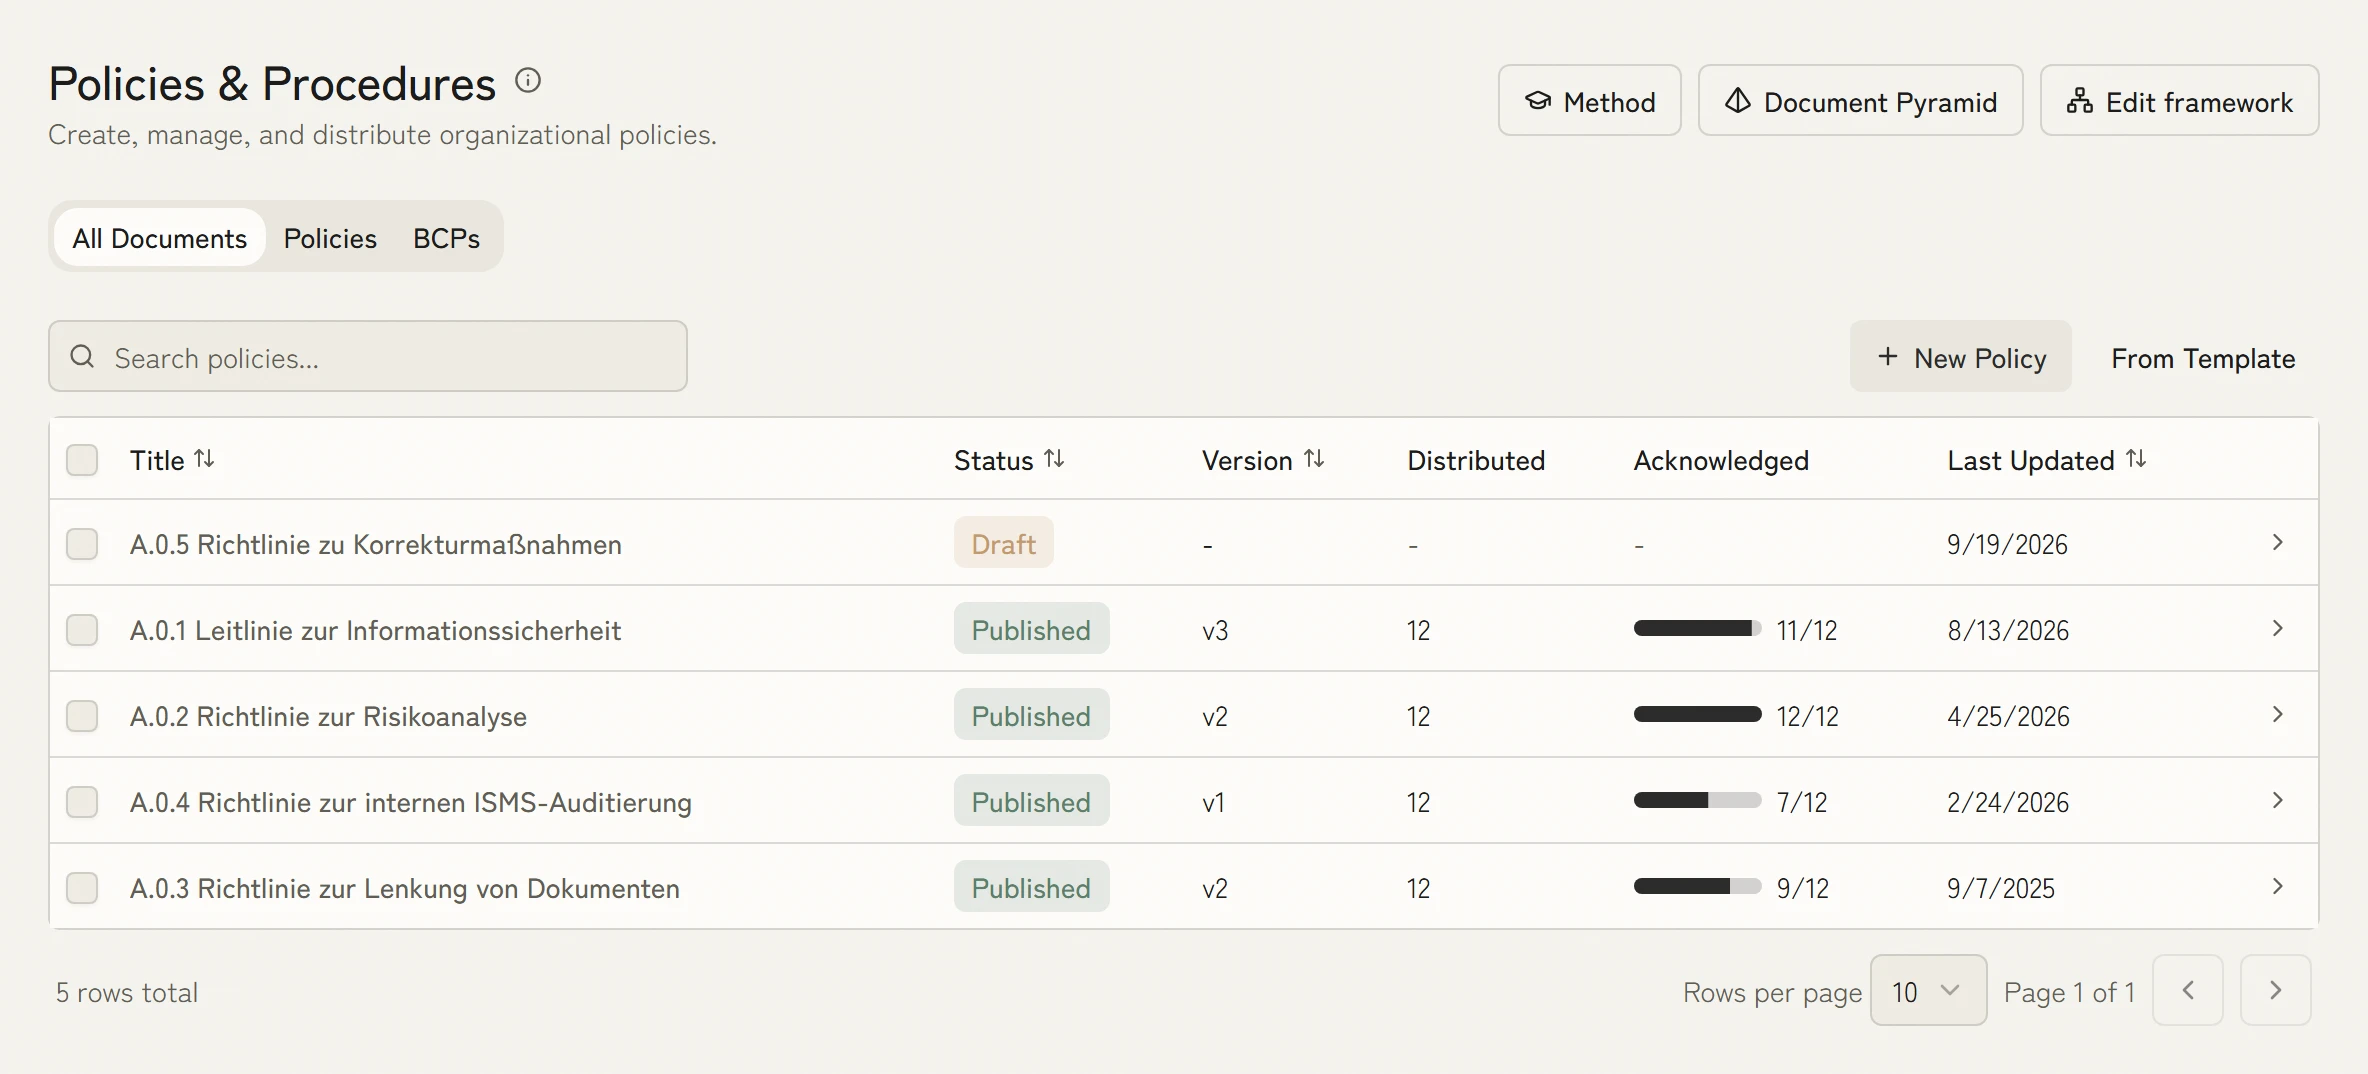
Govern comes out of policies and acknowledgements
The top-level policy and the policies below it carry status, version and the number of staff who acknowledged the current edition. That is the Govern evidence, and it comes out of day-to-day operation rather than out of a separate maturity spreadsheet.
6 functionsGovern (new in 2.0), Identify, Protect, Detect, Respond, Recover
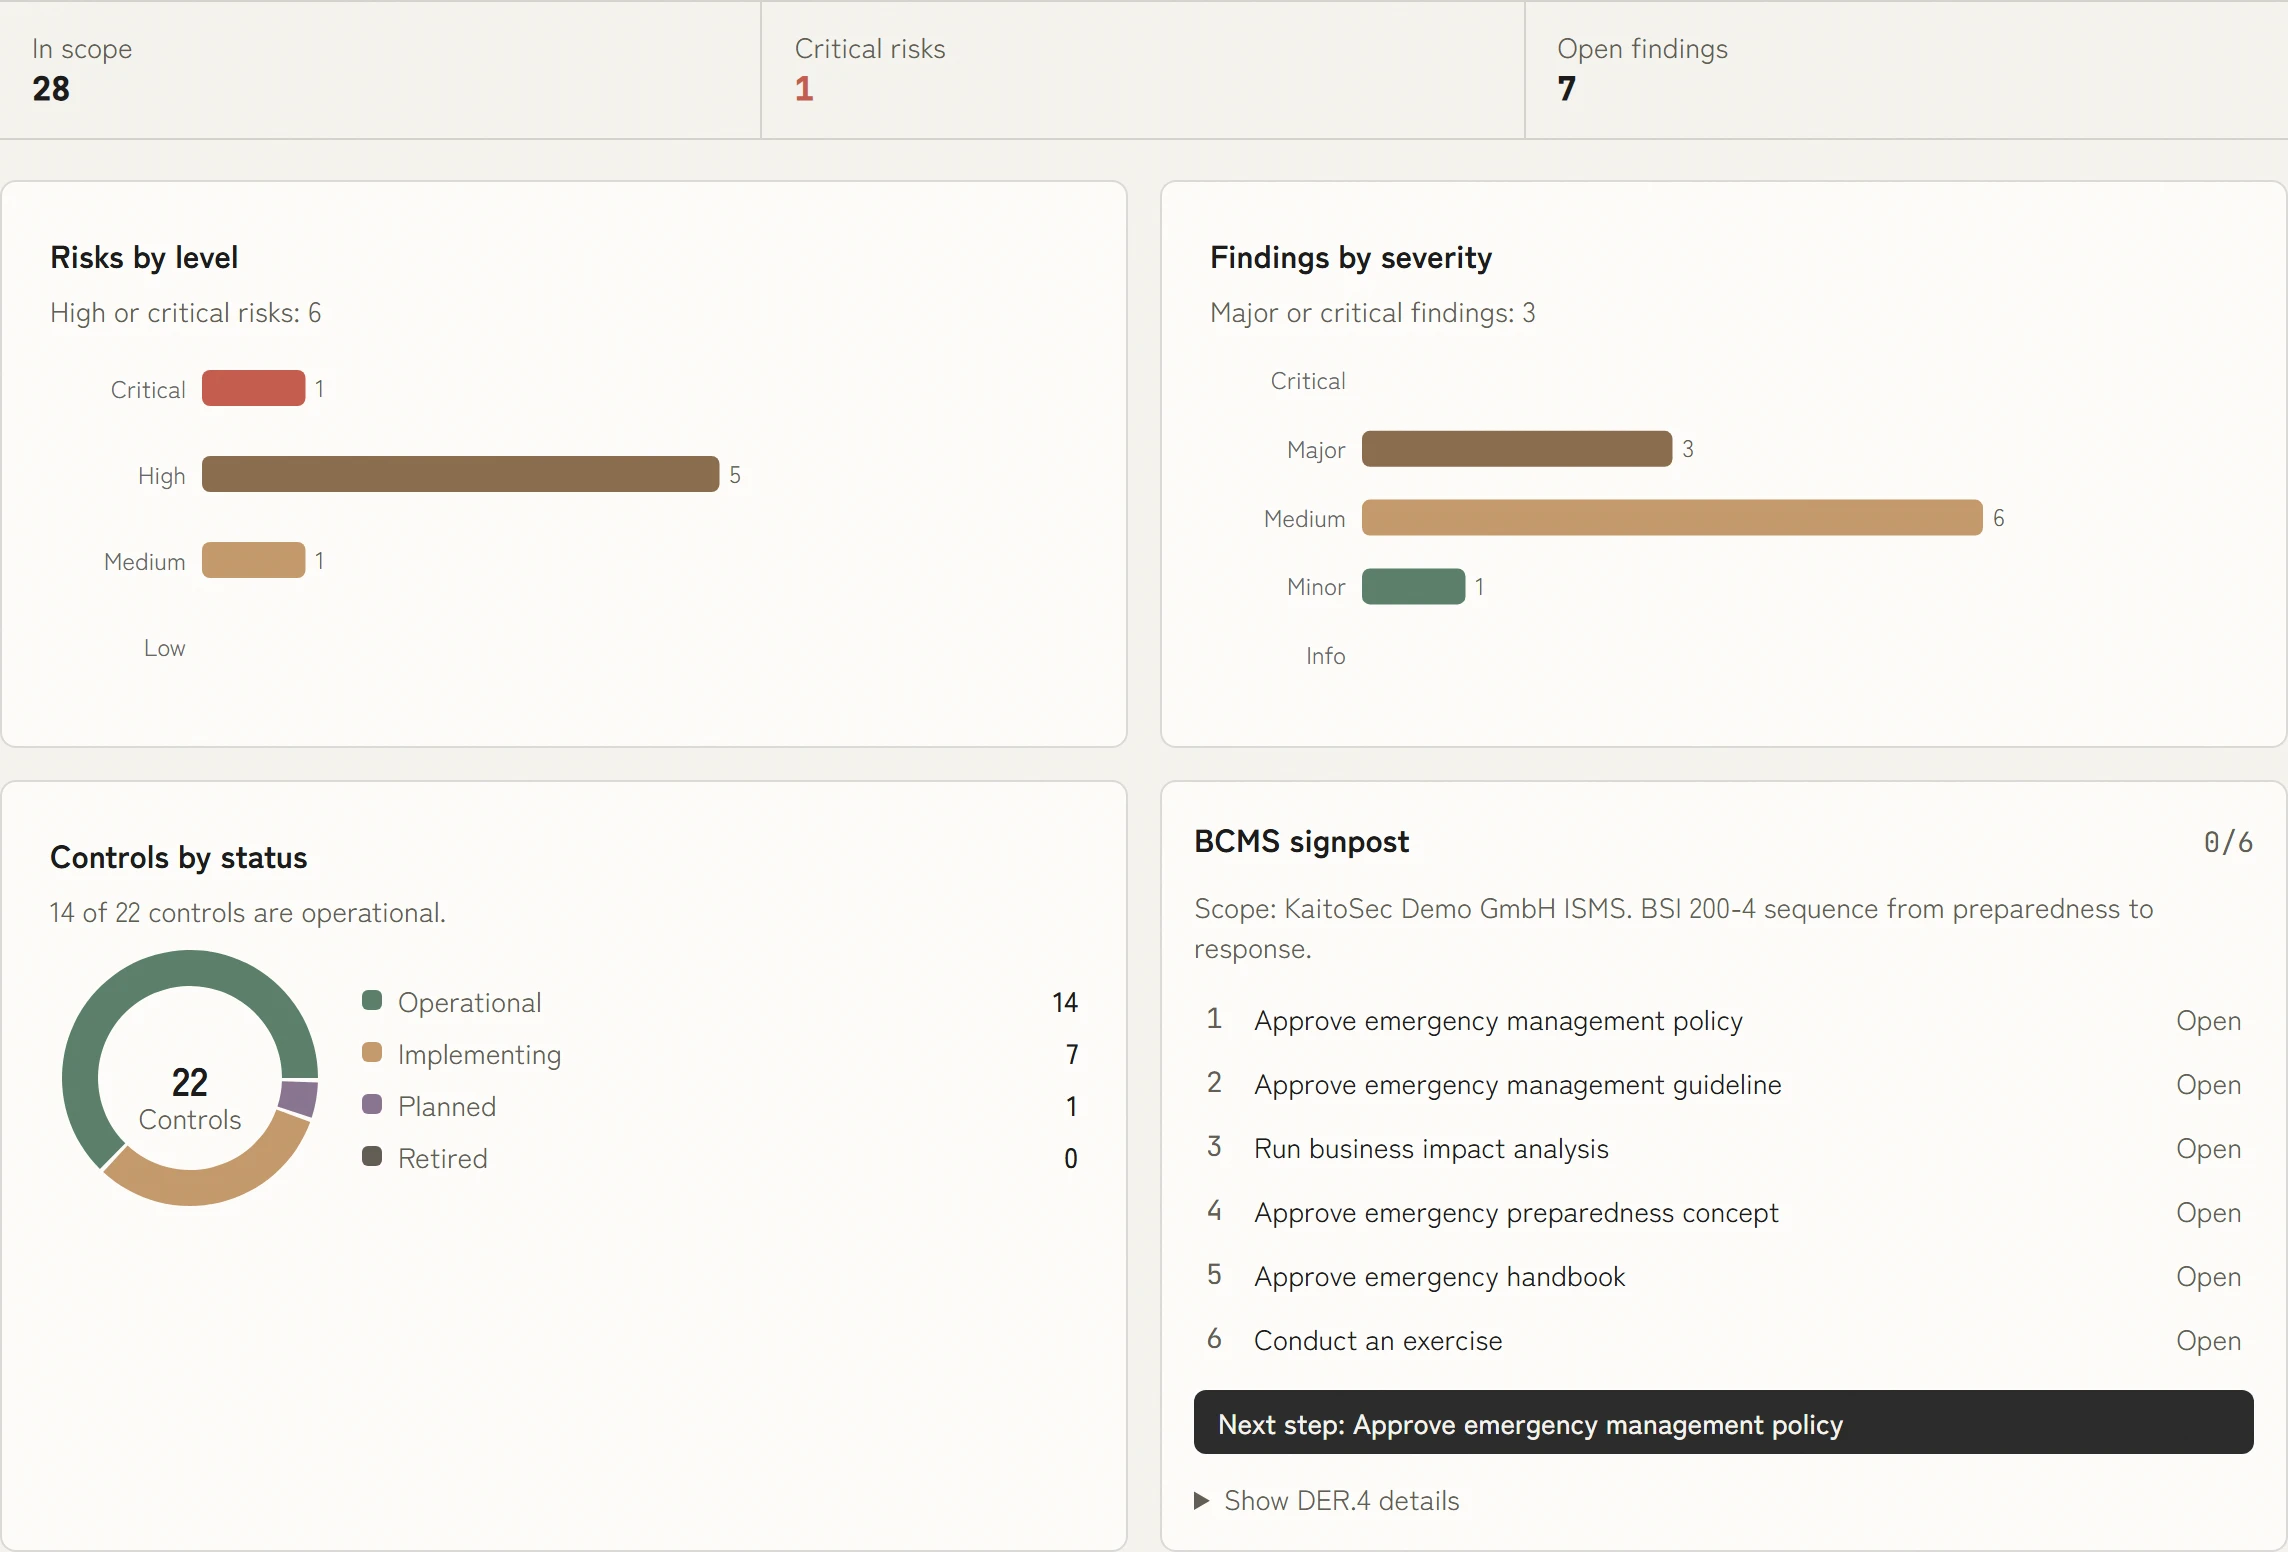
Detect and Respond in one picture
Risks and findings by severity, actions by status, the state of the BCMS: one picture for Detect, Respond and Recover that shows what is open today, not what was assessed a quarter ago.
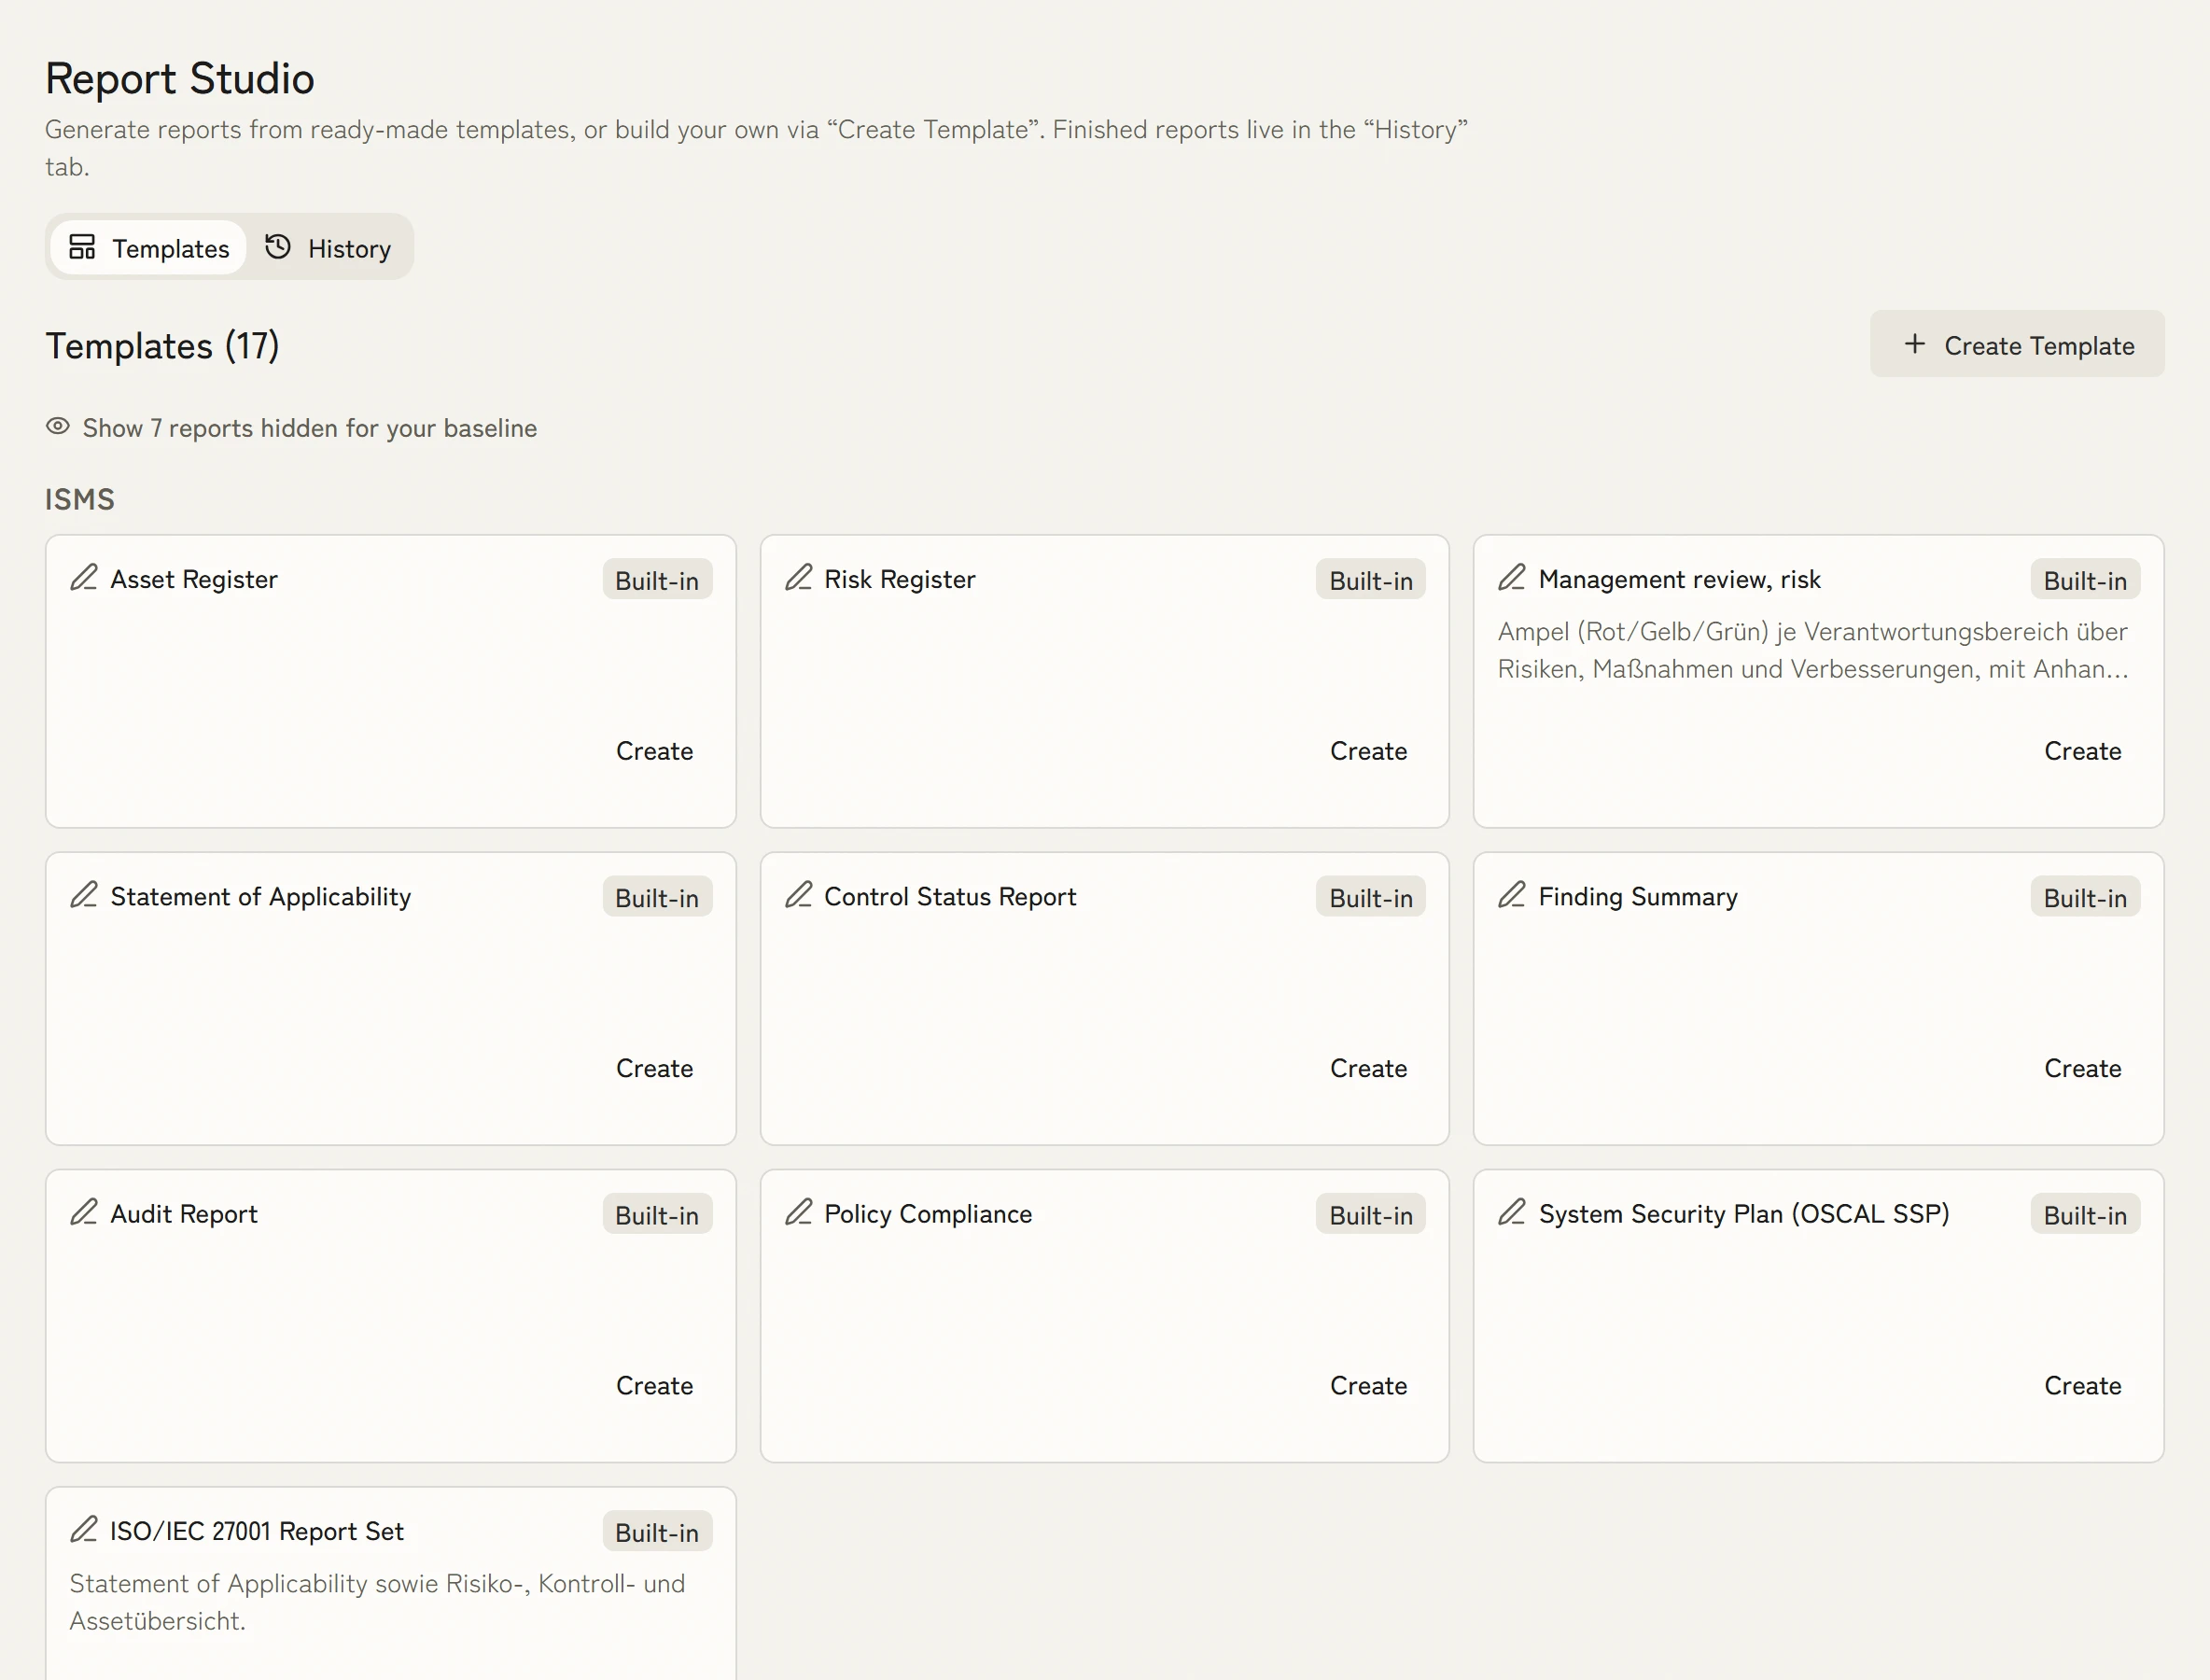
One report per audience, from the same state
Asset register, risk register, management review, Statement of Applicability and audit report all come out of the same state. Reporting to the board against the CSF uses the same figures the ISO audit sees.
CSF subcategories on ISO 27001, IT-Grundschutz and NIS2
Where the substance overlaps, every subcategory is mapped to the corresponding ISO 27001 control, the matching IT-Grundschutz building block and the relevant NIS2 measure. A control is implemented once and becomes visible in all four frameworks at once.
3 frameworksCross-mapped to ISO 27001, BSI IT-Grundschutz, NIS2
Connect NIST CSF with other standards
Connect the CSF with the standards that are actually audited in Europe.
- ISO 27001The international ISMS standardLearn more
- BSI IT-GrundschutzGerman baseline IT securityLearn more
- NIS2EU cybersecurity directiveLearn more
NIST CSF by company and role
More for NIST CSF
The framework international customers expect
The NIST Cybersecurity Framework is one of the most widely adopted security frameworks globally. Originally developed for US critical infrastructure, it has become a de facto standard for organisations of all sizes seeking a structured, risk-based approach to cybersecurity.
One implementation, many frameworks
KaitoSec's multi-framework mapping lets you satisfy NIST CSF subcategories using the same controls that cover ISO 27001 Annex A, BSI IT-Grundschutz and NIS2.
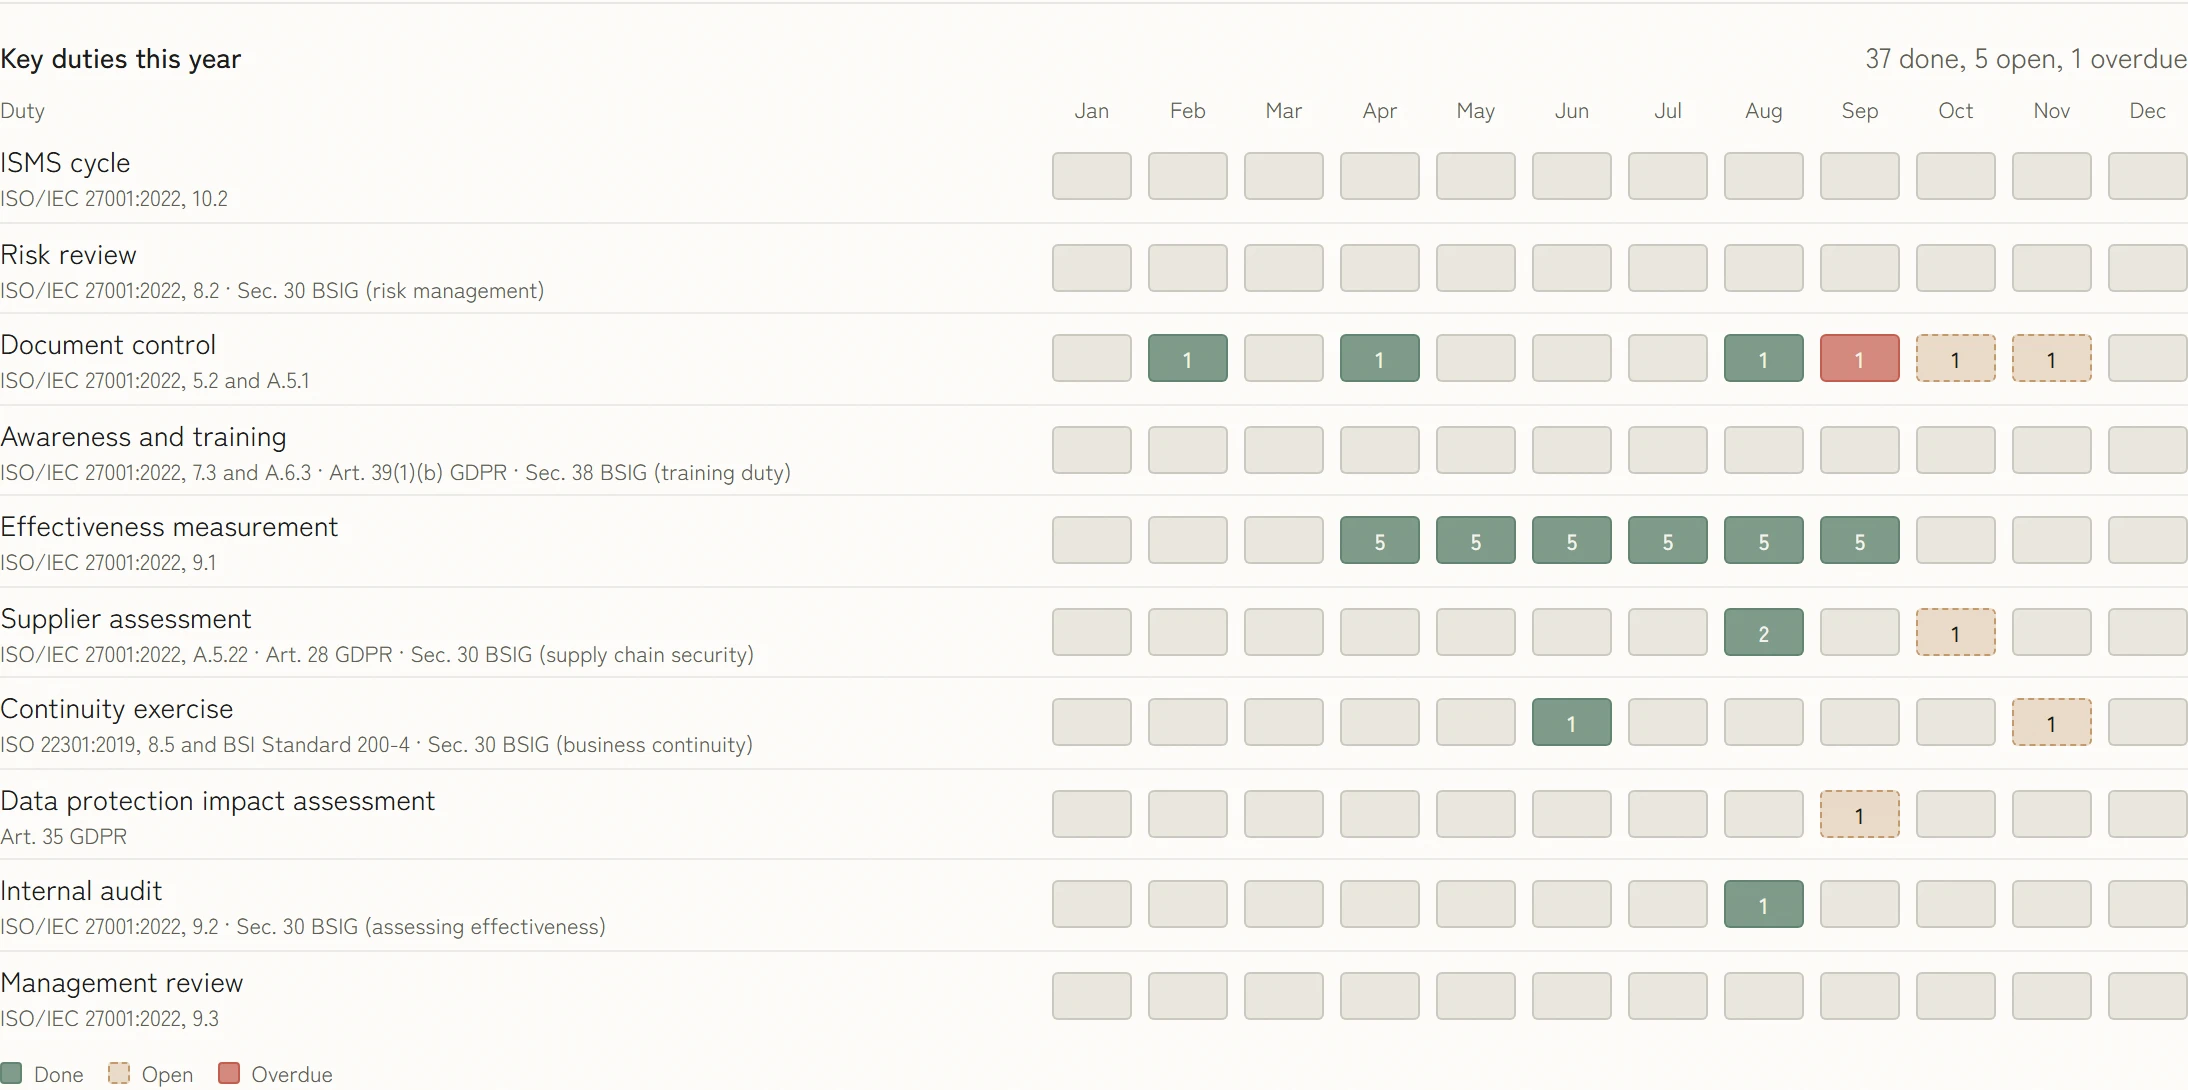
Govern function wired into the ISMS
CSF 2.0 elevated governance into a peer function alongside Identify, Protect, Detect, Respond and Recover. KaitoSec's policy and acknowledgement workflows, role assignments and management-review records produce the Govern evidence directly out of the operating ISMS.
Track maturity per function
Each CSF function shows current and target maturity, the underlying ISMS controls implementing it, and the gap between today and the next assessment. This view feeds management reviews and board briefings.
Profile builder for current and target state
Build current and target profiles for each part of the organisation. The comparison produces a work queue sorted by residual risk rather than chapter number.
Map CSF subcategories to ISO 27001, IT-Grundschutz and NIS2
Every CSF subcategory is mapped against the corresponding ISO 27001 control, BSI IT-Grundschutz Baustein and NIS2 measure where the substance overlaps. A control is implemented once and becomes visible in all four frameworks at once.
What NIST CSF 2.0 requires
NIST CSF 2.0 organises cybersecurity into six functions: Govern, Identify, Protect, Detect, Respond and Recover. Govern was added as a peer function in 2024. The framework prescribes no controls; it describes outcomes that you steer with a current and a target profile.
6functions
- Function GVGovern
- Function IDIdentify
- Function PRProtect
- Function DEDetect
- Function RSRespond
- Function RCRecover
The catalogue underneath
- 22
- categories
- 106
- subcategories
Frequently asked questions about NIST CSF
What changed in NIST CSF 2.0?
CSF 2.0, published in 2024, adds a sixth function, Govern, which covers organisational context, risk management strategy, roles and responsibilities, policy and oversight. The 2.0 release is also explicitly intended for organisations of all sizes and sectors, not only US critical infrastructure. KaitoSec ships the 2.0 catalogue out of the box.
How does NIST CSF compare to ISO 27001?
ISO 27001 is an auditable management system standard with mandatory clauses and a control library. NIST CSF is a risk-management framework with functions, categories and subcategories. Many organisations adopt CSF as the strategic frame and ISO 27001 as the management system that delivers it. KaitoSec carries both and shows the mapping at every level. This is the same one-control-many-frameworks idea our article Resilience Made Easy describes.
Can we use CSF profiles to drive improvement work?
Yes. The most common pattern is to build a current profile from where you are today, a target profile from where the business wants to be, and use the gap as the improvement backlog. KaitoSec stores profiles as first-class objects so the gap is always live, not a once-a-year spreadsheet.
Is NIST CSF relevant for European organisations?
Yes. CSF is sector-neutral and increasingly referenced in European supply-chain and customer due-diligence requests, particularly from US-headquartered customers. For European organisations carrying ISO 27001 or NIS2 obligations, CSF is the framing that customers with a US connection often expect alongside the local standard.

Your CSF profile in thirty minutes.
In the demo we build the current and target profile on your functions. You leave with a work queue sorted by residual risk, not by chapter number.