
Business Continuity: emergency plans from data you already have.
KaitoSec works out from your BIA which processes must run again first, and turns that into plans, emergency cards and exercises. In an emergency everyone knows what to do, and leadership sees what has been exercised.



 5.0 out of 5
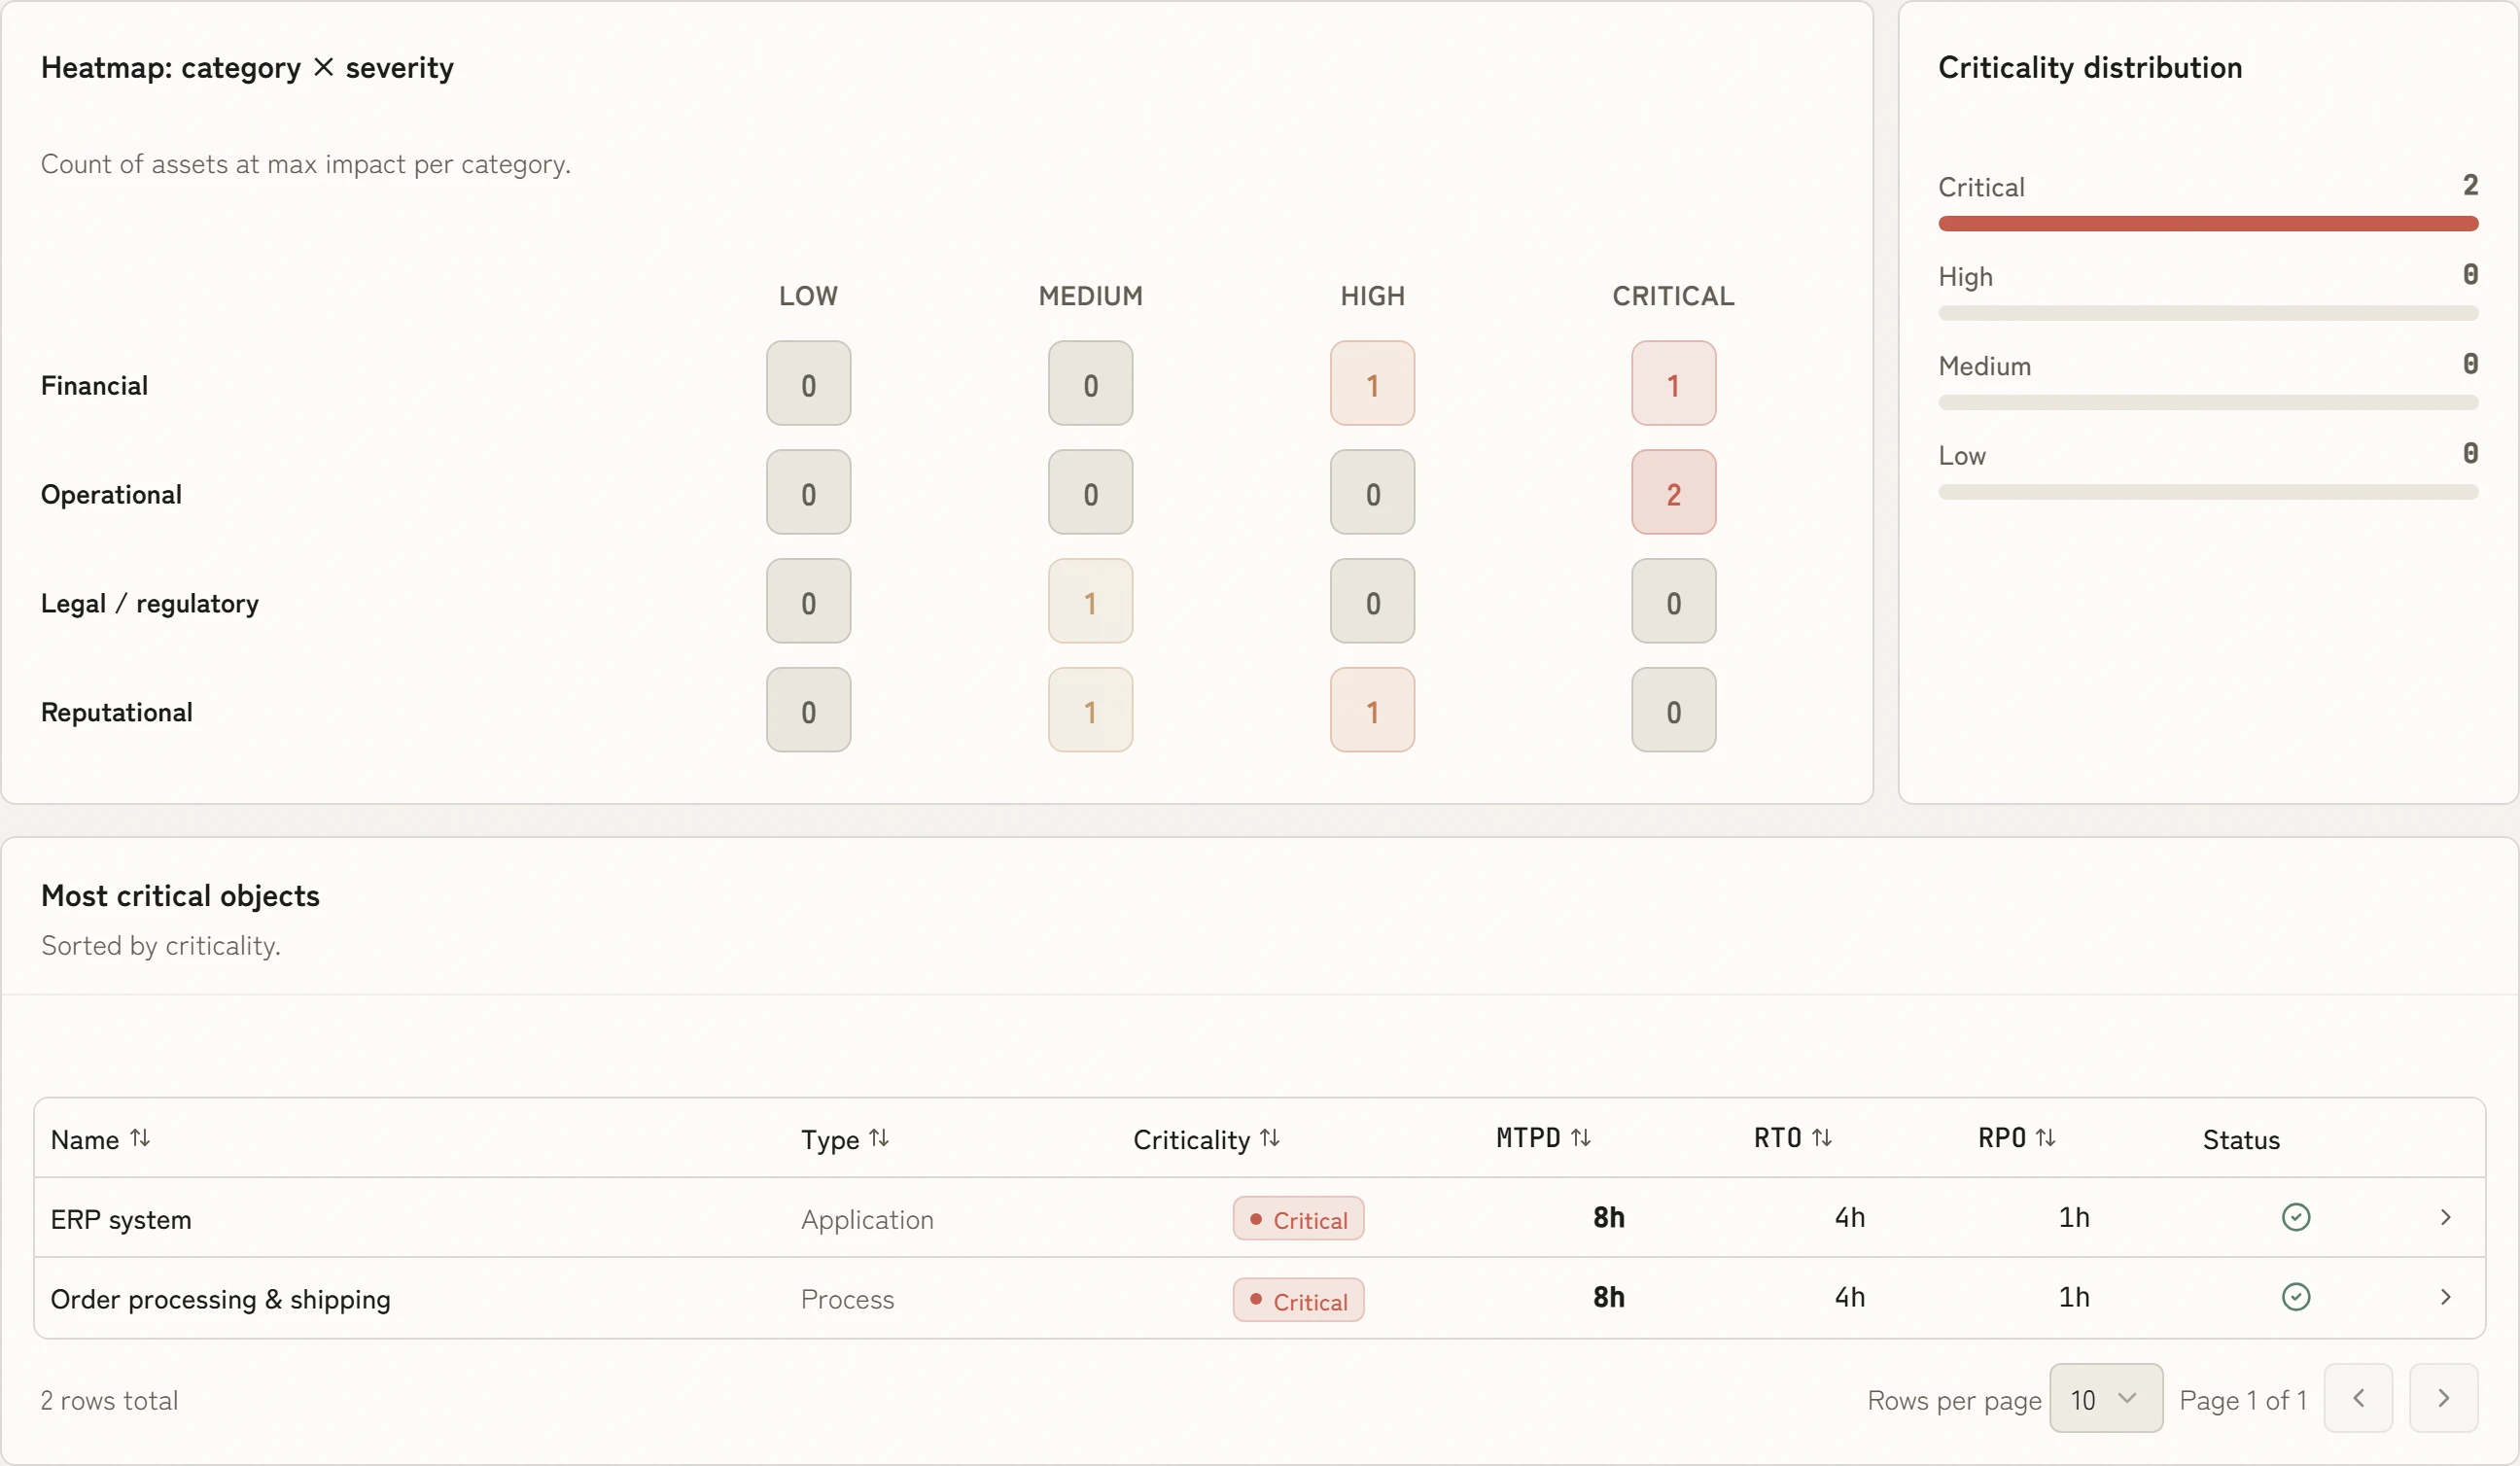
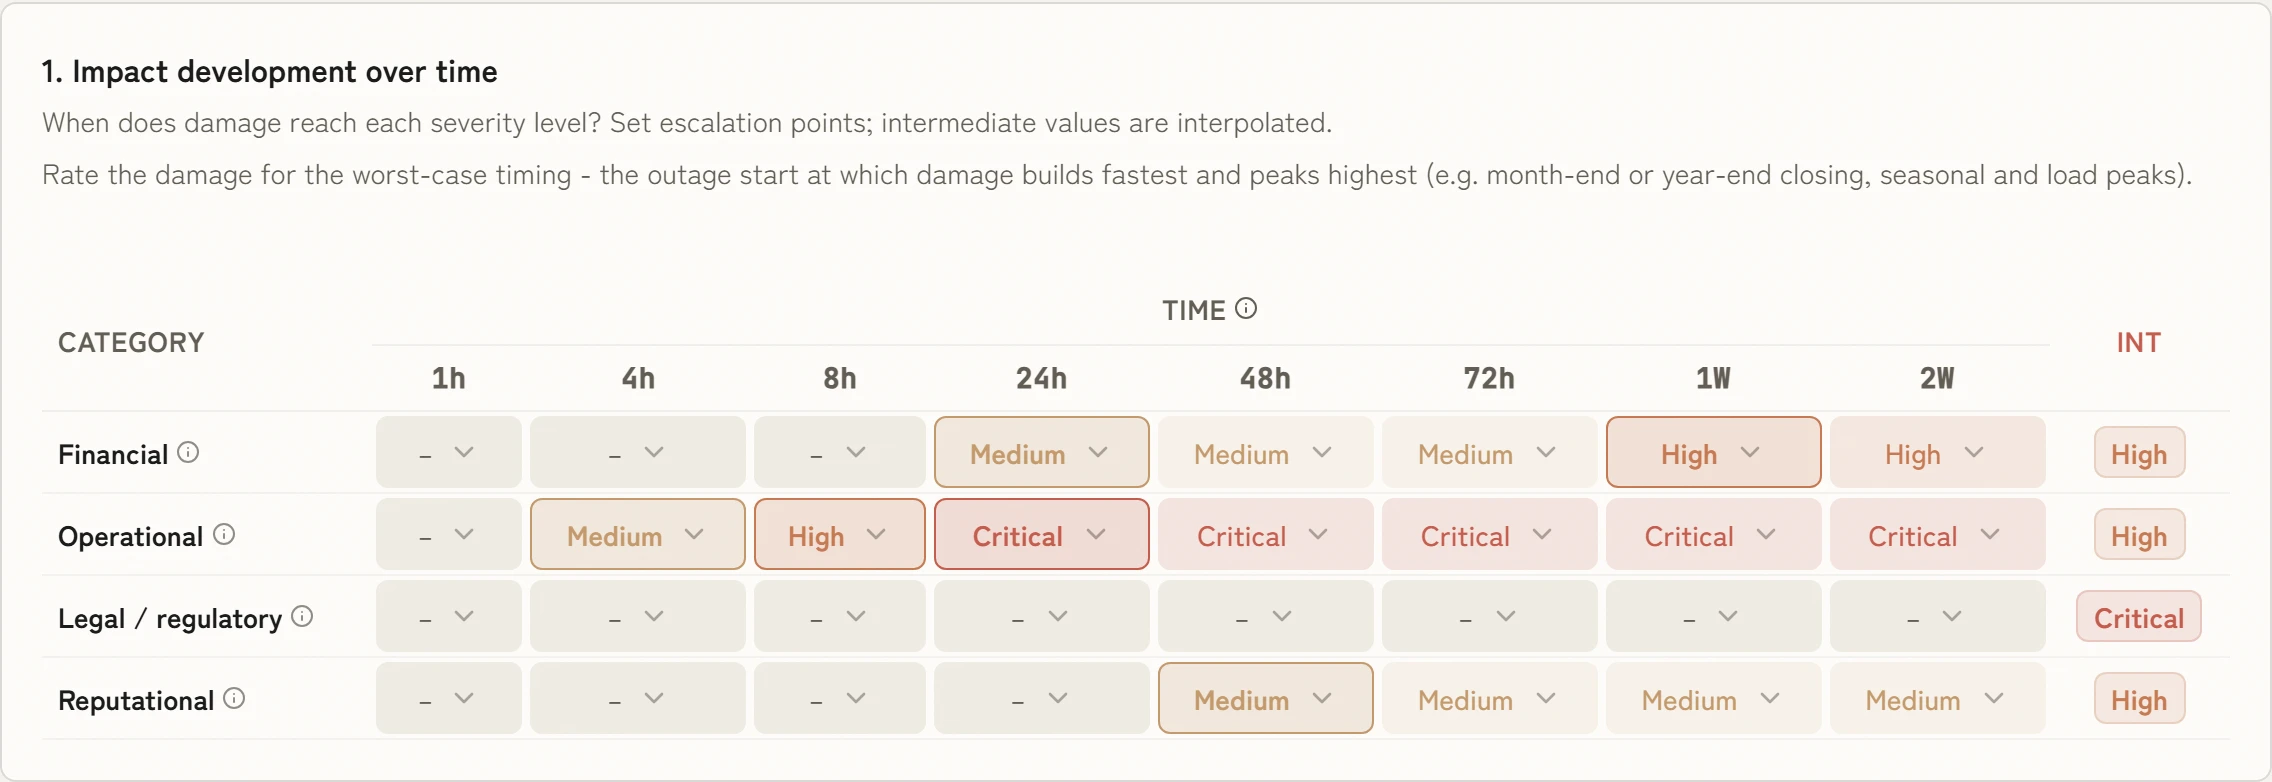
See how expensive every hour of downtime gets
The BIA shows for each process when the damage becomes medium, high or critical, from one hour to two weeks. That gives you the recovery time, the tolerable data loss and the order in which processes must run again.
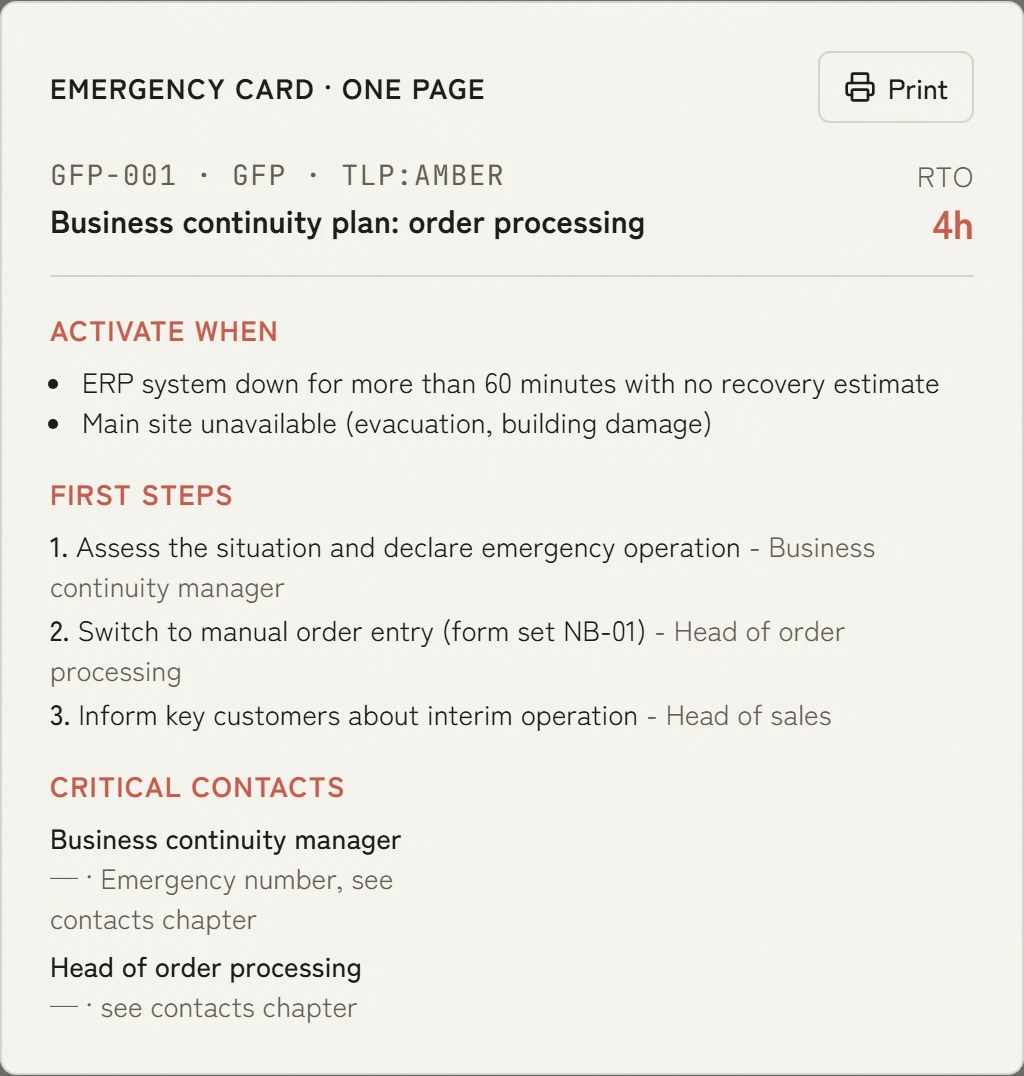
The first steps at a glance
From the business continuity plan, KaitoSec produces an emergency card with triggers, first steps, owners and key contacts. The card complements the emergency handbook: printed, it shows at a glance where to start, and the handbook covers the details.
Book a demo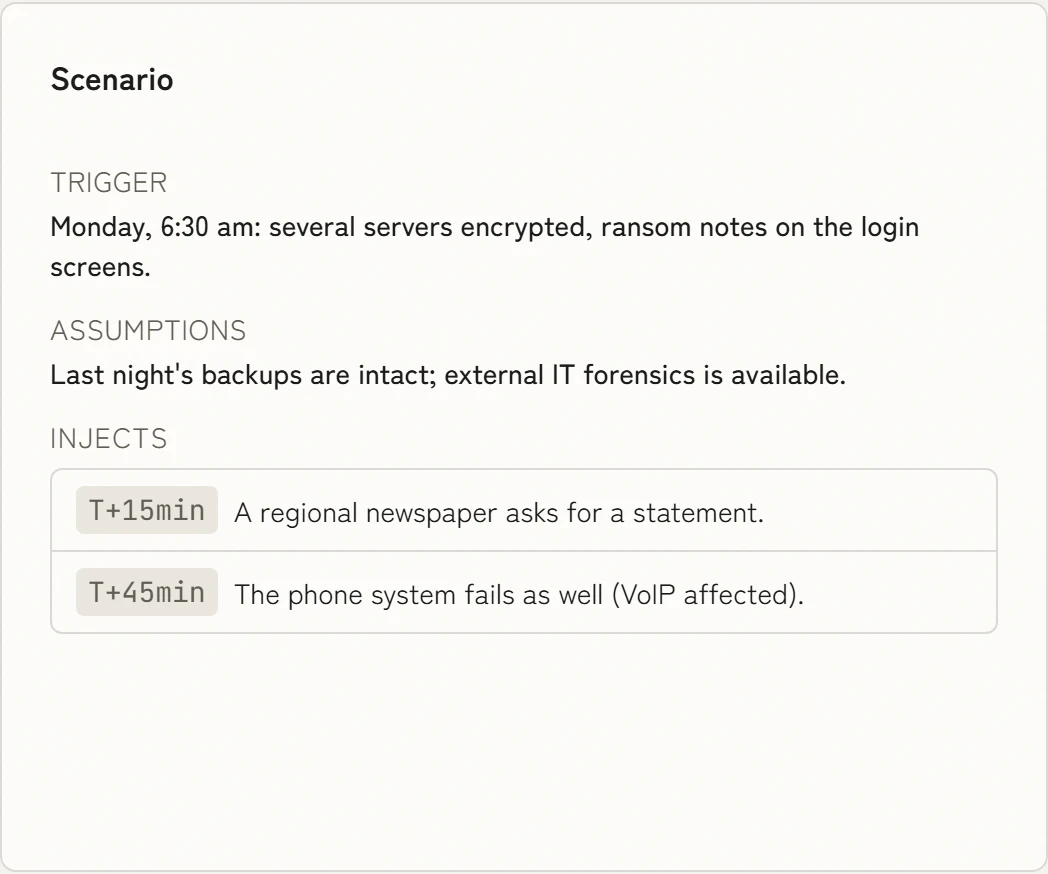
Practise before it gets serious
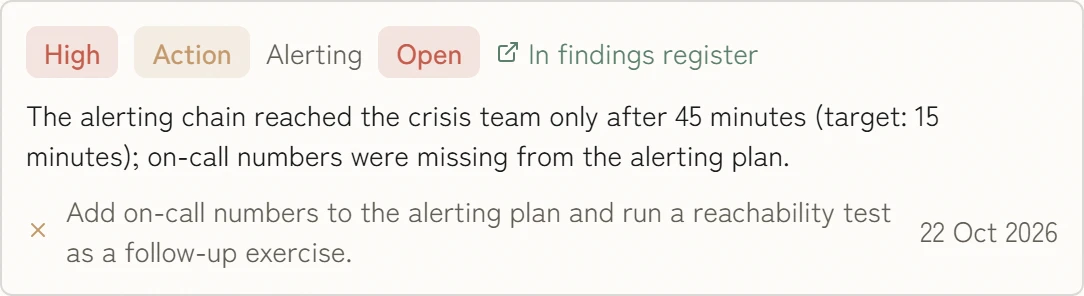
You plan tabletop exercises with a trigger, assumptions and timed events, for a ransomware attack for example. Findings and follow-up actions land on the plan, not in minutes in a folder.
Book a demo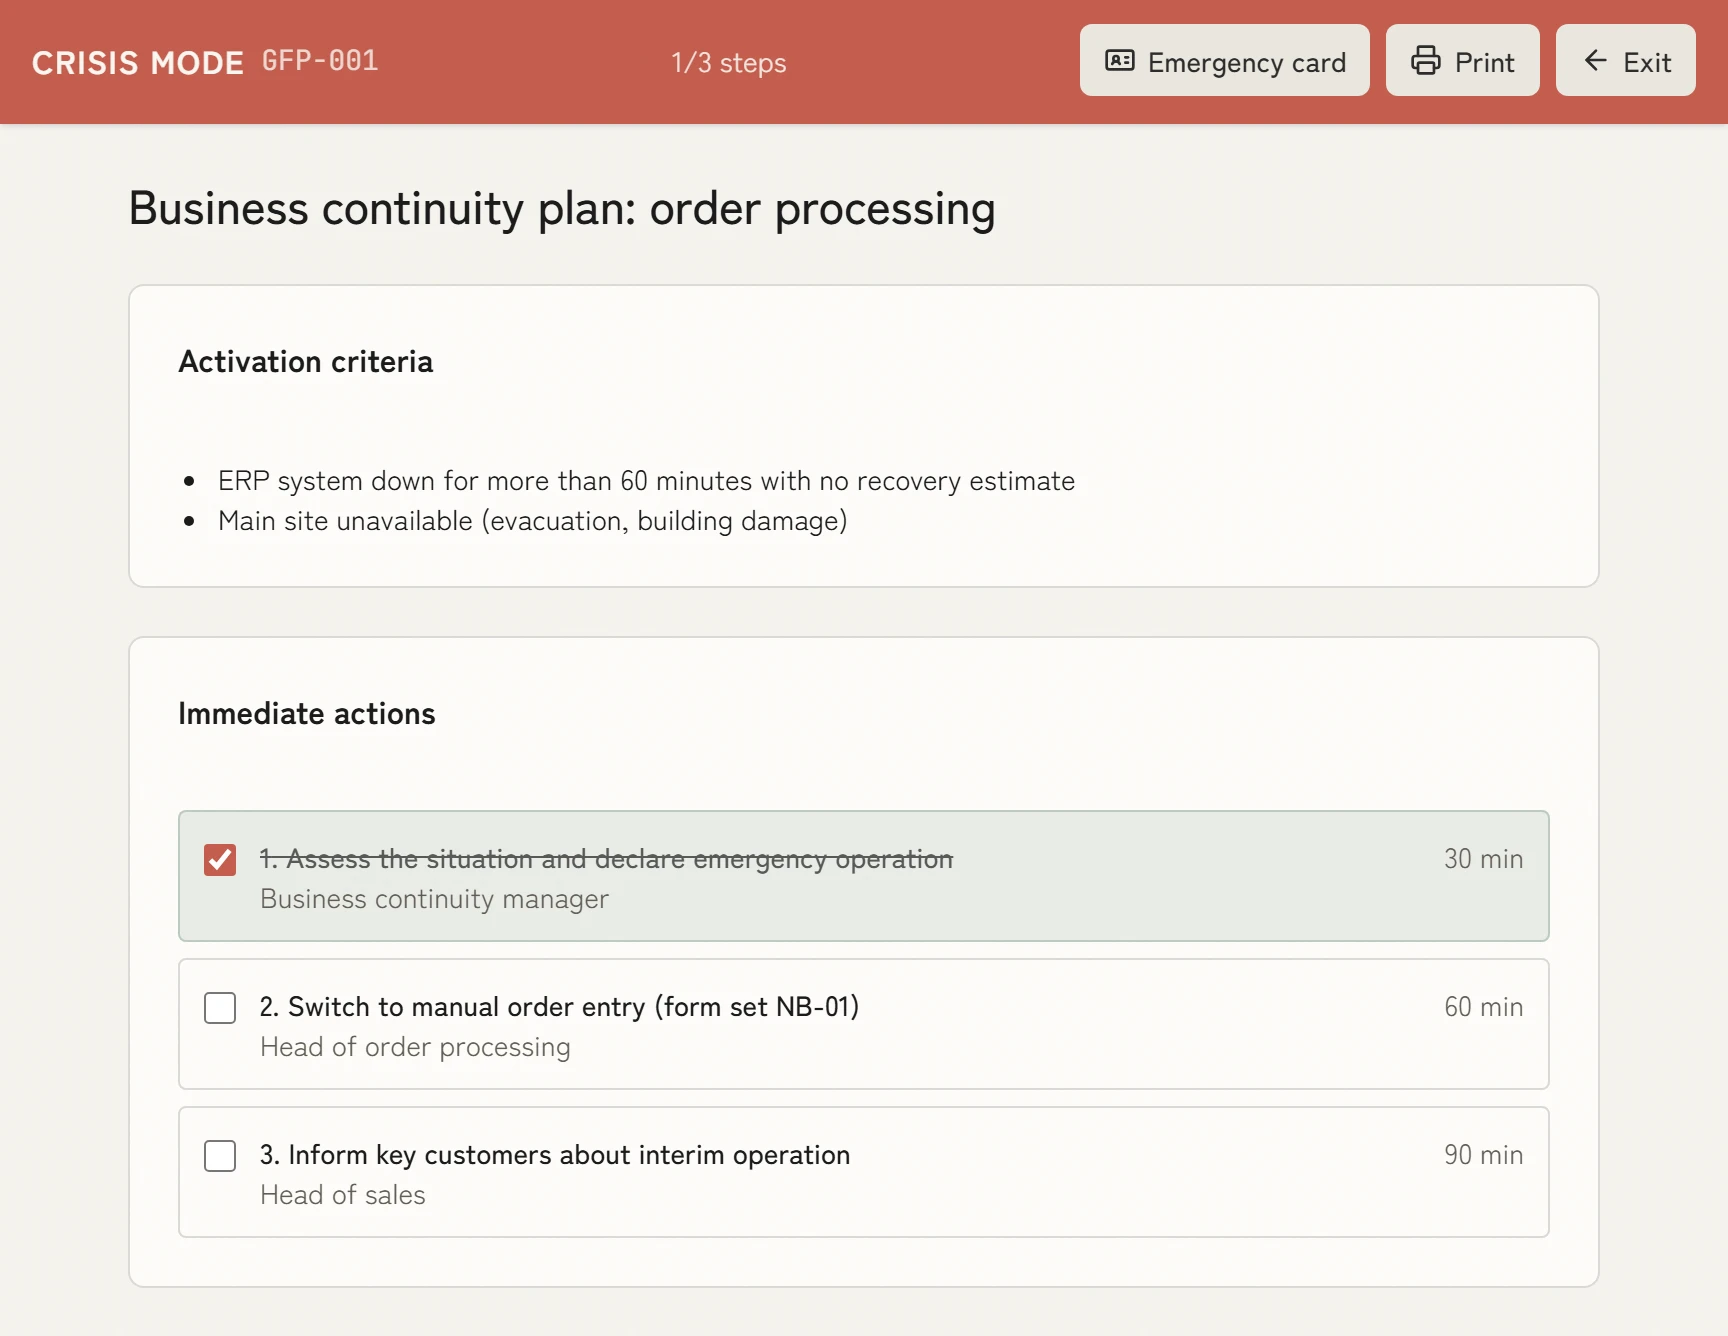
In an emergency, tick off instead of searching
When a plan is activated, crisis mode shows the activation criteria and immediate actions as a checklist. Status, decisions and communication are logged and later serve reporting and evidence obligations.
Book a demo- pre-mapped controls
- 100+100+
- of evidence created as the work is done
- 100 %100 %
- faster than manual work
- 10×10×
- management systems, one data model
- 4 in 14 in 1
What KaitoSec also does
These sit in the core of the platform and apply to every module.
Implemented once, done for every requirement.
More than 100 controls are already mapped to ISO 27001, NIS2, DORA and other requirements. You implement a control once and evidence it once. Every further requirement it covers costs no extra work.
You review and approve instead of filling empty fields.
Agents prepare the risk analysis, the statement of applicability and actions from audit reports. Every result is ready for approval. A person still makes the decision.
Nothing left to collect before the audit.
Evidence is created as the work gets done: a tested backup supplies its recovery time, a completed review its result. Your evidence is current every day, not just in the week before the audit.
Business continuity without prior knowledge.
In the BIA you set for each process when an outage starts to get expensive. Recovery time and order follow from that, and the help panel explains terms like RTO in plain words. For an incident, KaitoSec turns the plan into a one-page emergency card and, in crisis mode, a checklist to tick off.
You maintain each process only once.
Information security, business continuity management, data protection, AI governance and supplier management all work from the same process data. Every change takes effect in every system at once. Duplicate entry and conflicting registers go away.

Ask Chris how this would work for you.
Co-founder and CEO of KaitoSec. He walks through your case with you, live in the product.
Book a demo
The data for your business continuity is already there.
100+ integrations
All integrations















FAQ
What is a business impact analysis and why does it matter?
A business impact analysis identifies the processes and services that have to keep running, scores the consequences of their disruption over time and sets recovery targets such as RTO, RPO and MTPD. Without it, every continuity plan is a guess. With it, the rest of your resilience programme has somewhere to start.
How does KaitoSec connect business continuity with information security?
BCMS and ISMS share the same workspace, the same asset model, the same risk surface and the same evidence trail. A risk identified in your ISMS can drive a BIA update. A critical asset feeds both control selection and recovery planning. There are no duplicate registers and no silo handovers.
Do we need ISO 22301 certification to use the BCM features?
No. The BCM module is useful with or without certification. If you pursue ISO 22301, KaitoSec supports the full lifecycle. If you do not, the same module meets the continuity and resilience expectations of NIS2, DORA and customer due diligence.
What is the difference between a BC plan and a disaster recovery plan?
A BC plan covers the overall response: which processes keep going, who decides, how the organisation communicates, how the business escalates. A disaster recovery plan covers the technical restoration of systems. KaitoSec carries both and keeps the relationships explicit, so neither plan drifts from the other.
How often should BC plans be tested?
ISO 22301, NIS2 and DORA all expect regular testing, typically at least annually for critical plans and more often for high-impact processes. KaitoSec schedules, documents and tracks exercises in the same place as the plans themselves, so the cadence is provable without manual record-keeping.

Less work in your business continuity.
One critical process from your operation is enough. In thirty minutes you see how KaitoSec turns it into recovery targets, a plan and an exercise.