
Compliance Mapping: implement once, prove it many times over.
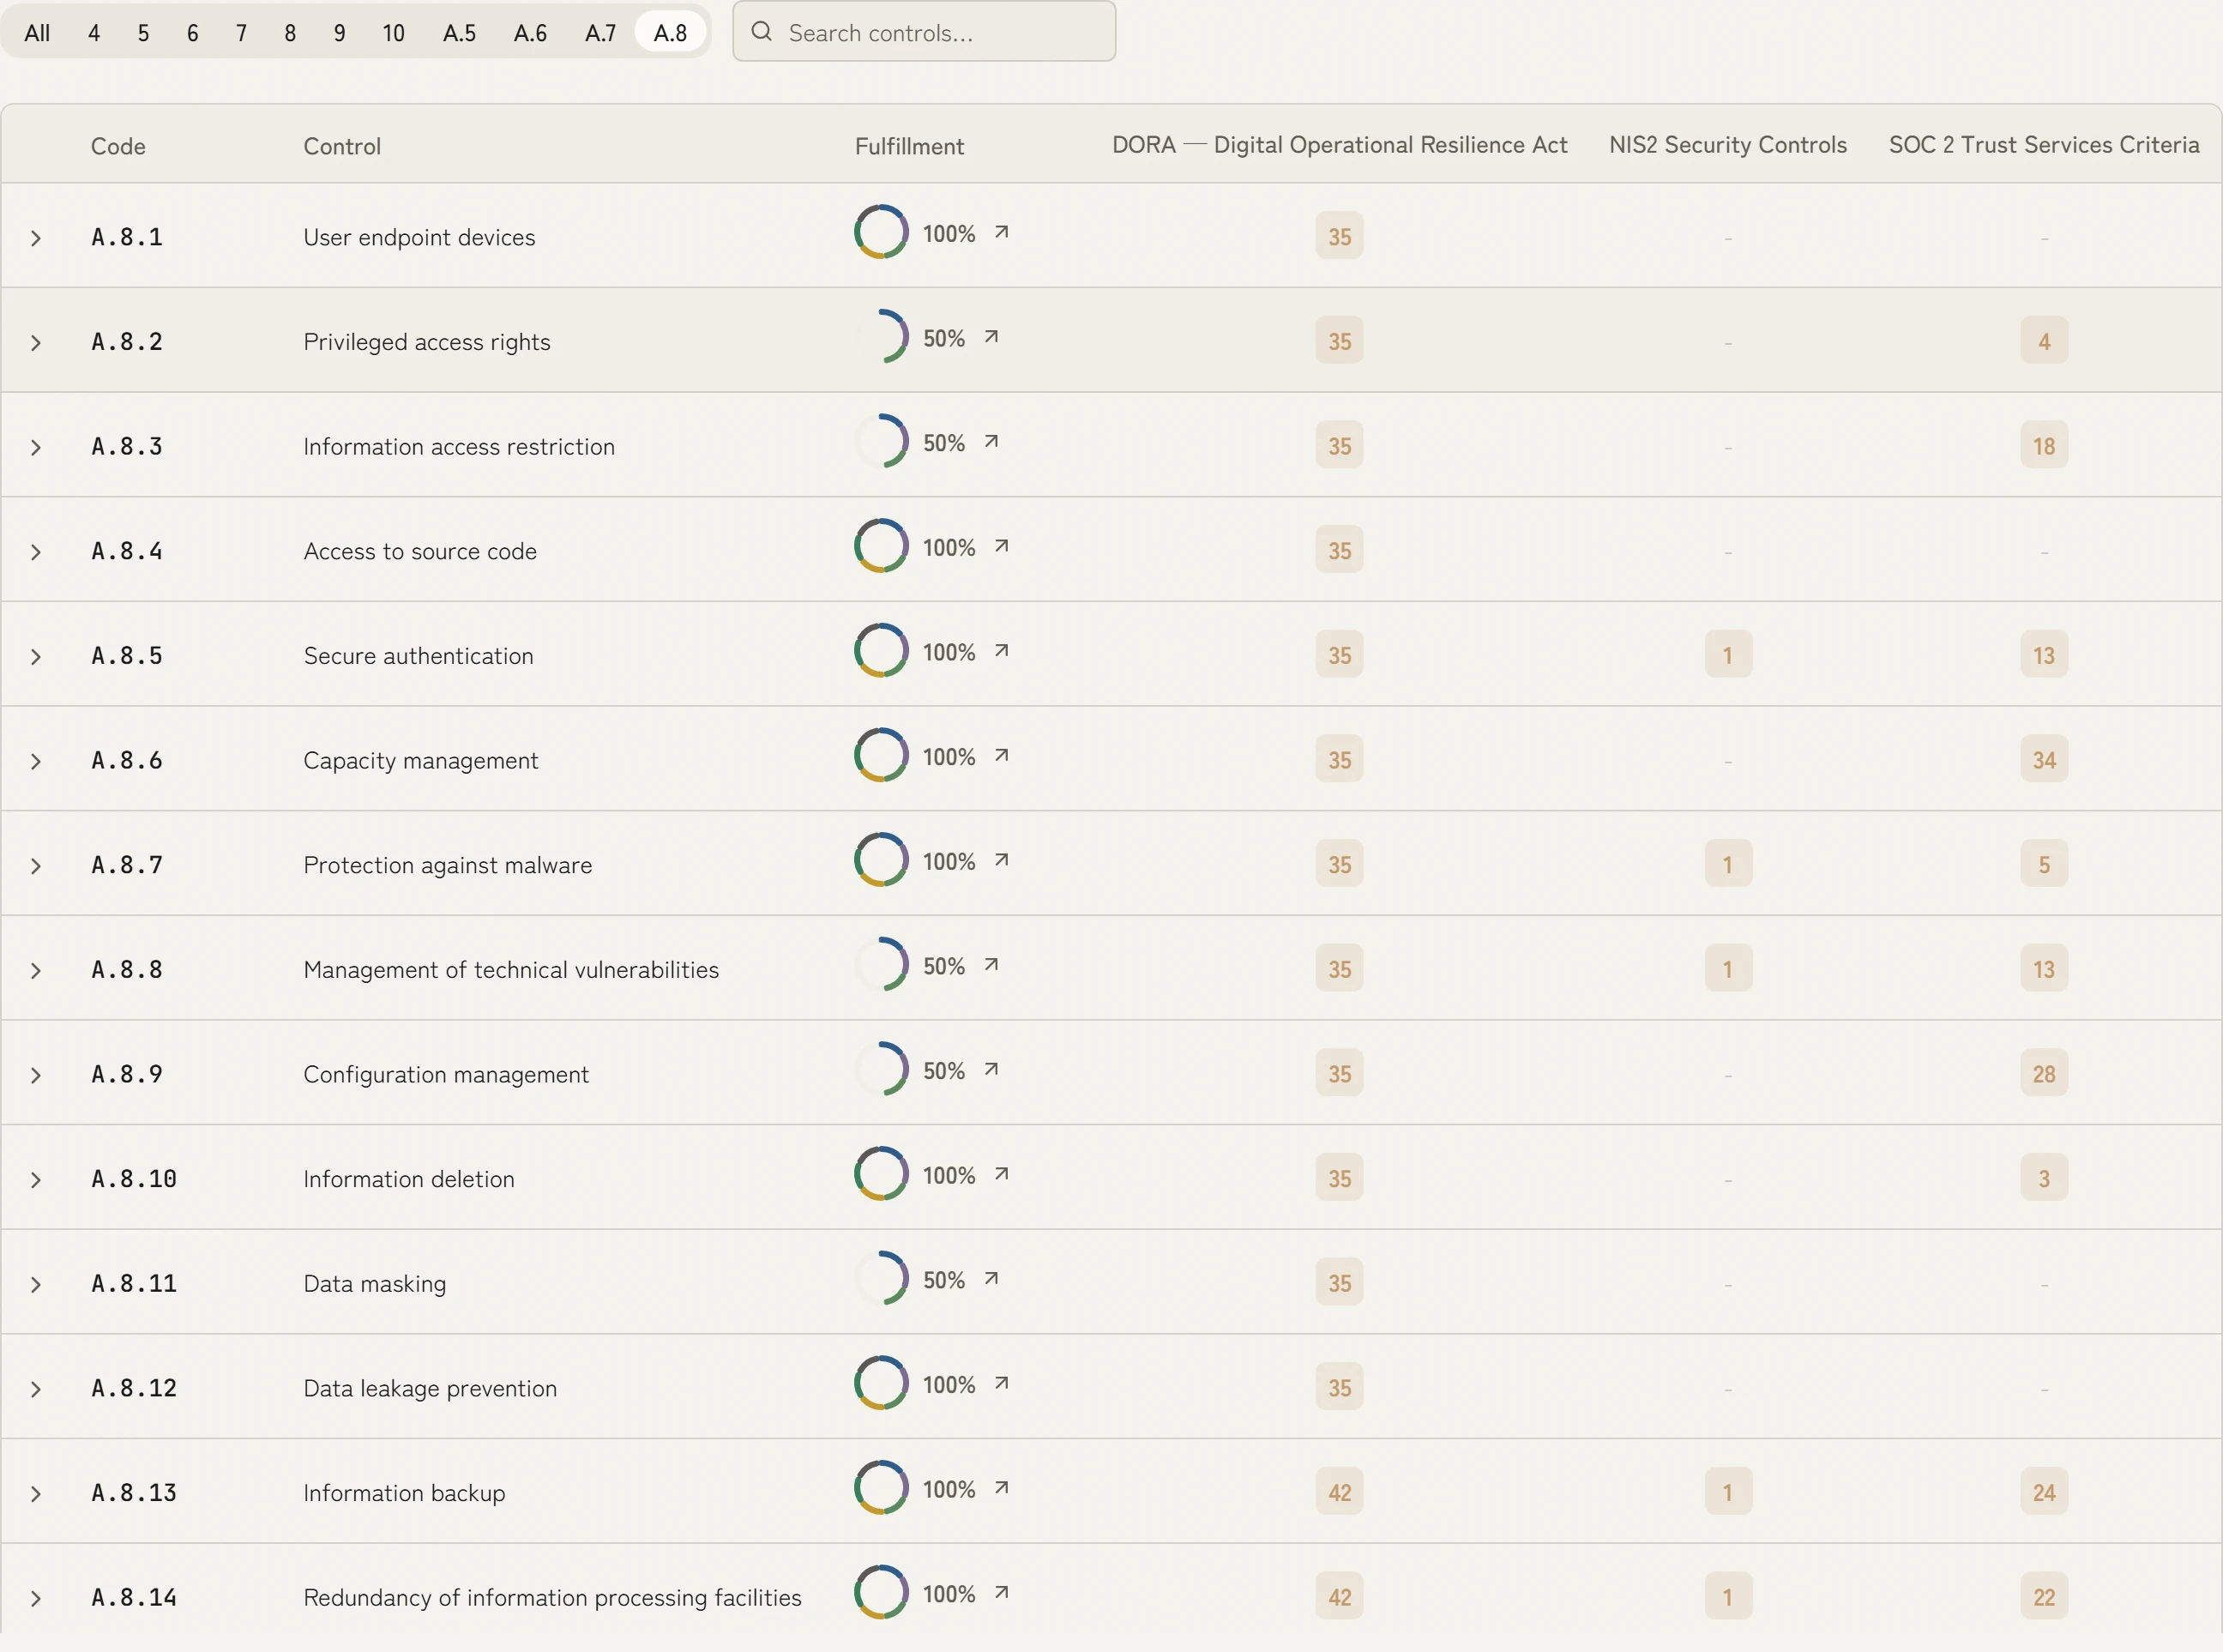
More than 100 controls are already mapped to ISO 27001, NIS2, DORA and further standards. When a standard is added, you see straight away what your implementation already meets and where something is really missing.



 5.0 out of 5
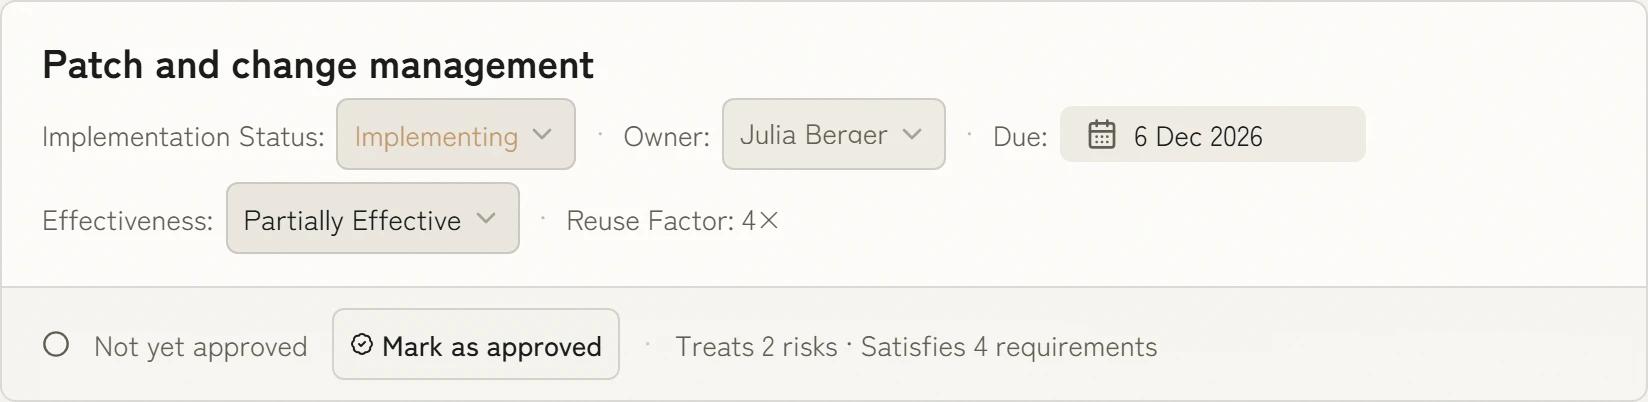
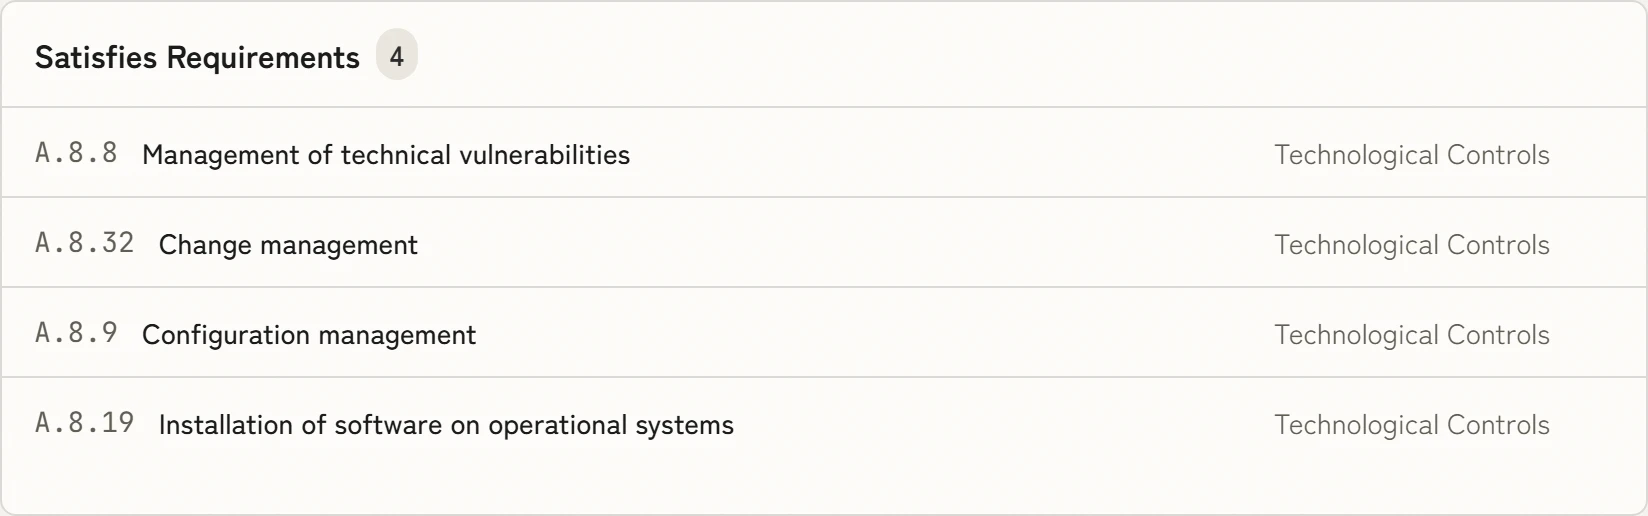
One control, many requirements met
Every control shows which requirements it meets, across all standards. You implement it once and evidence it once, and every linked requirement counts.
Book a demo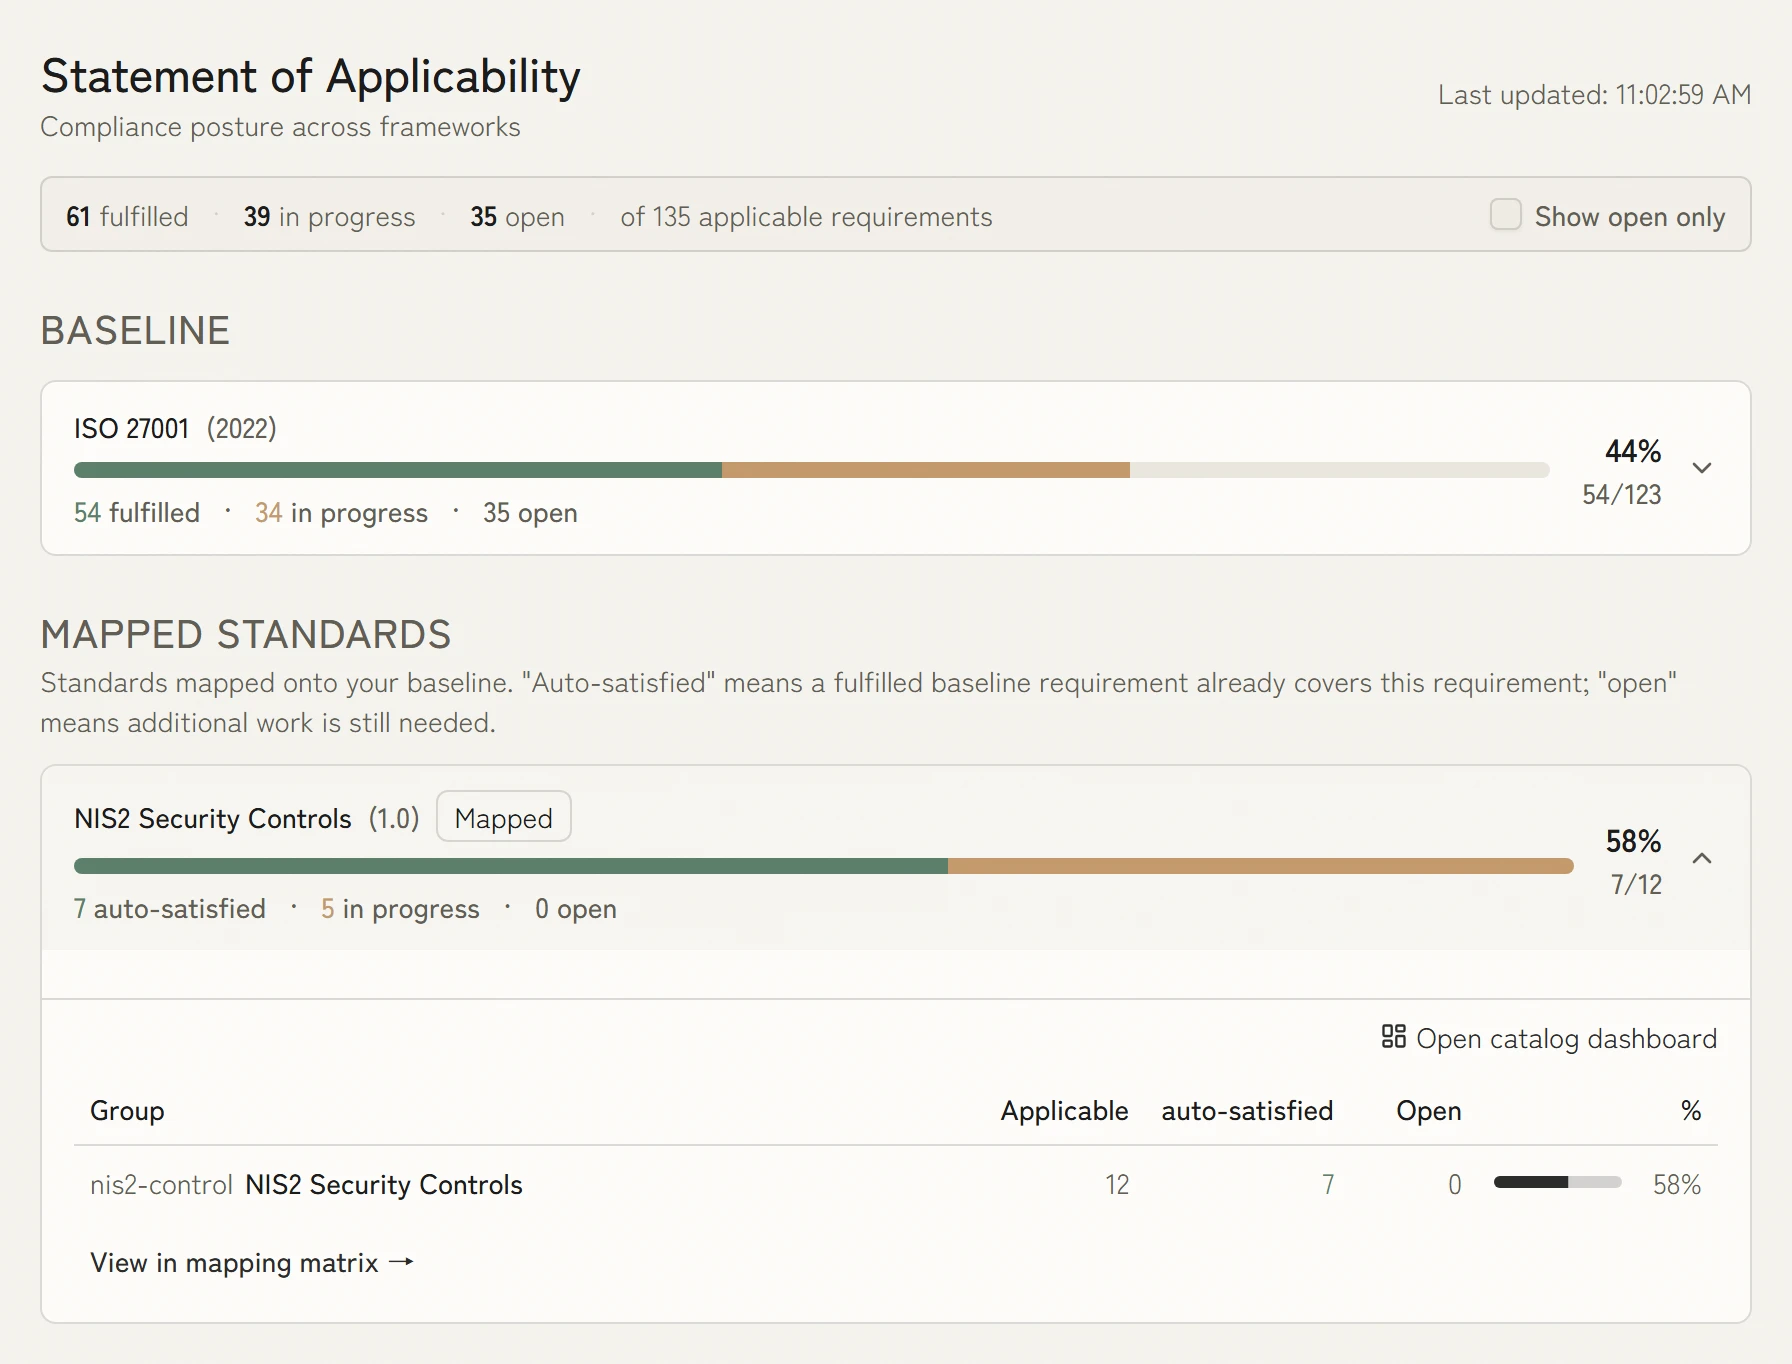
The next standard does not start from zero
The statement of applicability shows the state per standard. What your ISO 27001 implementation already meets for NIS2 is credited automatically, and you work only on the real gaps.
Book a demo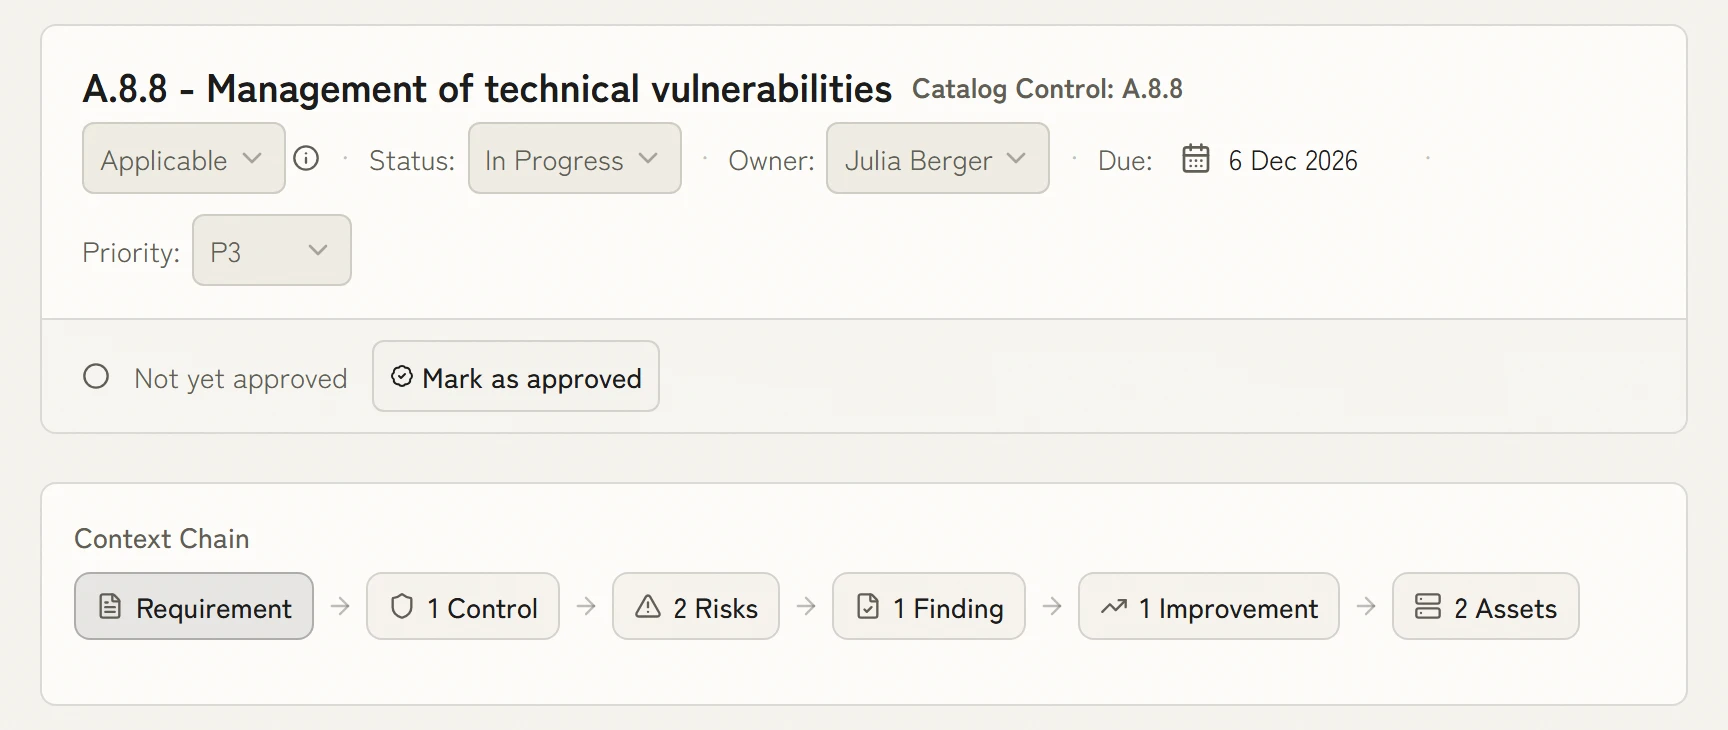
See what hangs on every requirement
Control, risks, findings, improvements and assets sit right on the requirement. When the auditor asks, the answer is one click away, without a second checklist.
Book a demo- pre-mapped controls
- 100+100+
- of evidence created as the work is done
- 100 %100 %
- faster than manual work
- 10×10×
- management systems, one data model
- 4 in 14 in 1
What KaitoSec also does
These sit in the core of the platform and apply to every module.
Implemented once, done for every requirement.
More than 100 controls are already mapped to ISO 27001, NIS2, DORA and other requirements. You implement a control once and evidence it once. Every further requirement it covers costs no extra work.
You review and approve instead of filling empty fields.
Agents prepare the risk analysis, the statement of applicability and actions from audit reports. Every result is ready for approval. A person still makes the decision.
Nothing left to collect before the audit.
Evidence is created as the work gets done: a tested backup supplies its recovery time, a completed review its result. Your evidence is current every day, not just in the week before the audit.
Understand requirements without prior knowledge.
In simple mode KaitoSec explains which rules apply to your organisation, in words rather than clause numbers. Your team excludes what does not apply. Anyone who needs more detail switches to expert mode and sees the same requirements with references to the standard and mapping.
You maintain each process only once.
Information security, business continuity management, data protection, AI governance and supplier management all work from the same process data. Every change takes effect in every system at once. Duplicate entry and conflicting registers go away.

Ask Chris how this would work for you.
Co-founder and CEO of KaitoSec. He walks through your case with you, live in the product.
Book a demo
The data for your compliance mapping is already there.
100+ integrations
All integrations















FAQ
Which frameworks does KaitoSec support?
ISO 27001:2022, NIS2, SOC 2, TISAX, BSI IT-Grundschutz, GDPR, DORA, ISO 22301, EU AI Act, ISO 42001, NIST CSF and KRITIS-DG are supported today. New frameworks are added regularly. If you need a specific framework, tell us in the demo.
How accurate are the cross-framework mappings?
Mappings come from a curated library that the KaitoSec compliance team builds and maintains, not from keyword matching. Where authoritative crosswalks exist (for example ENISA guidance for ISO 27001 to NIS2) they are the primary source. Customer-specific mappings are versioned alongside the library.
Can we customise the control library?
Yes. Custom controls can be added to a workspace and mapped manually to framework requirements. Custom controls behave identically to the library in gap analysis, SoA generation and reporting.
How does the SoA export work for ISO 27001 certification?
KaitoSec creates a structured SoA with applicability, justification and implementation state for Annex A controls. Export the approved version as PDF or share a controlled auditor view of the current working state.
What happens when one control covers multiple requirements?
KaitoSec shows the impact of a control across every relevant framework, including open gaps, missing evidence and the responsible owners.

Less work in your compliance mapping.
One control from your programme is enough. In thirty minutes you see which requirements it meets at once in KaitoSec and where a real gap remains.