
Policy Management: collect acknowledgements without chasing anyone.
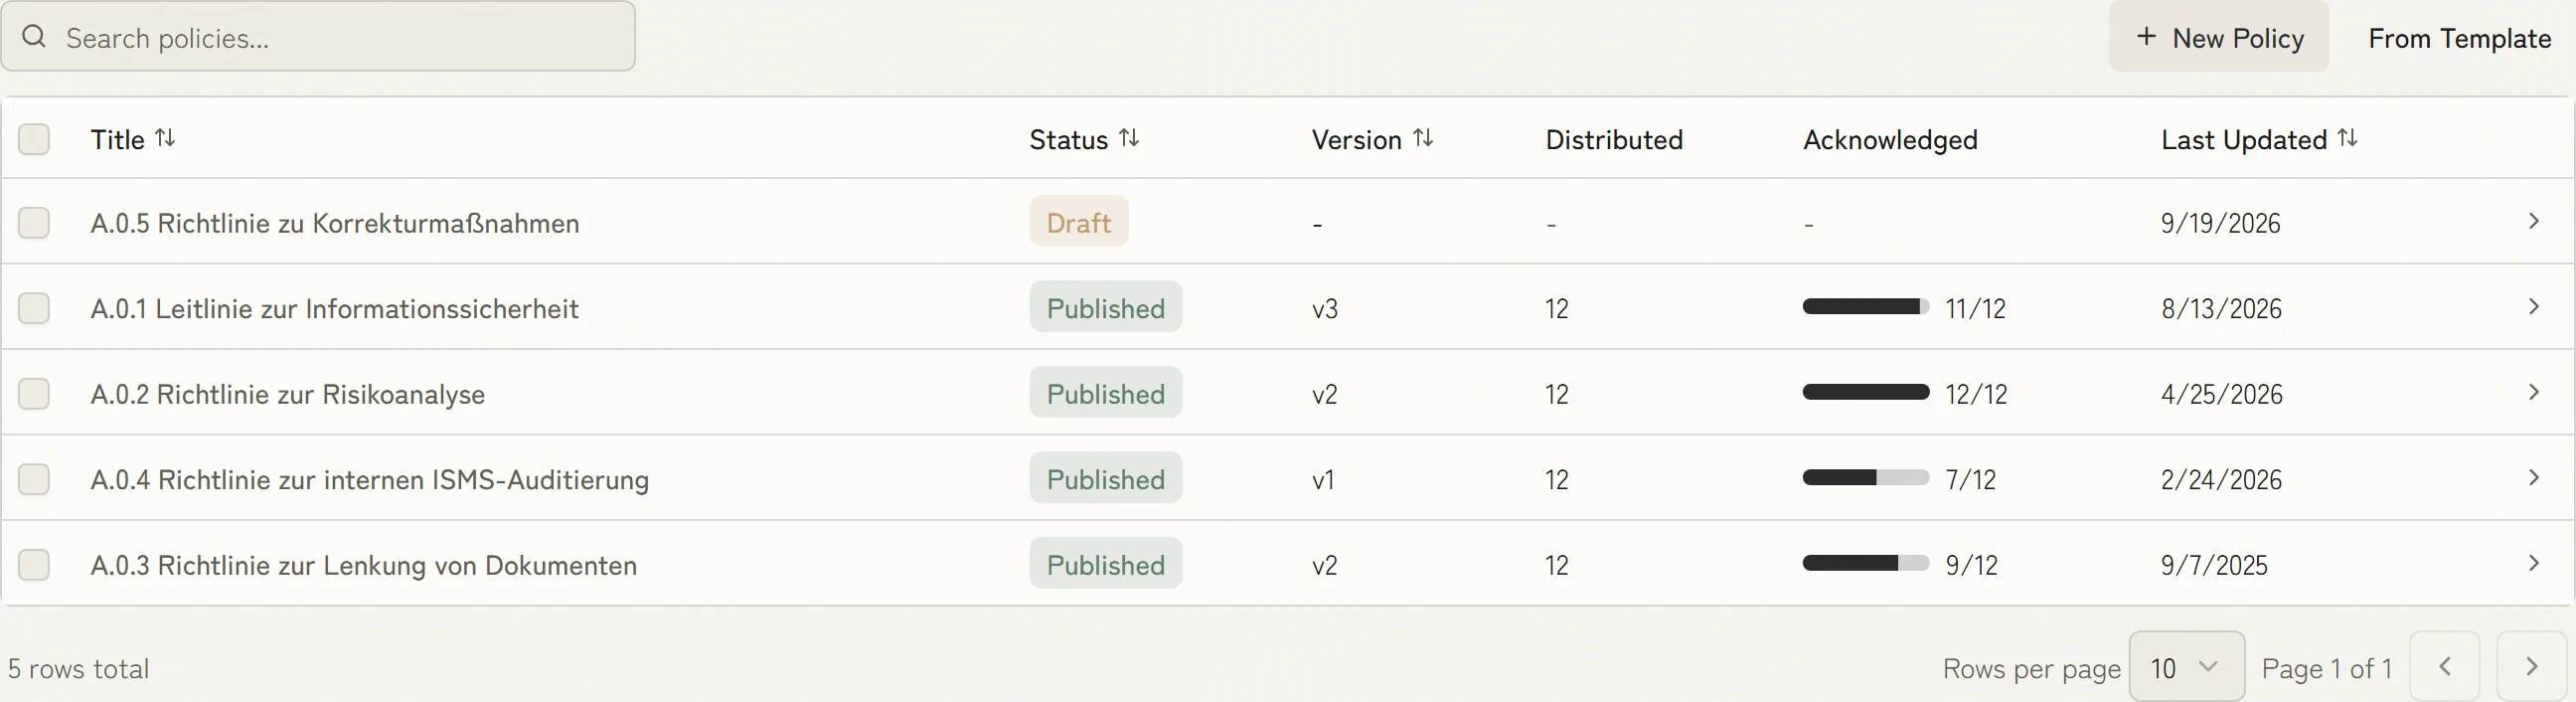
KaitoSec keeps version, approval, acknowledgements and the next review in one place. Staff see the current version, and the list of acknowledgements is ready for the audit.



 5.0 out of 5
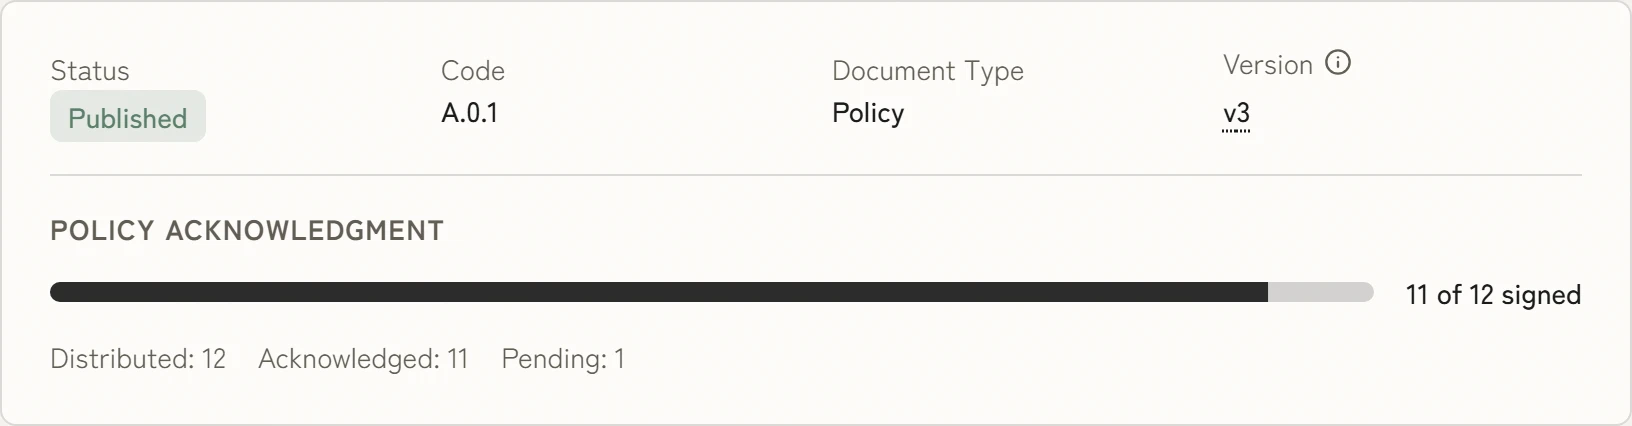
See who has acknowledged the version
You publish a version and see straight away who has acknowledged it and who is missing. In the audit you show that list instead of digging acknowledgements out of emails.
Book a demo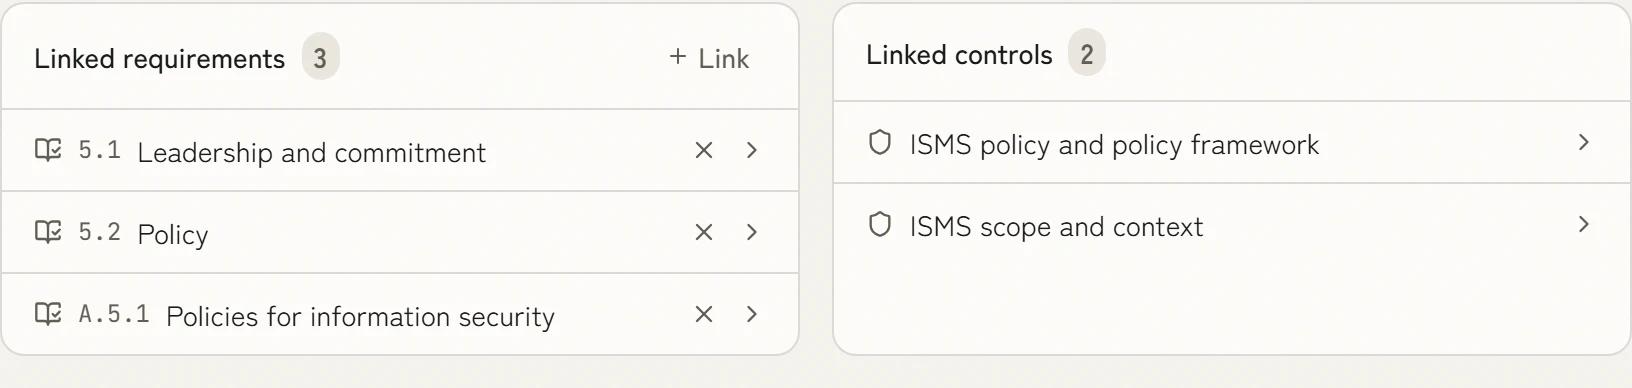
Every policy knows its requirements
The policy is linked to the requirements from ISO 27001, NIS2, Grundschutz, ISO 22301 or ISO 42001 and to the controls it implements. When the auditor asks for the evidence, the policy is one click away.
Book a demoNobody misses a recurring duty
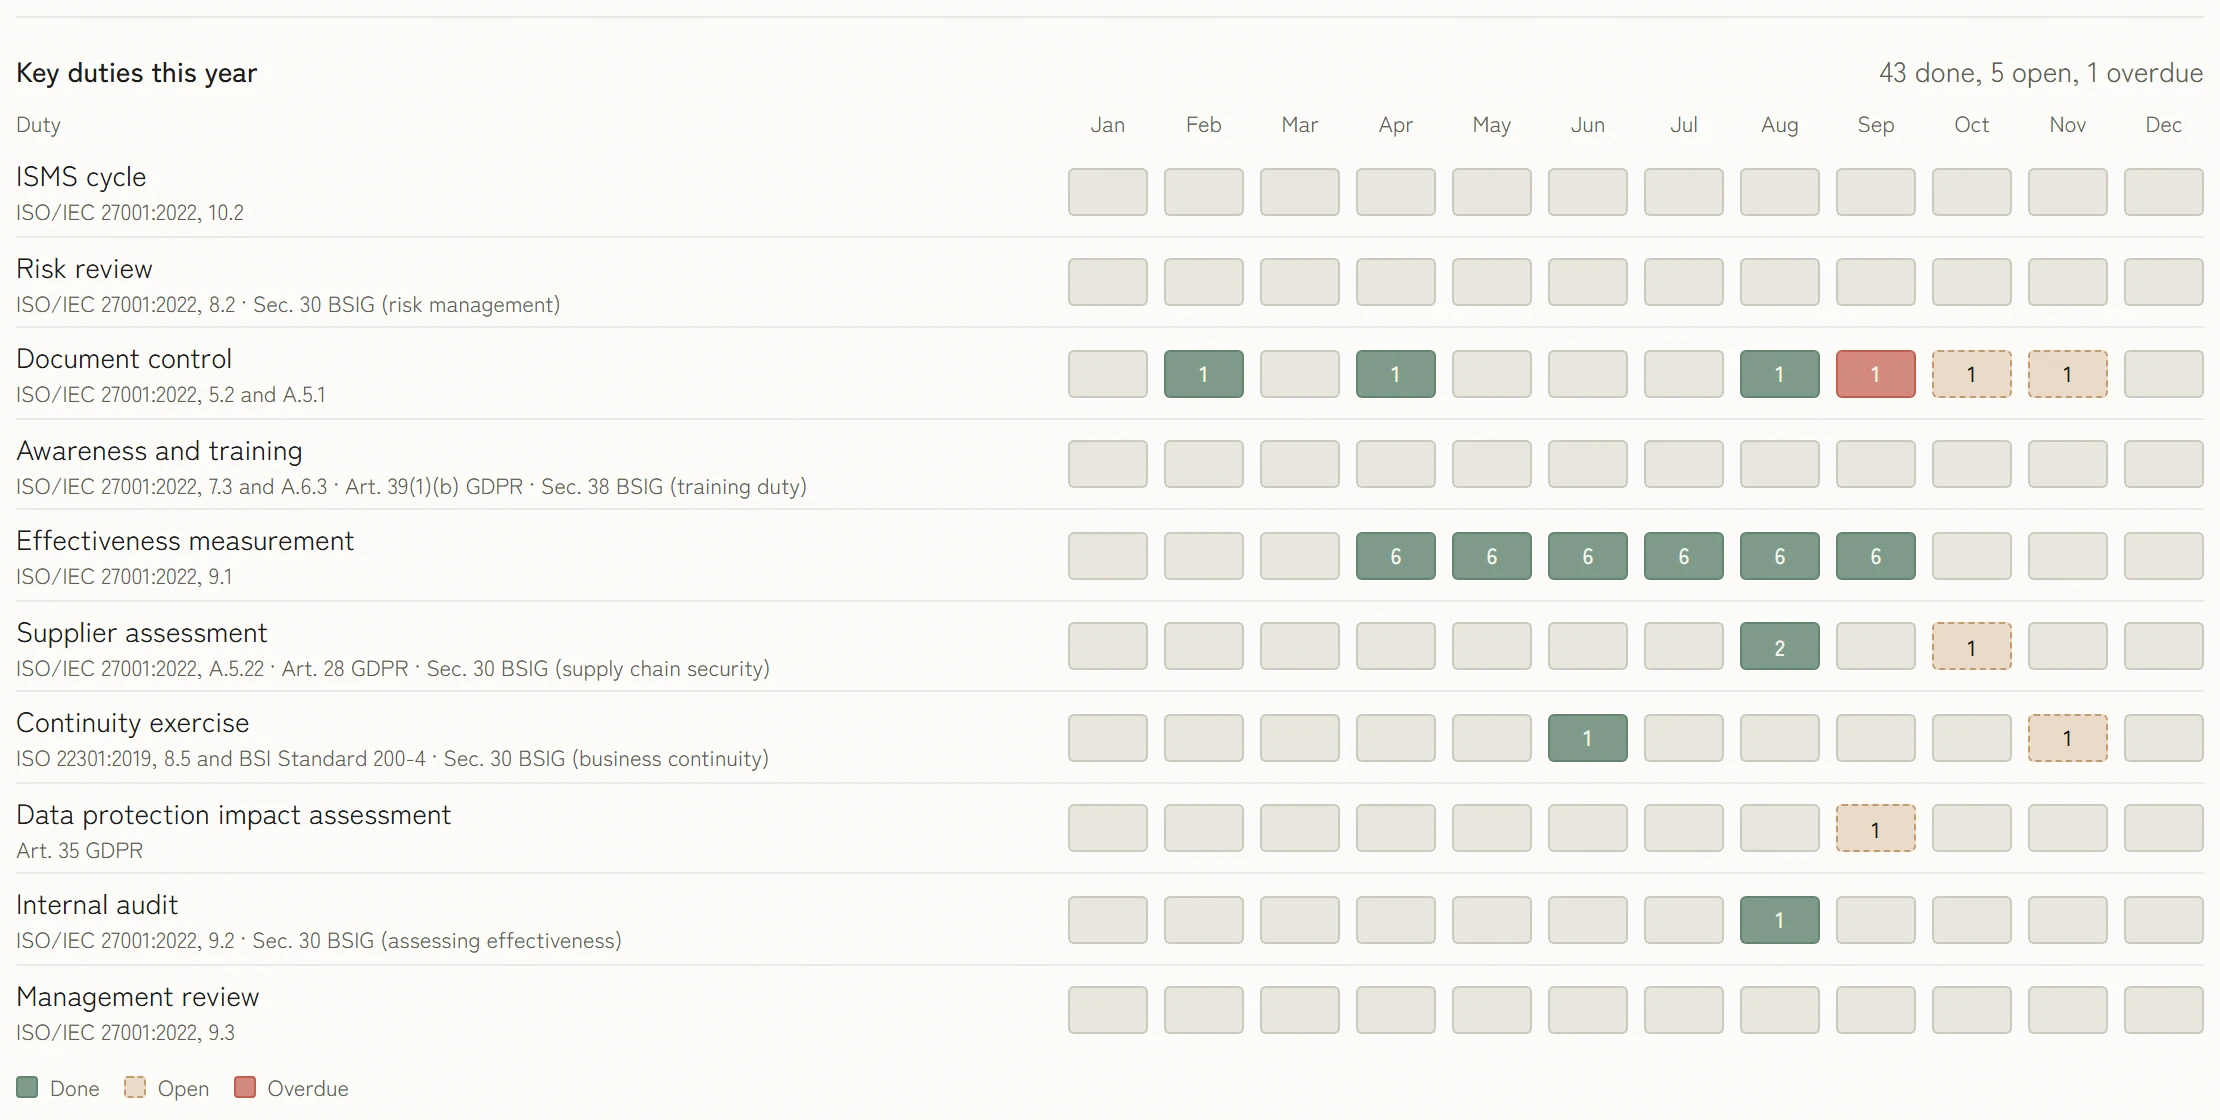
The annual plan shows per month which reviews and duties are done, open or overdue. KaitoSec reminds the owners before expiry, and outdated policies show up before the audit does.
- pre-mapped controls
- 100+100+
- of evidence created as the work is done
- 100 %100 %
- faster than manual work
- 10×10×
- management systems, one data model
- 4 in 14 in 1
What KaitoSec also does
These sit in the core of the platform and apply to every module.
Implemented once, done for every requirement.
More than 100 controls are already mapped to ISO 27001, NIS2, DORA and other requirements. You implement a control once and evidence it once. Every further requirement it covers costs no extra work.
You review and approve instead of filling empty fields.
Agents prepare the risk analysis, the statement of applicability and actions from audit reports. Every result is ready for approval. A person still makes the decision.
Nothing left to collect before the audit.
Evidence is created as the work gets done: a tested backup supplies its recovery time, a completed review its result. Your evidence is current every day, not just in the week before the audit.
Maintain policies without prior knowledge.
In simple mode your team works through the policies in order, and each one says what to do and why. Anyone who needs more detail switches to expert mode and sees the same policies with versions and approval paths.
You maintain each process only once.
Information security, business continuity management, data protection, AI governance and supplier management all work from the same process data. Every change takes effect in every system at once. Duplicate entry and conflicting registers go away.

Ask Chris how this would work for you.
Co-founder and CEO of KaitoSec. He walks through your case with you, live in the product.
Book a demo
The data for your policy management is already there.
100+ integrations
All integrations















FAQ
What policy templates are included?
The library includes templates for information security, access control, acceptable use, incident response, business continuity, data classification, supplier security and AI governance. Every template is a starting point and must be adapted to scope, organisation and legal context.
Can we customise templates for our organisation?
Yes. Every template is fully editable in the rich-text editor. You can add company-specific sections, update branding and adjust scope statements. Customised policies retain their framework linkages and version history.
How does policy management support ISO 27001 audits?
KaitoSec provides an audit-ready policy register listing every active policy, current version, approval date, review cycle and linkage to Annex A controls. The same register serves NIS2, ISO 22301 and ISO 42001 evidence without re-export.
Can policies be distributed to staff who do not use KaitoSec?
Yes. Acknowledgement requests are sent by email with a secure link. Recipients confirm they have read the policy in a browser, no account required. All acknowledgements are recorded and visible in the policy audit trail.

Less work in your policy management.
One policy from your library is enough. In thirty minutes you see how KaitoSec keeps version, approval, acknowledgement and next review together.