
KRITIS-DG: physical security and cyber in one programme.
The act requires physical security, supply-chain resilience and emergency preparedness on top of cybersecurity. KaitoSec runs it on the same data model as your ISMS and BCMS, and what you do for NIS2 counts here too.

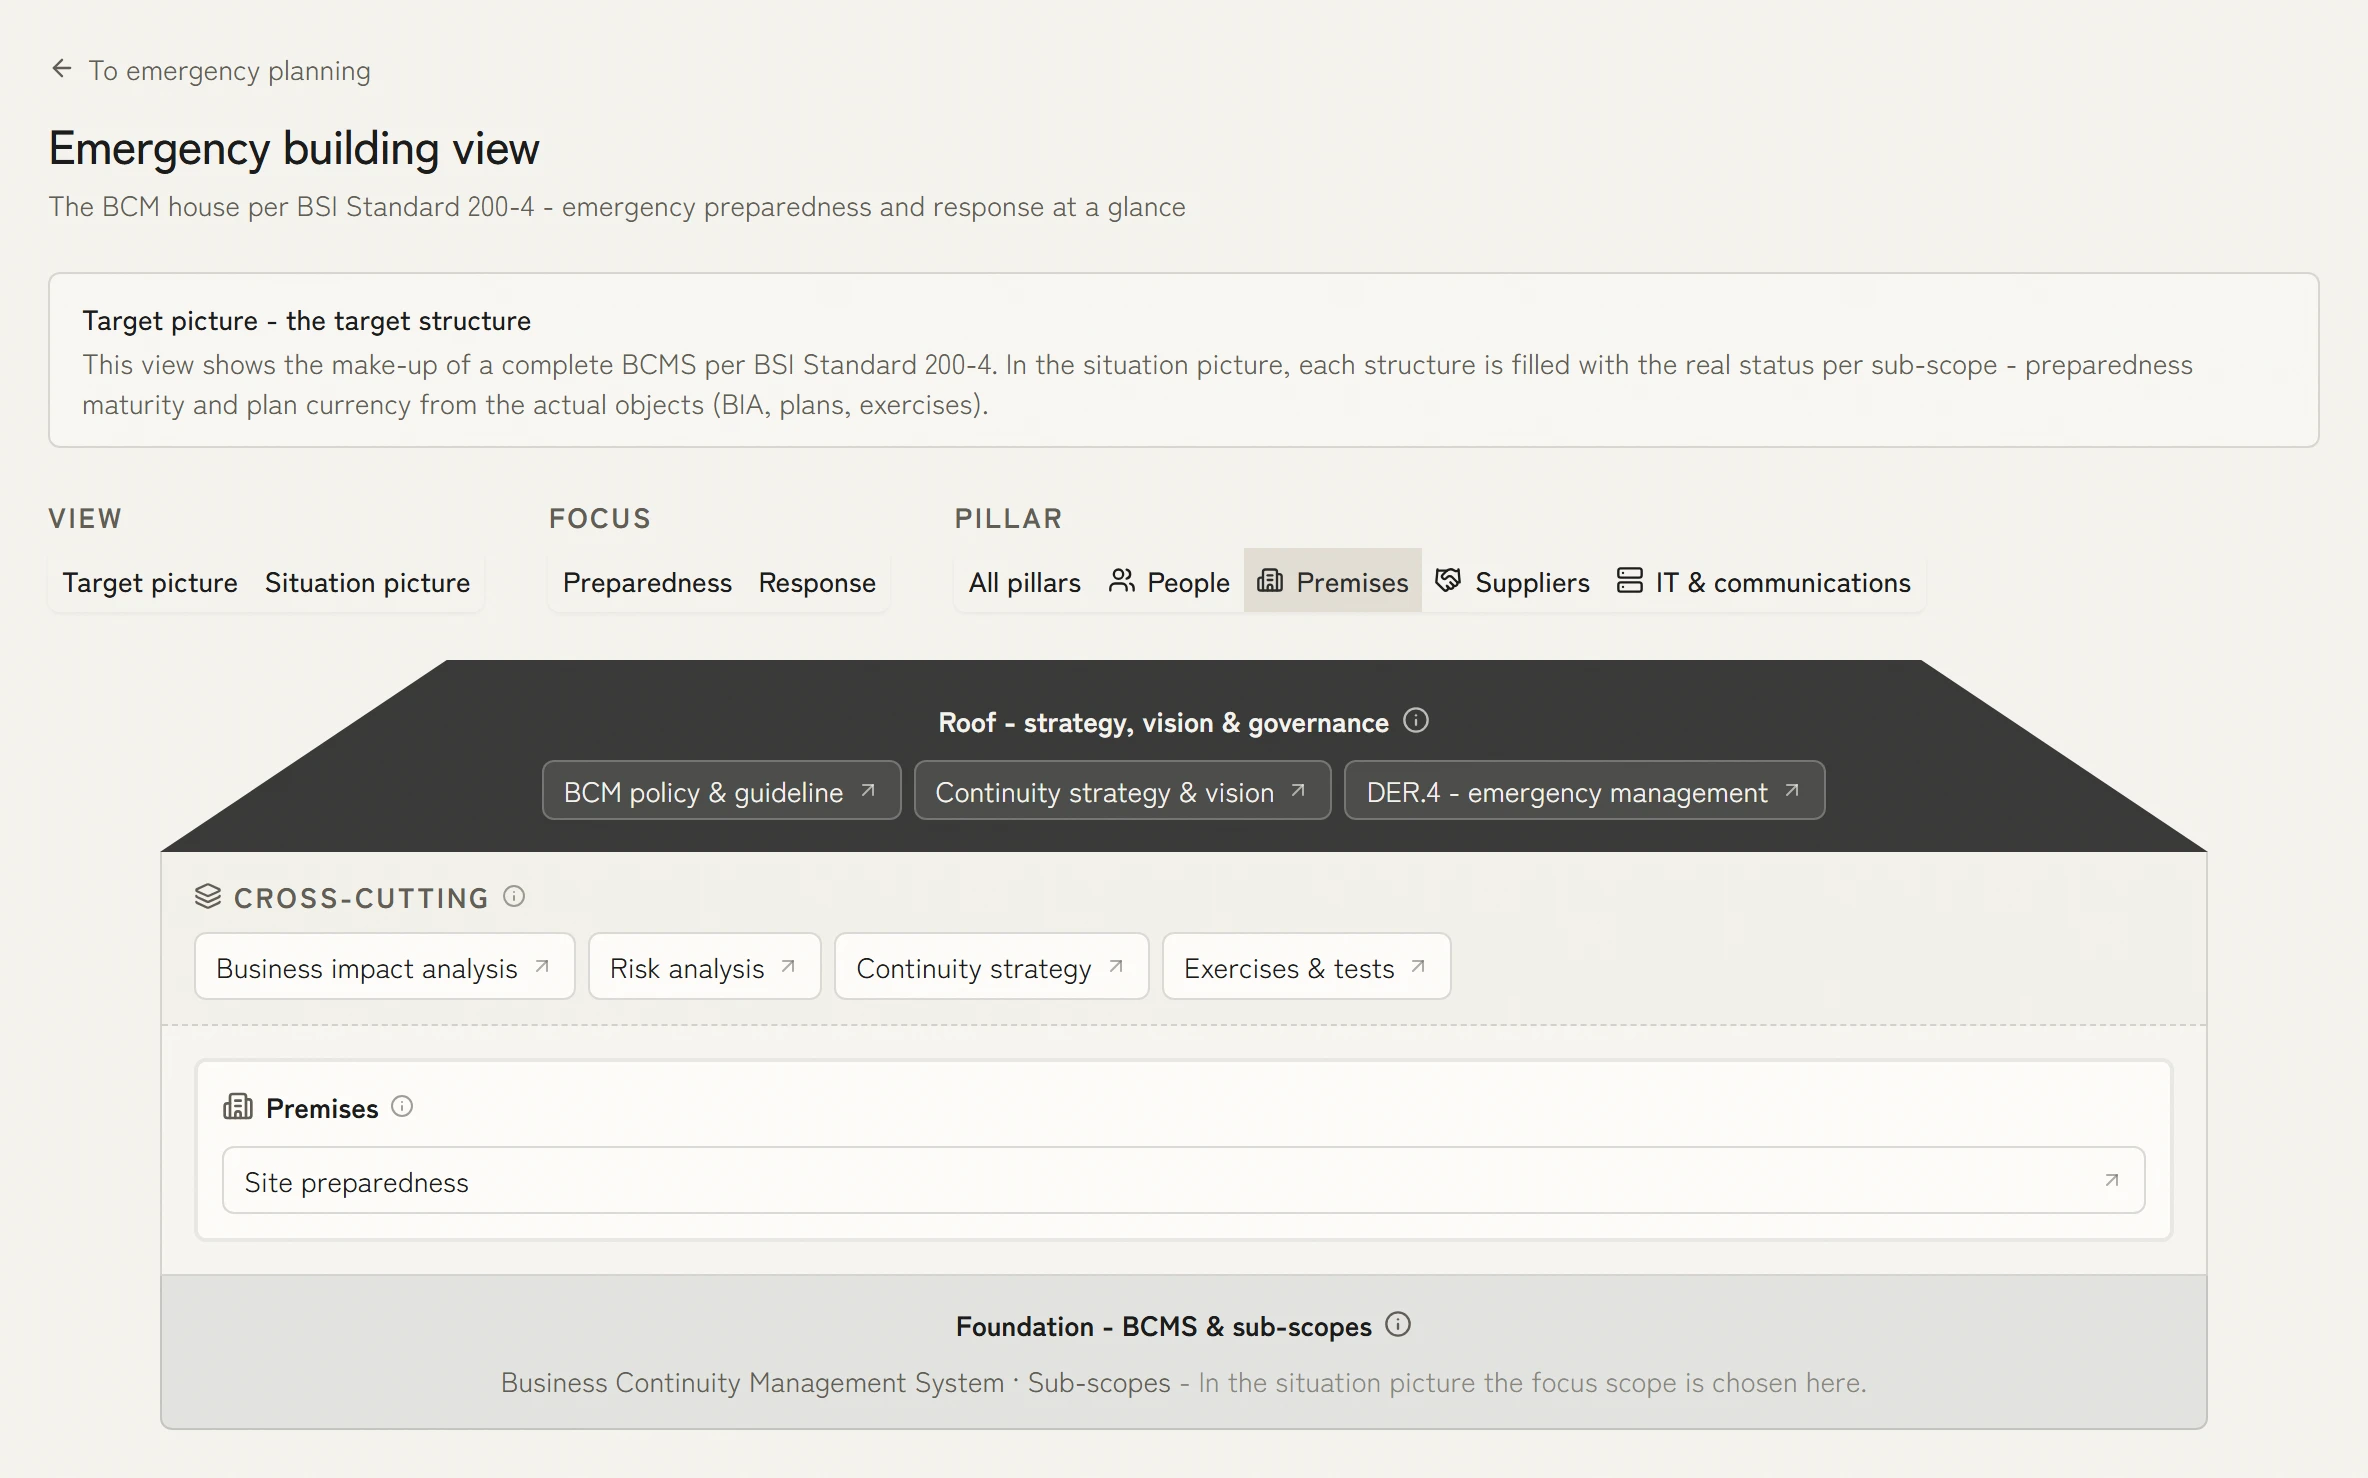


 5.0 out of 5
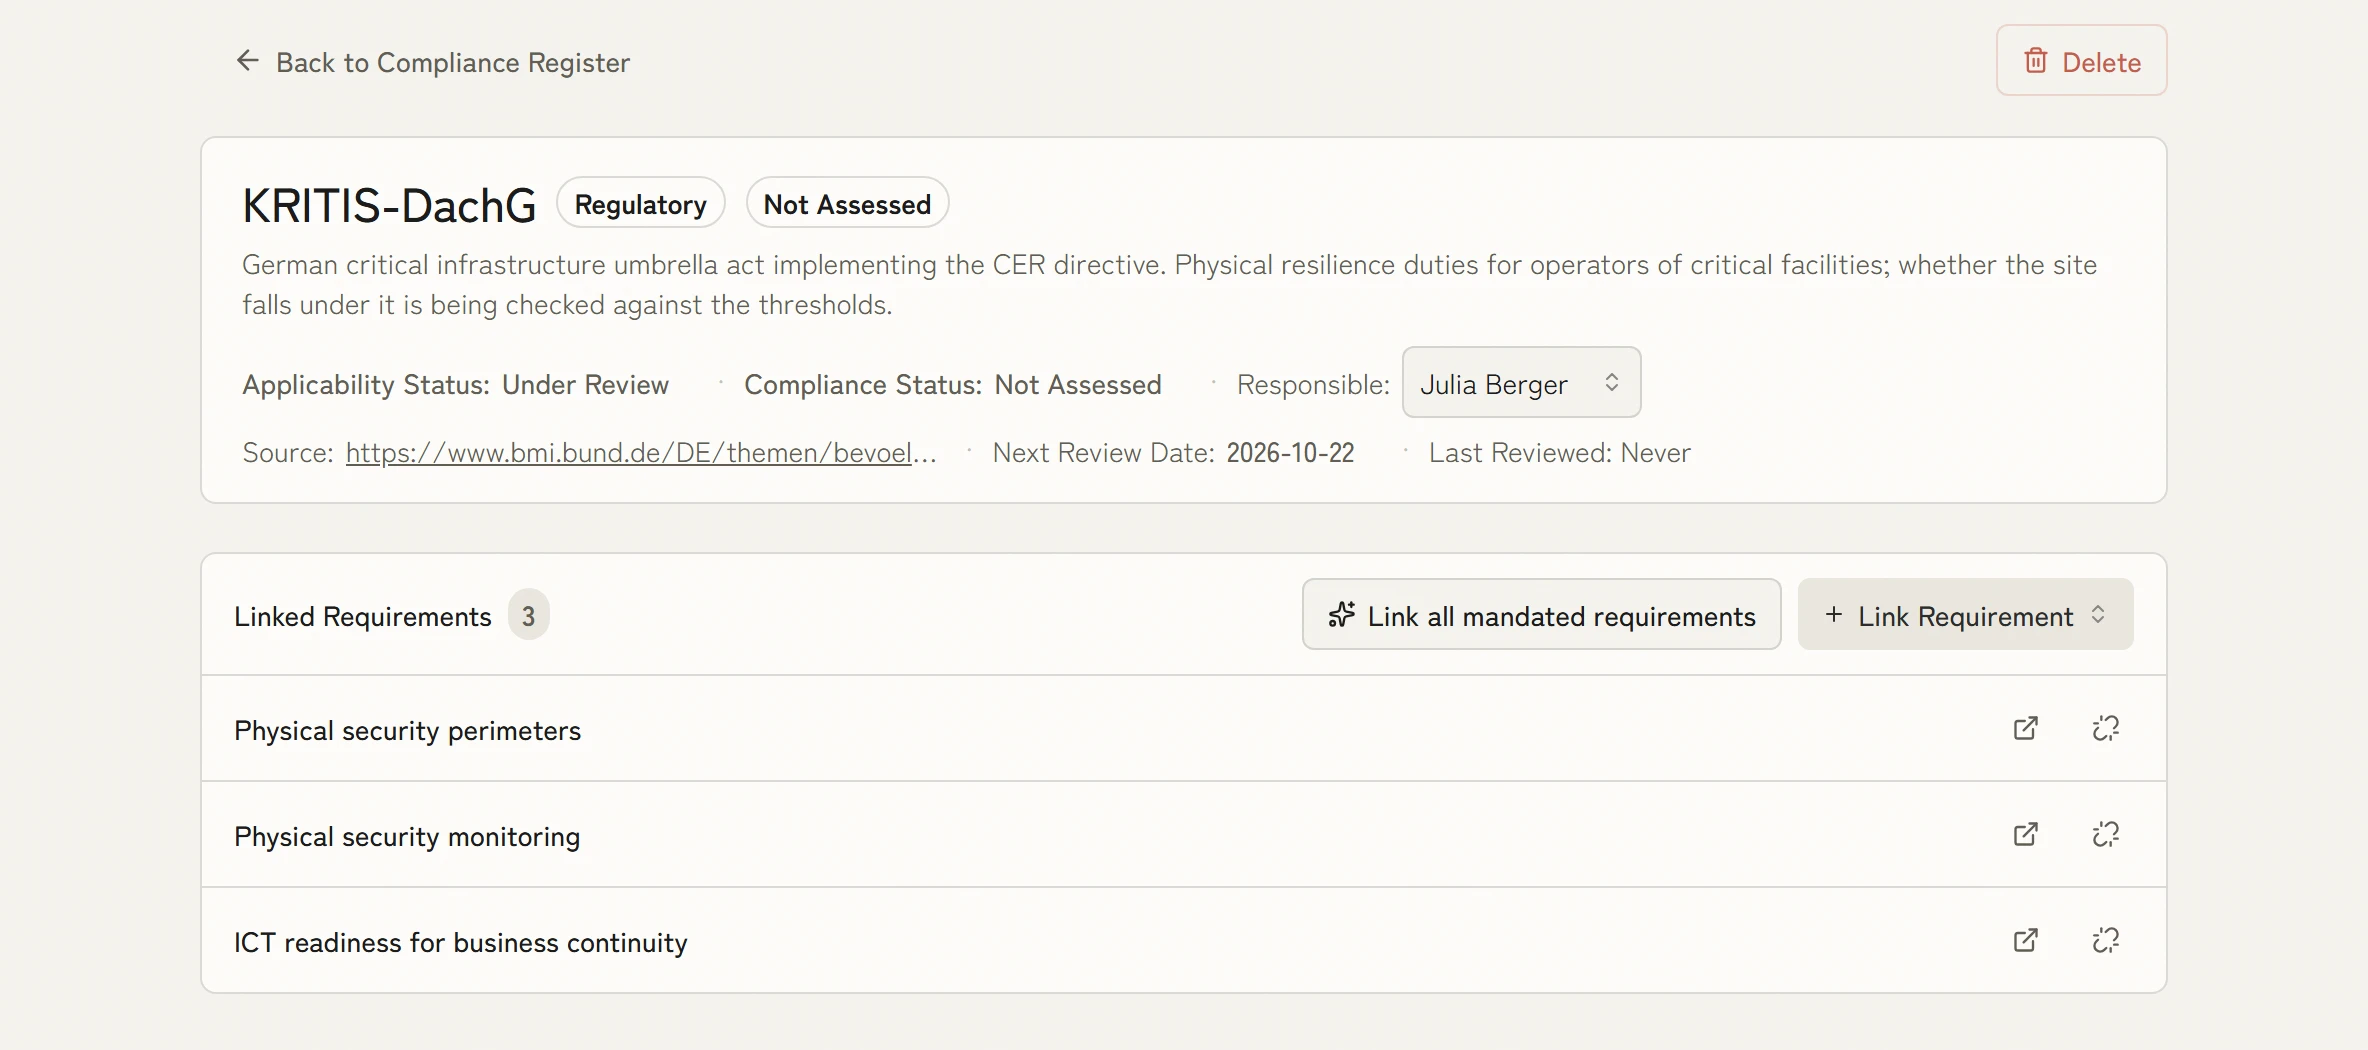
The obligation with an owner and a review date
The act sits in the compliance register like any other legal obligation, with status, owner, next review date and the linked requirements on physical security and emergency preparedness. While it is still being checked whether a site falls in scope, that is exactly what the record says.
11 sectorsCER critical-entity sectors transposed into German law
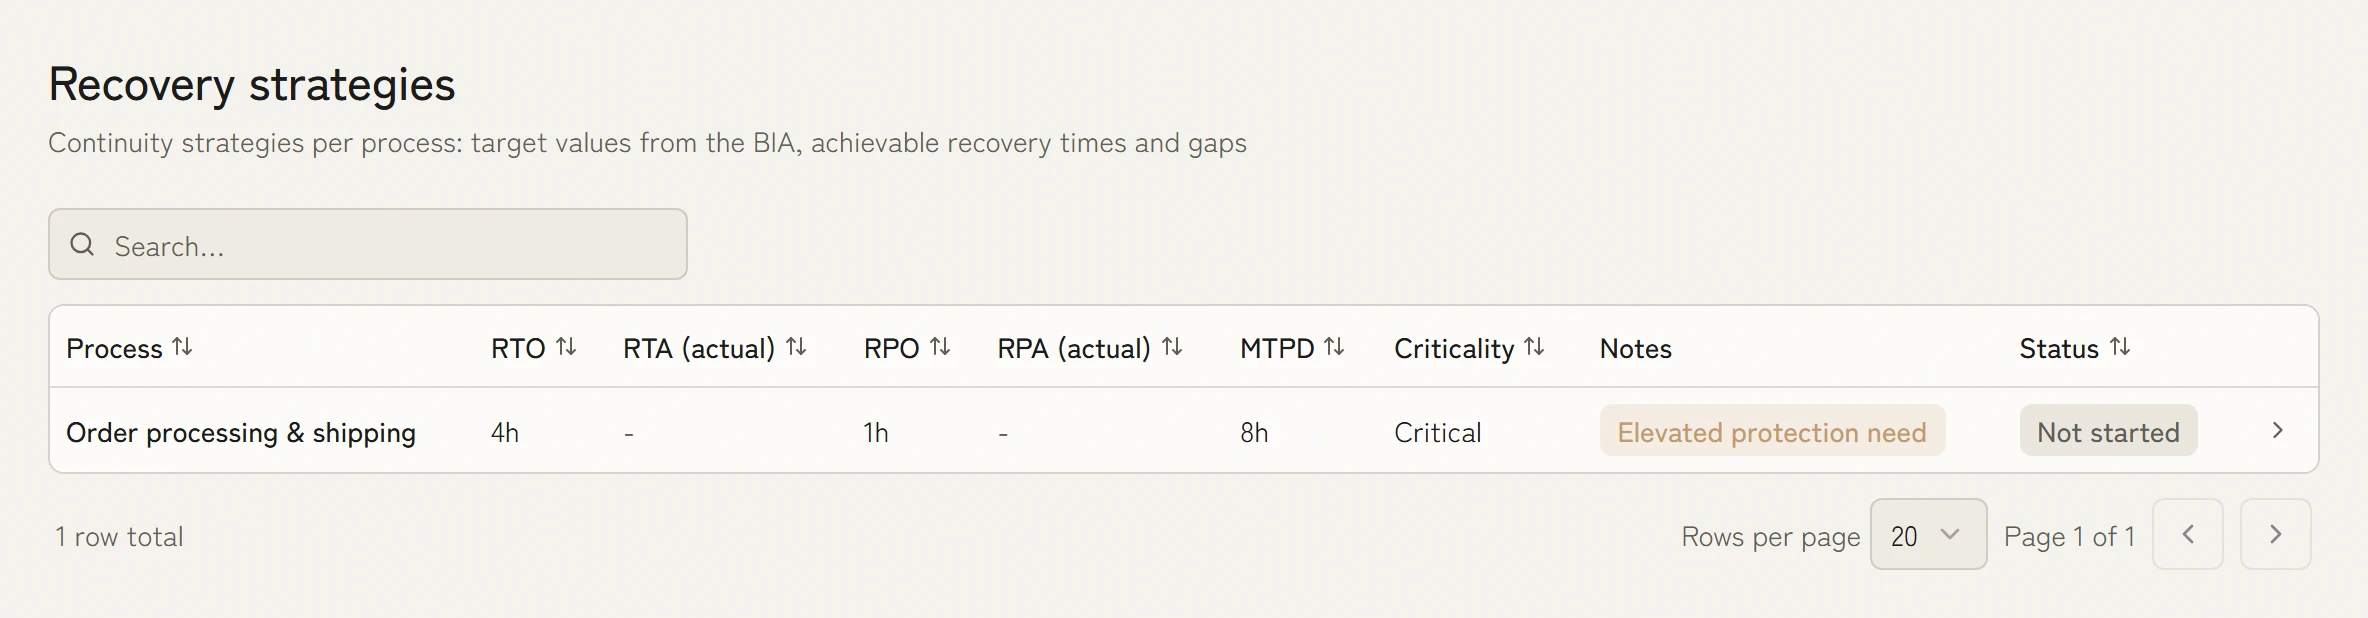
Targets and achievable times side by side
For each process, the recovery strategy shows what the BIA asks for in RTO, RPO and MTPD and what the chosen solution delivers today. The gap between the two is the statement a supervisor wants to hear.
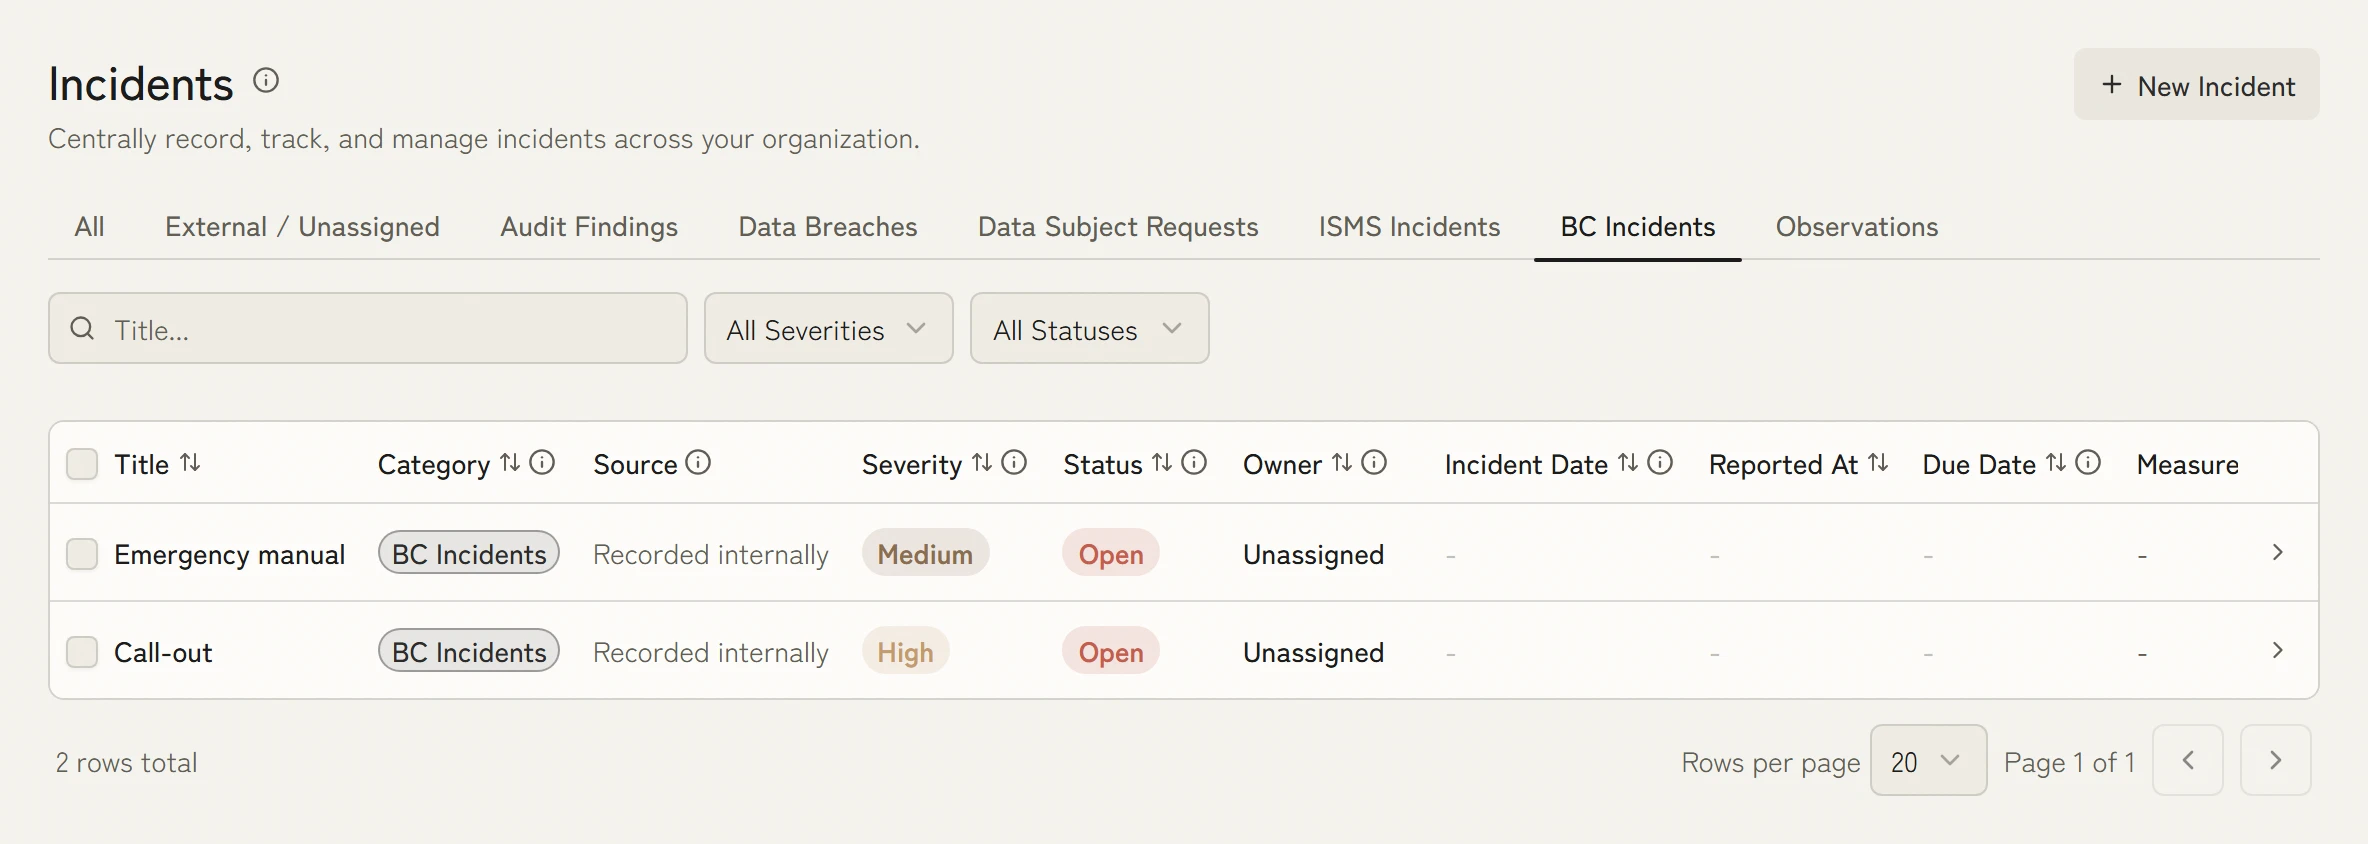
Emergencies run in the same case as attacks
Alerting, the emergency manual and the loss of a site run with severity and status in the same incident workflow as attacks on IT. What happened during the event feeds the notification under KRITIS-DG and, where there is a cyber element, the NIS2 notification.
KRITIS-DG and NIS2 on the same controls
Most operators carry both regimes at once. KaitoSec maps them onto the same controls, so an investment made for one counts as evidence for the other. That leaves no parallel programmes and no duplicate audit cycles.
2 regimesKRITIS-DG and NIS2 cross-mapped onto the same controls
Connect KRITIS-DG with other standards
Connect the resilience obligations with the management systems that evidence them.
- NIS2EU cybersecurity directiveLearn more
- ISO 22301The international BCM standardLearn more
- BSI IT-GrundschutzGerman baseline IT securityLearn more
KRITIS-DG by company and role
More for the KRITIS-Dachgesetz
Beyond cybersecurity
KRITIS-DG obliges operators of critical entities beyond cybersecurity: physical security, supply chain resilience and organisational continuity. KaitoSec models those layers on one inventory.
One resilience programme, two regimes
Most KRITIS operators carry both KRITIS-DG and NIS2 obligations. KaitoSec maps the two regimes against the same controls so an investment made for one is captured as evidence for the other. That leaves no parallel programmes and no duplicate audit cycles.
BCMS and physical security on one inventory
The ISO 22301 BCMS, the asset register, the supplier list and the physical-site catalogue live in one workspace. A failure of a primary site, a supplier or an ICT system traces through the same BIA chain that feeds your CER reporting.
Track obligations, evidence and deadlines
A single view of your KRITIS-DG obligations: sector classification, designated entities, physical security measures, BC plans, incident notifications and supervisory deadlines. Each obligation shows ownership, evidence status and the next supervisory checkpoint.
Physical and ICT asset register on one model
Sites, perimeters, controlled areas, ICT systems and processing activities share the same inventory. The KRITIS-DG resilience plan and the ISO 22301 BIA both read from the same source.
Incident notification and reporting
KRITIS-DG inherits the EU CER incident notification structure. KaitoSec calculates the relevant reporting deadlines, pre-fills the notification template, and connects the supervisory submission to the same incident workflow that feeds NIS2 reporting.
What the KRITIS-Dachgesetz requires
The KRITIS-Dachgesetz transposes the EU CER Directive into German law and reaches beyond cybersecurity: physical security of the facilities, supply-chain resilience, organisational continuity, notification of significant incidents and evidence towards the supervisor. For many operators it applies on top of NIS2.
Frequently asked questions about the KRITIS-Dachgesetz
What is the KRITIS-Dachgesetz?
The KRITIS-Dachgesetz is the German law transposing the EU Critical Entities Resilience (CER) Directive 2022/2557, in force since March 2026. It defines critical entities across 11 sectors and obliges their operators to maintain physical security, business continuity and supply-chain resilience measures, on top of the cybersecurity obligations that NIS2 imposes.
How does KRITIS-DG relate to NIS2 and BSIG?
NIS2 (transposed in Germany through the NIS2UmsuCG) governs cybersecurity for essential and important entities. KRITIS-DG governs physical and organisational resilience for critical entities. The two regimes overlap heavily for operators and are intended to be implemented together. The BSIG was rewritten by the NIS2UmsuCG, in force since 6 December 2025, and governs the cyber obligations, including those of operators of critical facilities. For a deeper comparison, read our article on how KRITIS-DG and NIS2 relate in practice.
Who is in scope of KRITIS-DG?
Operators in 11 sectors including energy, transport, banking, financial market infrastructure, health, drinking water, wastewater, digital infrastructure, public administration, space and food. The Bundesamt für Bevölkerungsschutz und Katastrophenhilfe (BBK) plays the supervisory role together with the BSI for cyber matters.
We already run NIS2. What does KRITIS-DG add?
Most of your cybersecurity controls already serve KRITIS-DG. What KRITIS-DG adds is the physical, organisational and supply-chain resilience dimension: site security, BC plans for non-ICT disruption, supplier resilience and resilience plans for the entity as a whole. KaitoSec models these on top of the same asset register your ISMS and BCMS already use.

Your resilience plan in thirty minutes.
In the demo we settle scope, physical preparedness, recovery and reporting paths. You leave knowing what KRITIS-DG adds on top of NIS2.