
SOC 2 with an evidence trail, not screenshot diaries.
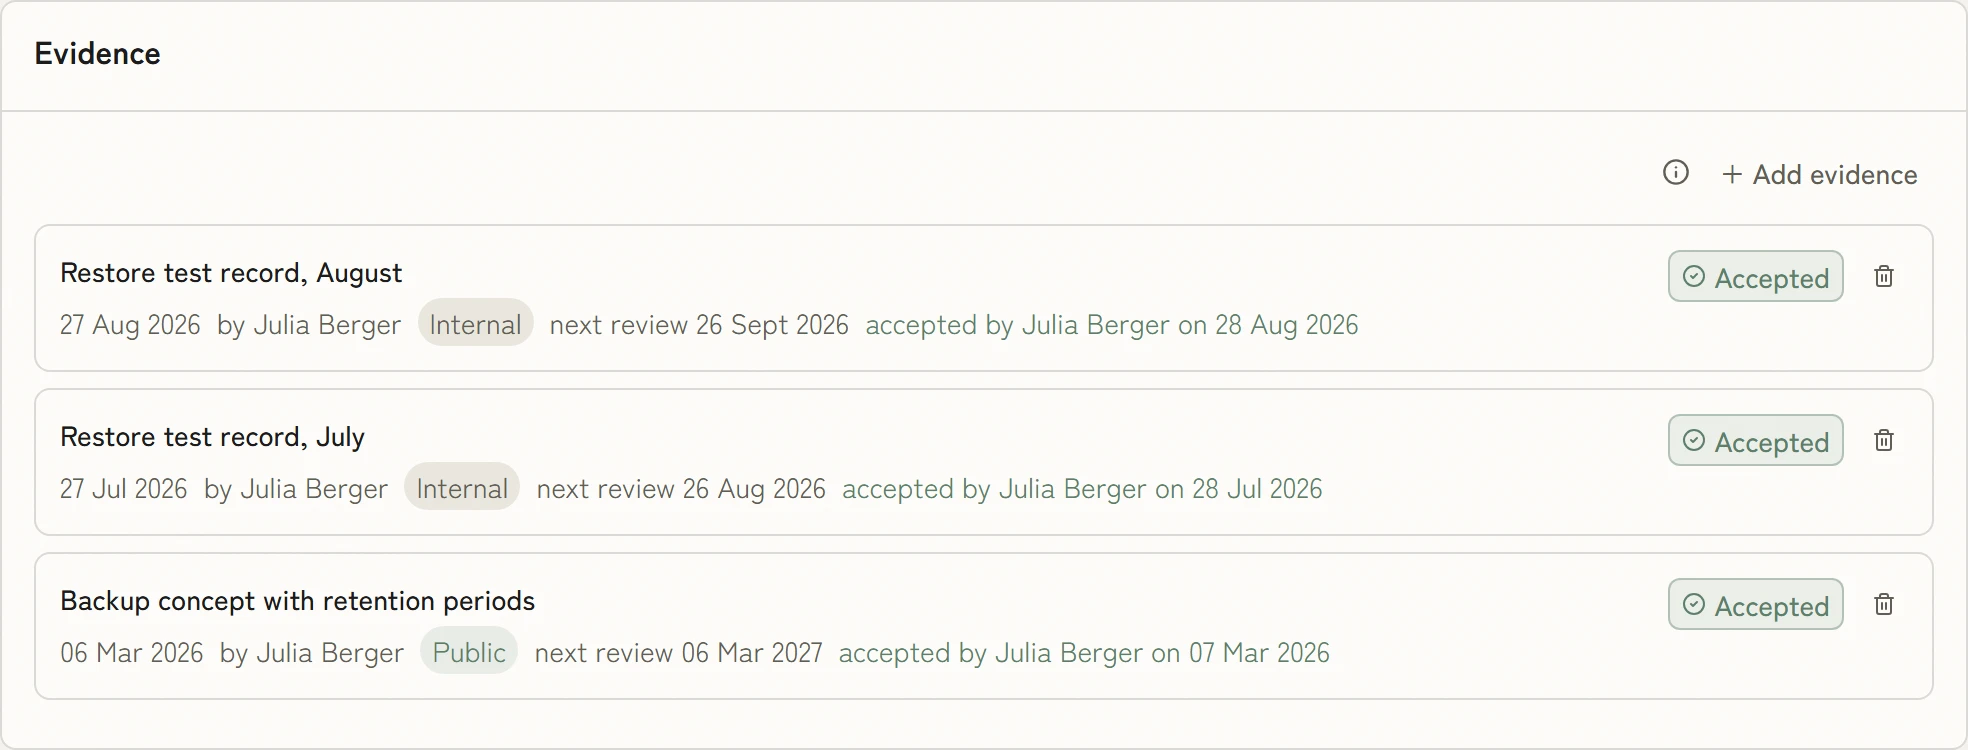
Map the Trust Services Criteria to your controls and reuse what you have already implemented for ISO 27001. Evidence builds up on the record across the observation period instead of being gathered just before the report.



 5.0 out of 5
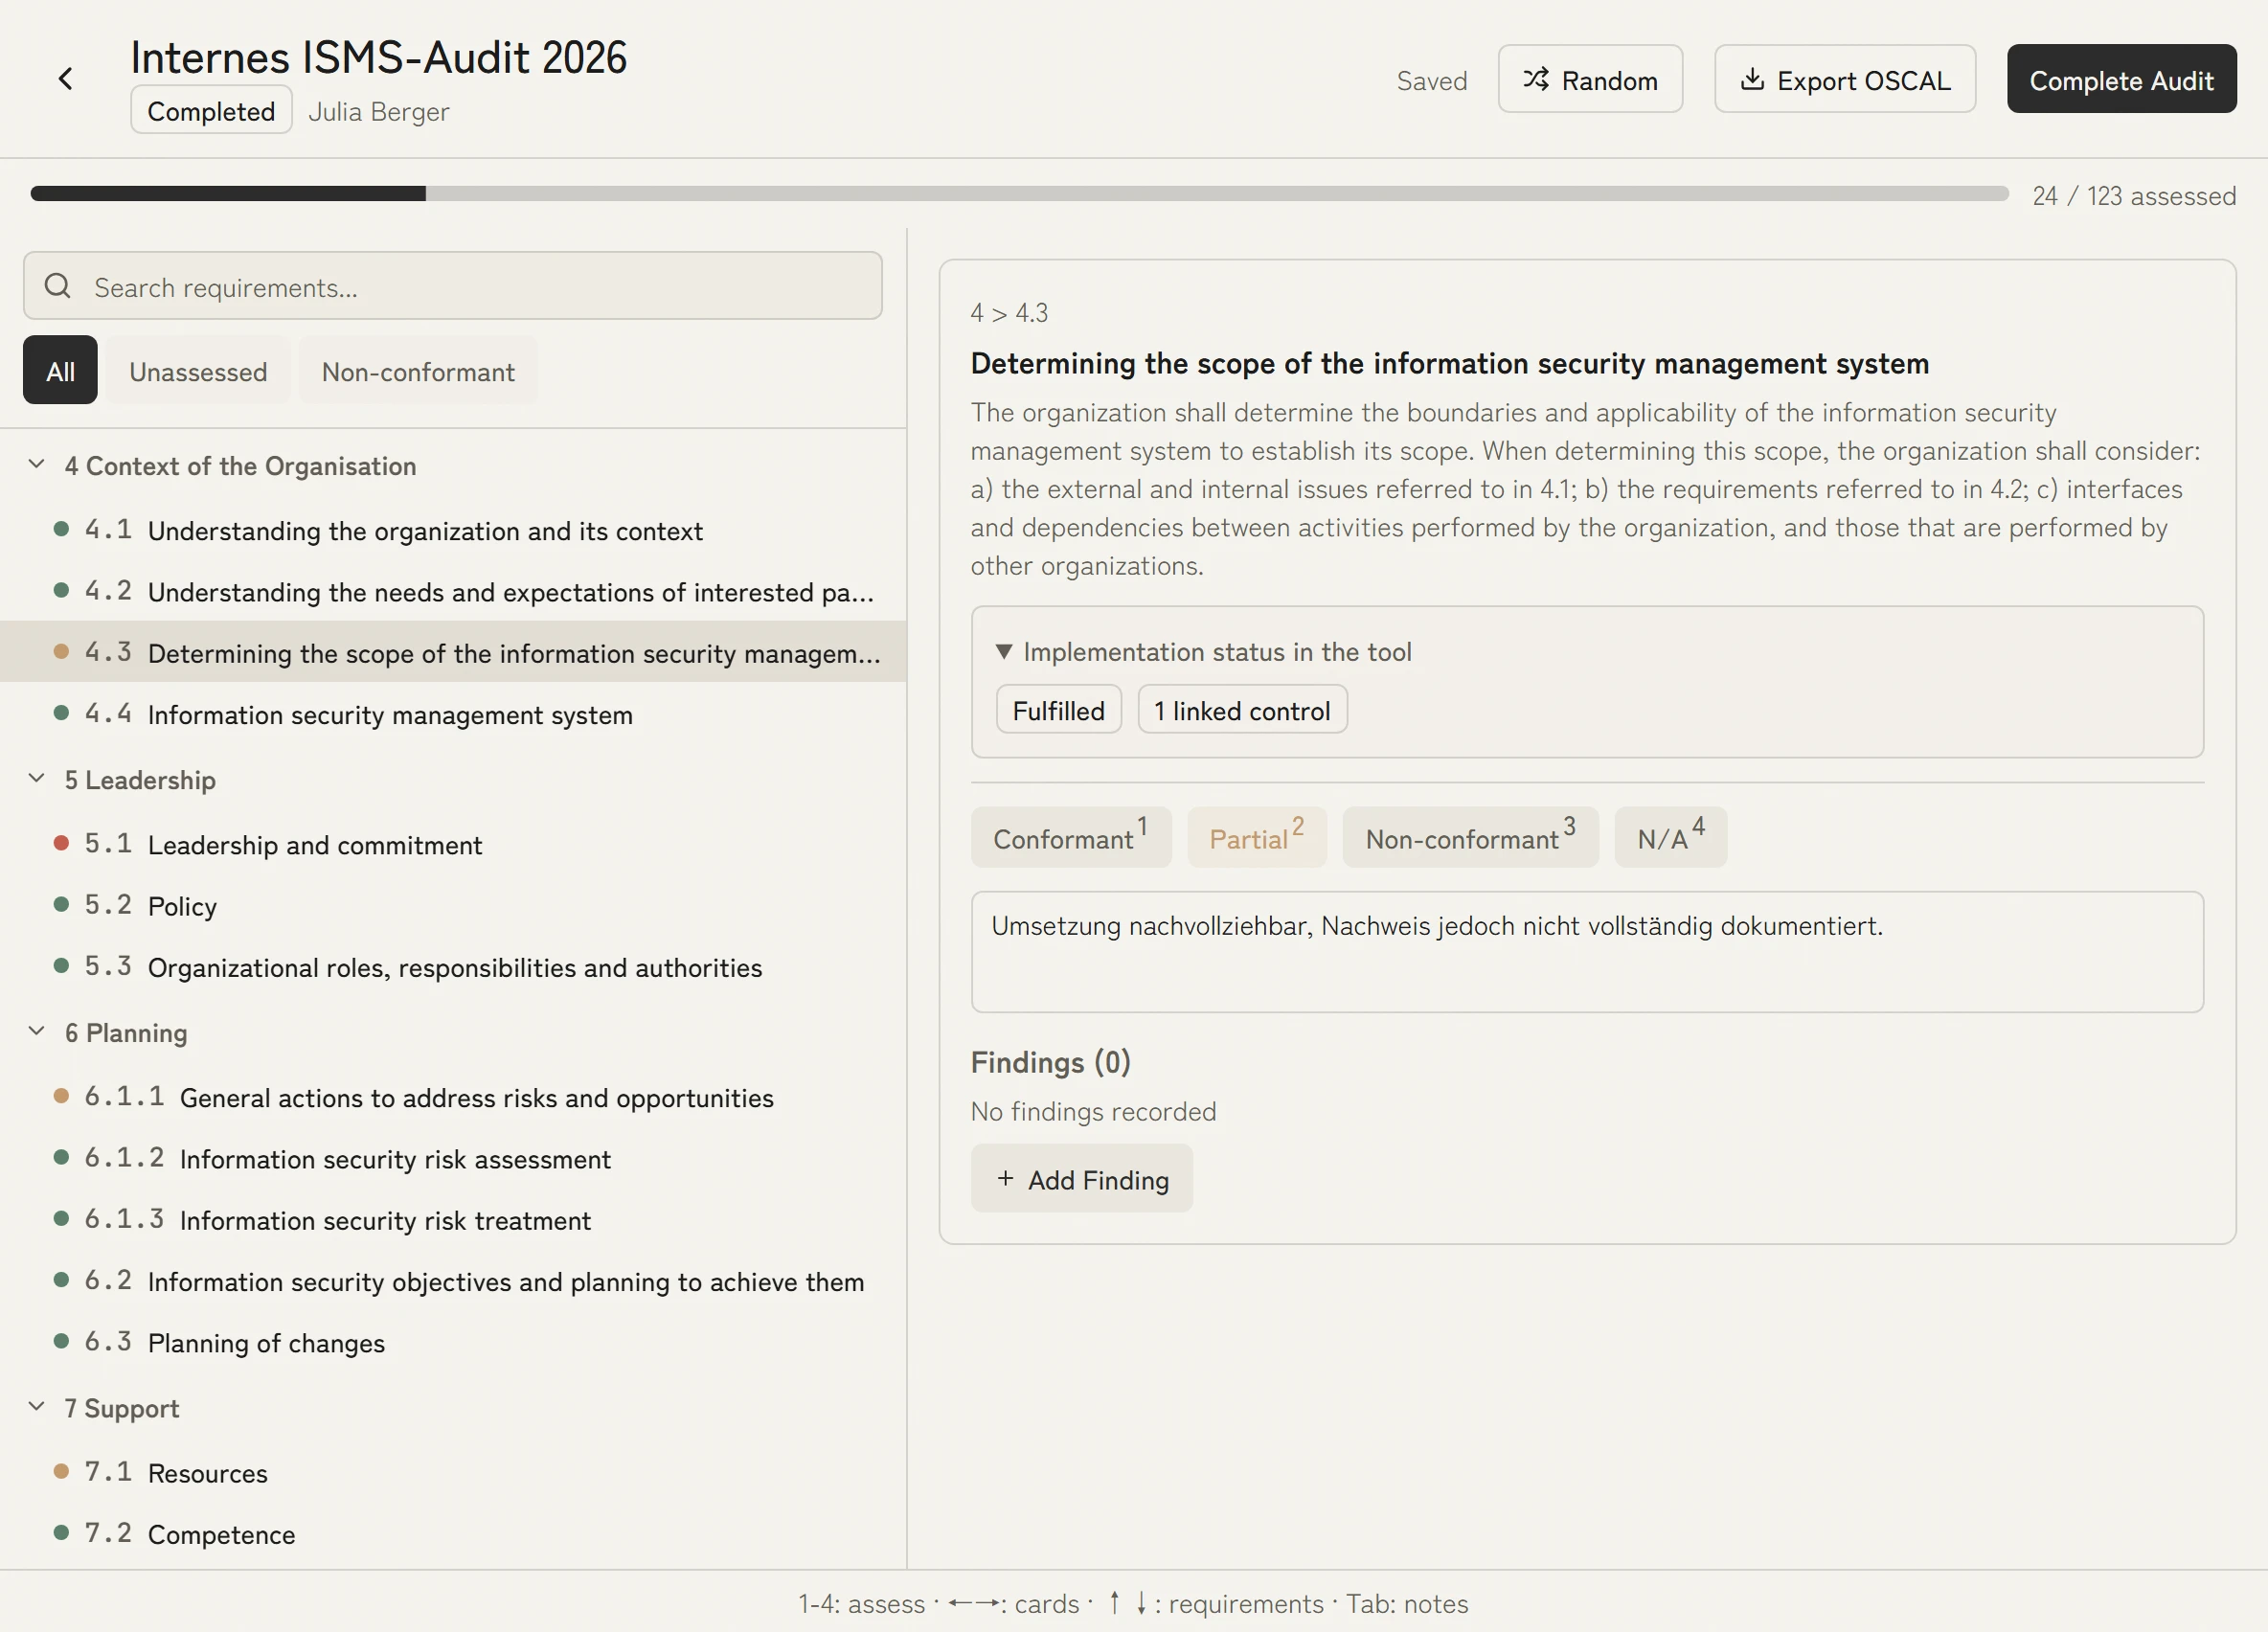
Work with the auditor in the same state
The auditor rates requirement by requirement as compliant, partially compliant or non-compliant and attaches notes and findings to the record itself. Fieldwork happens where the evidence lives, not across email chains and shared drives.
2 report typesType I point-in-time and Type II over observation period
Metrics that evidence the period
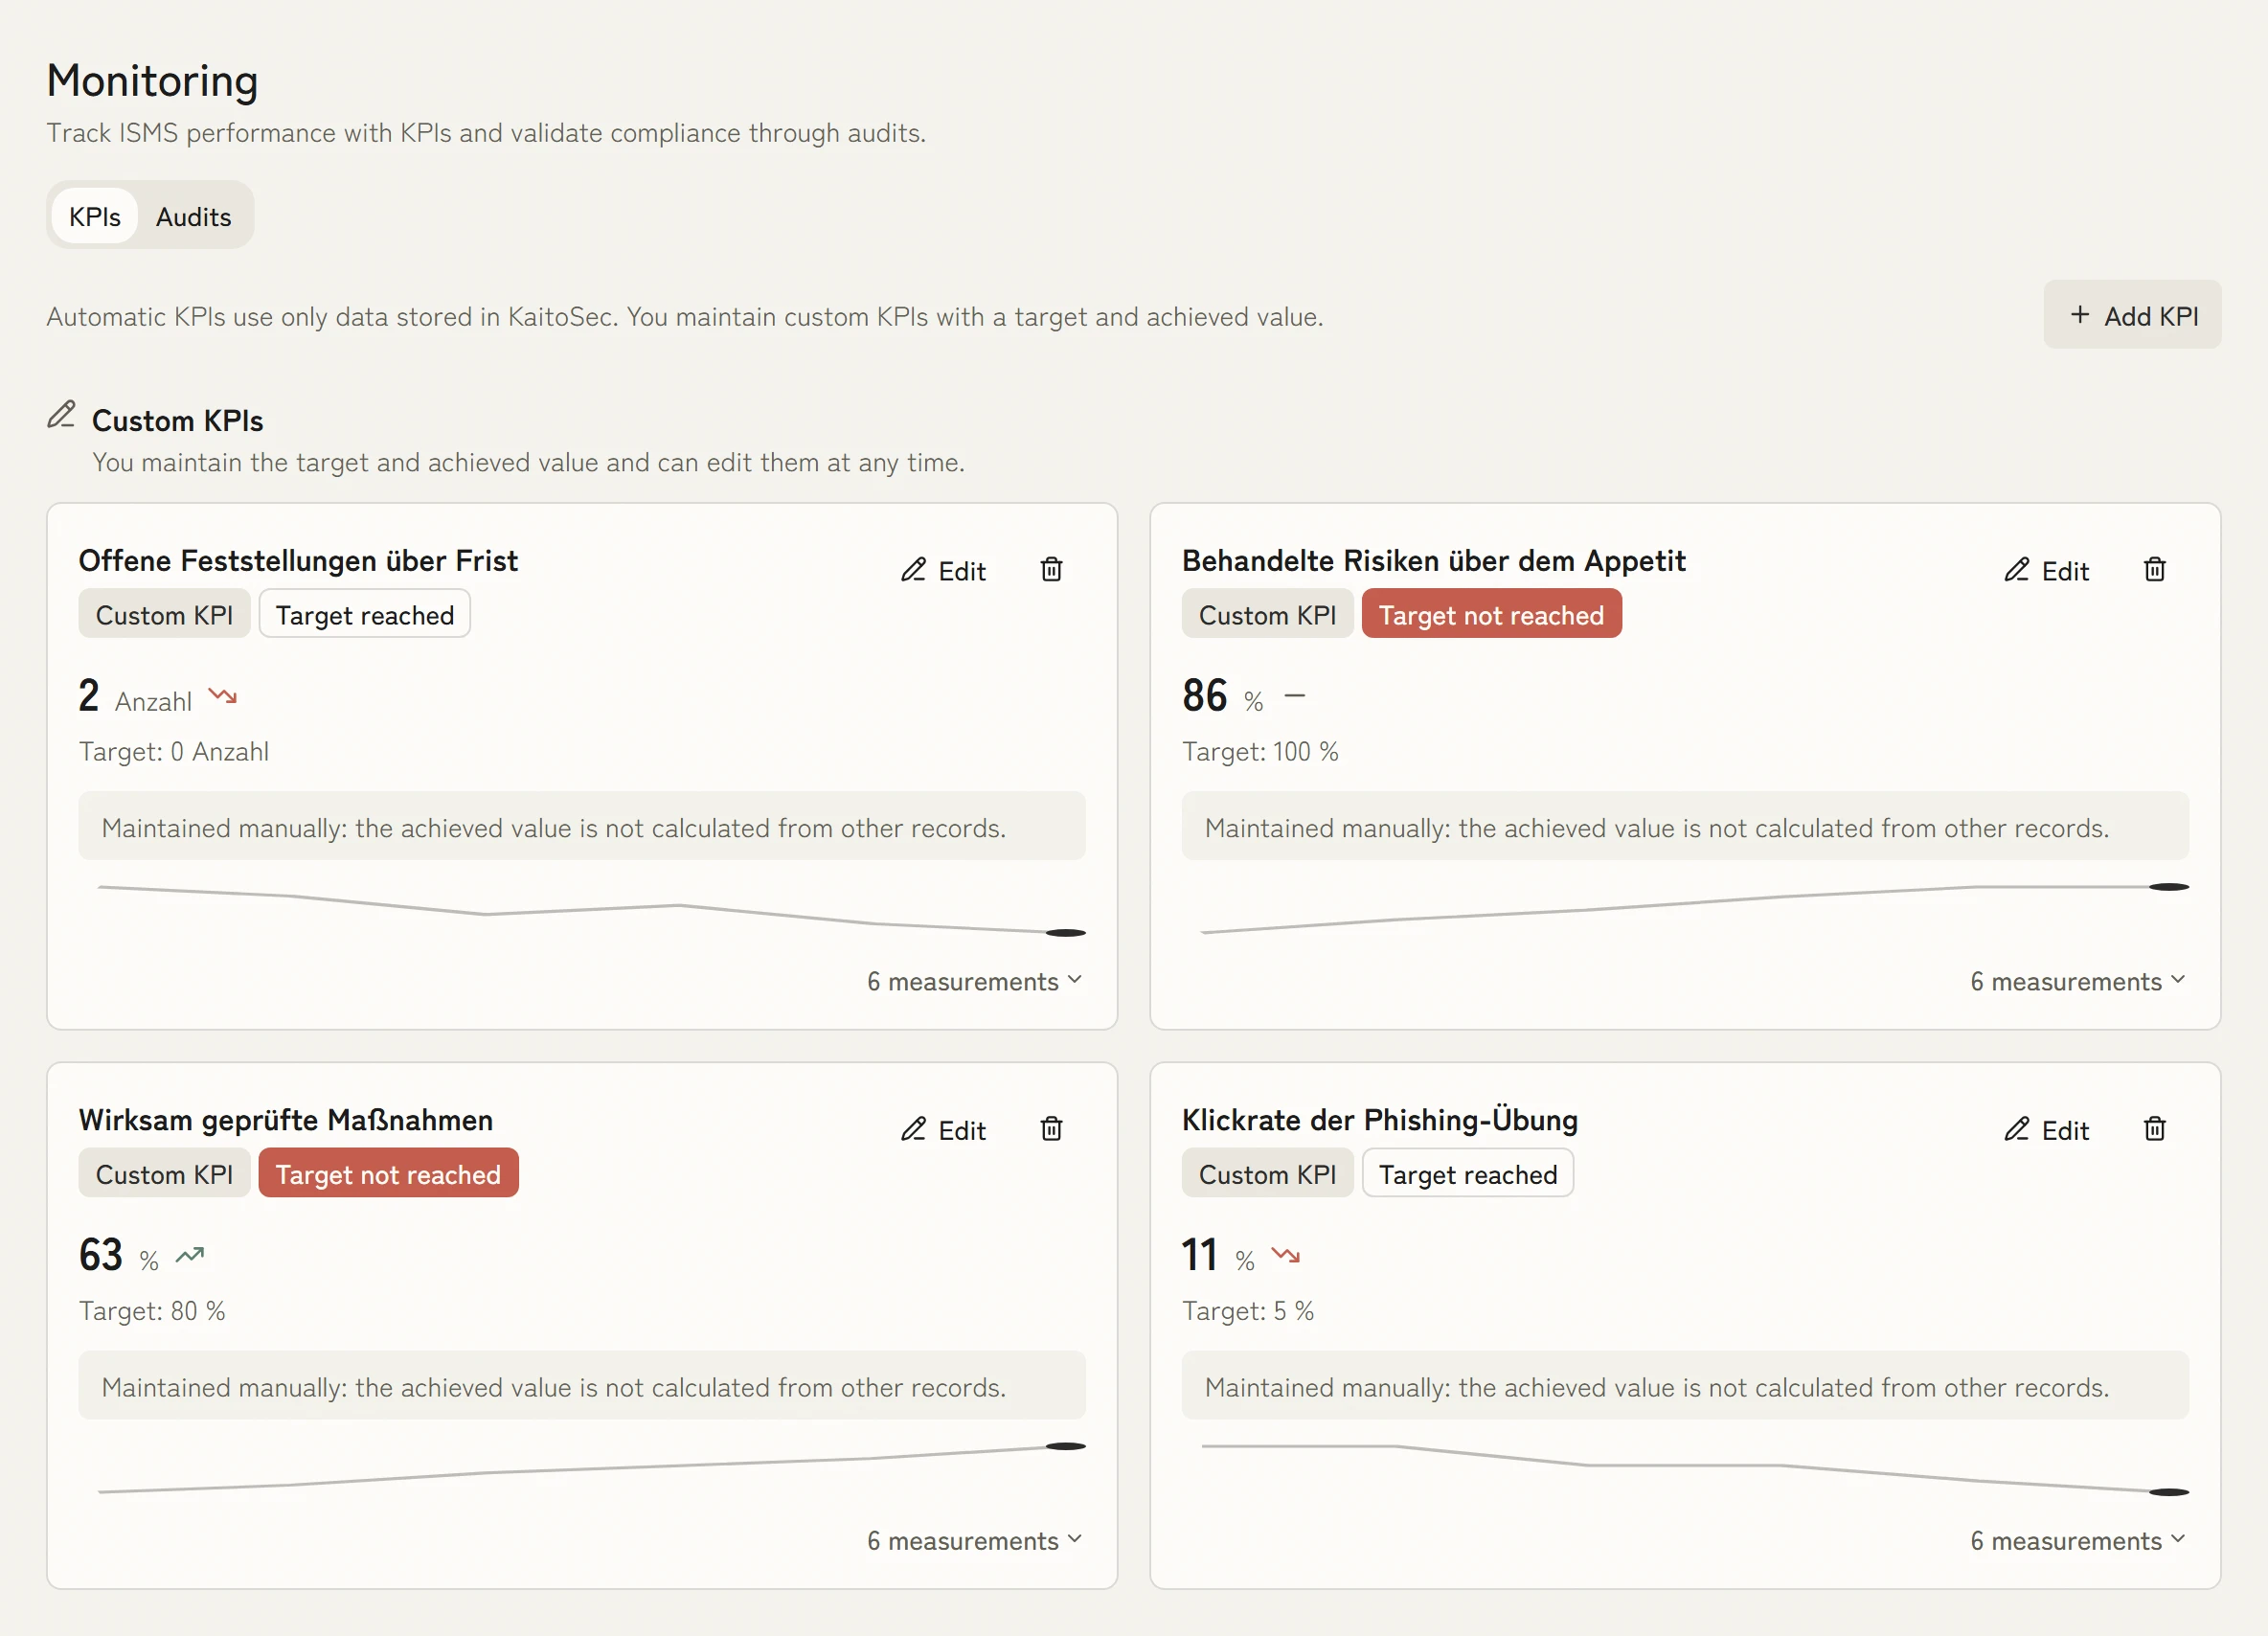
Your own metrics with a target and a history show whether a control holds across the period: findings past their due date, the click rate of the phishing exercise. That history is precisely what a Type II report wants to see.
The cycle the evidence comes out of
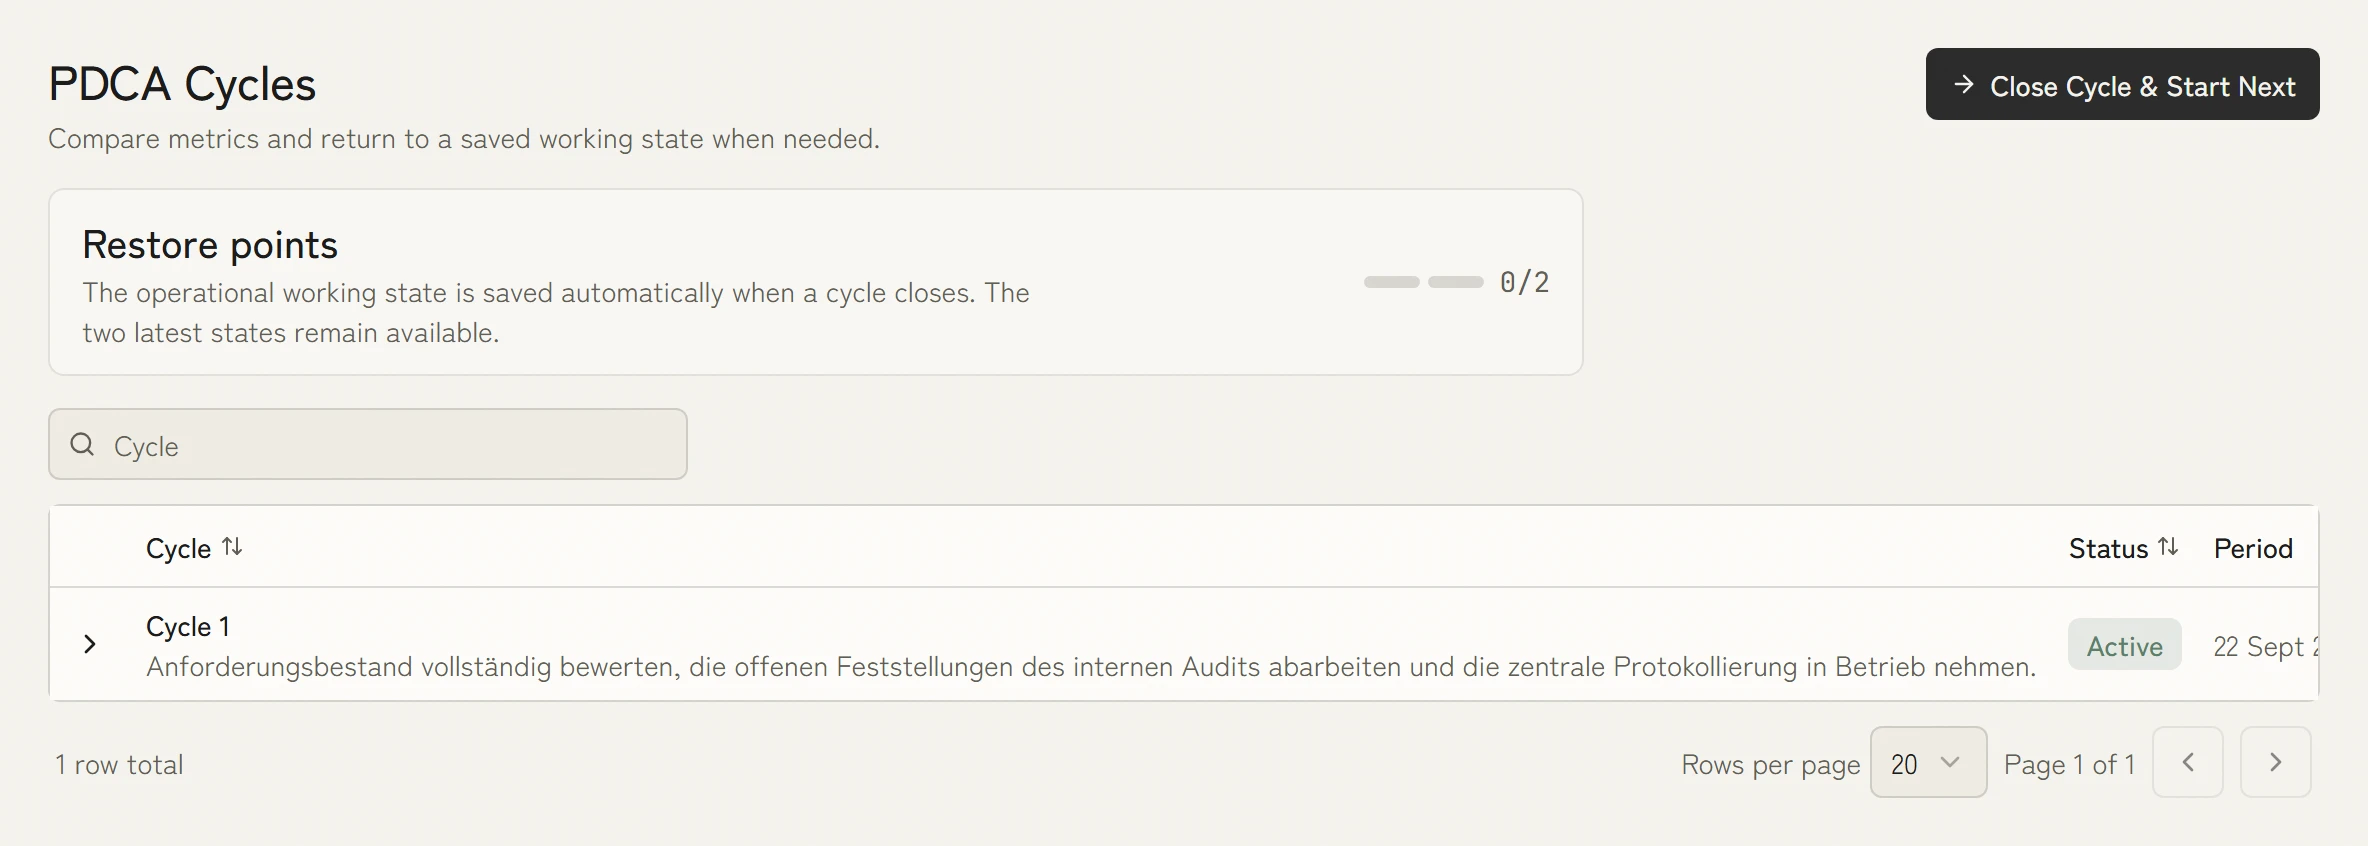
A PDCA cycle holds its objective, its period and its readiness, and saves the state when it closes. Comparing two cycles shows what actually changed between two reports.
SOC 2 and ISO 27001 from one control library
The Trust Services Criteria and Annex A ask for much the same thing. KaitoSec keeps the control once and shows it to both regimes, with its own mapping and without duplicating the evidence.
1 libraryShared controls feed SOC 2 and ISO 27001 from one workspace
Connect SOC 2 with other standards
Put the SOC 2 work to use for the standards that examine the same controls.
SOC 2 by company and role
More for SOC 2
Evidence tied to the relevant period
SOC 2 Type II considers control effectiveness over a period. KaitoSec connects relevant signals from cloud, identity and developer systems to the corresponding control; your team reviews and approves the evidence.
Type I and Type II readiness
A Type I report confirms your controls are suitably designed at a point in time. A Type II report covers operating effectiveness over an observation period. KaitoSec supports both, with a clear pathway from your first Type I to ongoing Type II readiness.
Controlled sharing with customers
Provide approved SOC 2 reports, security policies and subprocessors under controlled access. Sales and security then work from the same reviewed state.
Map controls to the Trust Services Criteria
Map your existing controls to all five Trust Services Criteria: Security (CC), Availability (A), Processing Integrity (PI), Confidentiality (C) and Privacy (P). KaitoSec shows which criteria your auditor is examining and what evidence is required for each.
Cloud systems as reviewable evidence sources
Connect AWS, GCP, Azure, GitHub and Okta as potential evidence sources. Access reviews, encryption status and vulnerability scans are assigned to the corresponding control for professional review.
Work with your auditor in one workspace
Invite your CPA firm to a dedicated workspace where they can review evidence, raise requests, and mark controls as tested. Audit fieldwork happens inside KaitoSec, no email chains, no shared drives, no confusion about which evidence version is current.
What SOC 2 requires
SOC 2 examines a service organisation's controls against the Trust Services Criteria. Security is mandatory; availability, processing integrity, confidentiality and privacy are added depending on what you commit to. A Type I report looks at design at a point in time, a Type II report at operating effectiveness across an observation period.
Frequently asked questions about SOC 2
What is the difference between SOC 2 Type I and Type II?
A SOC 2 Type I report assesses whether your controls are suitably designed at a specific point in time. A SOC 2 Type II report tests whether those controls operated effectively over an observation period, typically 6 to 12 months. Enterprise customers almost always require Type II because it demonstrates sustained operational effectiveness, not just good intentions.
Which Trust Services Criteria do we need to include?
Security (the Common Criteria) is mandatory in every SOC 2 engagement. The remaining four, Availability, Processing Integrity, Confidentiality and Privacy, are optional and selected based on what matters to your customers. Most SaaS companies include Security and Availability as a minimum.
How long does it take to get a SOC 2 report?
Duration depends on scope, maturity, implementation gaps, observation period and the CPA firm. KaitoSec structures controls and period-specific evidence; agree a defensible timeline with the auditor.
Do we need to hire a specialist to prepare for SOC 2?
KaitoSec provides enough built-in guidance that many engineering-led teams complete SOC 2 preparation independently. The actual audit must be performed by an independent CPA firm. KaitoSec does not replace the auditor but takes away much of the manual work that makes audits expensive.
Can SOC 2 evidence be reused for ISO 27001?
Yes. SOC 2 Trust Services Criteria and ISO 27001 Annex A controls overlap significantly. KaitoSec maintains a cross-mapping and reuses evidence across both frameworks wherever possible. Organisations frequently pursue SOC 2 first for their US customer base and ISO 27001 for European enterprise sales, using the same underlying control library. Our article Resilience Made Easy explains the idea behind it: implement once, evidence it wherever it applies.

Your SOC 2 plan in thirty minutes.
In the demo we settle the criteria, the observation period and the evidence sources. You leave knowing whether Type I or Type II is the next step.