
ISO 42001: your AI management system builds on your ISMS
AI systems sit in the same register as servers and applications, and your ISMS work counts wherever the substance matches. Impact assessments, AI risks and the mapping to the EU AI Act run in the same workspace.



 5.0 out of 5
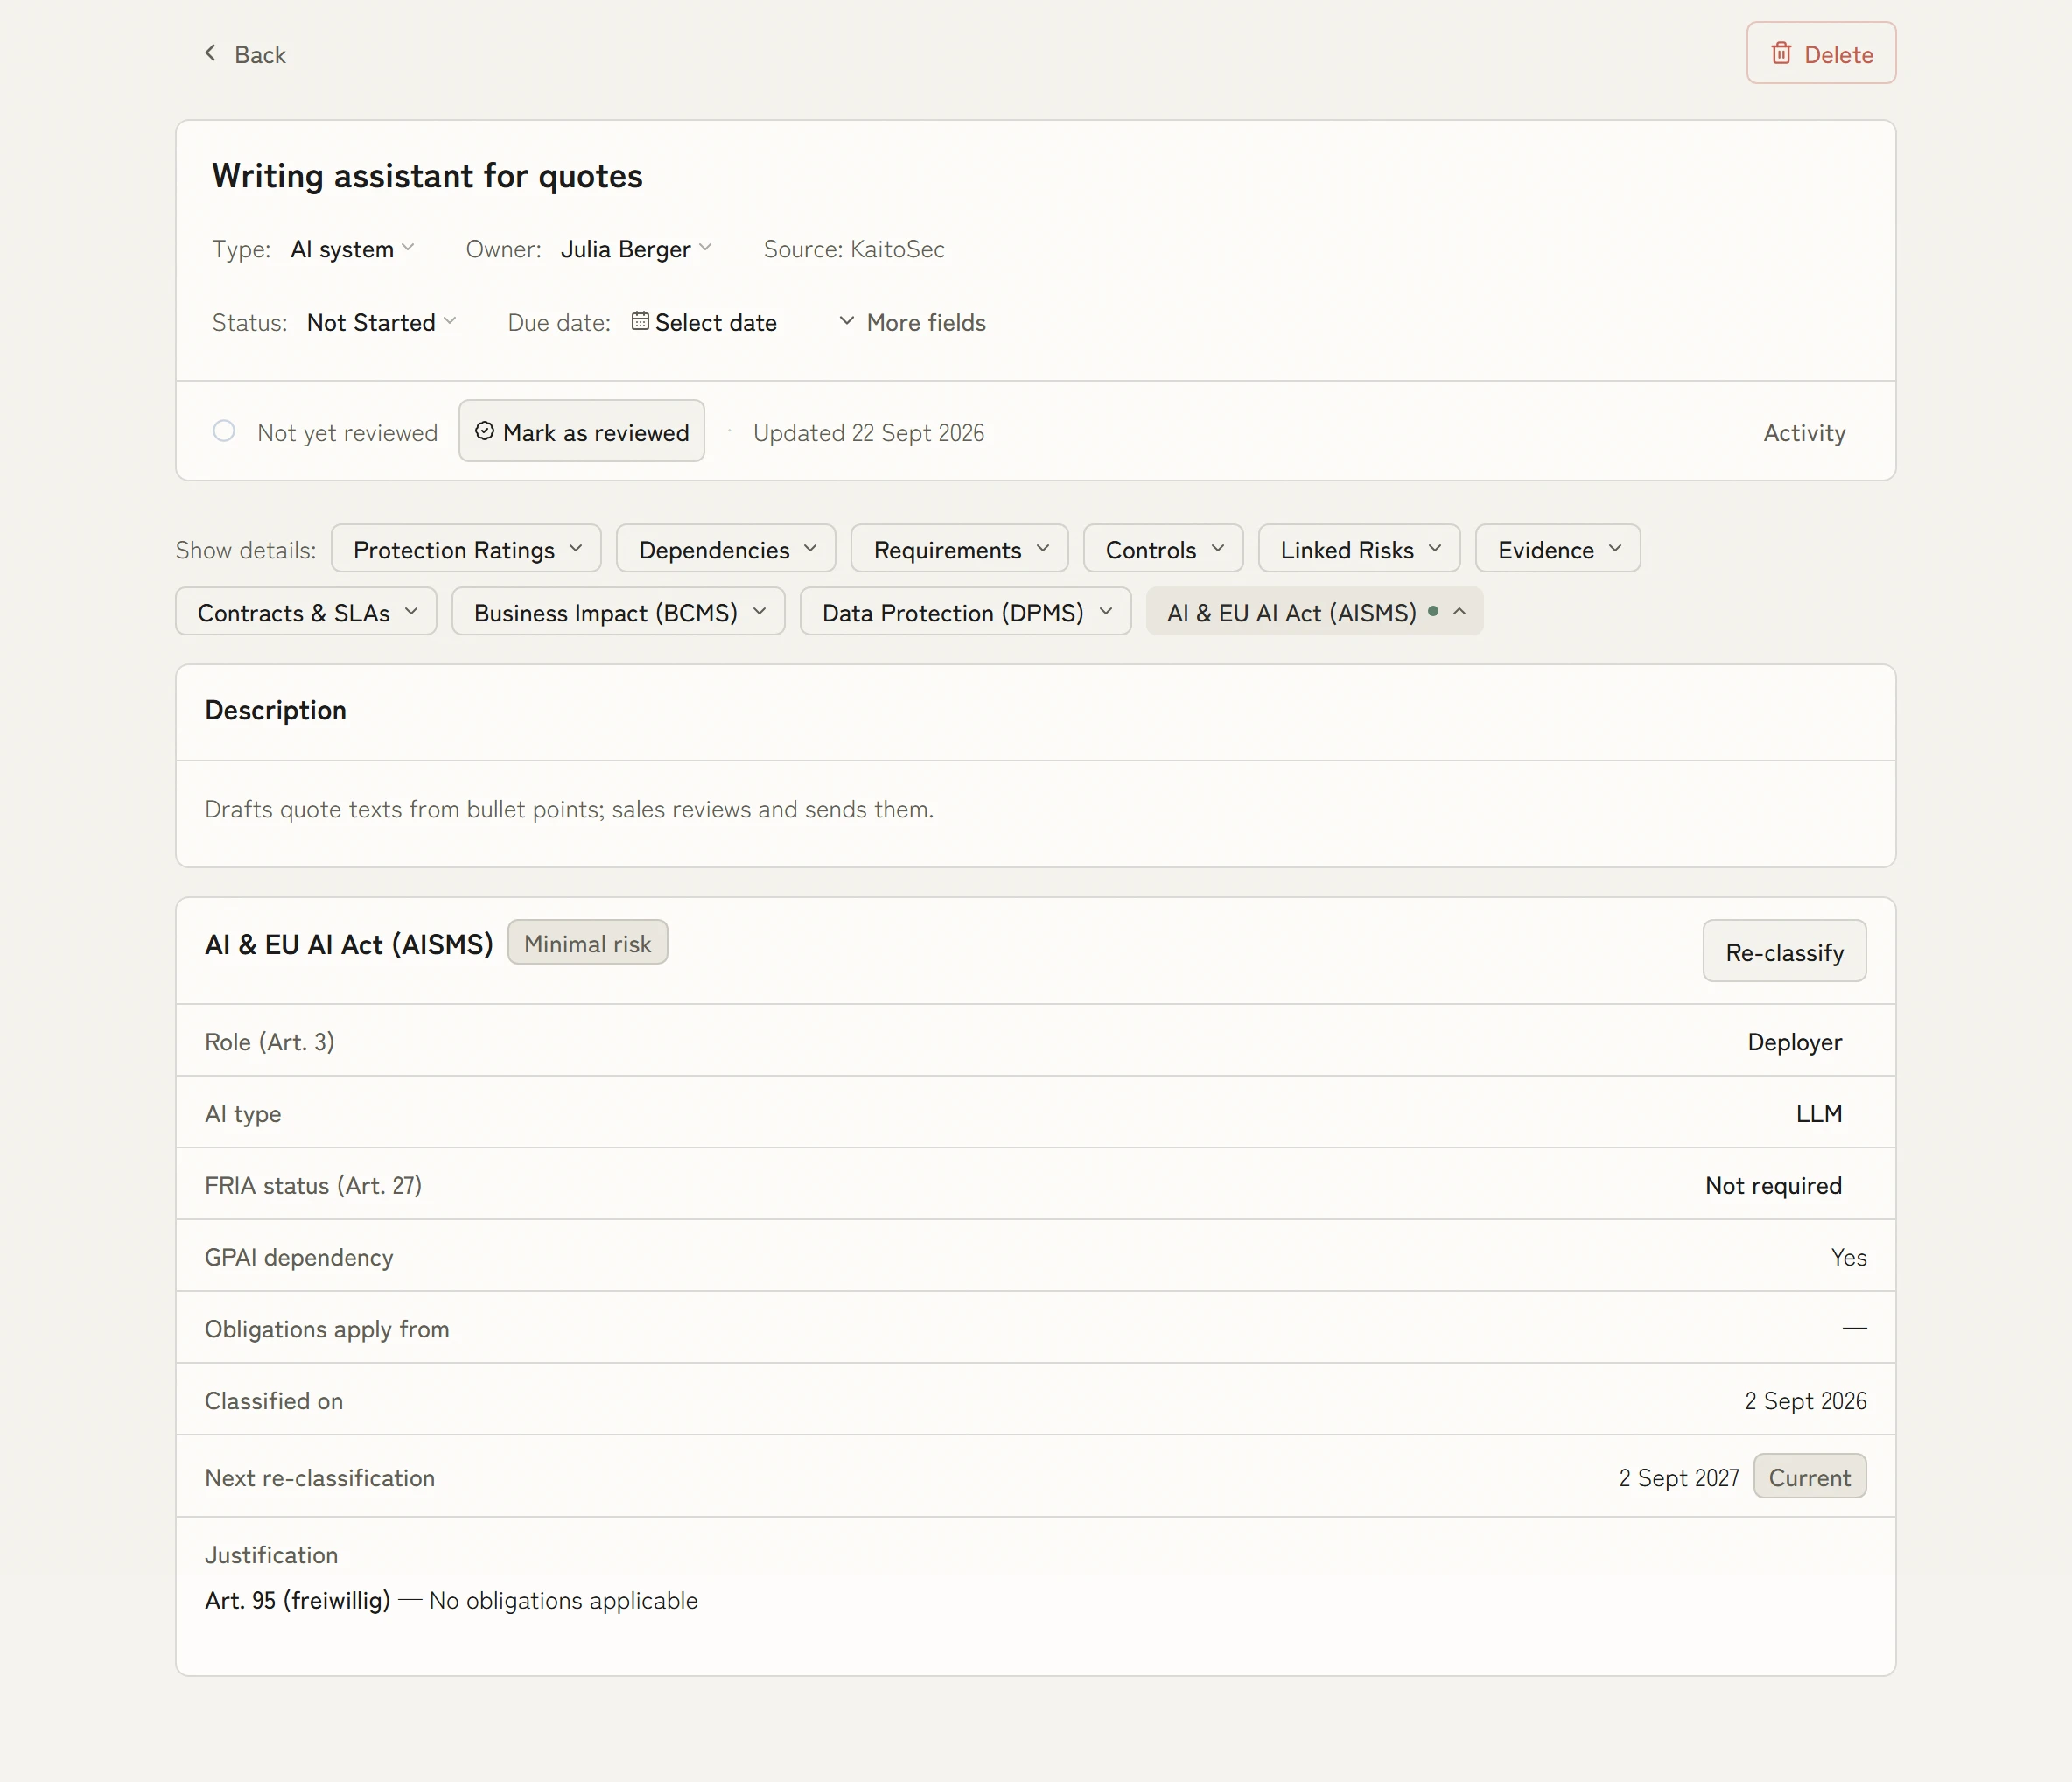
AI systems are target objects like any other
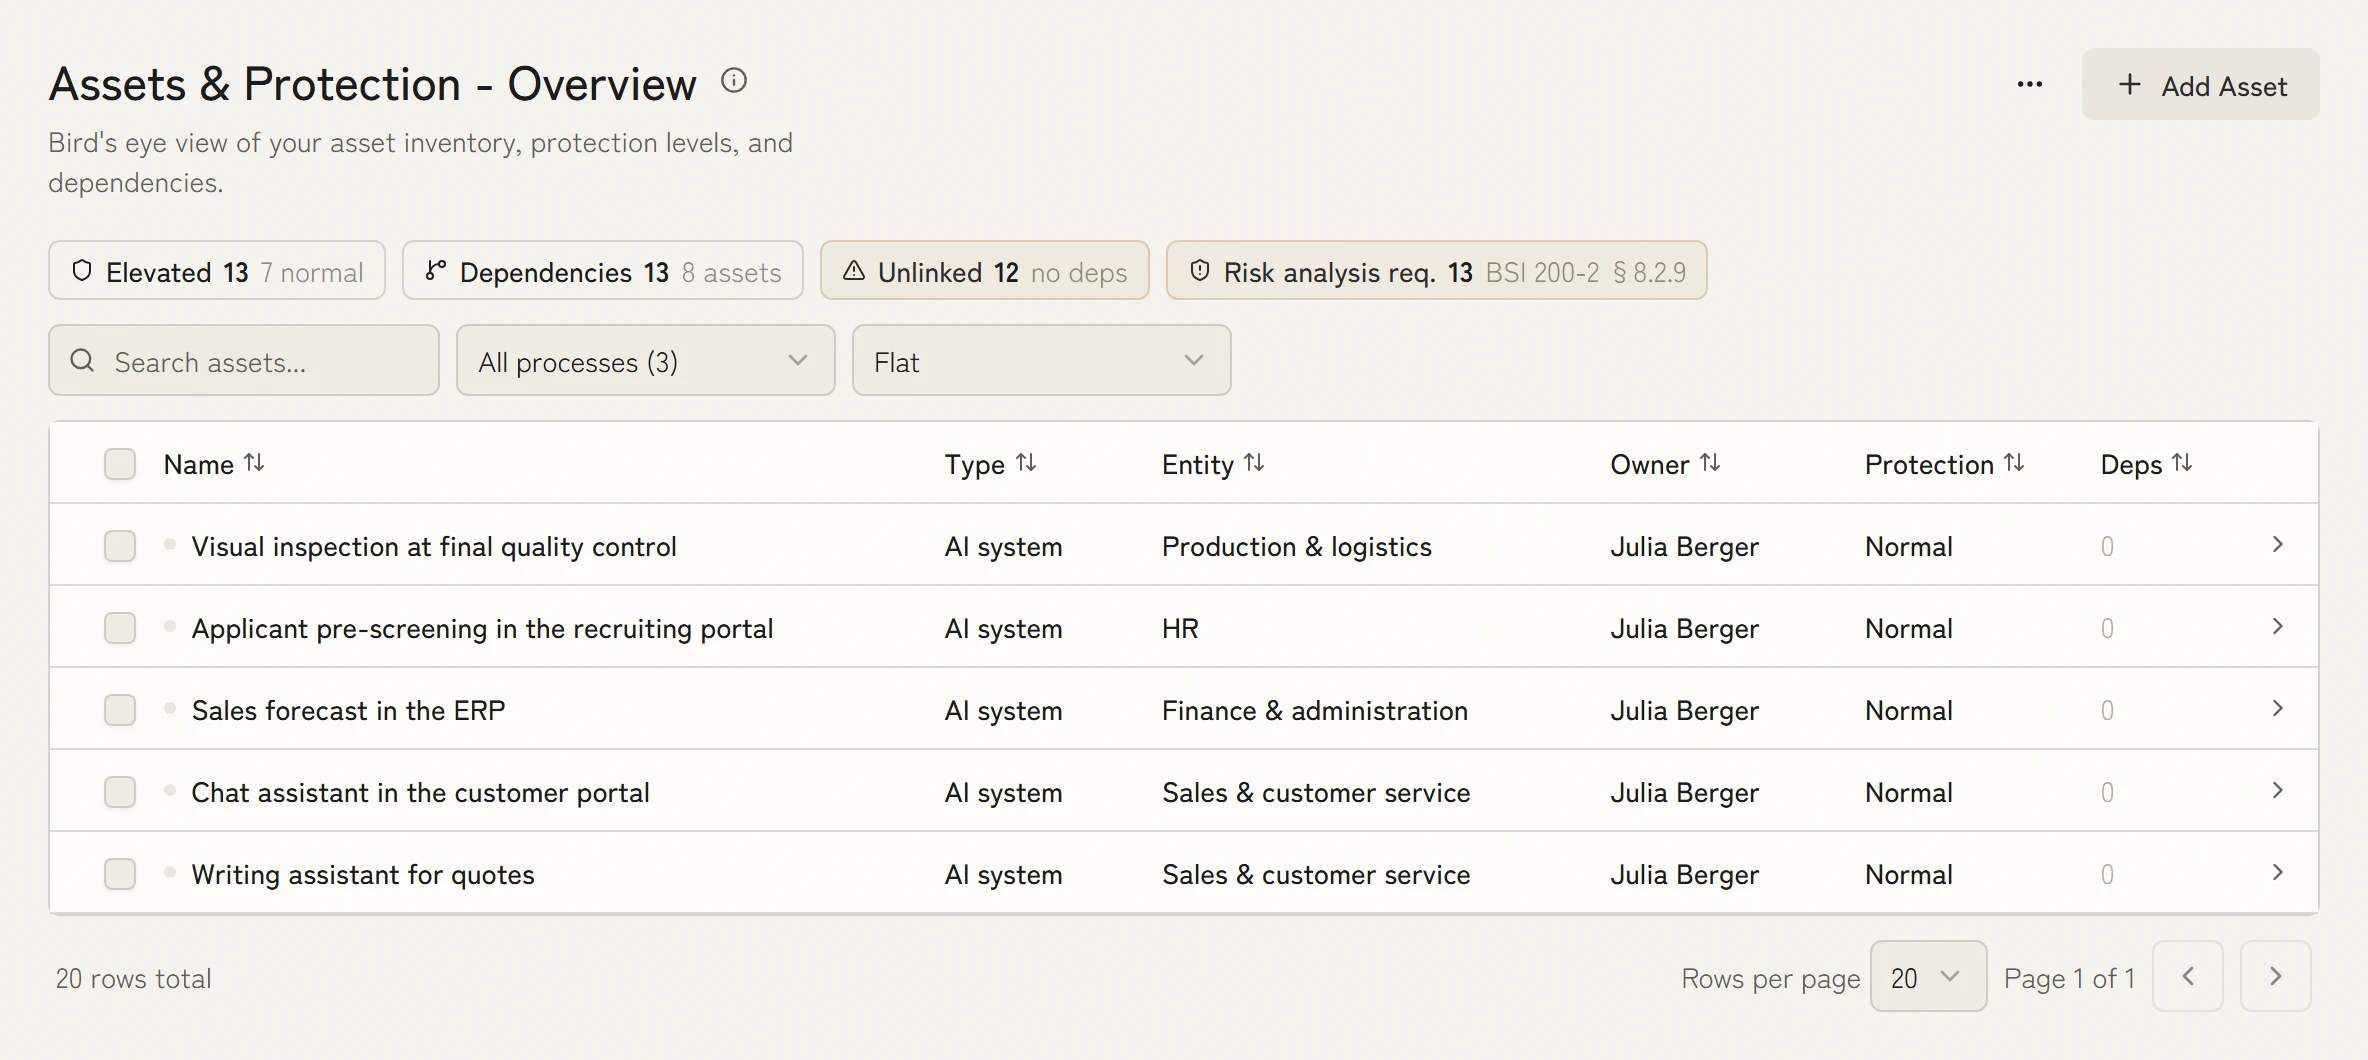
A language model sits in the same register as servers and applications, with unit, owner and protection level. Controls, requirements and risks reach it from there, with no second inventory kept for AI.
1 data modelThe AIMS shares assets, risks and evidence with ISMS, BCMS and DSMS
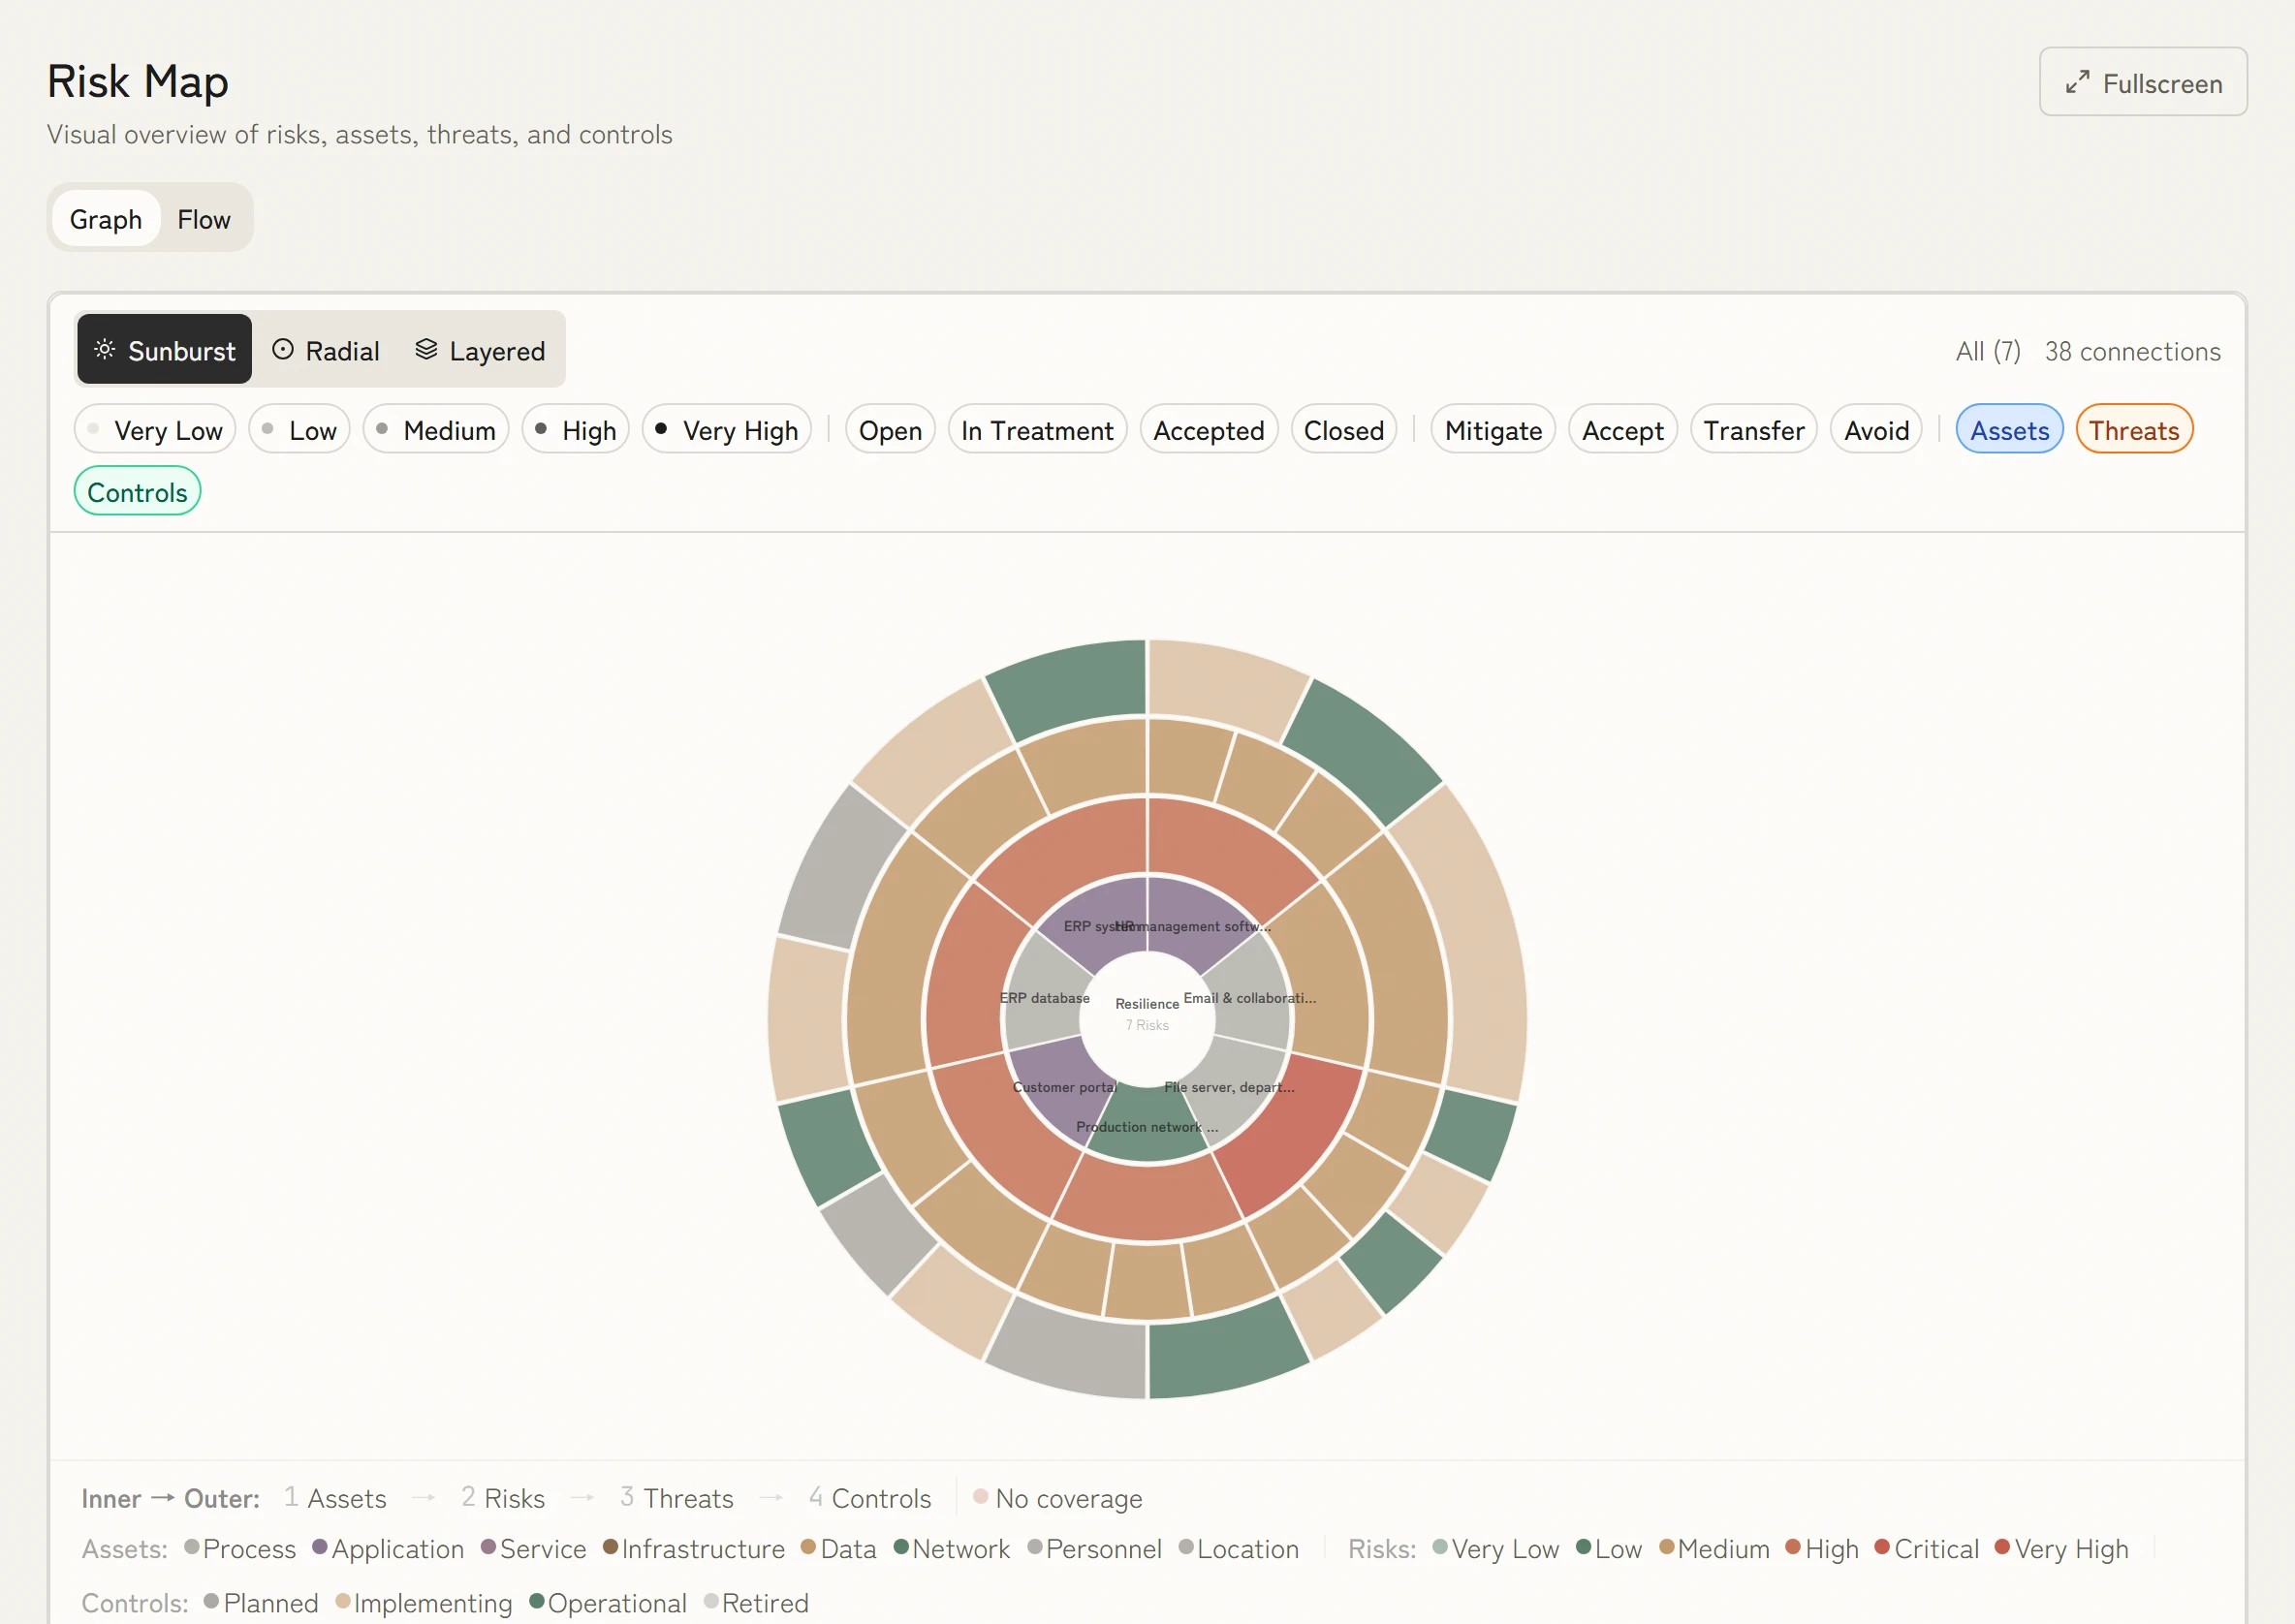
See AI risks in their context
The risk map shows target objects, risks, threats and controls as connected rings. Model drift, bias or missing explainability therefore hang on the system they affect and on the control that treats them.
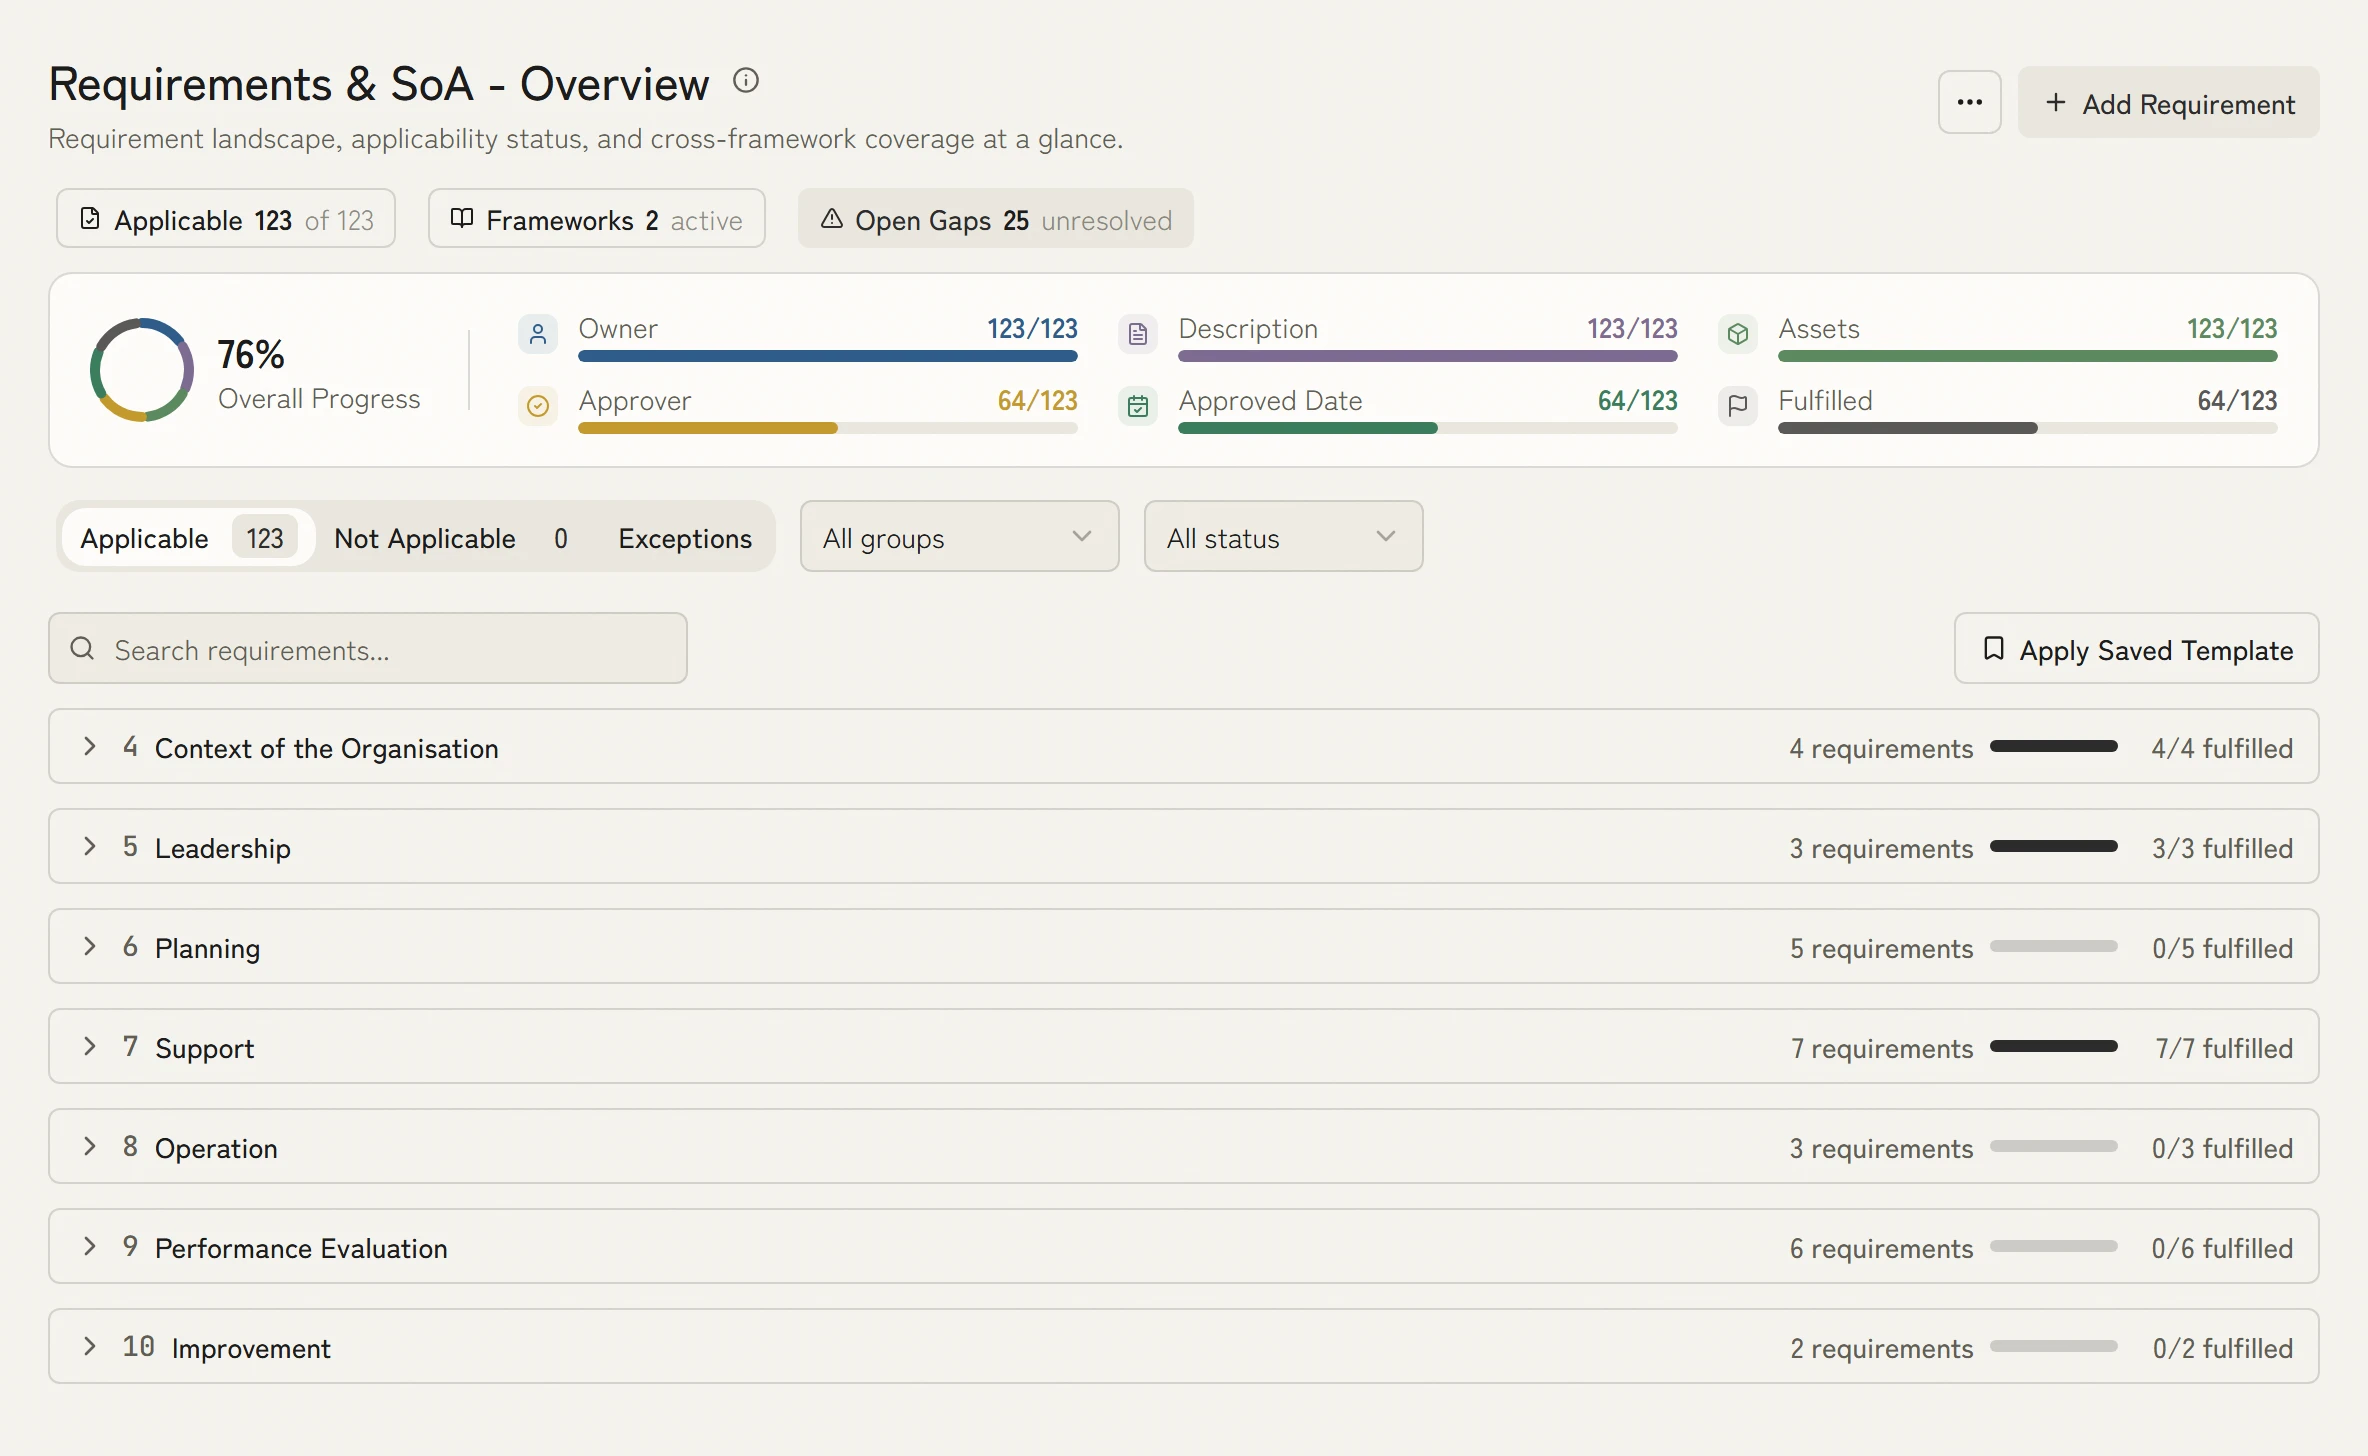
Clauses 4 to 10 with their current state
ISO 42001 follows the same structure as ISO 27001. Context, leadership, planning, support, operation, evaluation and improvement show their state side by side, and the ISMS work counts wherever the substance overlaps.
ISO 42001 alongside ISO 27001 and the EU AI Act
The AIMS shares assets, risks and evidence with the ISMS, the BCMS and the DSMS. Where a control serves several frameworks, KaitoSec shows that instead of keeping it three times.
1 AIMSLifecycle, impact, risk and audit on one management system
Connect ISO 42001 with other standards
Connect the AIMS with the management systems already running.
ISO 42001 by company and role
More for ISO 42001
AI lifecycle management
ISO 42001 requires organisations to govern AI systems across their full lifecycle, from design and development through deployment, monitoring, and decommissioning. KaitoSec provides lifecycle stage tracking for every AI system, with controls and documentation requirements surfaced at each stage.
AI risk management framework
The standard requires a systematic approach to identifying, assessing, and treating risks specific to AI, including model drift, bias, adversarial attacks, and explainability failures. KaitoSec's AI risk register extends your existing risk management process with AI-specific risk categories and treatment workflows.
EU AI Act pre-alignment
ISO 42001 covers many duties of the EU AI Act, such as risk and quality management, especially for high-risk systems. A presumption of conformity only arises through harmonised standards. KaitoSec maintains a mapping between ISO 42001 controls and EU AI Act obligations, so your AIMS work directly contributes to regulatory compliance.
Track implementation per clause
A central view of your ISO 42001 AIMS, covering policy documentation, AI system inventory, risk register, objectives, and audit programme. The dashboard tracks implementation maturity across all clauses of the standard and shows how close you are to certification readiness.
Run structured AI impact assessments
Control area A.5 of ISO 42001 requires assessing the impacts of AI systems; Annex B explains implementation. KaitoSec implements structured AI impact assessments covering individual, societal, and environmental impacts, linked to your AI system records and updated whenever system scope changes.
Use the overlap across frameworks
For organisations managing ISO 42001 alongside the EU AI Act, GDPR, and ISO 27001, KaitoSec's cross-framework view shows which controls and evidence items serve multiple frameworks simultaneously, minimising duplication and keeping your team focused on genuine gaps.
What ISO 42001 requires
ISO 42001 asks for a management system for artificial intelligence: context and scope, leadership and policy, objectives and planning, governance across the whole lifecycle, impact assessments for individuals and society, and evaluation, audit and improvement. Annex A supplies 38 controls in nine areas.
7clauses in the management system
- Clause 4Context
- Clause 5Leadership
- Clause 6Planning
- Clause 7Support
- Clause 8Operation
- Clause 9Evaluation
- Clause 10Improvement
Annex A · 38 controls
- 38
- controls in nine areas
Frequently asked questions about ISO 42001
What is ISO 42001 and who published it?
ISO 42001 is the international standard for Artificial Intelligence Management Systems (AIMS), published by the International Organisation for Standardization in December 2023. It provides a framework for establishing, implementing, maintaining, and continually improving AI governance within an organisation, applicable to any sector or size.
How does ISO 42001 relate to the EU AI Act?
ISO 42001 covers many duties of the EU AI Act, such as risk and quality management. A certificate alone does not establish conformity; a presumption of conformity only arises through harmonised standards. KaitoSec maintains a live mapping between ISO 42001 controls and EU AI Act requirements, so organisations building an AIMS are simultaneously making progress on regulatory compliance. Our article Resilience Made Easy explains the cross-framework mapping behind it.
Can we certify to ISO 42001 like we can with ISO 27001?
Yes. ISO 42001 is an auditable management system standard with the same high-level structure as ISO 27001, ISO 9001, and ISO 14001. Third-party certification bodies can perform audits against ISO 42001 and issue certificates. KaitoSec prepares your documentation and evidence to the level required by accredited certification bodies.
What is the difference between ISO 42001 and ISO 27001 for AI?
ISO 27001 covers information security management broadly and includes controls relevant to AI systems as assets. ISO 42001 is AI-specific and covers AI lifecycle management, impact assessment, responsible AI practices, and AI-specific risk categories that are outside the scope of ISO 27001. KaitoSec supports both standards and cross-maps overlapping controls.
What do AI Impact Assessments under ISO 42001 cover?
Impact assessment is anchored in Annex A of ISO 42001 as control area A.5; Annex B explains implementation, including impacts on individuals (such as bias and discrimination), society (such as displacement of jobs), and the environment (such as energy consumption). KaitoSec's impact assessment templates follow this structure and require documented decisions on each impact category for every AI system in scope.

Your AIMS plan in thirty minutes.
In the demo we walk through the inventory, impact assessment and Annex A. You leave knowing how much of your ISMS already counts for the AIMS.