
Asset Management: one inventory instead of four lists.
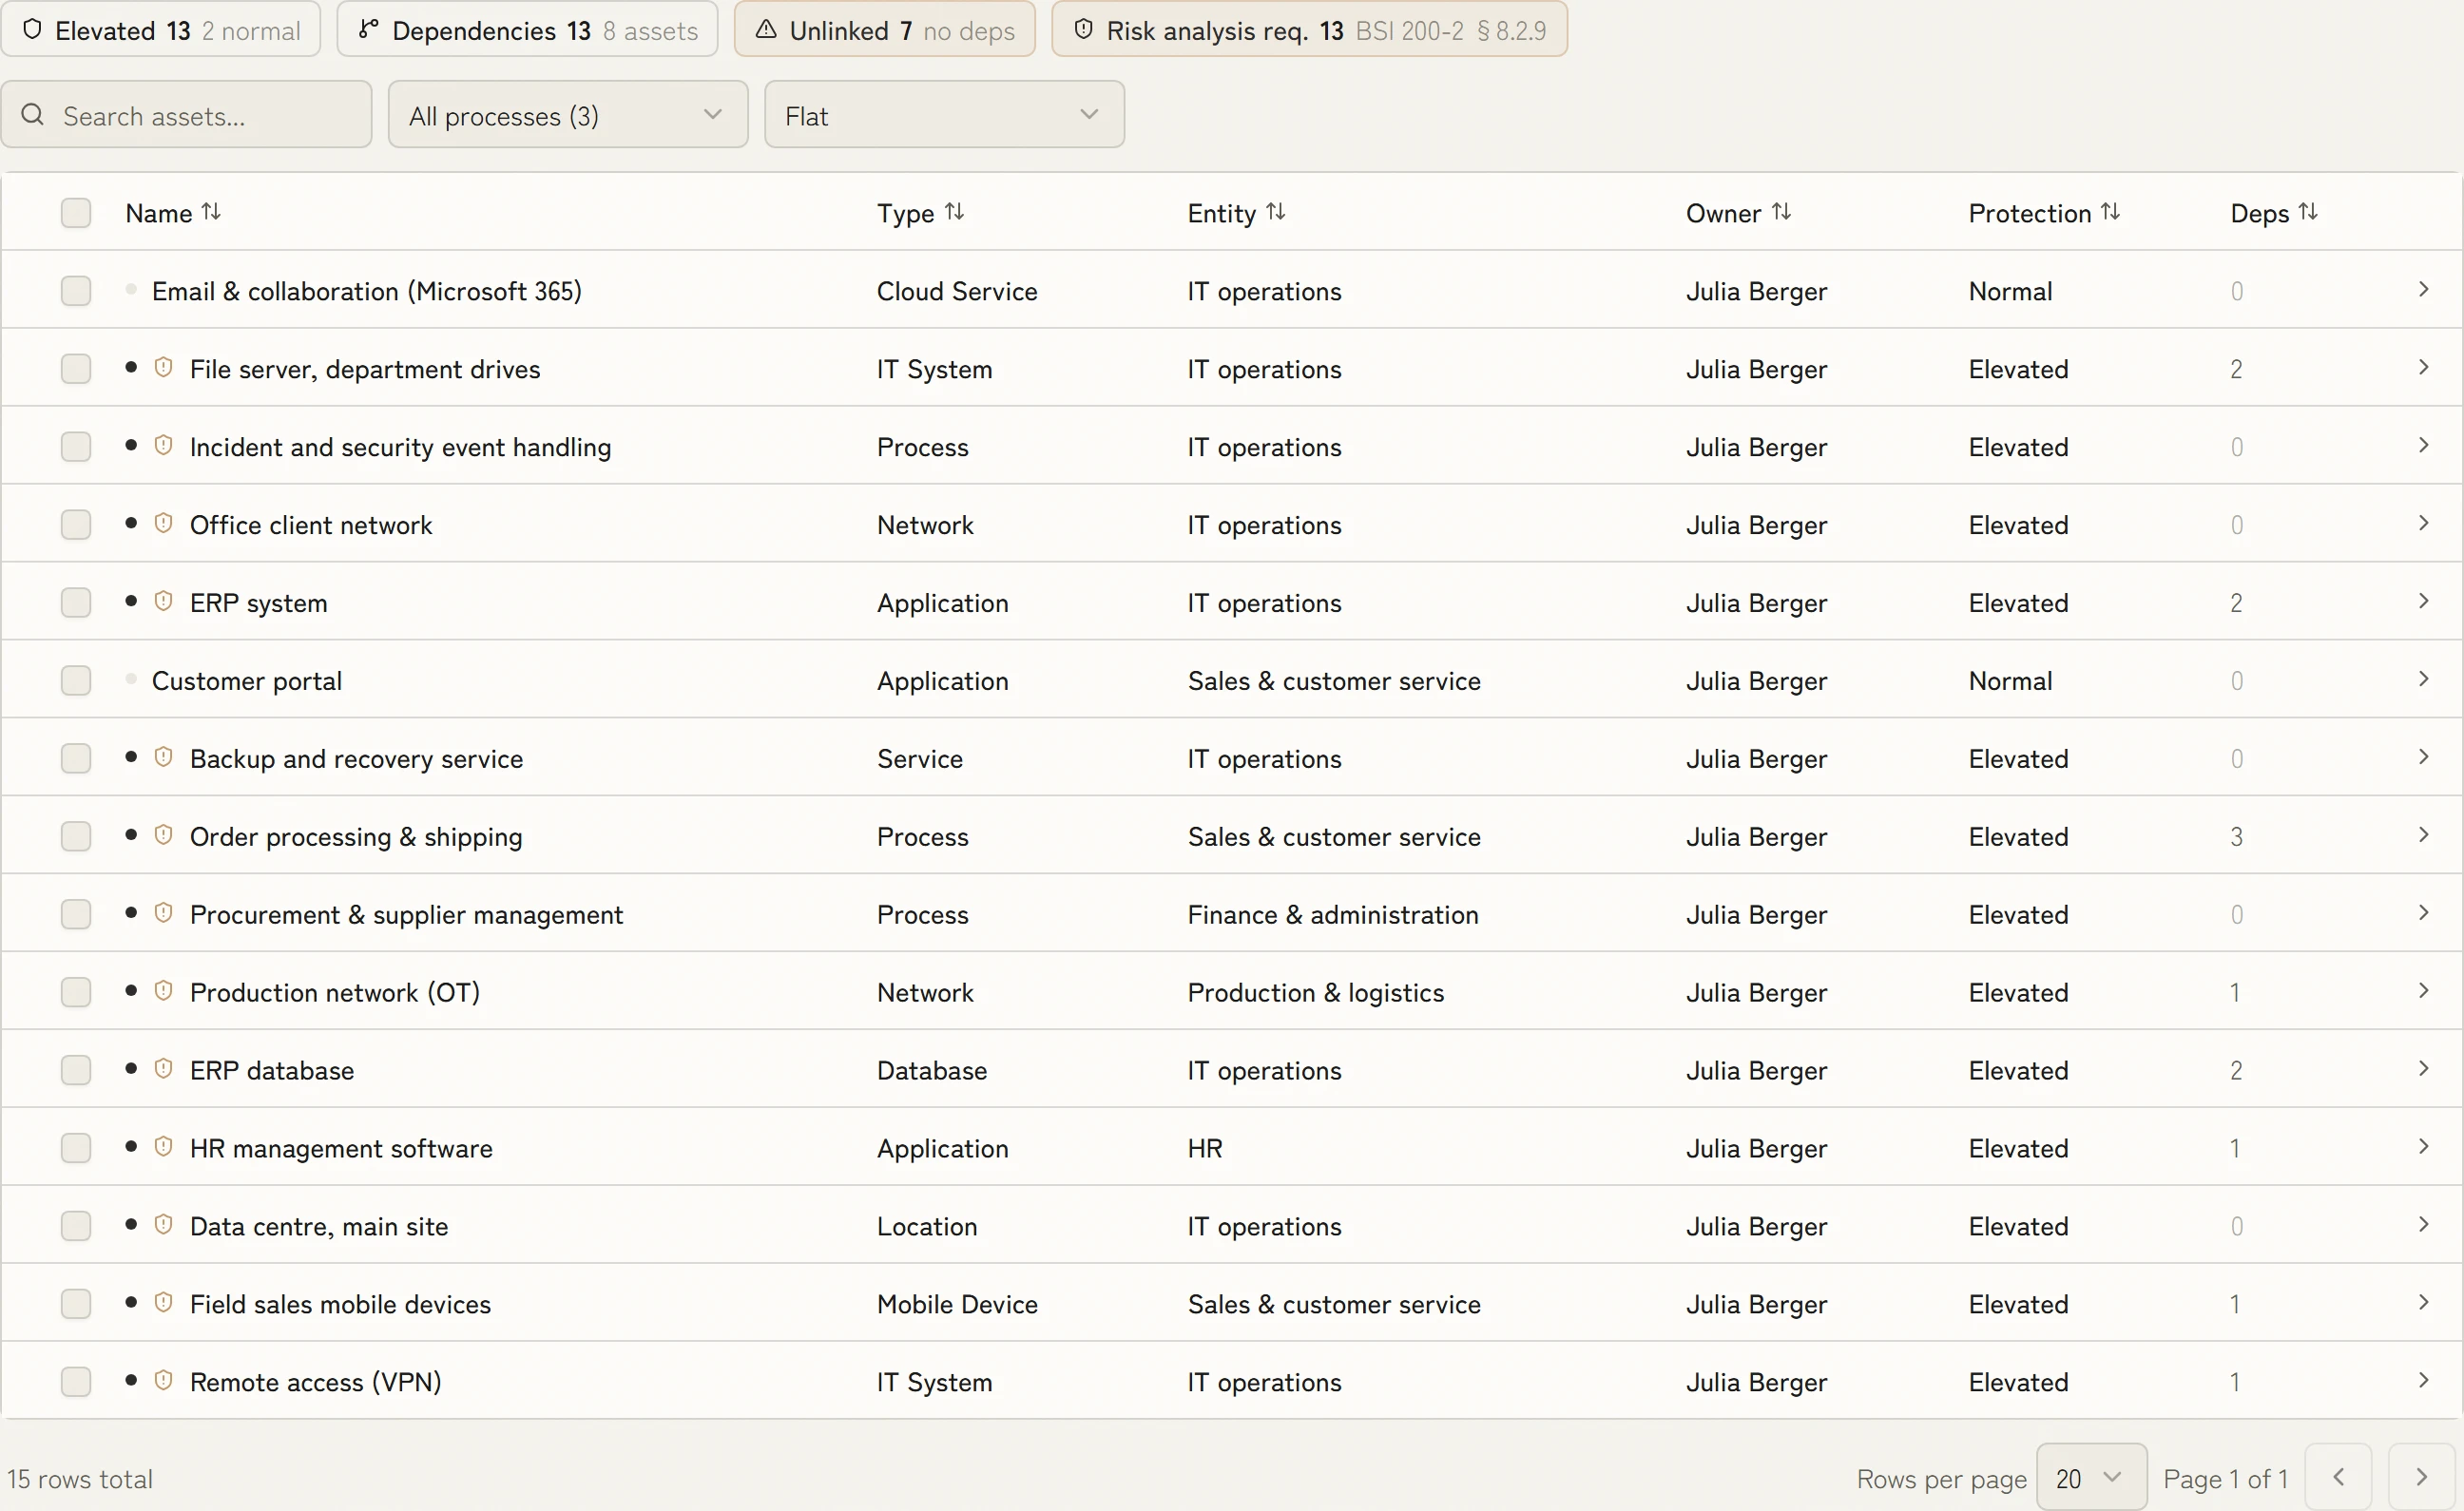
KaitoSec takes over your inventory from existing lists and connected systems. IT, security, privacy and business continuity work from the same inventory, and nobody keeps a second list for the audit.



 5.0 out of 5
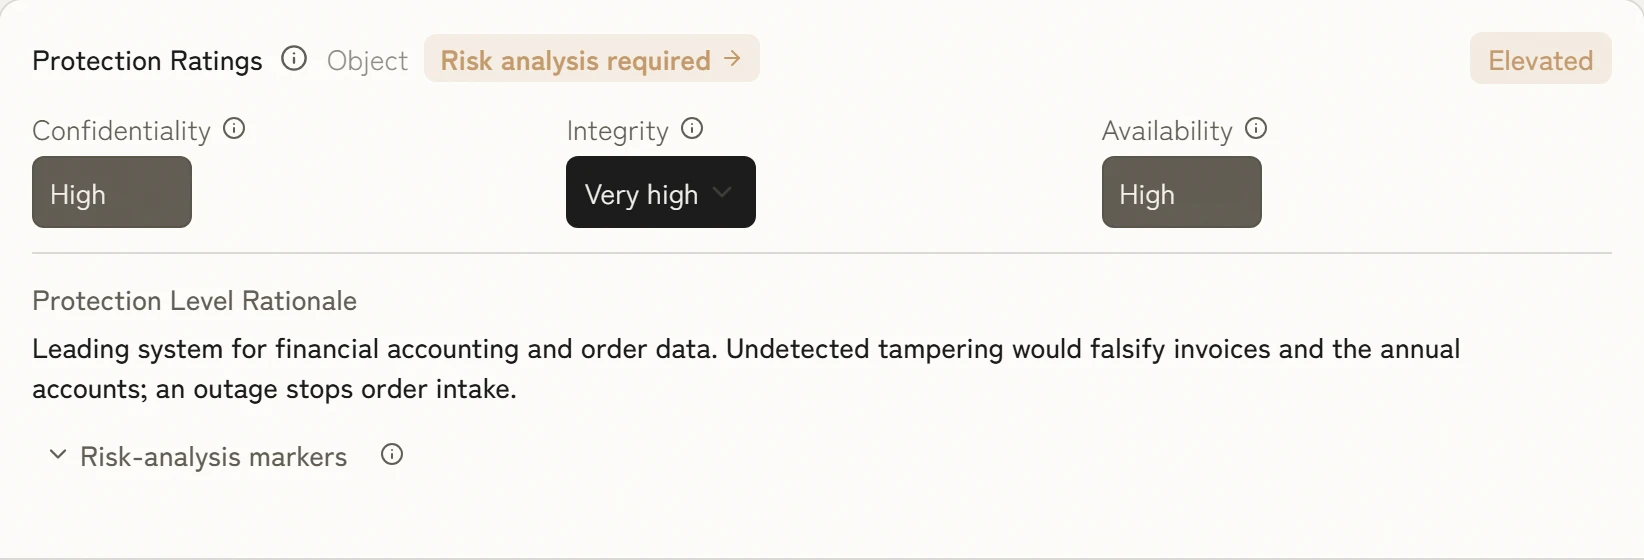
Set protection needs once, use them everywhere
You assess confidentiality, integrity and availability under ISO 27001 or BSI IT-Grundschutz, with a rationale. Risk analysis, business continuity and privacy work from the same classification instead of collecting it again.
Book a demo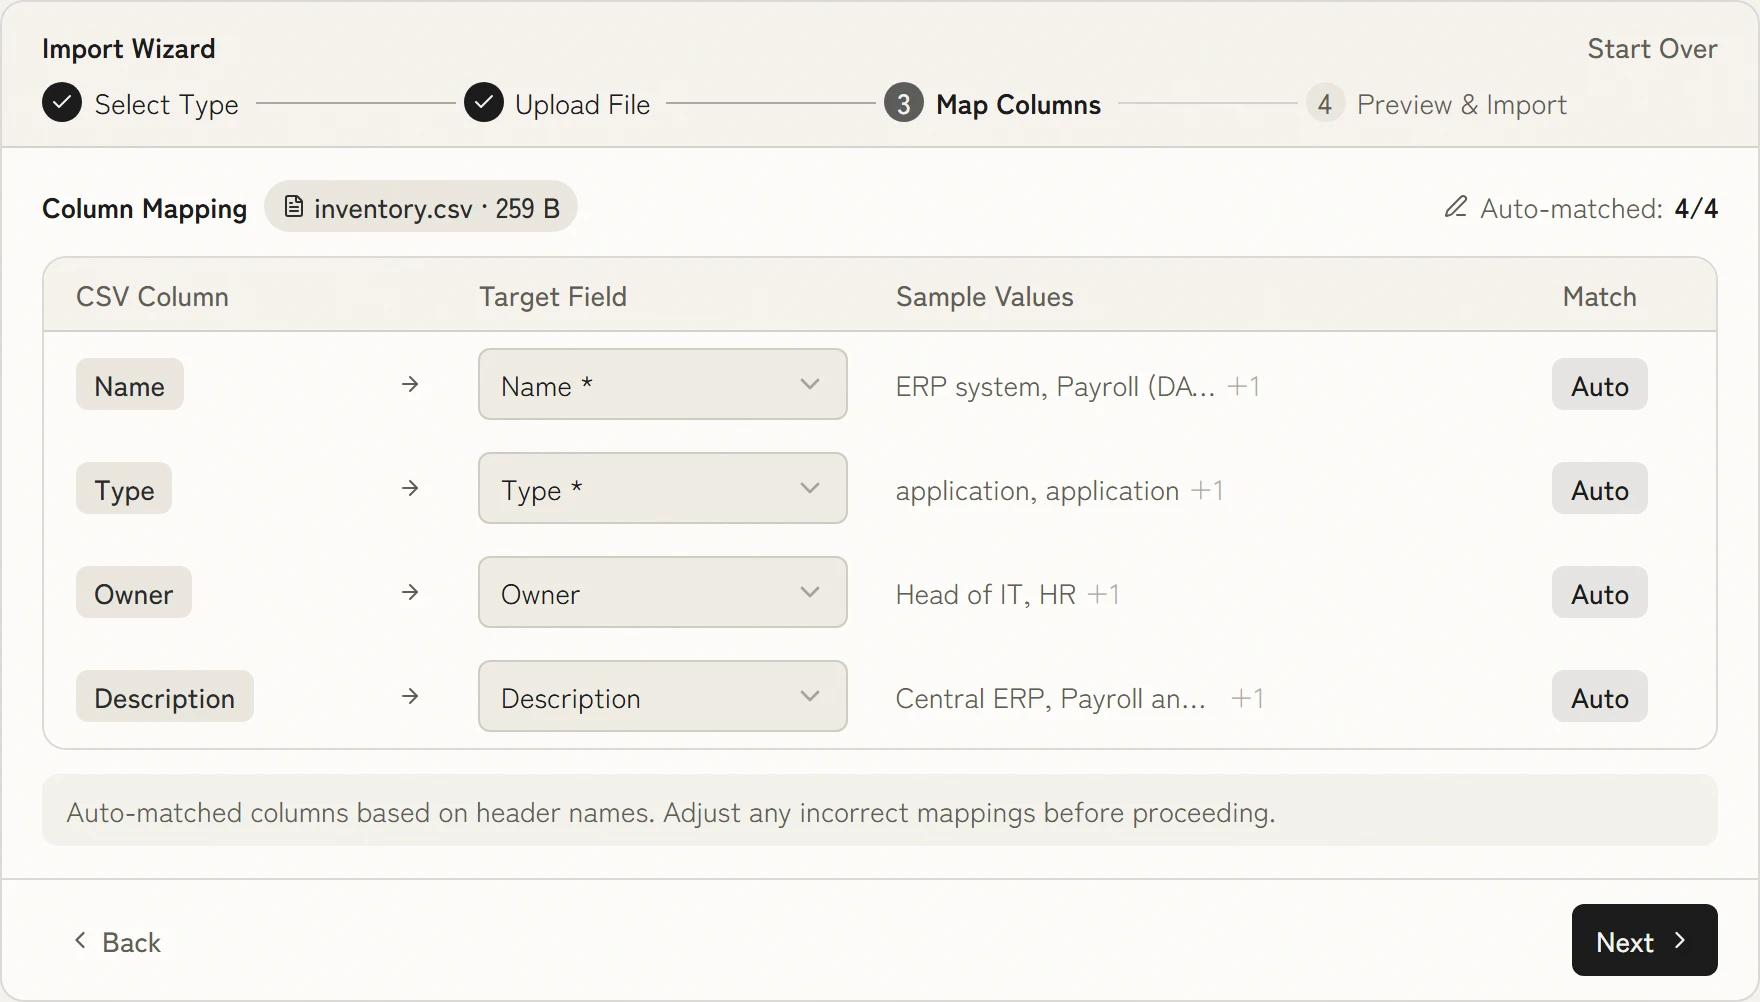
Import existing lists instead of retyping them
You upload your CSV file and KaitoSec maps the columns to the inventory fields automatically. You check duplicates, owners and classification before the data goes into the inventory.
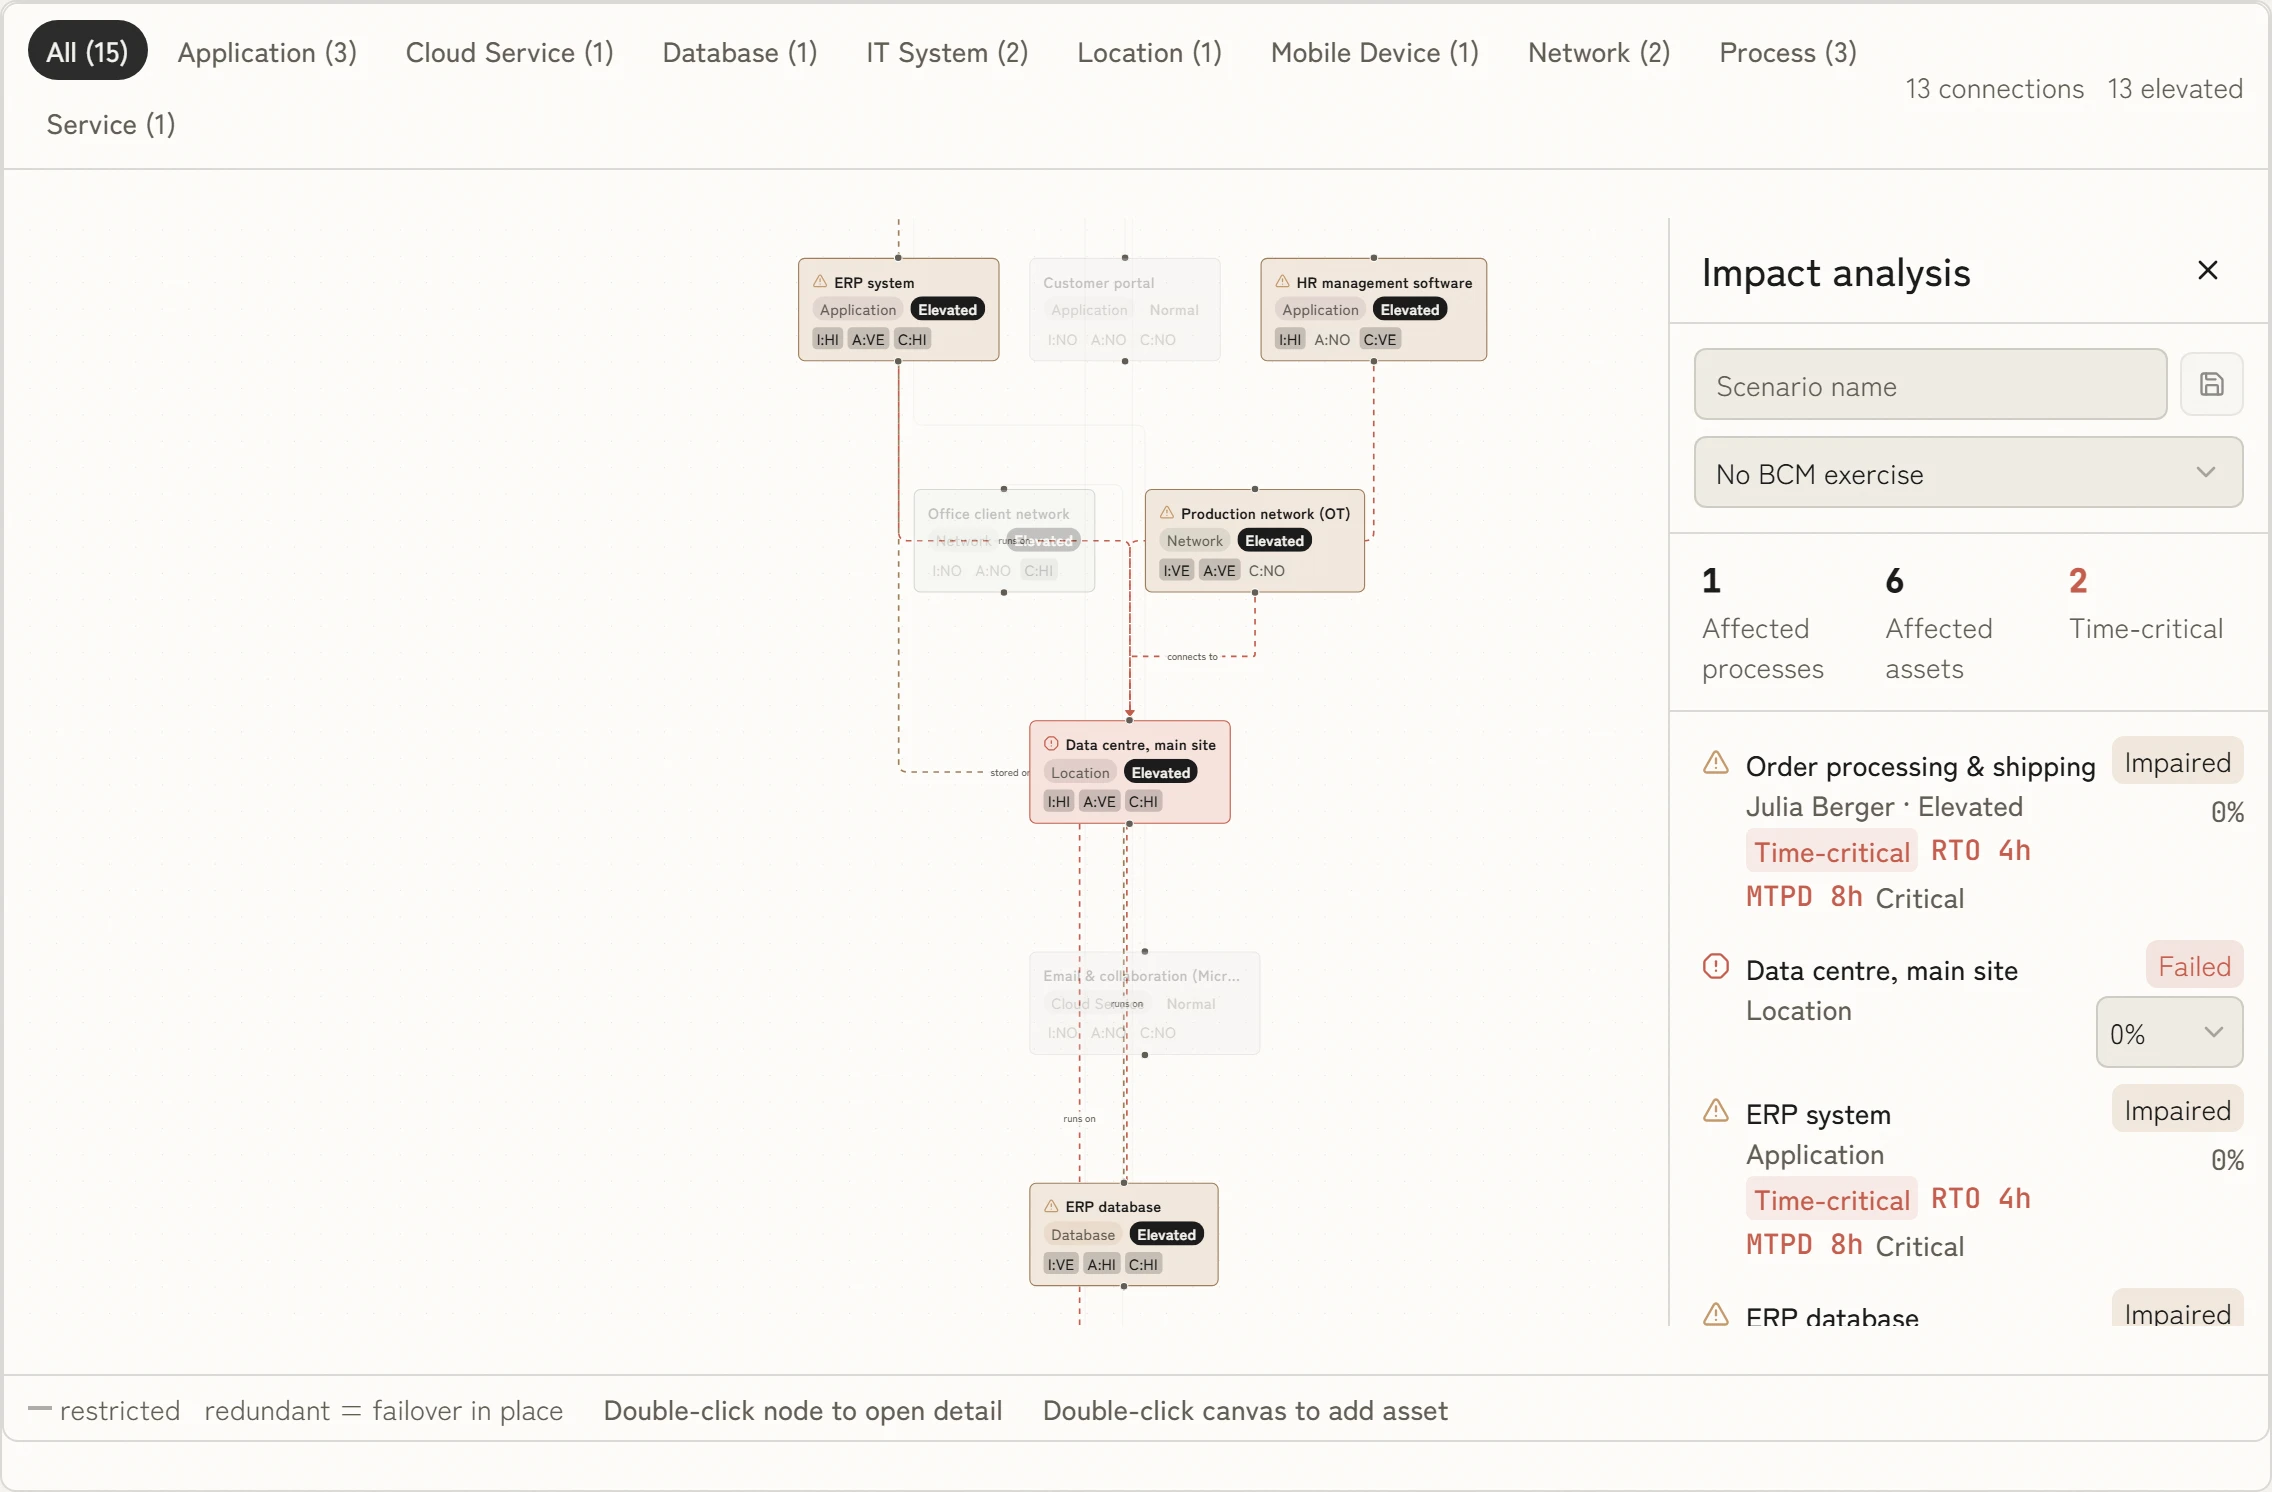
Book a demoSee what goes down when a system goes down
The asset map shows which systems and processes depend on an asset. If the data centre fails, KaitoSec marks everything affected and shows recovery times right next to it.
- pre-mapped controls
- 100+100+
- of evidence created as the work is done
- 100 %100 %
- faster than manual work
- 10×10×
- management systems, one data model
- 4 in 14 in 1
What KaitoSec also does
These sit in the core of the platform and apply to every module.
Implemented once, done for every requirement.
More than 100 controls are already mapped to ISO 27001, NIS2, DORA and other requirements. You implement a control once and evidence it once. Every further requirement it covers costs no extra work.
You review and approve instead of filling empty fields.
Agents prepare the risk analysis, the statement of applicability and actions from audit reports. Every result is ready for approval. A person still makes the decision.
Nothing left to collect before the audit.
Evidence is created as the work gets done: a tested backup supplies its recovery time, a completed review its result. Your evidence is current every day, not just in the week before the audit.
Asset inventory without prior knowledge.
In simple mode your team goes through a pre-filled list, ticks what belongs and decides for each asset whether it needs normal or elevated protection. Anyone who needs more detail switches to expert mode and sees the same assets with dependencies and protection goals.
You maintain each process only once.
Information security, business continuity management, data protection, AI governance and supplier management all work from the same process data. Every change takes effect in every system at once. Duplicate entry and conflicting registers go away.

Ask Chris how this would work for you.
Co-founder and CEO of KaitoSec. He walks through your case with you, live in the product.
Book a demo
The data for your asset management is already there.
100+ integrations
All integrations















FAQ
What types of assets can KaitoSec track?
Hardware (servers, endpoints, network), software (on-premises and SaaS), cloud infrastructure (IaaS, PaaS), data stores, AI systems and models, plus organisational assets such as processes, services and locations. Custom asset types extend the model where you need them.
How does the record of processing activities work?
Processing activities live in the same register as the IT assets that perform them. Each activity carries data categories, legal basis, recipients and responsible team, and is linked to the underlying systems and vendors. Changes to an asset surface on the activities it feeds, so the RoPA never drifts.
Can we import an existing asset spreadsheet?
Yes. A CSV import with field mapping brings in the existing inventory. You then review owners, classification and links to risks, controls and continuity dependencies.
How does asset management support BSI Grundschutz?
The asset register maps directly to BSI IT-Grundschutz target-system modelling. Grundschutz modules can be assigned to asset groups and the required documentation is generated from the model, with the same data feeding ISO 27001 mapping where both frameworks are in scope.

Less work in your asset management.
One system from your inventory is enough. In thirty minutes you see how KaitoSec classifies it, gives it an owner and links it to processes and vendors.