
Trust Center: answer customer questions without gathering everything again.
Certificates, reviewed evidence, reports and subprocessors sit in one place. When the next security questionnaire arrives, the material is already there, and every piece of evidence carries its confidentiality level.



 5.0 out of 5
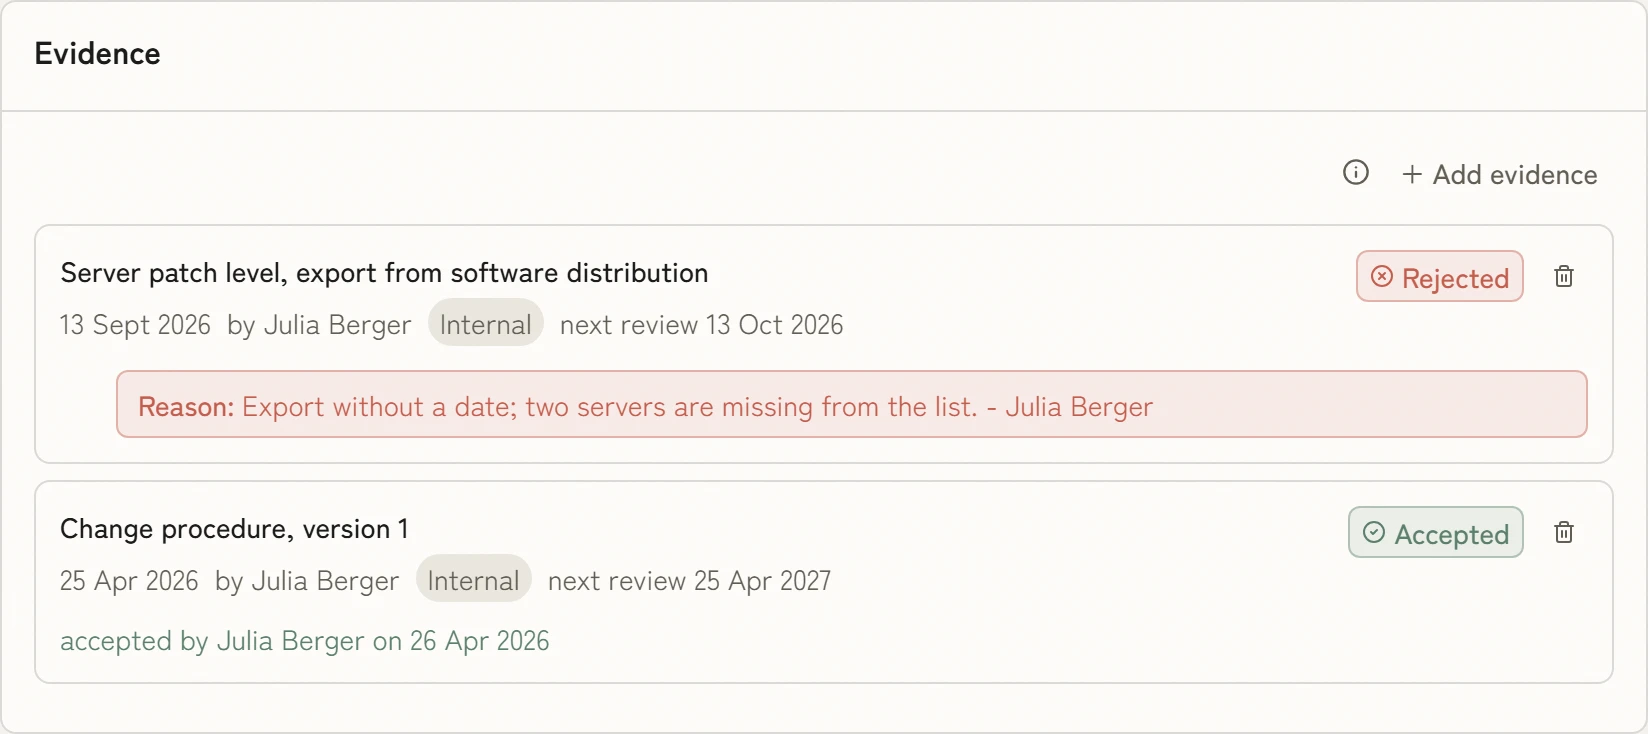
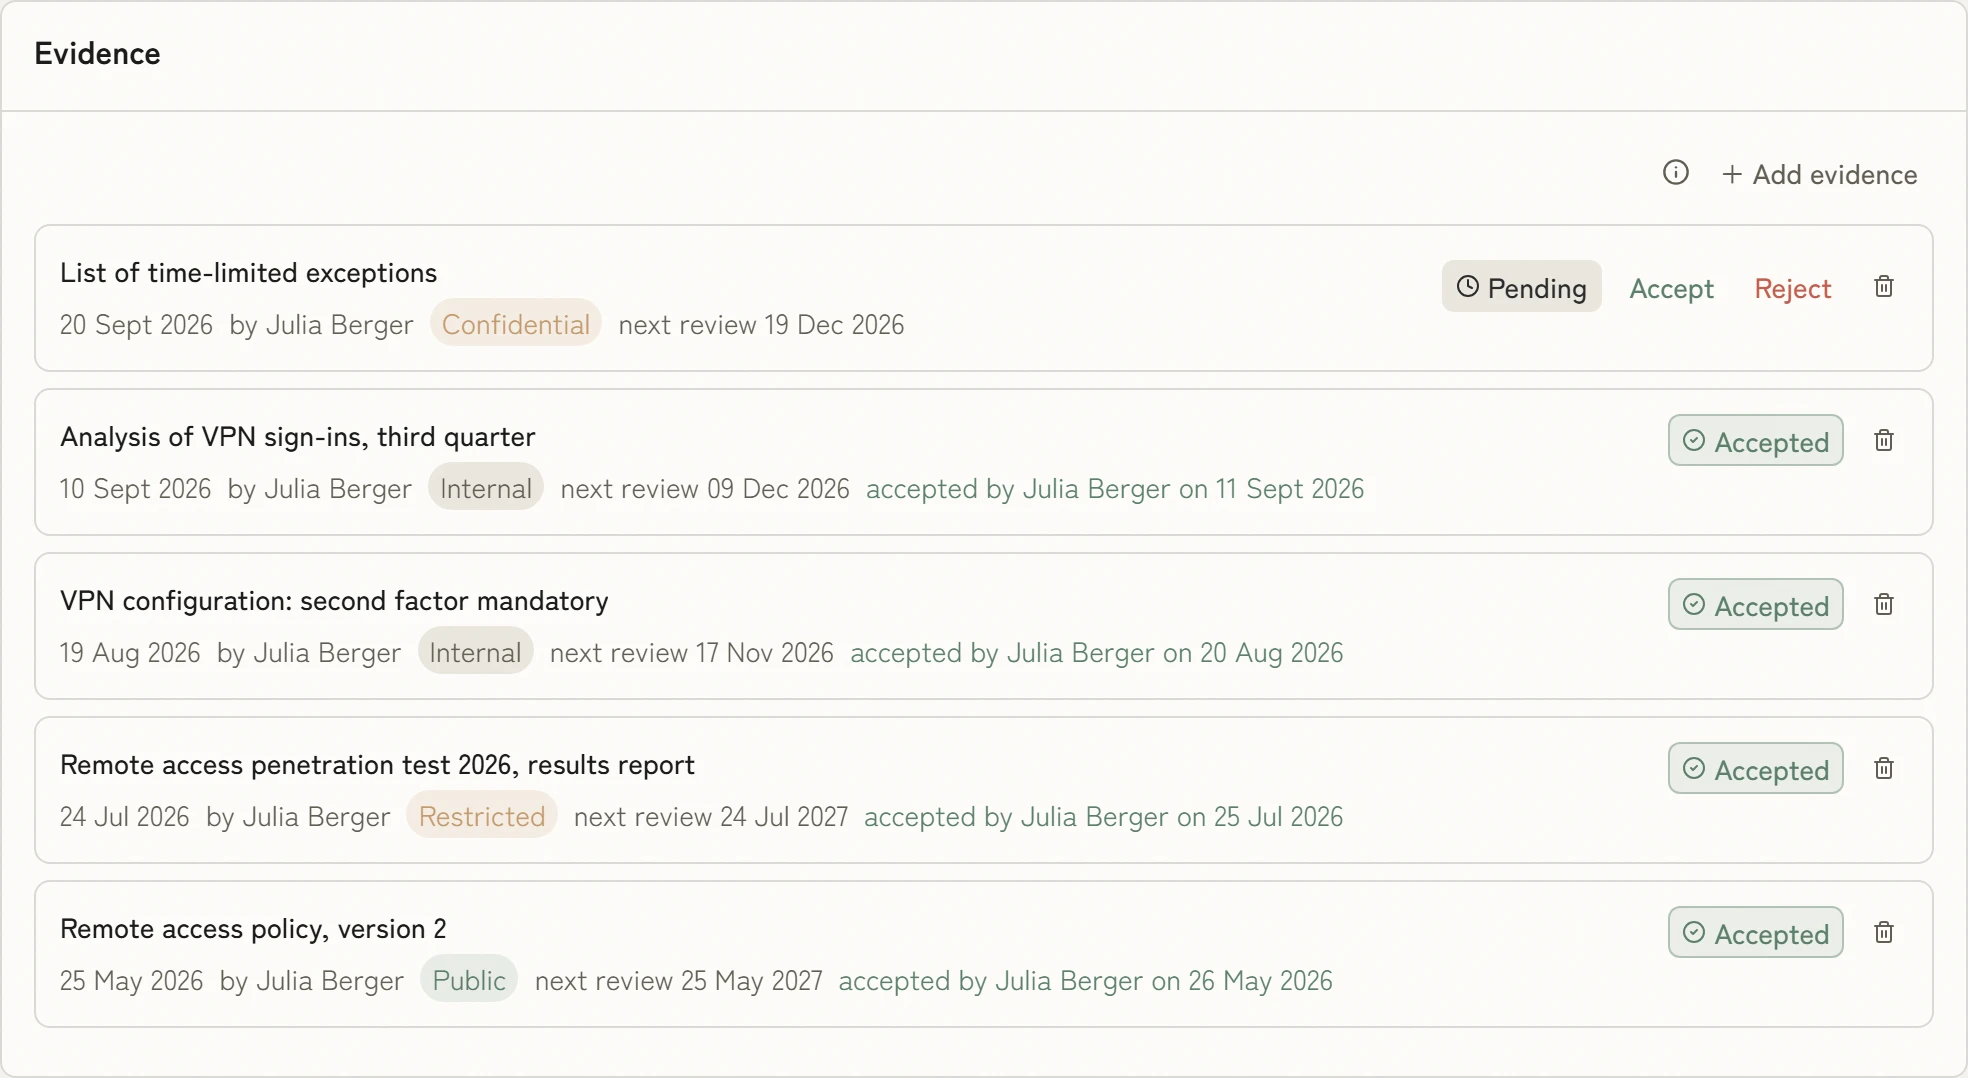
Only reviewed evidence goes out
Every piece of evidence is reviewed before it counts. An export without a date or with servers missing is rejected with a reason, and every item carries its confidentiality level and next review date.
Book a demo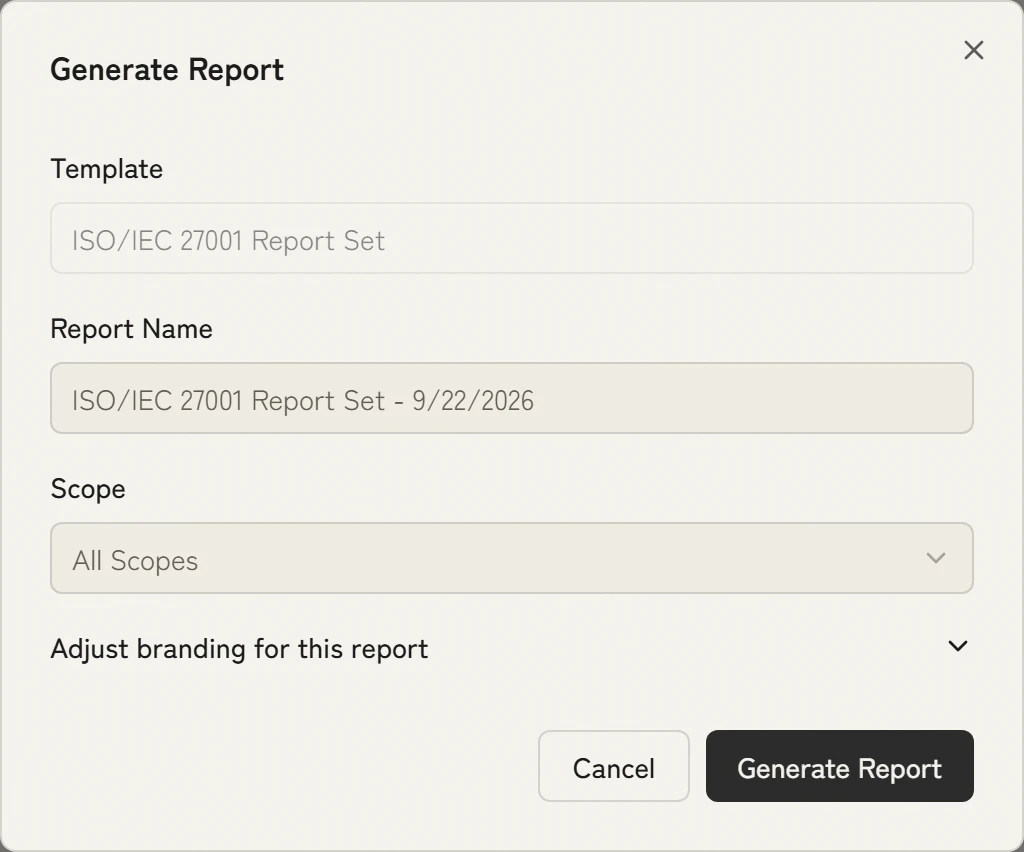
The customer report in one step
You create the statement of applicability, an ISO 27001 report set or a vendor report as a PDF from the current state. The report history records what you shared and when.
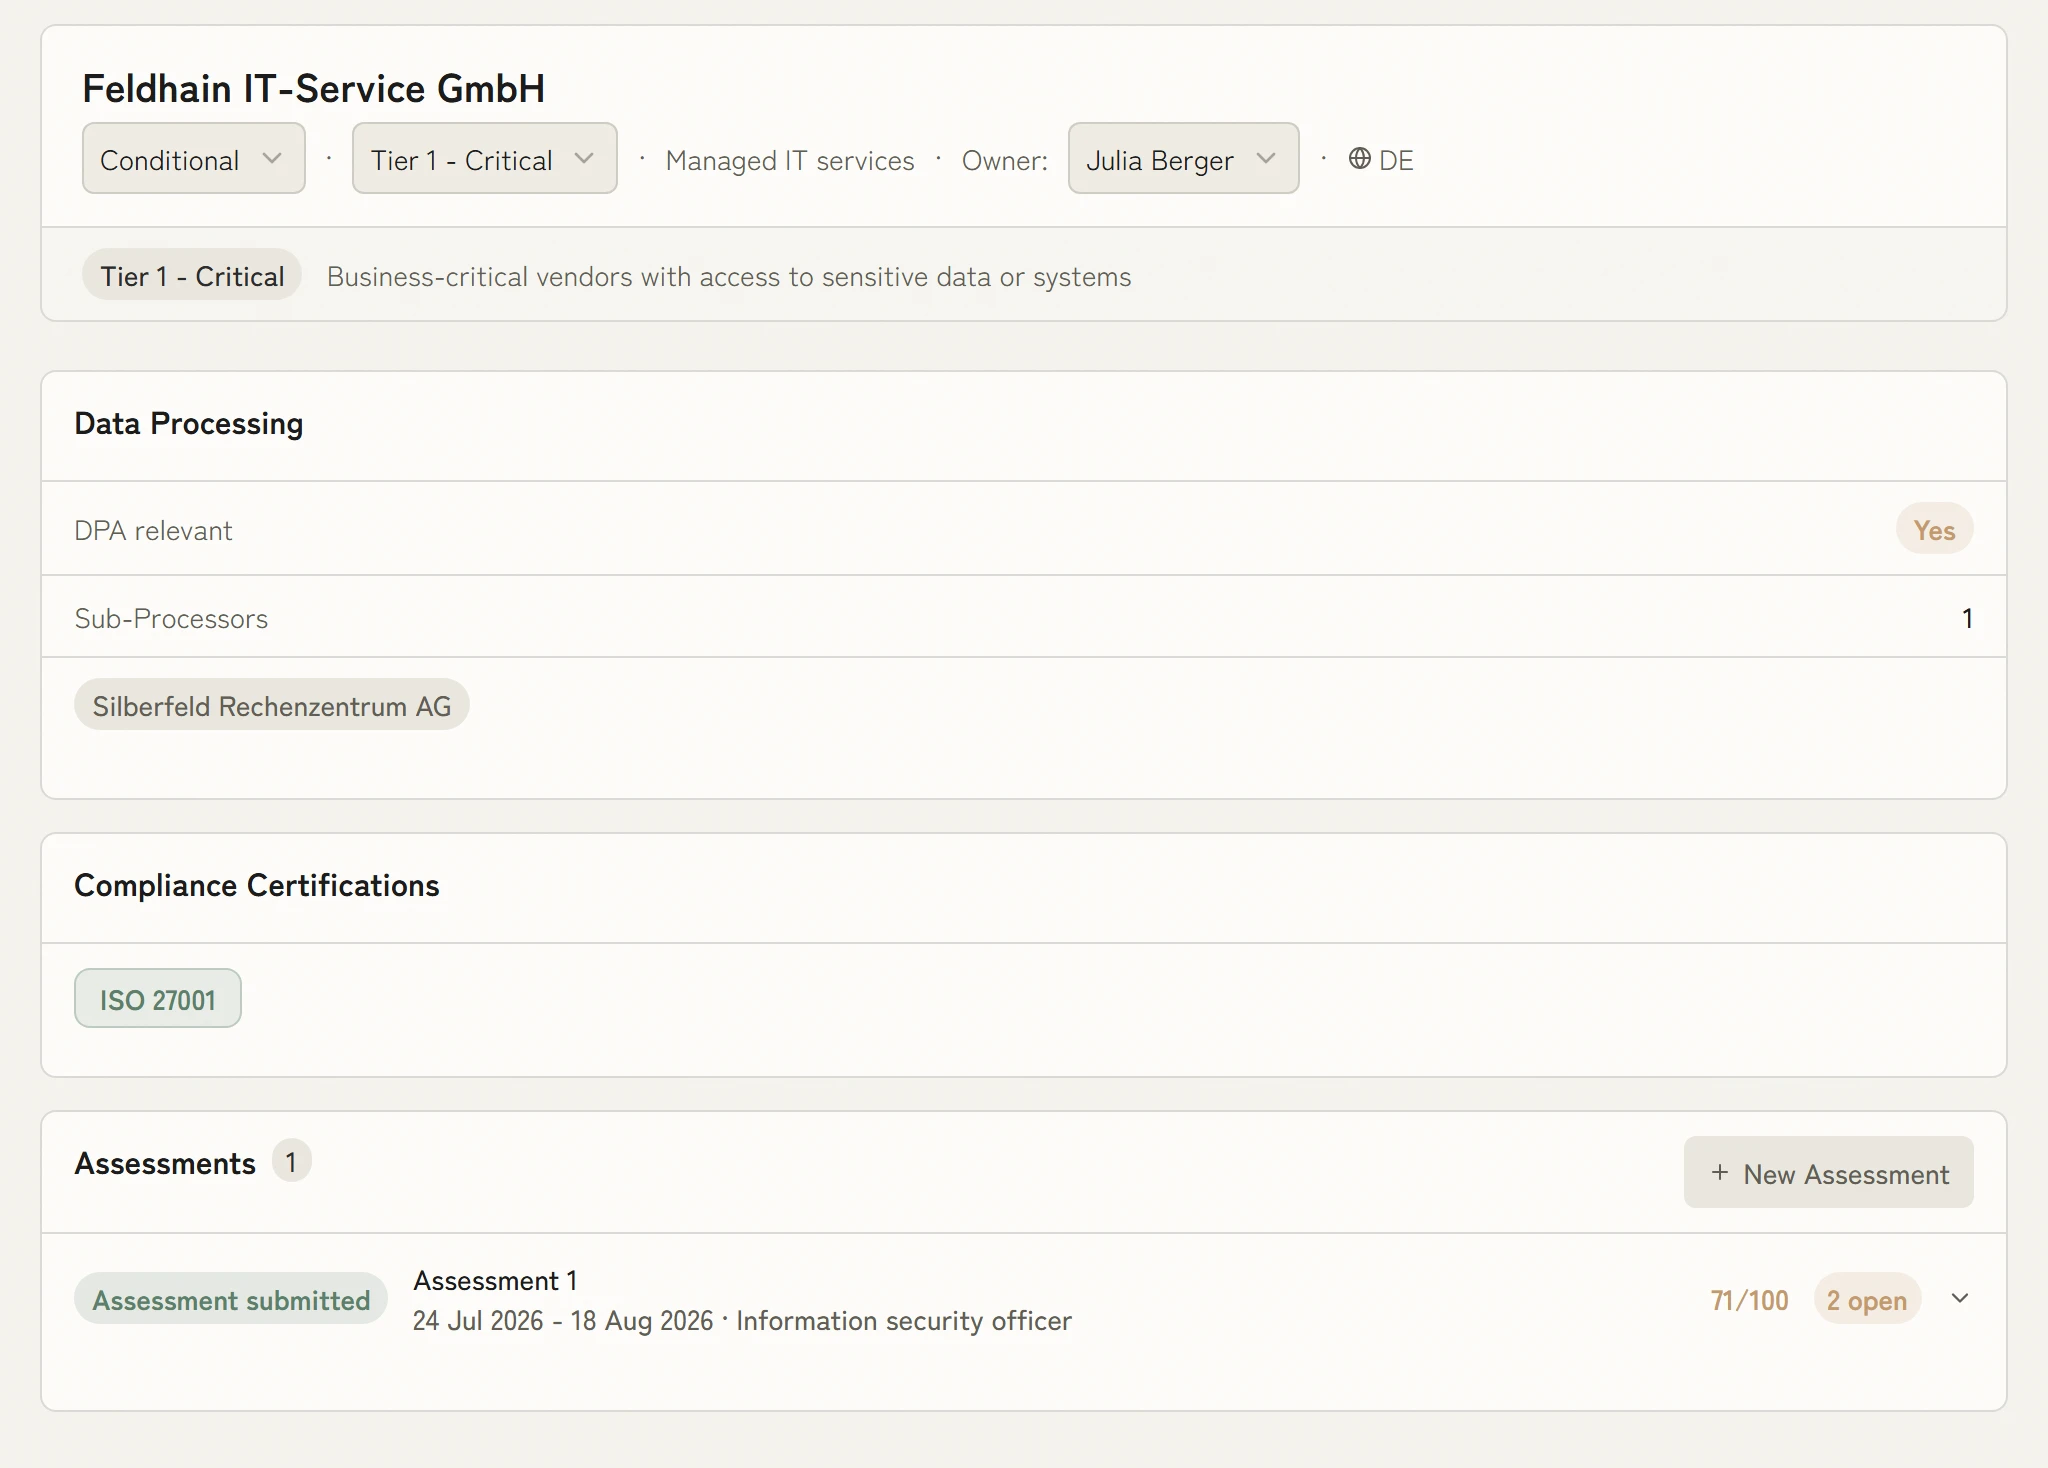
Book a demoThe subprocessor list is already maintained
Every processor sits in the register with its agreement, its own subprocessors, certification and latest assessment. The list customers ask for is the one your operation keeps anyway.
- pre-mapped controls
- 100+100+
- of evidence created as the work is done
- 100 %100 %
- faster than manual work
- 10×10×
- management systems, one data model
- 4 in 14 in 1
What KaitoSec also does
These sit in the core of the platform and apply to every module.
Implemented once, done for every requirement.
More than 100 controls are already mapped to ISO 27001, NIS2, DORA and other requirements. You implement a control once and evidence it once. Every further requirement it covers costs no extra work.
You review and approve instead of filling empty fields.
Agents prepare the risk analysis, the statement of applicability and actions from audit reports. Every result is ready for approval. A person still makes the decision.
Nothing left to collect before the audit.
Evidence is created as the work gets done: a tested backup supplies its recovery time, a completed review its result. Your evidence is current every day, not just in the week before the audit.
The right answer, even without expertise.
Sales does not need to know the standards: it points to approved material, and every piece of evidence shows its confidentiality level. That makes clear what may go out, and sensitive evidence stays with security and compliance.
You maintain each process only once.
Information security, business continuity management, data protection, AI governance and supplier management all work from the same process data. Every change takes effect in every system at once. Duplicate entry and conflicting registers go away.

Ask Chris how this would work for you.
Co-founder and CEO of KaitoSec. He walks through your case with you, live in the product.
Book a demo
The data for your customer security reviews is already there.
100+ integrations
All integrations















FAQ
Does KaitoSec publish a public trust page?
No. KaitoSec keeps the approved state that trust pages and security reviews rely on: evidence, reports, certificates and subprocessors. You share it as reports, exports or read-only access, and decide each time what goes out.
How do we control what a customer receives?
Every piece of evidence carries a confidentiality level and a review status. Reports are created from the current state and stay in the report history, so it remains traceable what was shared with whom and when.
Can an auditor look at the state directly?
Yes. The auditor role gives read-only access to assets, requirements, risks and controls and lets the auditor review evidence, without changing anything in the workspace.
How does this help with GDPR questions from customers?
Subprocessors, data processing agreements and the processing activities they touch are kept in the vendor register and the record of processing. Customer questions about them are answered from the same records your data protection work uses.

Less work in your customer security reviews.
One questionnaire you answered recently is enough. In thirty minutes you see which evidence, reports and subprocessor records KaitoSec already holds for it.