
QMS
QMS and ISMS from one process map
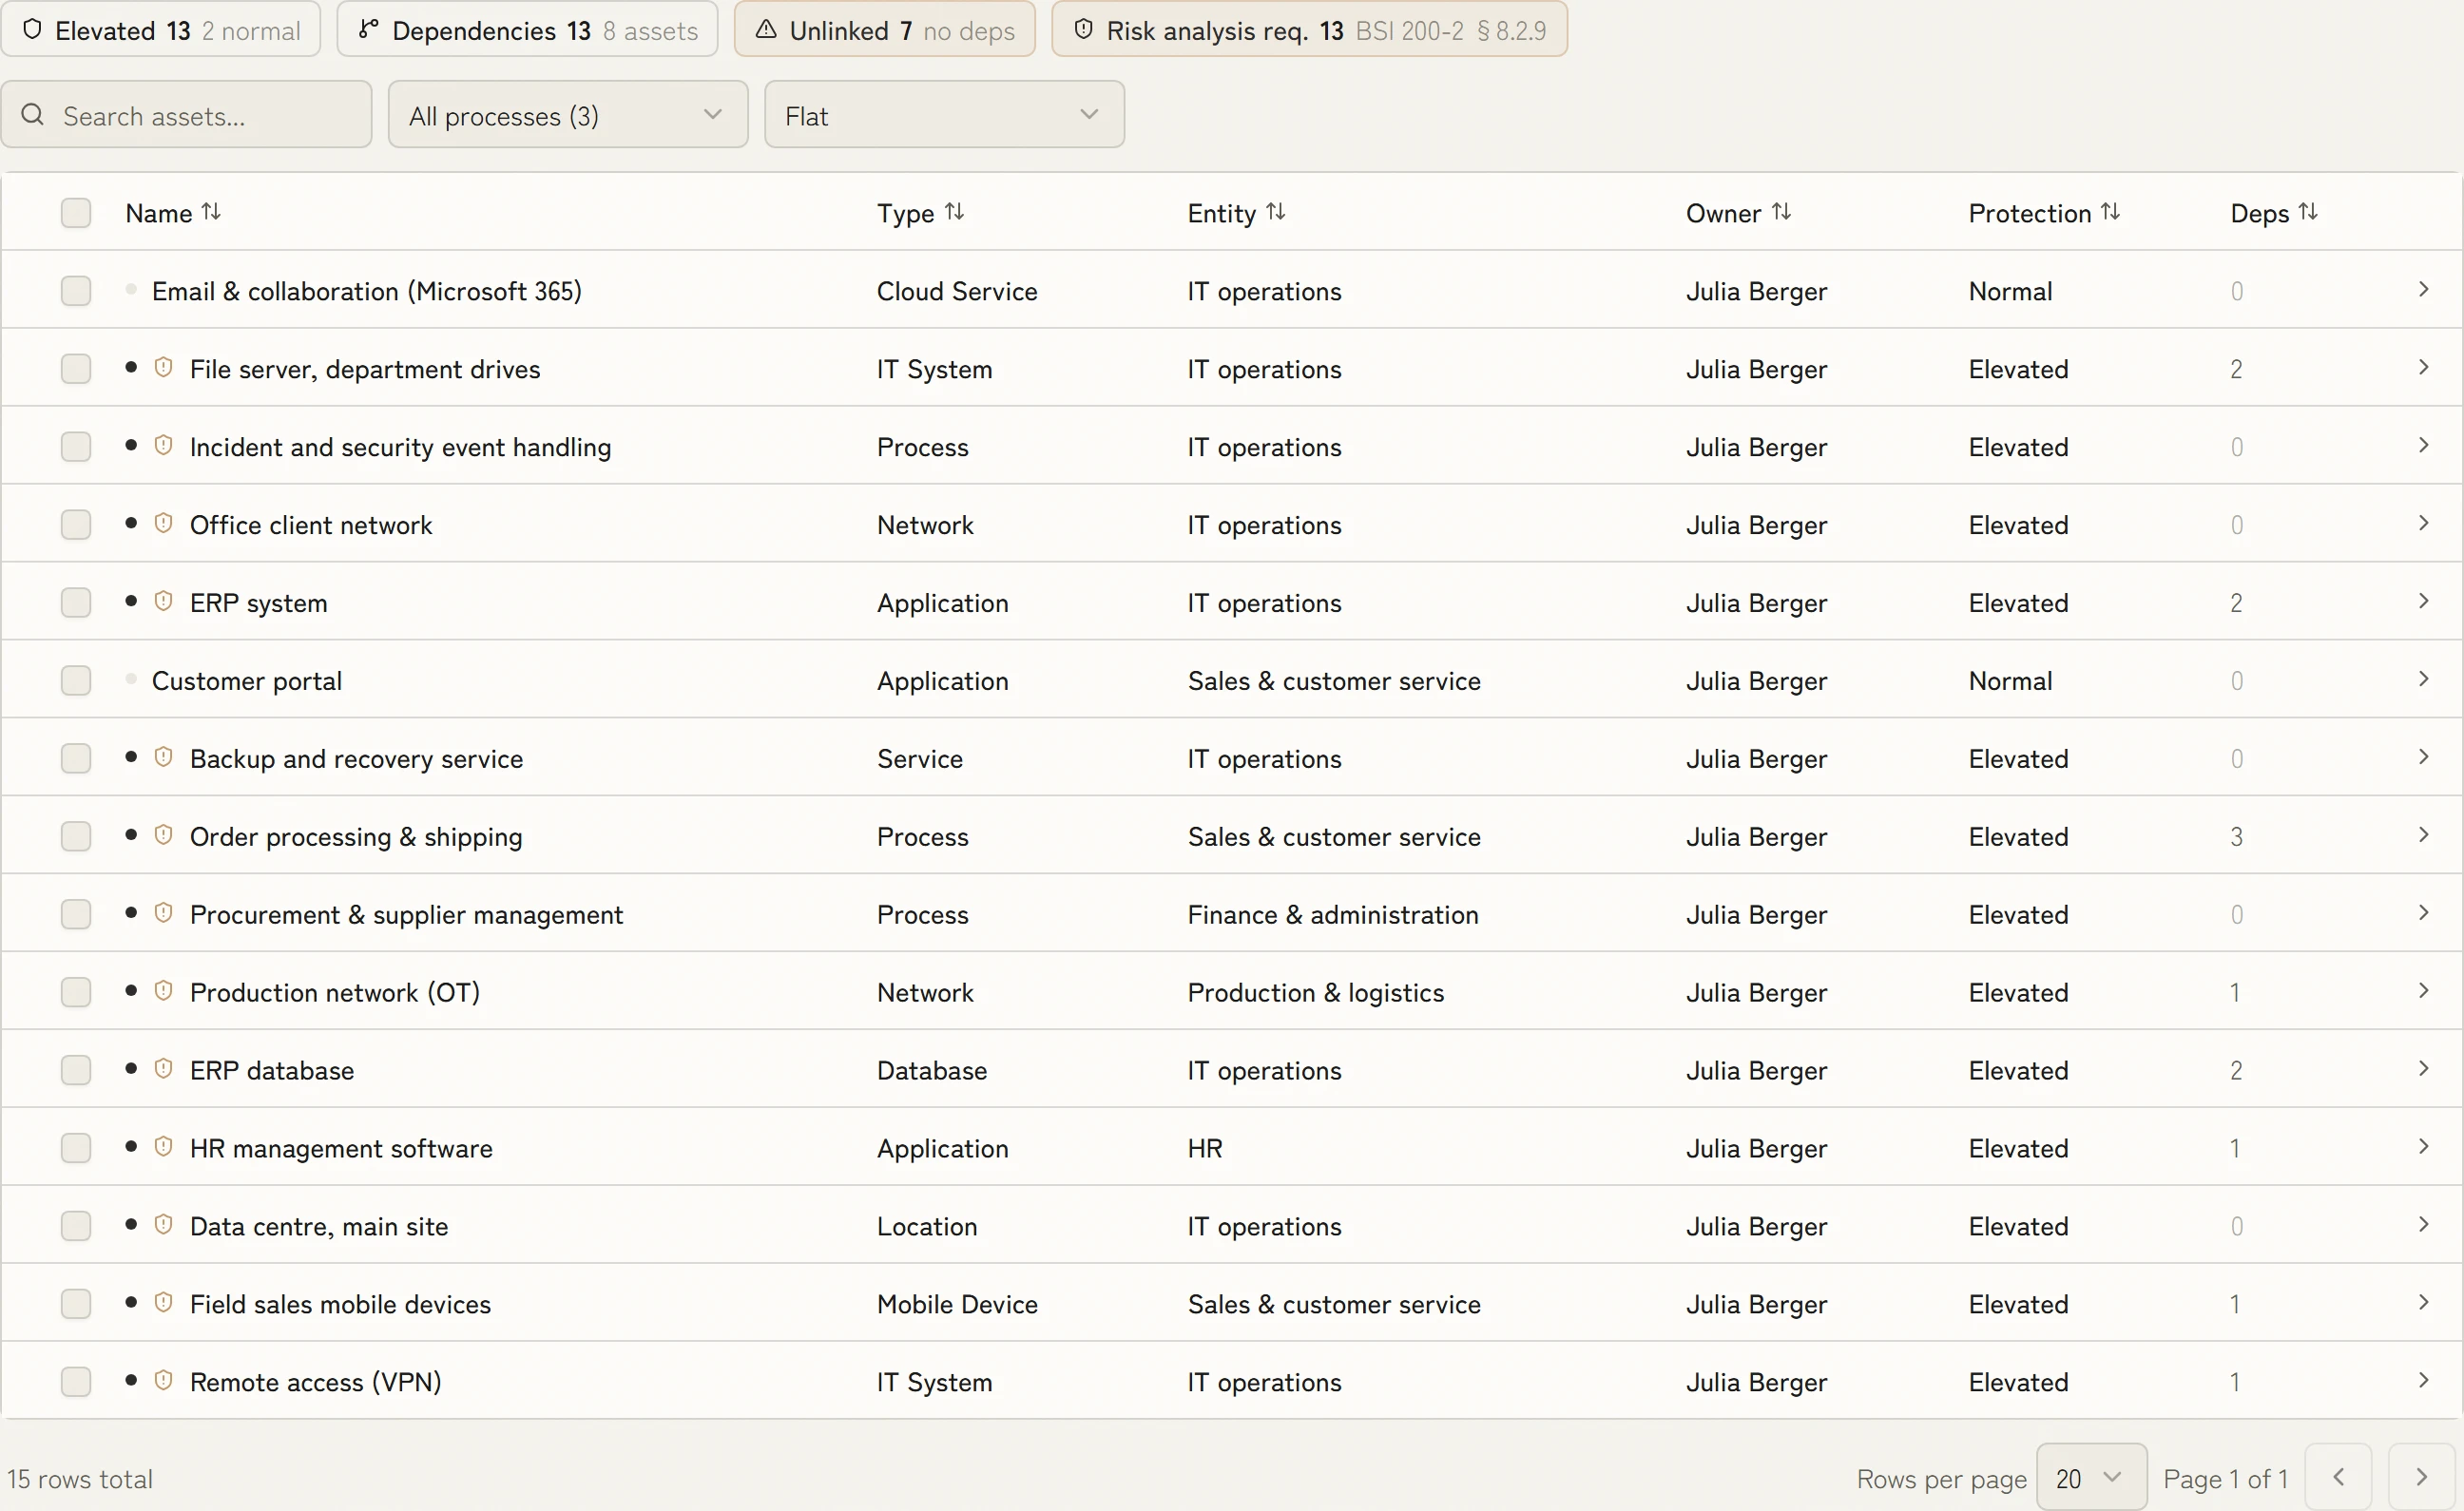
An ISMS needs documented processes first. KaitoSec uses your QMS process landscape as the structural base for ISMS, BCMS and the GDPR record.



 5.0 out of 5
What changes for your team
The process landscape as the starting point for the ISMS
Business processes, owners, documents, applications and vendors are modelled once. ISMS structural analysis, BCMS BIA and GDPR RoPA build on top instead of being captured in parallel. Without documented processes any ISMS is an assertion, not a system.
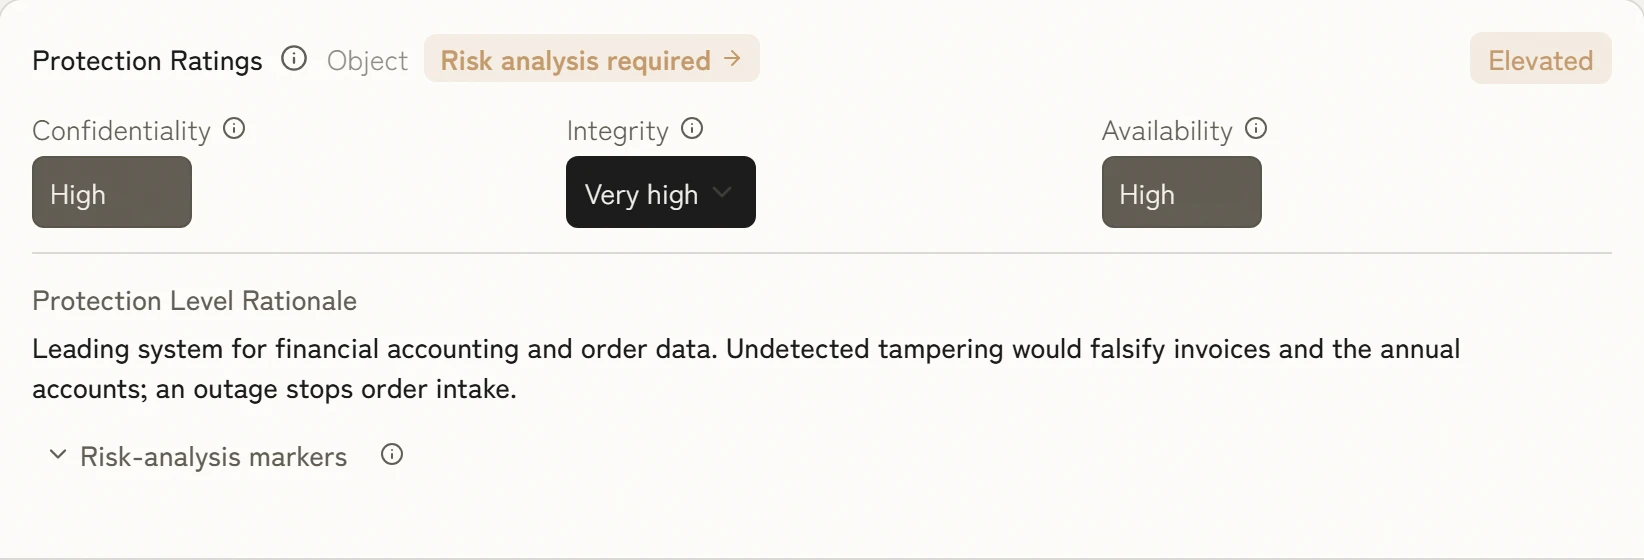
Reuse your Aiio processes instead of modelling them again
Bring approved QMS process data from Aiio into the structural base for ISO 27001 Annex A, BSI modules and ISO 22301 BIAs. Aiio models processes; KaitoSec links them to risks, controls and evidence.
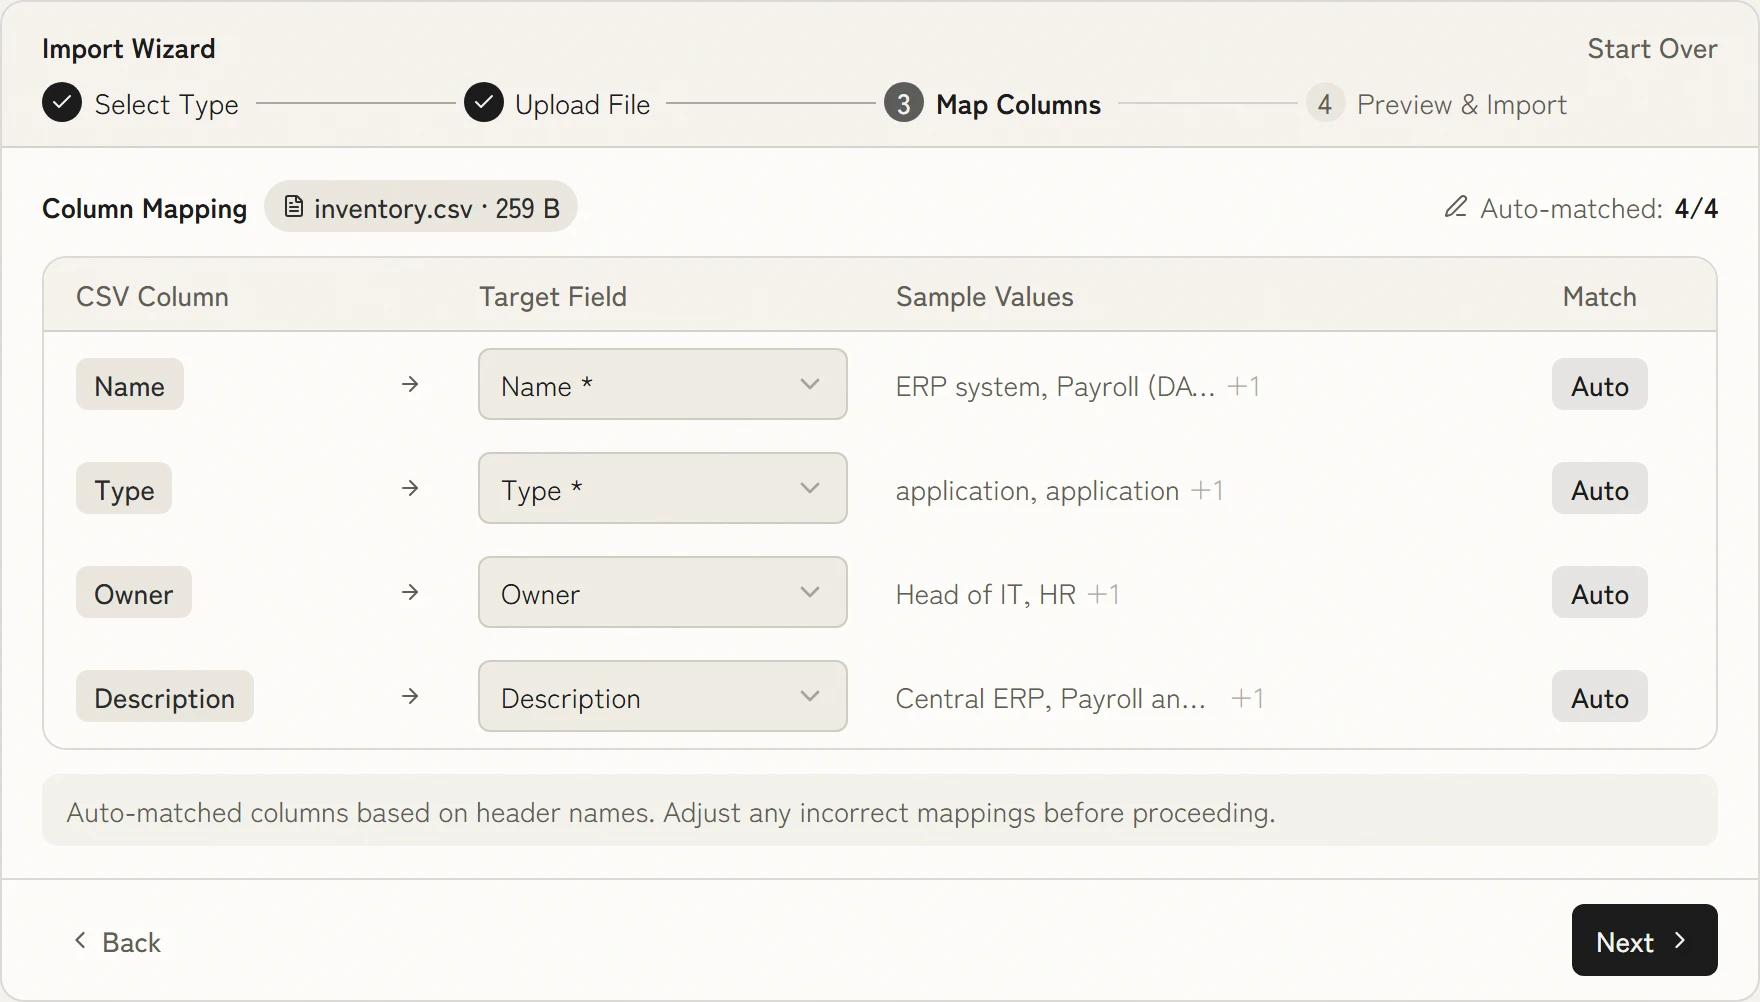
See what every process change affects
When a process changes, KaitoSec shows the linked controls, risks and recovery plans for review. This makes it clear where QMS, ISMS and BCMS need to be brought up to date.
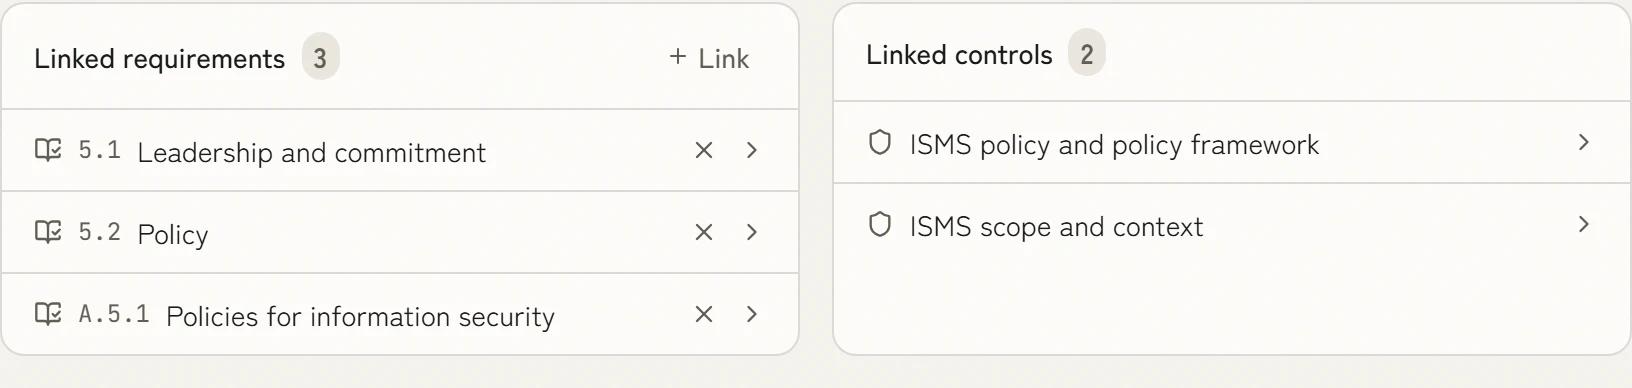
Audit-ready against several standards at once
A documented process landscape satisfies ISO 9001 cl. 4.4, ISO 27001 cl. 4.4 and ISO 22301 cl. 4.1 together. The crosswalks ship with KaitoSec and are maintained by KaitoSec, not by your team.
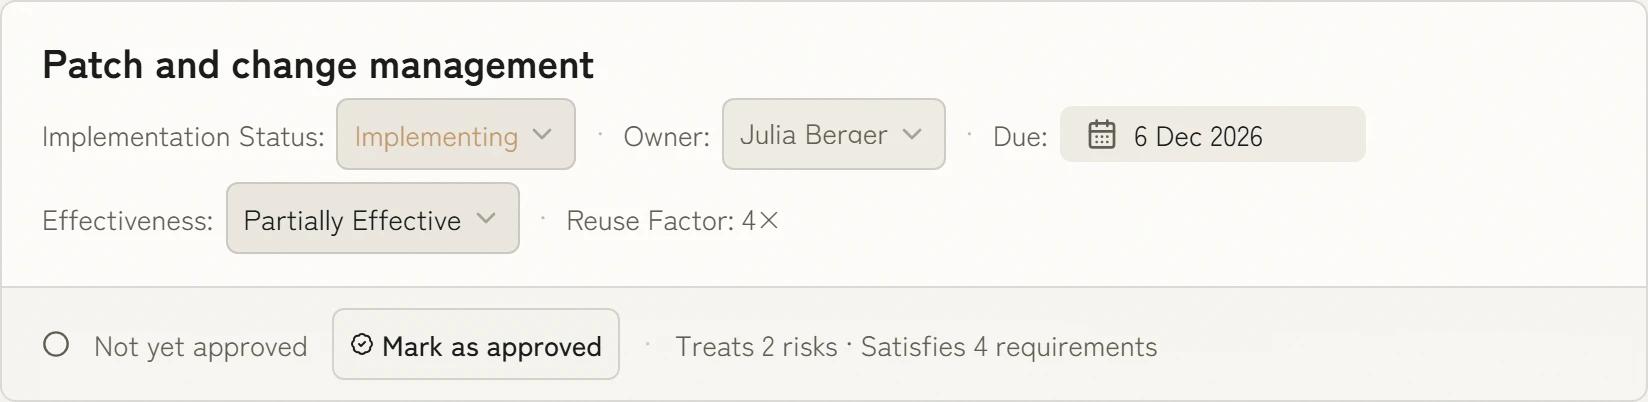
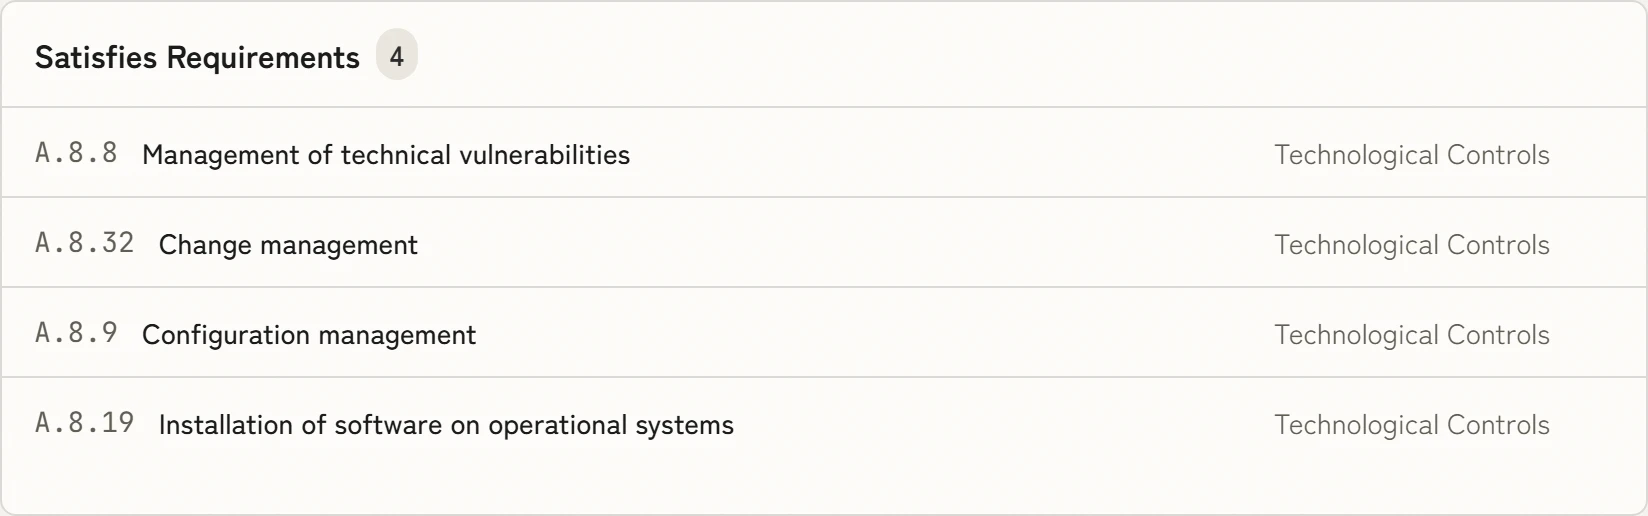
Processes, applications and documents come from the systems you already use.
100+ integrations
All integrations
















Matching standards and modules
Relevant requirements
How KaitoSec supports the work

Bring calm to your working week.
A personal demo in 30 minutes: we go through your process map and show how the ISMS and BCMS build on it.