
Skip to content

Security officer & CISO

Maintain every control once, prove it for every standard.

Information security, business continuity, data protection and AI governance in one system. You maintain controls once, prove them for every matching standard and show leadership what needs deciding next.

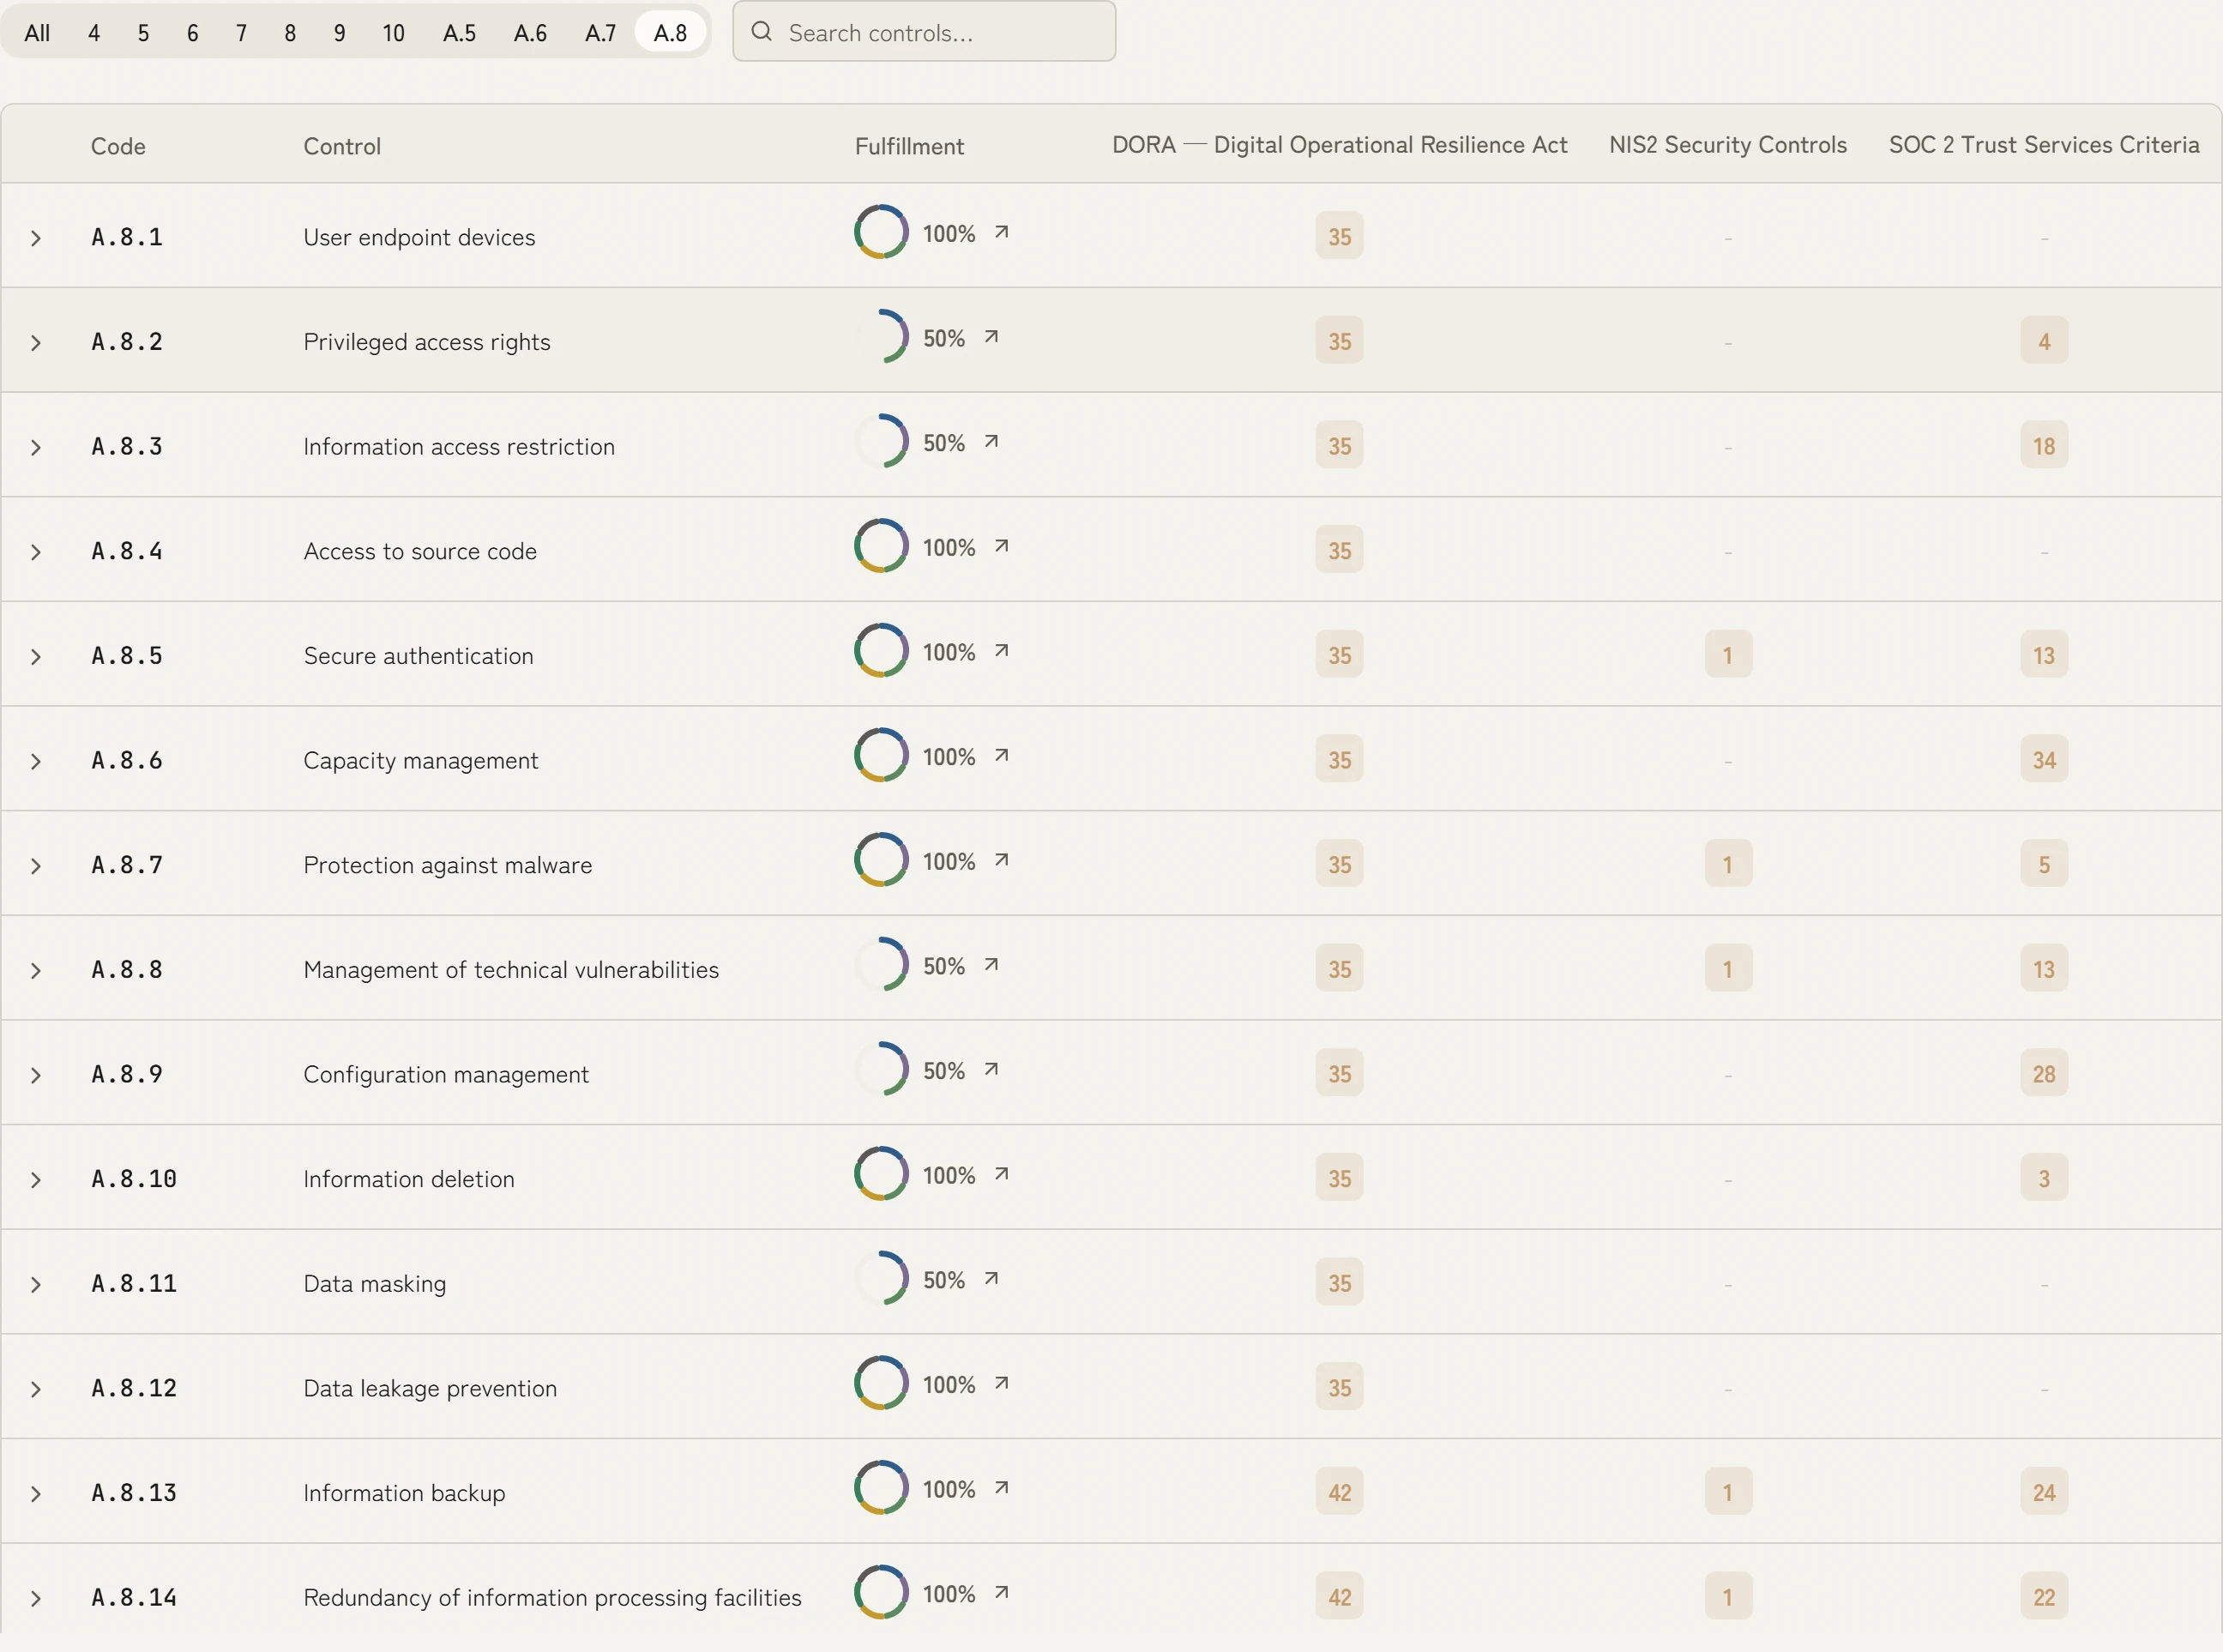
Catalog matrix in KaitoSec: fourteen ISO 27001 controls from chapter A.8 with their fulfilment and, beside each, the number of mapped requirements from DORA, NIS2 and SOC 2.
Counts for DORA, NIS2 and SOC 2
  • TeleTrusT trust seal, IT Security made in Germany
  • Member of BITMi, Bundesverband IT-Mittelstand e. V.
  • OMR Reviews5.0 out of 5
  • HOSTING INGERMANY
  • GDPR-COMPLIANT
  • GRUNDSCHUTZ++ READY

What changes for your team

  1. Four management systems, one control library

    Maintain controls, policies and risks once and evidence them across ISO 27001, BSI Grundschutz, NIS2, GDPR, ISO 22301 and ISO 42001 in parallel. An ISMS tool on its own will not keep you operational when an incident stops production. KaitoSec covers the four management systems together.
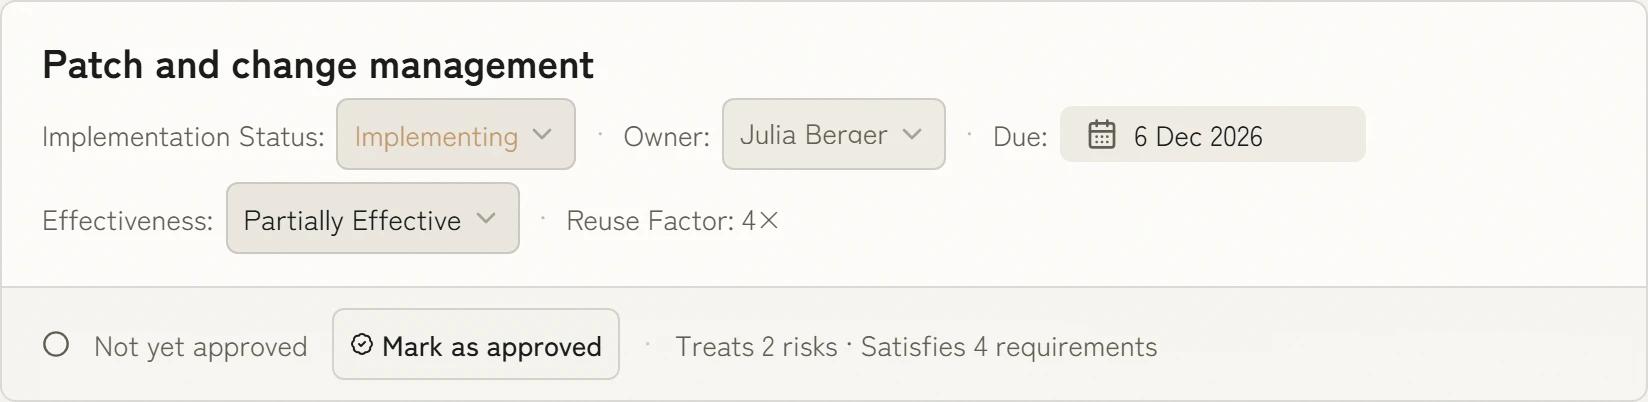
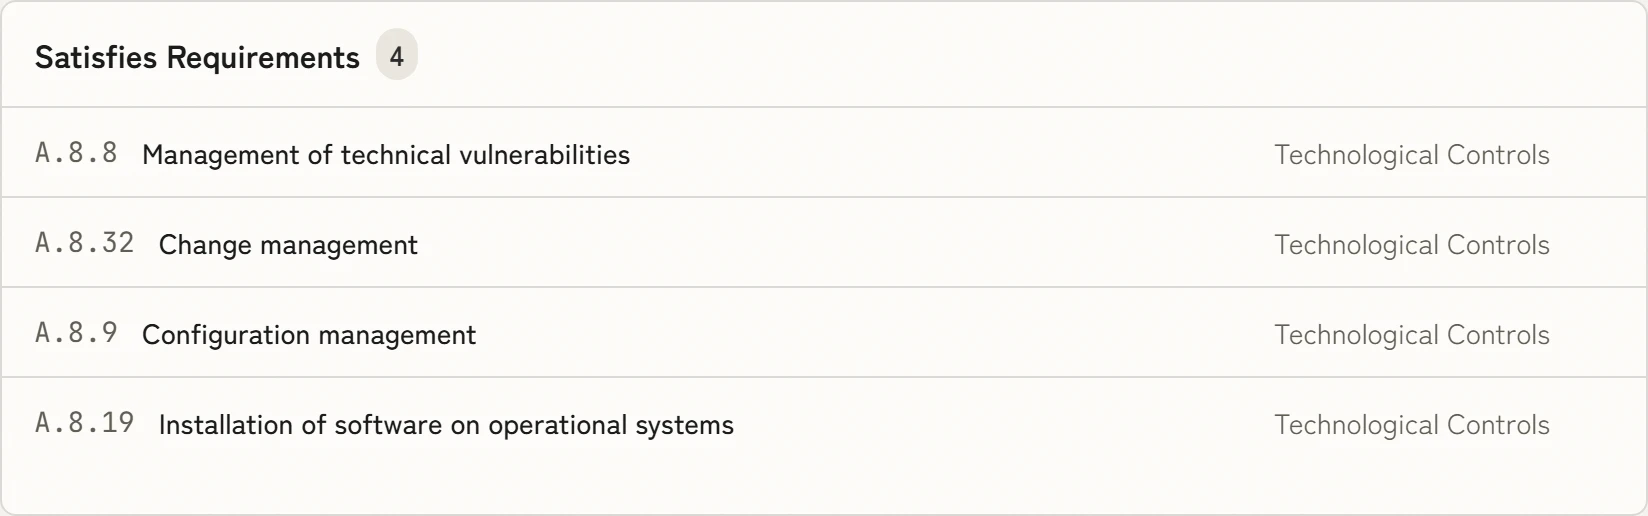
    The control Patch and change management with status, owner, due date and effectiveness, above the four ISO 27001 requirements it meets.
    The requirements the control meets: A.8.8, A.8.32, A.8.9 and A.8.19.
  2. Resilient in an incident, not just in an audit

    A certificate does not protect against ransomware. KaitoSec runs BIA, RTO/RPO, recovery plans and exercises next to your ISMS and ties every incident back to the controls that should have prevented it. Continuity is part of the system, not an appendix.
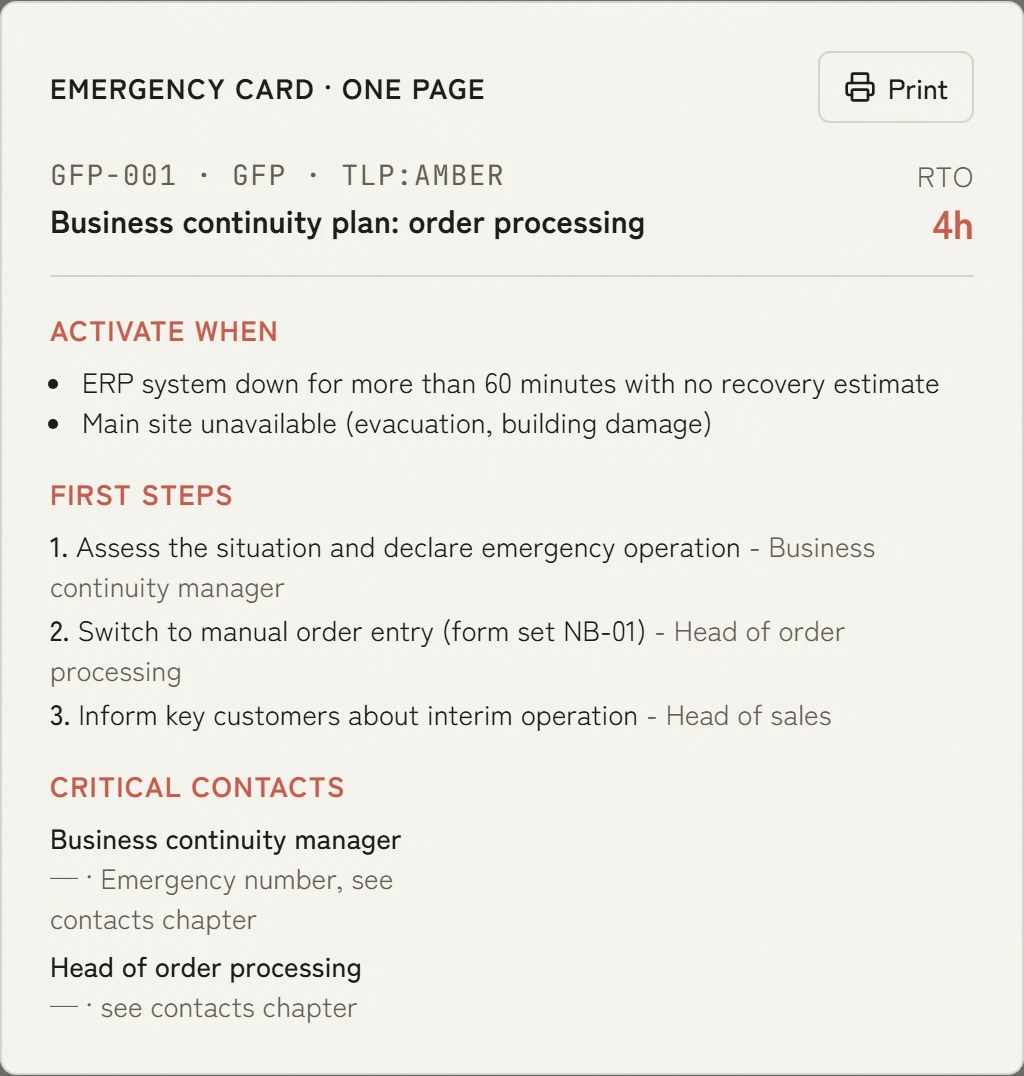
    Emergency card of a business continuity plan on one page: activation criteria, first steps with owners and critical contacts.
  3. Audit-ready without patching spreadsheets

    Evidence, approvals and risk treatments are versioned and linked to the controls they affect. Prepare Stage 1 and Stage 2 packages from the approved state. Who decided what and when remains on record.
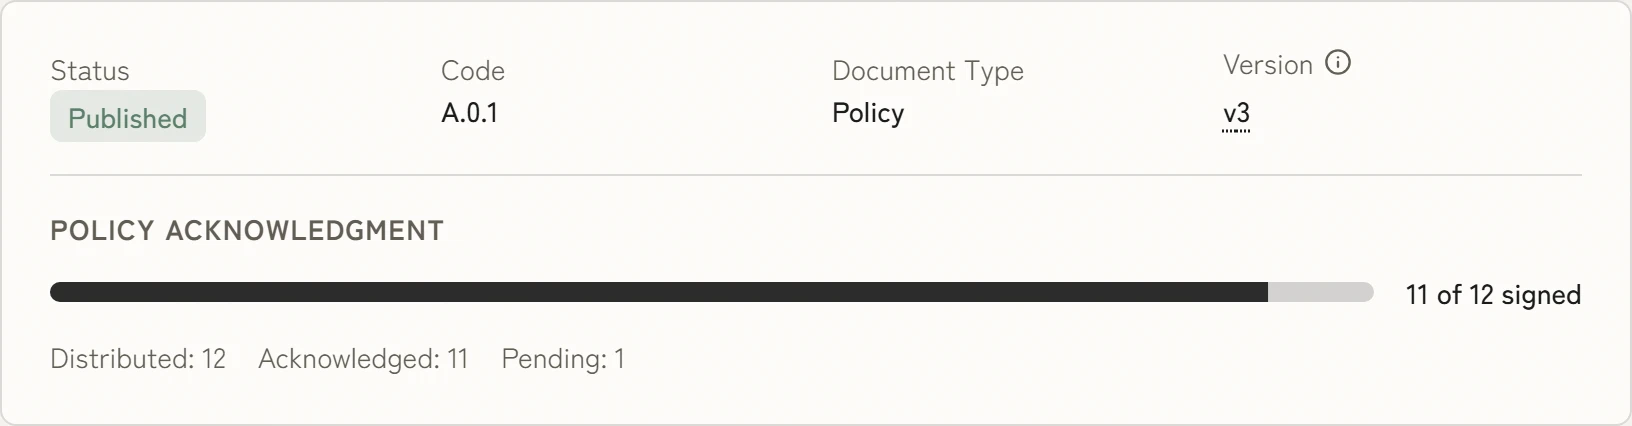
    Information security policy, published as version 3: 11 of 12 employees have acknowledged it.
The control Patch and change management with status, owner, due date and effectiveness, above the four ISO 27001 requirements it meets.
The requirements the control meets: A.8.8, A.8.32, A.8.9 and A.8.19.

The evidence comes from the systems you already use.

100+ integrations

All integrations

  • Microsoft Defender
  • Microsoft Entra ID
  • Microsoft Intune
  • PRTG
  • macmon NAC
  • Jira
  • Personio
  • i-doit
  • Matrix42
  • Microsoft Defender
  • Microsoft Entra ID
  • Microsoft Intune
  • PRTG
  • macmon NAC
  • Jira
  • Personio
  • i-doit
  • Matrix42
  • Docusnap 365
  • AWS
  • Microsoft Azure
  • Google Cloud
  • SharePoint Online
  • Confluence
  • Microsoft Teams
  • Excel & CSV
  • Docusnap 365
  • AWS
  • Microsoft Azure
  • Google Cloud
  • SharePoint Online
  • Confluence
  • Microsoft Teams
  • Excel & CSV

Bring calm to your working week.

A personal demo in 30 minutes: we go through your management systems and show how one control counts for several standards.













