
Process owners
See what your process depends on, and prove it in the audit
Process owners need the view of applications, vendors, risks and incident roles. KaitoSec delivers it in live operations.



 5.0 out of 5
What changes for your team
From process to application to vendor
Every process shows which applications it consumes and which vendors hang off it. A vendor outage, an application end-of-life or a new third-country transfer risk surfaces at the process, not in a separate list procurement keeps.
Business continuity that works, not just on paper
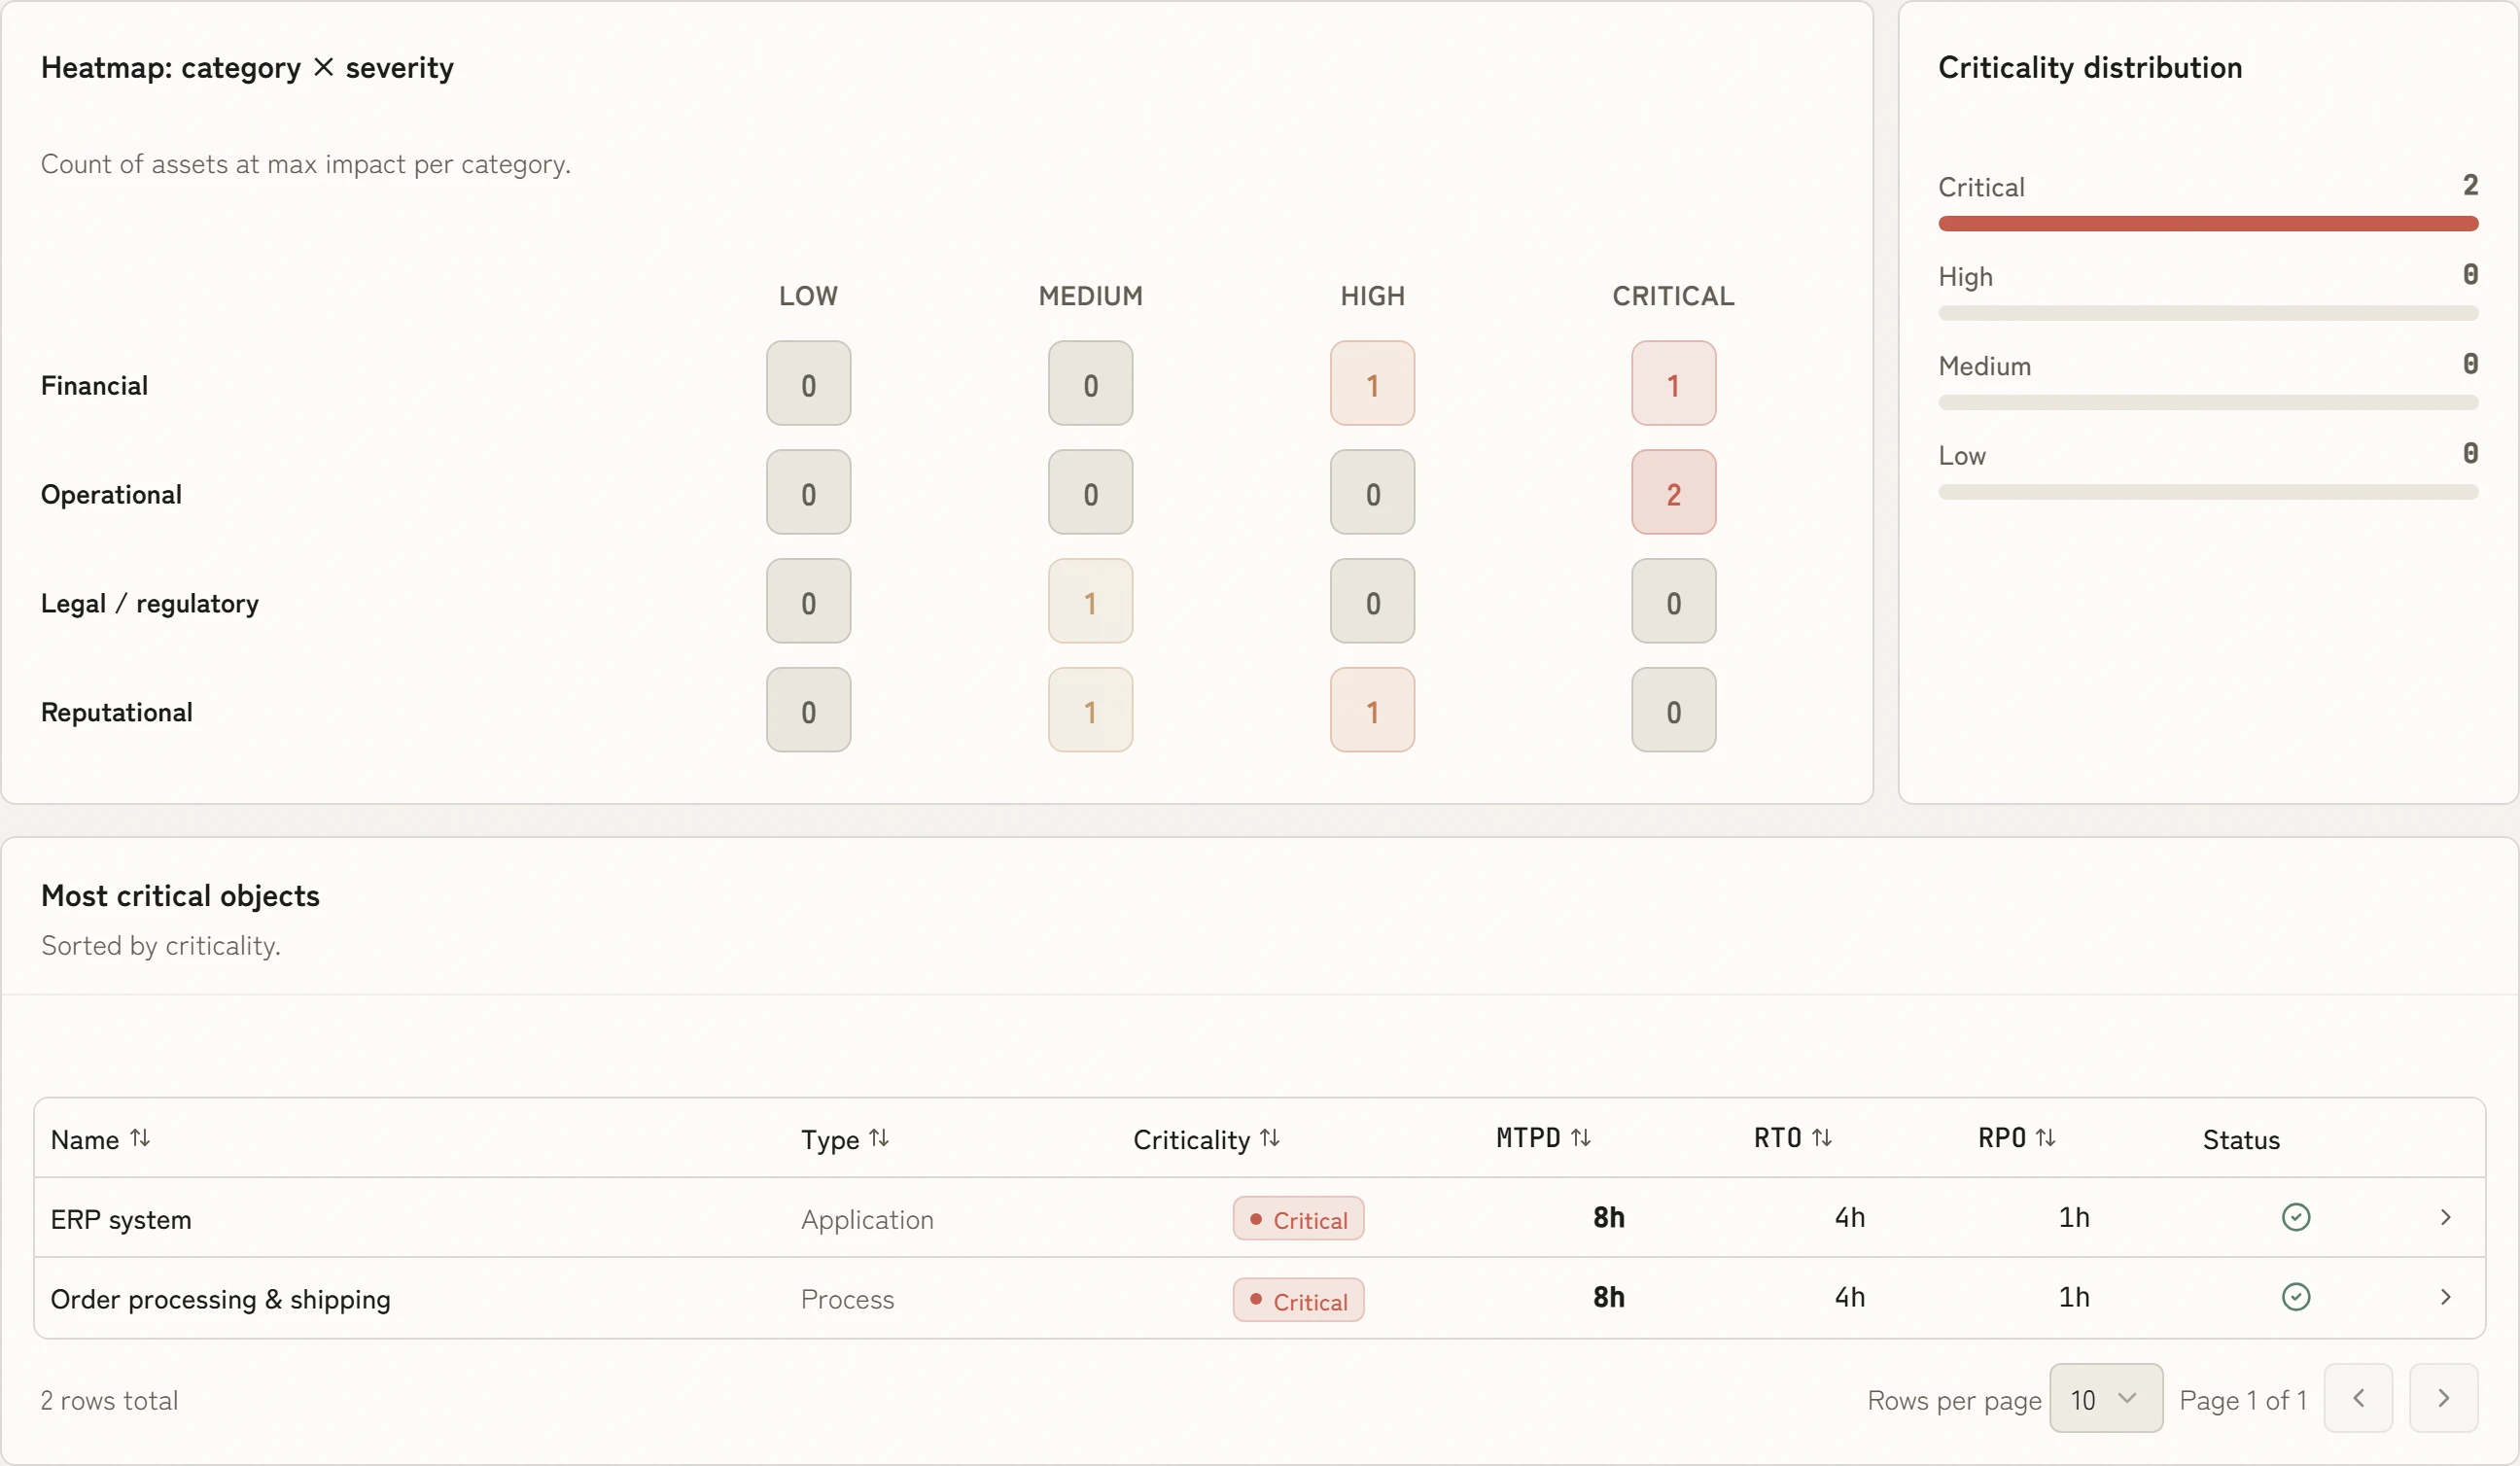
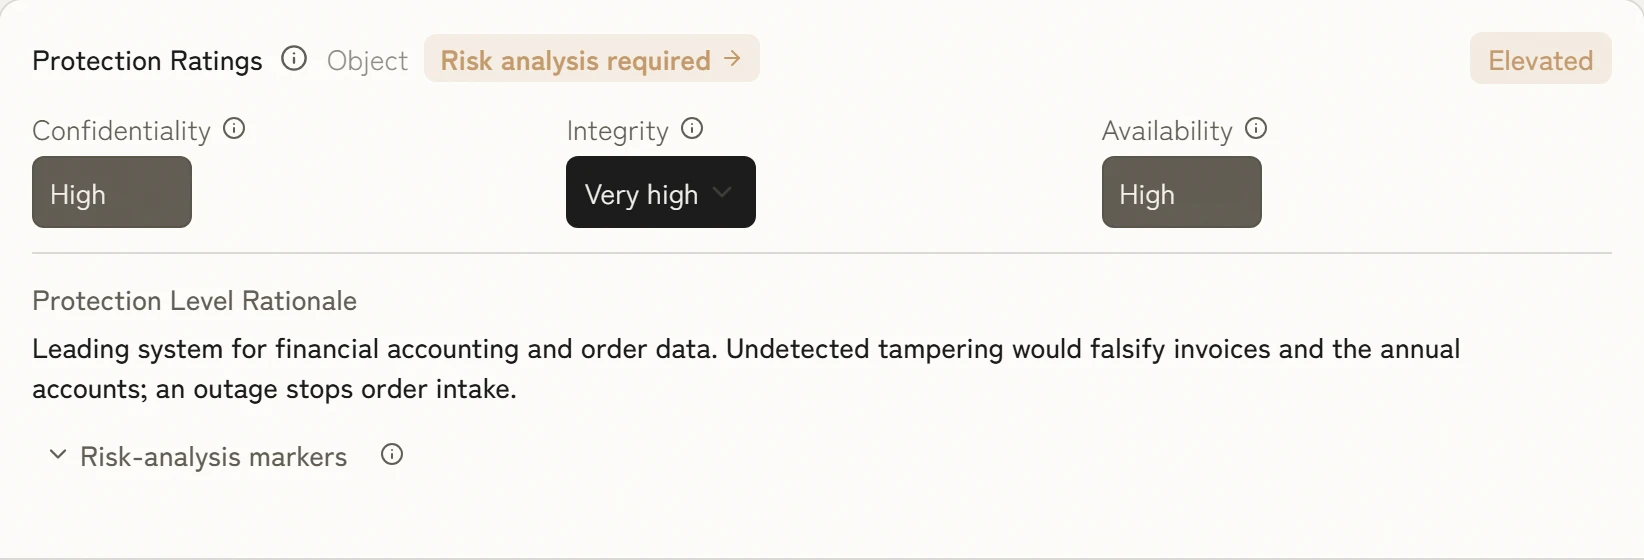
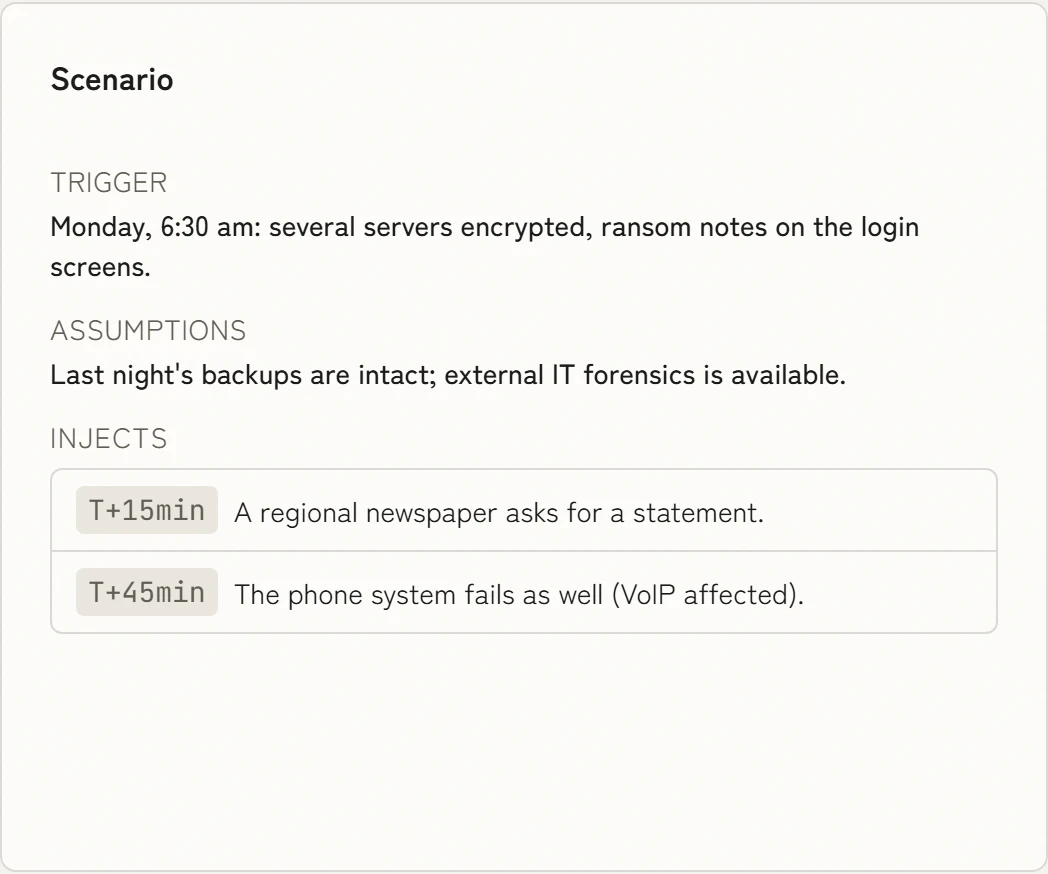
BIA, RTO and RPO are maintained at the process, not the IT system. When a central system is disrupted you see immediately which processes are affected, which recovery plans apply and who makes the restart decision.
Take processes over from Aiio
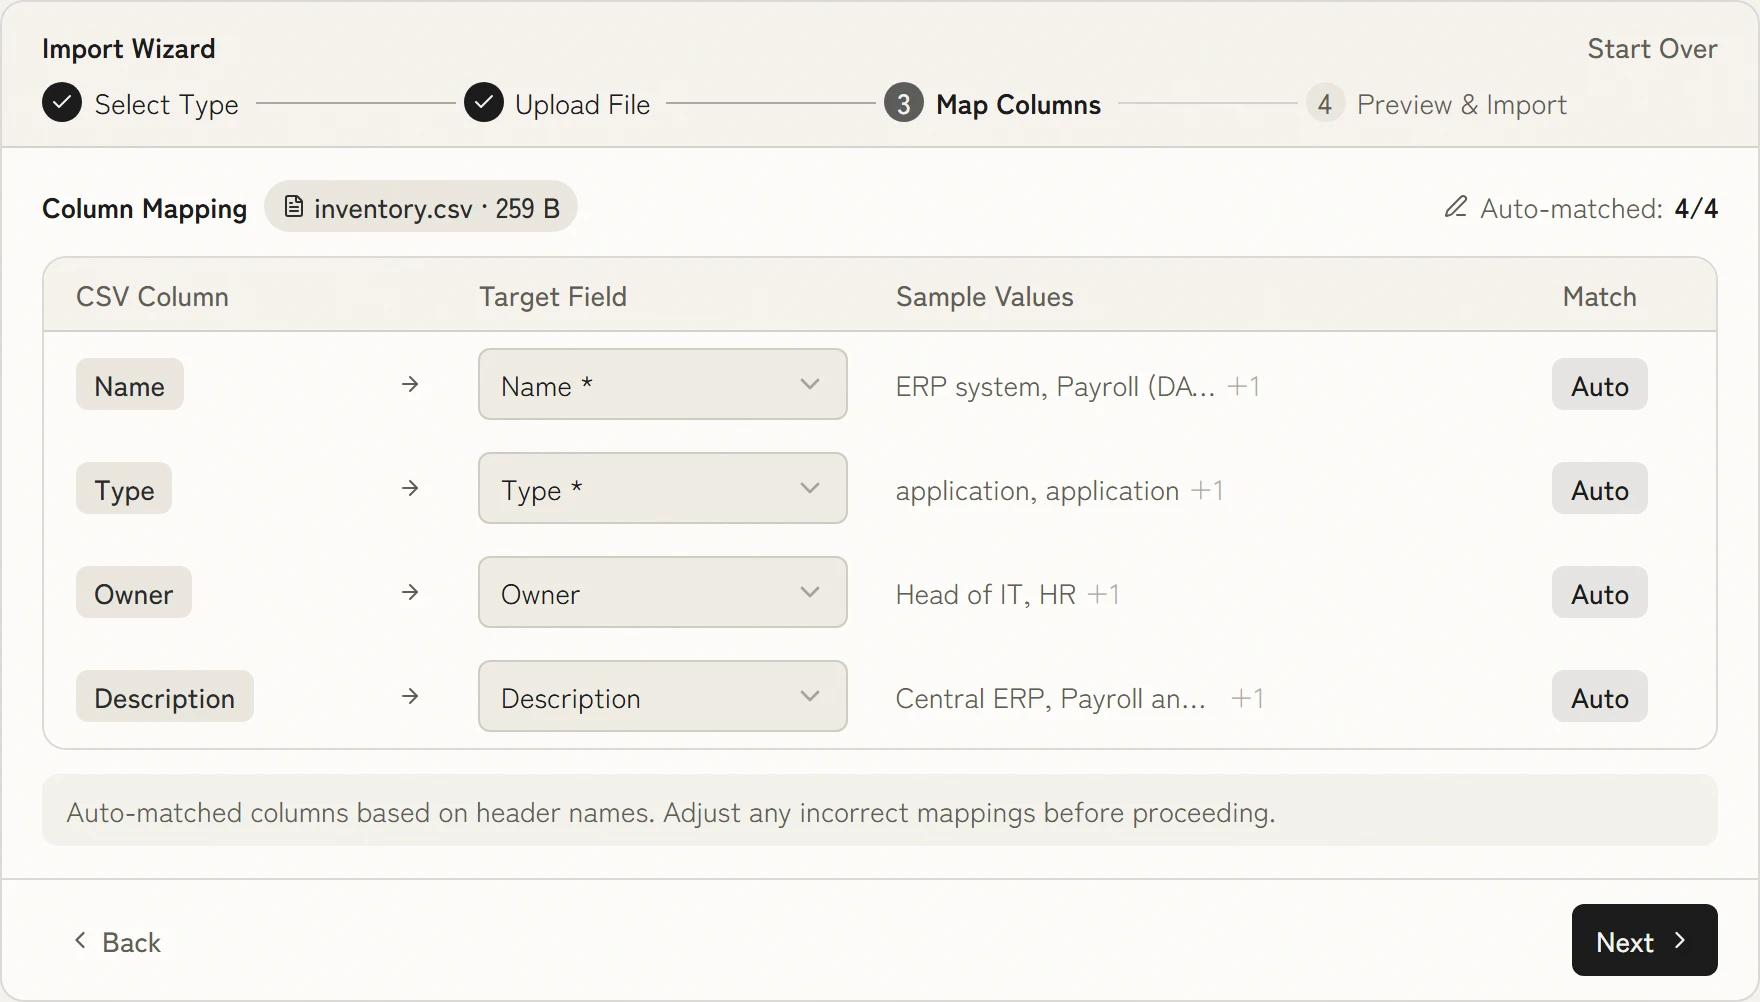
Aiio documents the process landscape. KaitoSec takes over that structure and links it to controls, risks and incidents. You do not model your process twice, and you avoid spreadsheet migration between quality and security.
Ownership that holds up in an audit
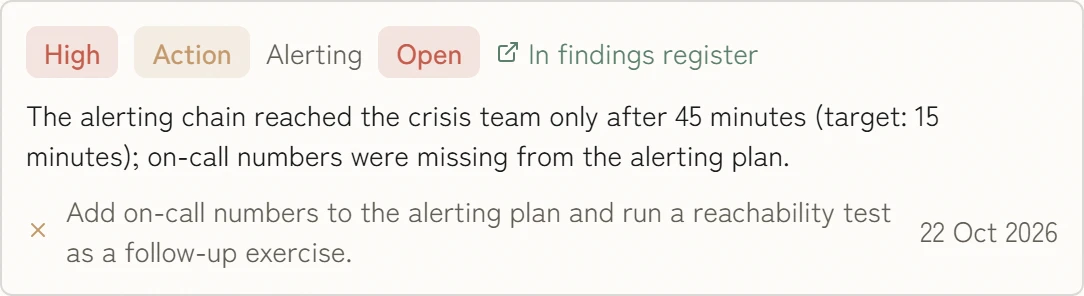
Who owns what is recorded in the system together with approvals, reviews and escalation paths. In an audit you present process ownership as lived practice, not as an org chart appended to the documentation.
Applications and dependencies come from the systems you already use.
100+ integrations
All integrations
















Matching standards and modules
Relevant requirements
How KaitoSec supports the work

Bring calm to your working week.
A personal demo in 30 minutes: we take one of your processes and show which applications, suppliers and emergency plans depend on it.