
Leadership
A security posture leadership can act on.
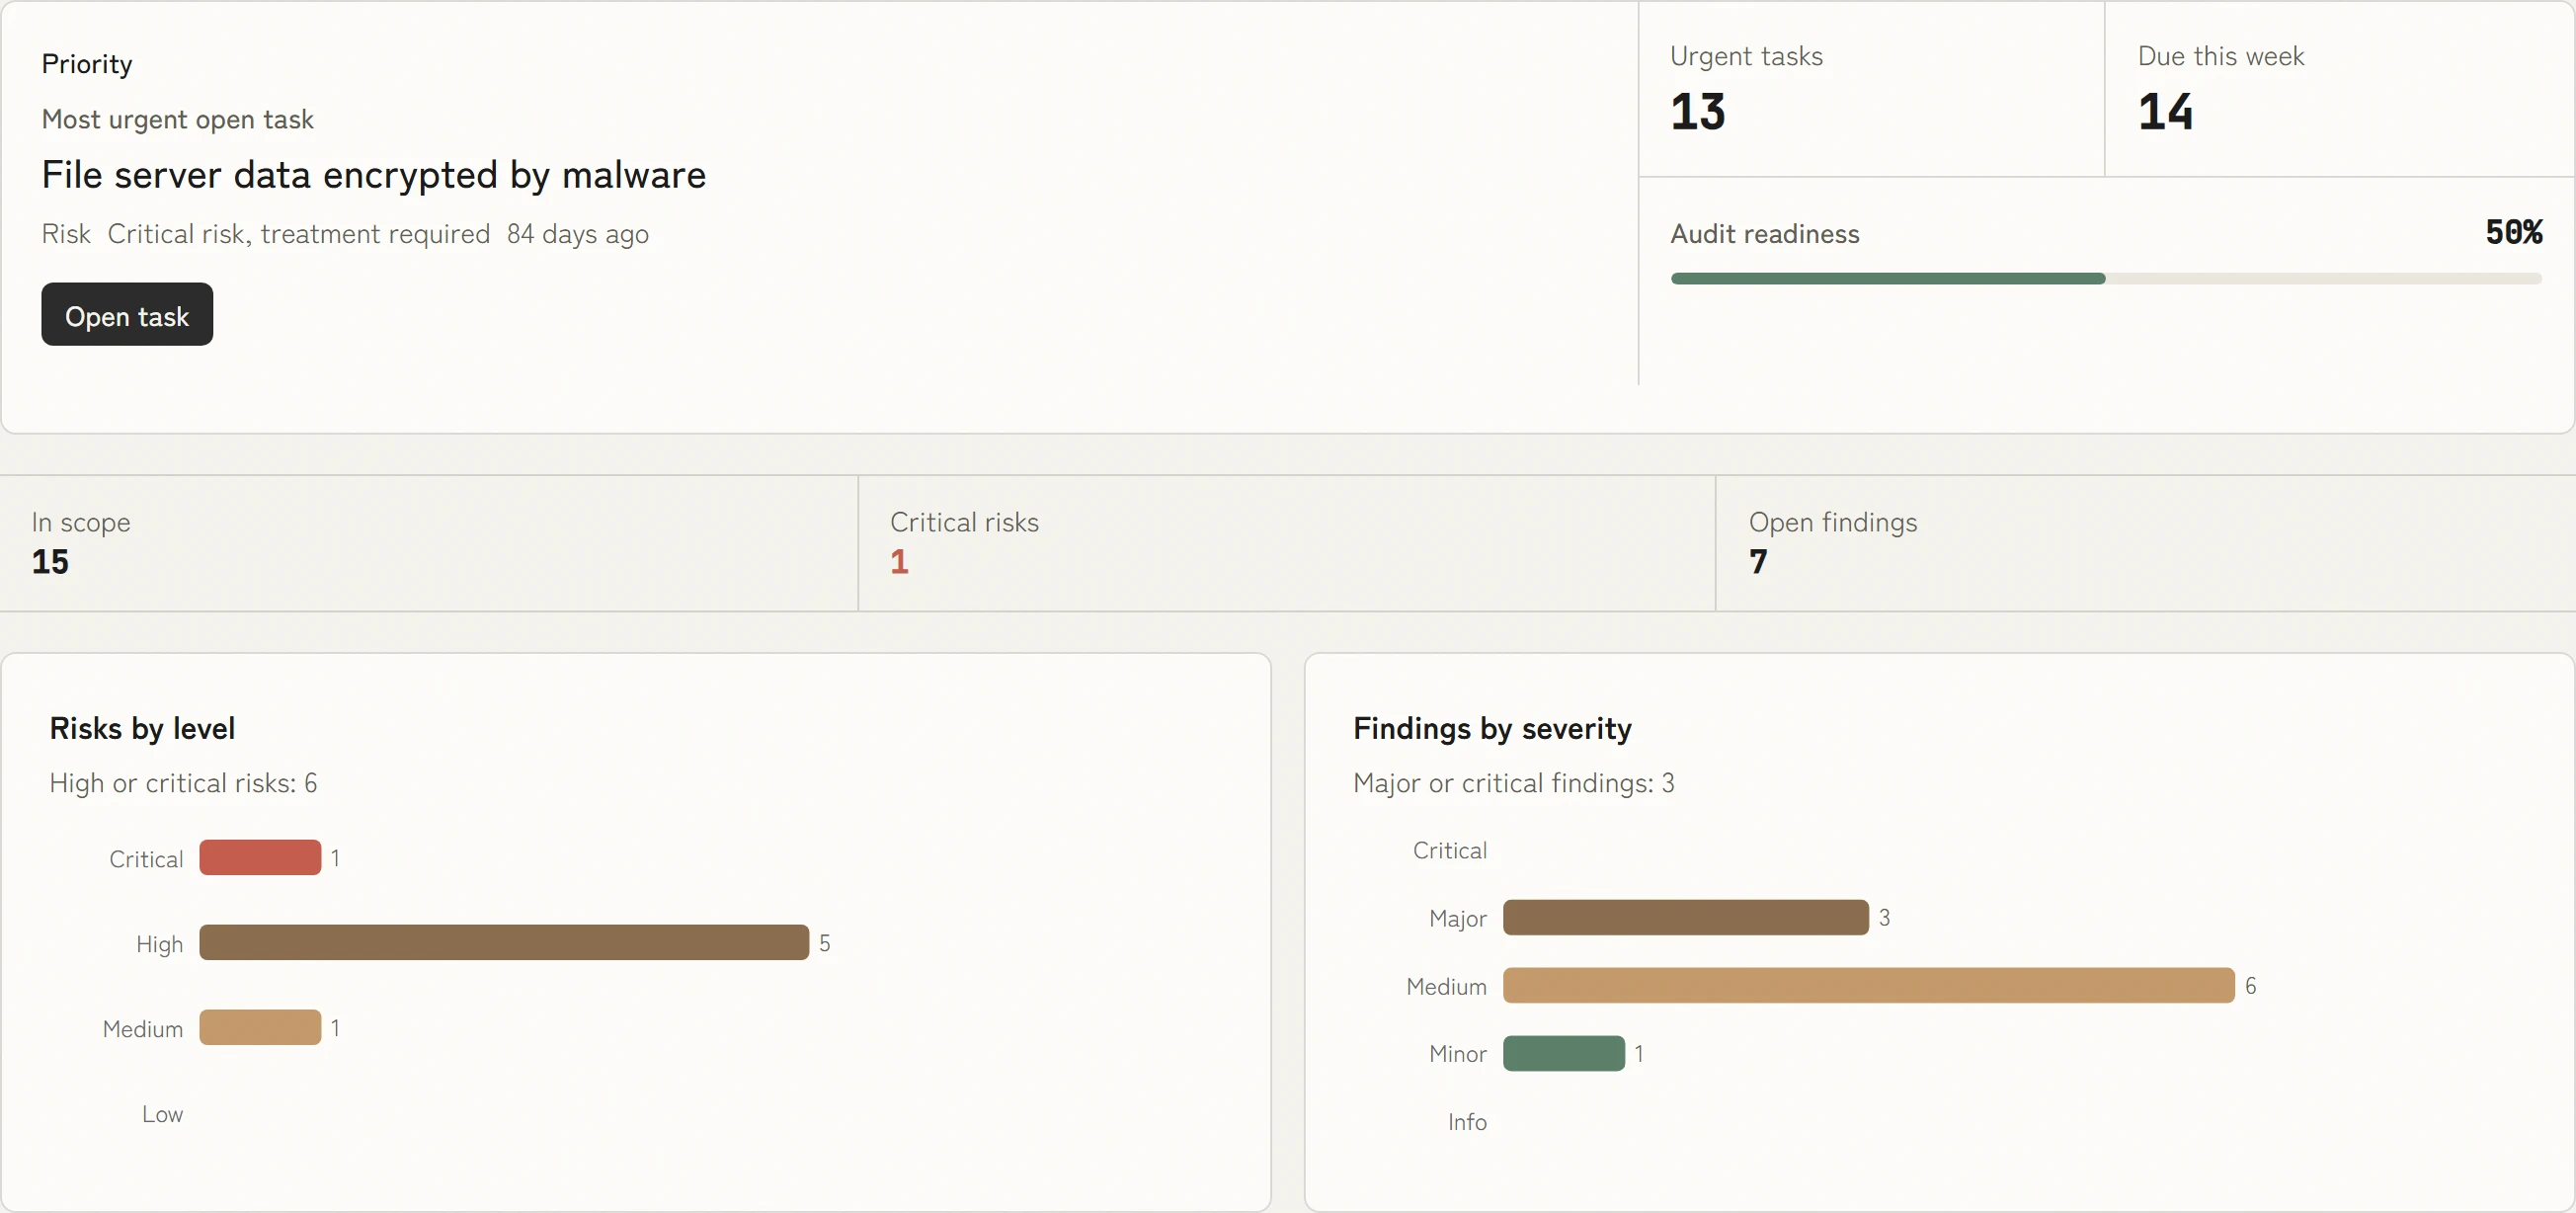
KaitoSec brings risks, residual risks, approvals and exercise outcomes from all management systems into one understandable view. You see what needs deciding, and every decision stays on record.



 5.0 out of 5
What changes for your team
Make leadership accountability traceable
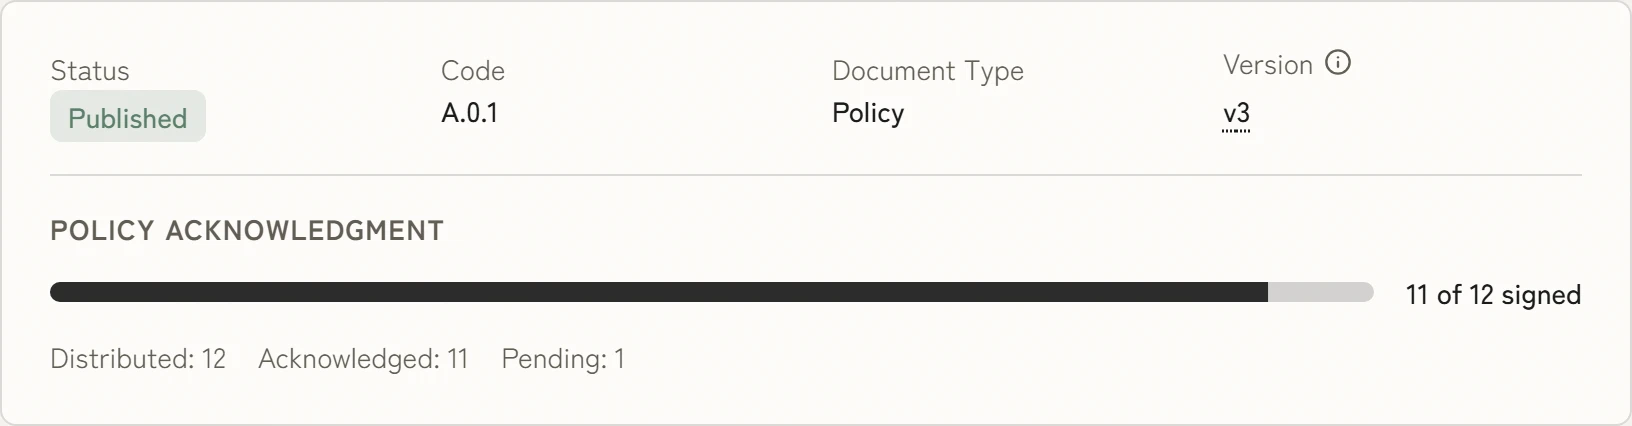
Document training, approvals and oversight of material risks as a reviewable evidence chain. KaitoSec supports governance; legal assessment depends on the specific circumstances.
One report instead of four separate ones
Risks from ISMS, BCMS, DSMS and AIMS roll up into one consolidated picture for the board, the insurer or investors. No spreadsheet stitching between departments, no gaps between quarters.
Decisions that hold up in an audit
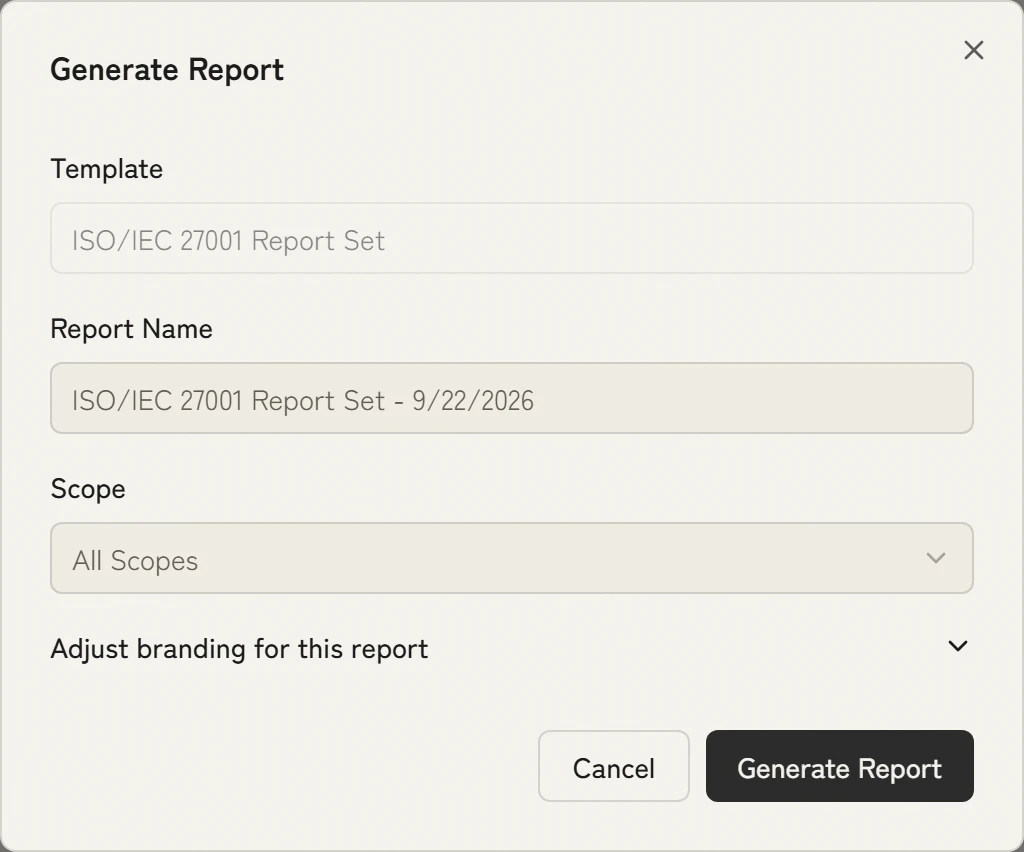
Risk acceptance, residual risk and control choices are versioned and timestamped. Who decided what, when and on whose sign-off is on record. Auditor, regulator and D&O insurer see the reasoning, not just the outcome.
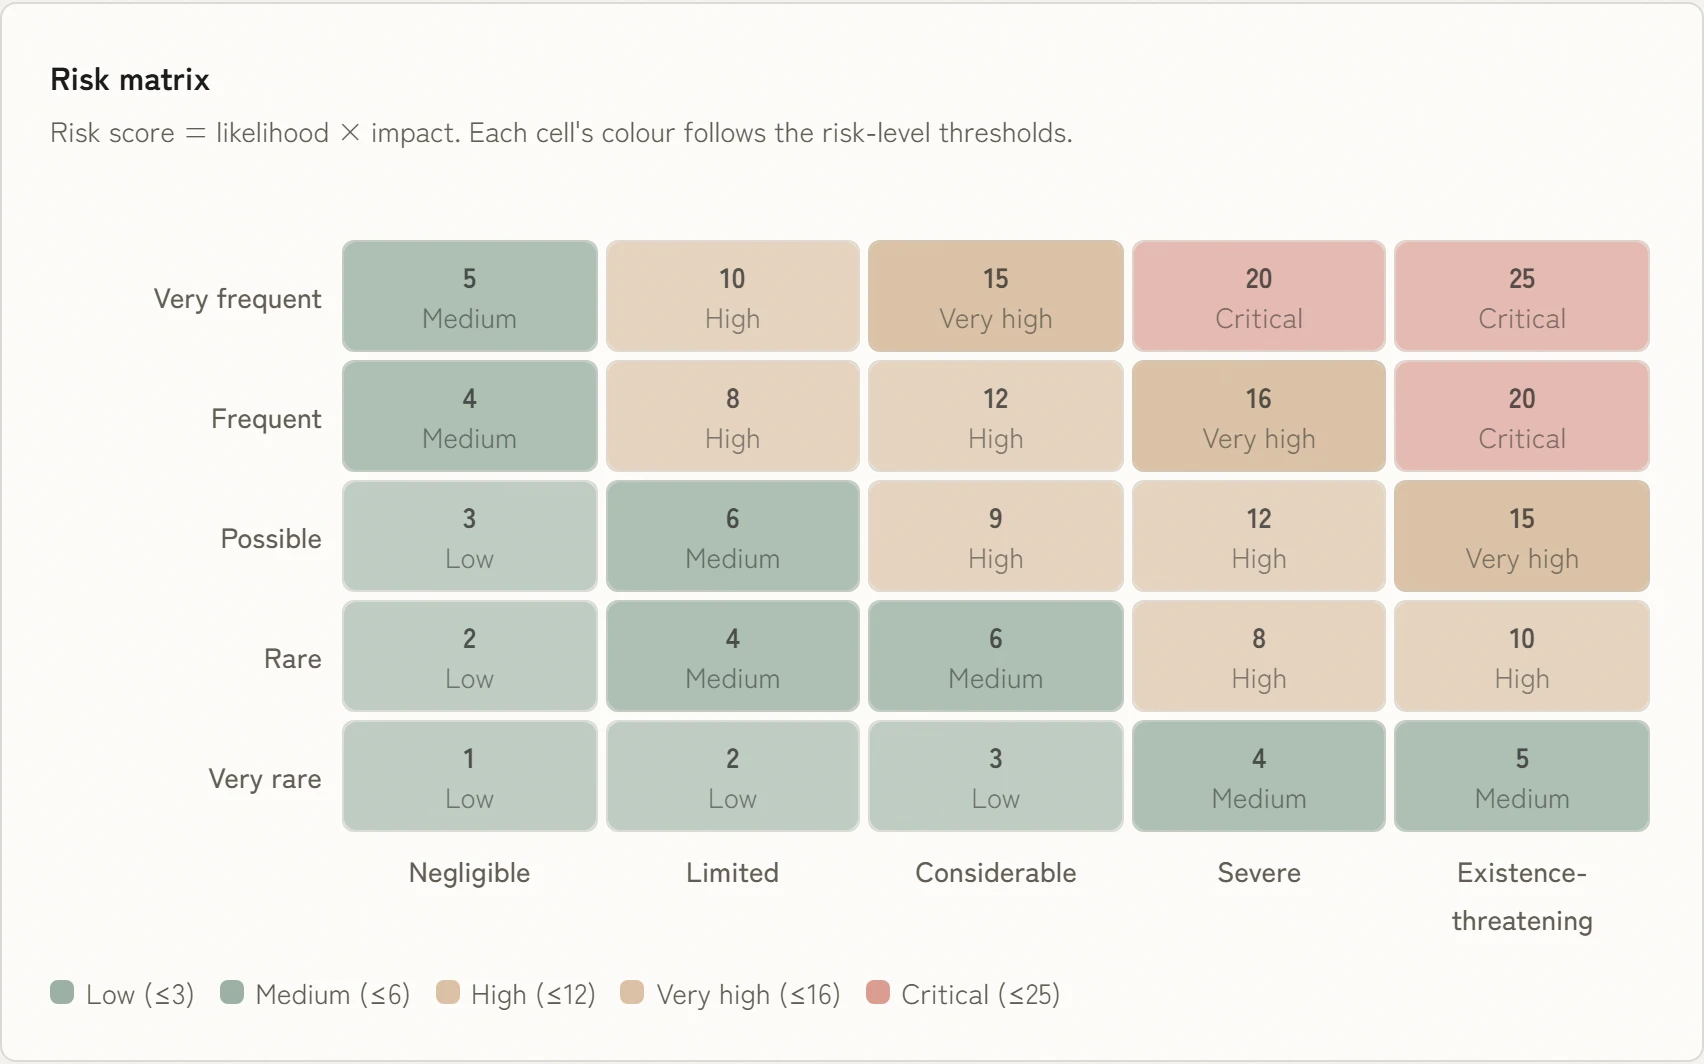 Inherent riskResidual risk
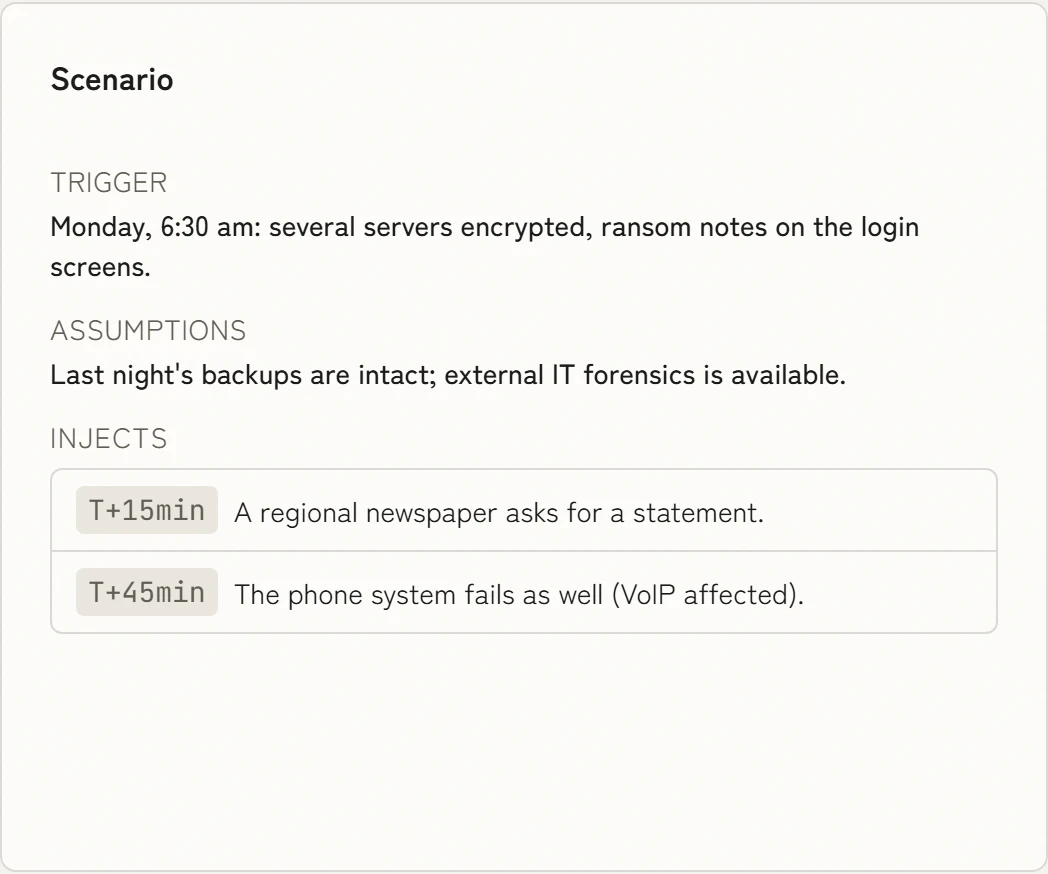
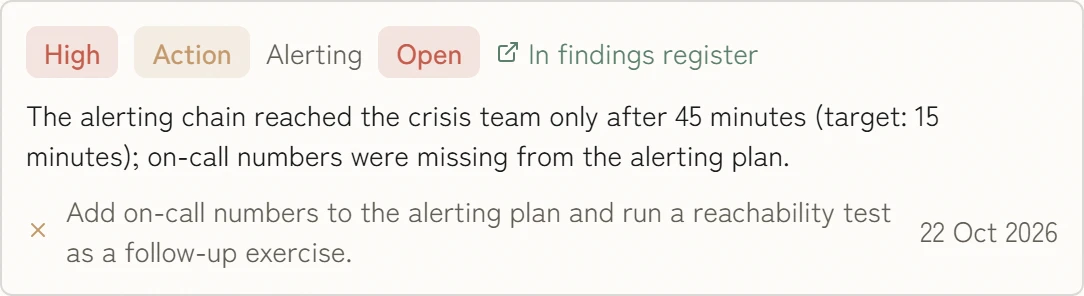
Prove crisis readiness instead of claiming it
BIA, RTO/RPO and exercise records live in the same system as the compliance evidence. When the regulator asks whether plans are actually rehearsed and exercises carried out, you answer with logged test and exercise results from live operations, not with a plan document no one has ever tested.
The picture builds on the systems you already use.
100+ integrations
All integrations
















Matching standards and modules
How KaitoSec supports the work

Bring calm to your working week.
A personal demo in 30 minutes: we show you the picture your leadership gets of risks, approvals and exercises.