
NIS2
What NIS2 actually requires of your organisation
The German NIS2 implementation act has applied since 6 December 2025, and the BSI registration deadline expired on 6 March 2026. Articles, templates and a checker help you place your organisation; the legal assessment stays with you.

What to clarify first
50 / 250
employees
From 50 employees or more than 10 million euros in turnover and balance sheet total you are an important entity, from 250 or more than 50 million euros in turnover a particularly important one (Section 28 BSIG).
6 March 2026
registration with the BSI
Registration was due three months after the law entered into force (Section 33 BSIG). Organisations that have not registered yet do that first.
24 h · 72 h · 30 d
reporting cascade
Early warning, incident report and final report for a significant incident (Section 32 BSIG). Alongside it the ten minimum measures (Section 30) and the duty of management (Section 38).
This page is orientation, not legal advice. The binding classification of your organisation belongs in a professional and legal review.


 5.0 out of 5
Where to start
- Knowledge HubArticles on scope, duties, accountability and practical implementation.Browse articles
- Template Library49 adaptable Word and Excel starting points for policies, registers, incident forms and supplier reviews.Download templates
- NIS2 Compliance CheckerStructured questions on scope and maturity with an orientation report by email.Start the checker
- For energy utilitiesHow energy utilities implement NIS2, Section 30 BSIG and the BNetzA IT security catalogue in one system, IT and OT included.Read the sector page
Read in depth
Ten articles on scope, the measures, reporting, accountability and the supply chain, each with the provisions it rests on.
Basics & Compliance
Scope, registration, deadlines and how NIS2 relates to ISO 27001.
Risk Management
The ten statutory minimum measures, how they are read and where implementations usually fail.
Incident Response
The reporting cascade at 24 hours, 72 hours and 30 days, and what belongs in each step.
Governance & Accountability
The personal duty of the management body and the policy set small organisations actually need.
Supply Chain Security
The supplier inventory without which the supply chain duties cannot be evidenced.
The legal frame
The frame moved. The certificate folder did not.
Management approves, oversees and is liable.
The management bodies of essential and important entities must approve the cybersecurity risk-management measures, oversee their implementation and can be held liable for infringements. Members of those bodies are required to follow training.
Reporting deadlines run in hours, not weeks.
An early warning within 24 hours of becoming aware, an incident notification within 72 hours, a final report within one month. Assembling the facts during the incident does not meet that clock.
Continuity sits in the same list of duties as cryptography.
Business continuity, backup management, disaster recovery and crisis management are part of the minimum measures, not an annex for later.
The supply chain is part of your own risk.
The minimum measures include supply chain security, covering the relationships with direct suppliers and service providers. An organisation that does not know its suppliers cannot assess them.
NIS2 on top of what you already have
In KaitoSec NIS2 sits on the same controls as ISO 27001. What your ISMS already meets counts for NIS2, and you see straight away which requirements are still open.
NIS2 in KaitoSec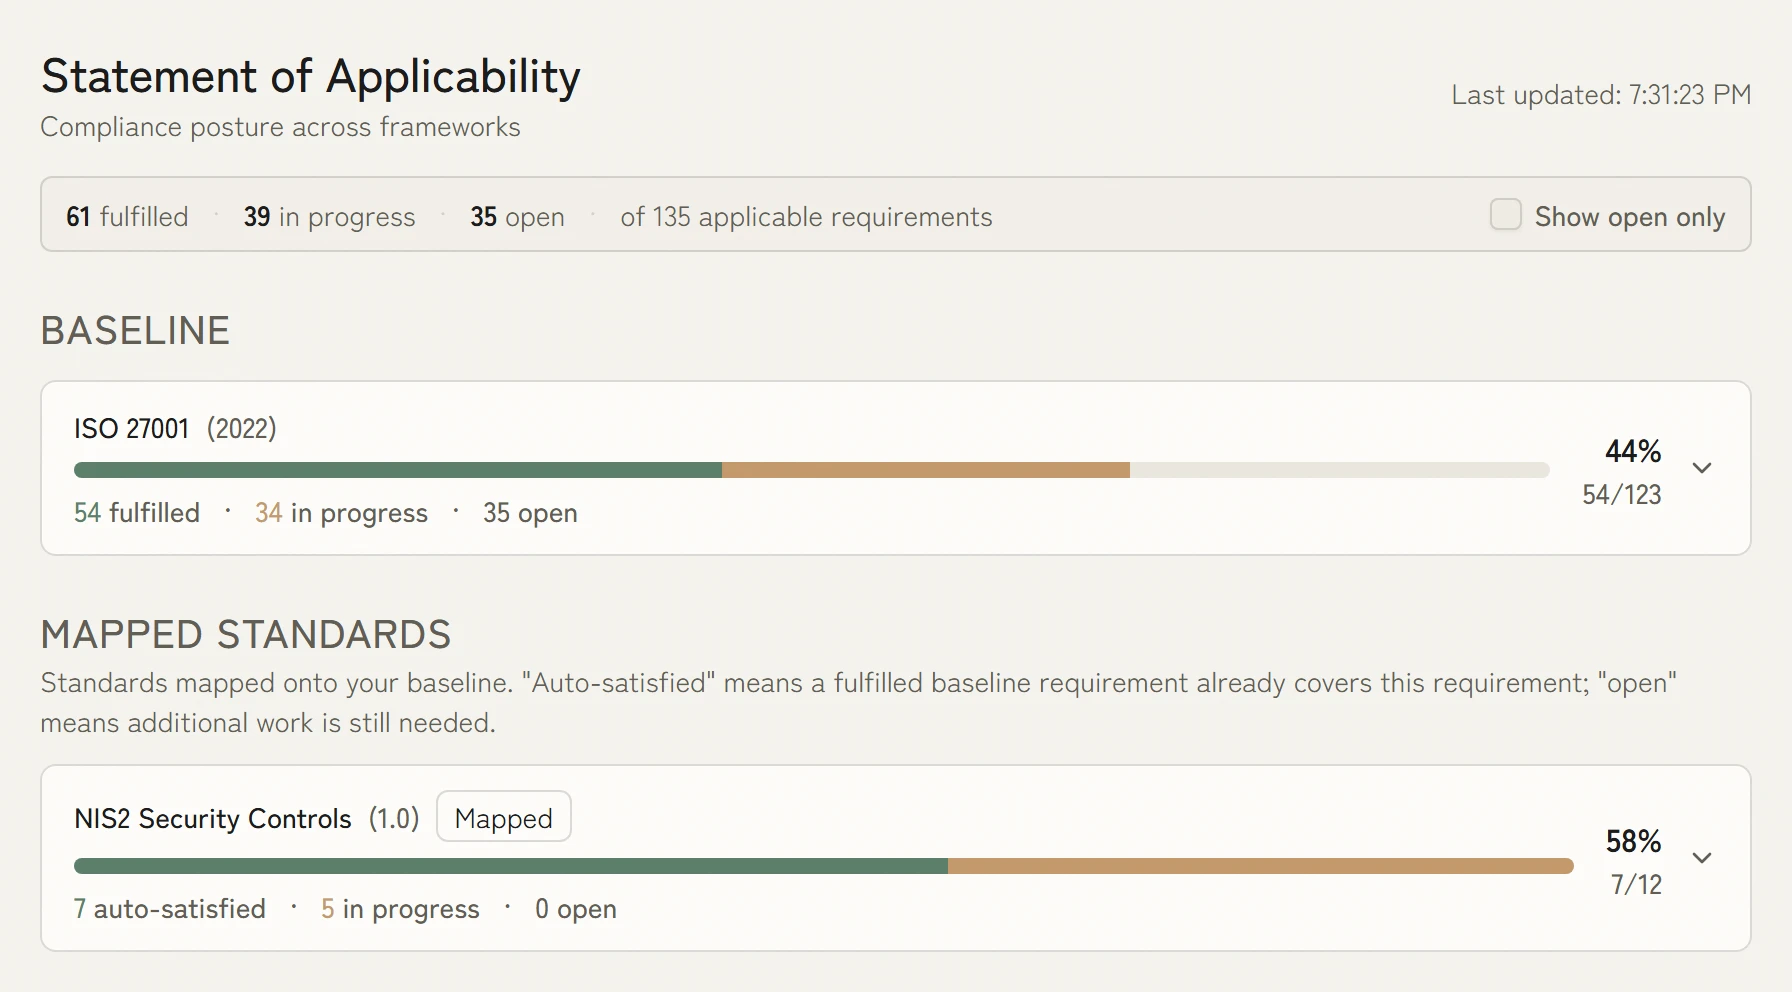

From classification to implementation.
Once the classification stands, the work starts: ten measures under Section 30 BSIG, reporting routes, the supply chain and the evidence the BSI expects. We go through your case and tell you what is still open.